CTEM vs.
PTaaS
Penetration testing proves how attackers could break in. Continuously reducing exposure across the business requires a program built around that evidence.
Penetration Testing as a Service
Deliver on-demand and continuous penetration testing with real-time findings and retesting.
Continuous Threat Exposure Management
Discover, prioritize, validate, and reduce exposures using business and threat context.
From Point-in-Time Tests to Continuous Validation
Penetration testing has long been the clearest way to prove whether attackers can actually exploit an environment. Traditional engagements, however, are scoped, scheduled, and delivered as static reports that age quickly.
Penetration Testing as a Service (PTaaS) modernizes that model with on-demand and continuous testing, real-time findings, direct collaboration with testers, and retesting that keeps pace with change.
PTaaS is increasingly adopted to support continuous threat exposure management (CTEM) programs, offering dynamic scoping and real-time collaboration across the teams involved.
Innovation Insight: Penetration Testing as a Service, Mitchell Schneider, Dhivya Poole, 3 October 2025
Gartner is a registered trademark of Gartner, Inc. and/or its affiliates and is used herein with permission. All rights reserved. Gartner does not endorse any vendor, product or service depicted in its research publications, and does not advise technology users to select only those vendors with the highest ratings or other designation. Gartner research publications consist of the opinions of Gartner’s research organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this research, including any warranties of merchantability or fitness for a particular purpose.
Continuous Threat Exposure Management (CTEM) is the broader program. It scopes what matters to the business, discovers exposures across the attack surface, prioritizes them by risk, validates what is exploitable, and mobilizes teams to reduce it. PTaaS is one of the strongest ways to deliver the validation stage.
What Is Penetration Testing as a Service (PTaaS)?
PTaaS is a delivery model for penetration testing that combines testing expertise with a platform for scoping, real-time findings, collaboration, and retesting.
Its purpose is to prove which weaknesses attackers can actually exploit, and to get those findings to the teams who fix them faster than a static report allows.
Scope
Define the applications, networks, cloud environments, or business services to test and the rules of engagement.
Test
Combine automated, agentic, and human testing to exploit weaknesses the way an attacker would.
Report
Deliver findings in real time with evidence, severity, and remediation guidance, often directly into ticketing tools.
Retest
Retest fixed findings on demand to confirm the weakness is closed.
- Proves real exploitability with evidence, not theoretical severity.
- Finds logic flaws, chained attacks, and weaknesses scanners miss.
- Delivers findings in real time so remediation can start immediately.
- Supports on-demand retesting and compliance-driven testing.
- Testing covers the assets in scope, not the full attack surface.
- Findings are not always tied to business priorities or asset ownership.
- Results can sit apart from vulnerability, cloud, and identity programs.
- More tests do not automatically mean less exposure across the business.
What Is Continuous Threat Exposure Management (CTEM)?
Continuous Threat Exposure Management (CTEM) is a cybersecurity operating model designed to continuously identify, assess, validate, and reduce exposures that could lead to a successful attack.
Unlike PTaaS, which focuses on testing defined targets, CTEM addresses exposures across infrastructure, applications, cloud environments, identities, and external attack surfaces. It connects technical findings with business priorities to determine what matters most and coordinate action.
Gartner's CTEM framework organizes these activities into five interconnected stages that repeat as the organization's environment and threats evolve.
Scoping
Identify critical business functions, assets, and security priorities to define what the program must protect.
Discovery
Continuously identify vulnerabilities, misconfigurations, identity weaknesses, and other exposures.
Prioritization
Assess exploitability, reachability, threat intelligence, and business impact to determine what matters most.
Validation
Use automated, agentic, and human testing to prove whether exposures can actually be exploited and reached.
Mobilization
Assign ownership, coordinate remediation, and verify that corrective actions have reduced exposure.
Beyond Individual Vulnerabilities
CTEM considers how weaknesses across technologies, identities, configurations, and access relationships create opportunities for attackers. This provides a more complete understanding of an organization's exposure than vulnerability findings alone.
From Findings to Risk Reduction
CTEM connects discovery and prioritization with exploitability validation, accountable remediation owners, and measurable outcomes. The objective is not simply to identify security problems, but to systematically reduce the risk they create.
CTEM is an operating model, not simply another security tool. Organizations can build a CTEM program using existing technologies, integrated platforms, internal teams, and external expertise. What defines CTEM is how these capabilities work together to continuously reduce meaningful security exposure.
CTEM vs. PTaaS: Key Differences
PTaaS and CTEM are closely connected, but they operate at different levels. PTaaS is a testing capability. CTEM is the program that decides where testing matters most and acts on the results. The table below compares the two.
These distinctions describe typical scope and emphasis. Many PTaaS programs already feed CTEM, and mature programs scope testing around business risk.
The central difference: PTaaS answers “Can this be exploited?” CTEM answers “Which exposures matter most, and are we reducing them?” PTaaS is one of the strongest inputs to that answer.
Where PTaaS Alone Falls Short
A mature PTaaS program delivers high-confidence findings. On its own, it still leaves gaps that limit how much exposure the organization actually reduces.
Scope Set Without Business Context
Tests target what was requested, which may not reflect the business services, assets, or attack paths that matter most.
Coverage Outside the Test Scope
Even continuous testing covers only what is in scope. New assets, changes, and misconfigurations outside it can go unvalidated until the scope is updated.
Findings Disconnected From Other Data
Pentest results often live apart from vulnerability, cloud, identity, and attack surface data, so related exposures are not seen together.
Fixes Without Root-Cause Change
Remediating individual findings closes tickets, but the same classes of weakness return if root causes and ownership are not addressed.
Connect the Work. Reduce the Risk.
CTEM addresses these gaps by scoping testing around business priorities, combining PTaaS results with continuous discovery, and mobilizing owners to fix root causes, so every test moves measurable exposure down.
These limitations are not universal. Organizations with mature PTaaS programs may already practice elements of CTEM. The opportunity is to formalize those capabilities into a broader, repeatable program.
From PTaaS to CTEM: Where to Start
You don't replace PTaaS to adopt CTEM. You make it the validation engine of a broader program.
- 01 Phase 1
Start With Your Testing Program
Keep your PTaaS engagements, findings, and retest workflows. They become the foundation of CTEM validation.
Foundation - 02 Phase 2
Scope by Business Impact
Choose test targets based on the business services and attack paths that matter most.
Scoping - 03 Phase 3
Broaden Discovery
Feed testing with continuous discovery across assets, cloud, identities, and third parties.
Discovery - 04 Phase 4
Prioritize What to Validate
Rank exposures by business risk, then use PTaaS to prove which are exploitable and reachable.
Prioritization · Validation - 05 Phase 5
Mobilize and Measure
Route findings to the right owners, fix root causes, and track exposure reduction over time.
Mobilization
CTEM vs. PTaaS, Answered.
Common questions from security leaders weighing how Penetration Testing as a Service and Continuous Threat Exposure Management fit together, and how to get started.
01 Does CTEM replace penetration testing?
No. Penetration testing remains one of the most important ways to validate exposures. In a CTEM program, PTaaS delivers the evidence of exploitability that the validation stage depends on.
CTEM adds what PTaaS alone doesn’t cover: business scoping, continuous discovery across the full attack surface, risk-based prioritization, and coordinated mobilization across teams.
02 What is the main difference between PTaaS and CTEM?
PTaaS is a way to deliver penetration testing continuously and collaboratively. CTEM is an operating model for continuously reducing the exposures most likely to impact the business. PTaaS is a capability; CTEM is the program that directs it.
03 How is PTaaS different from traditional penetration testing?
Traditional penetration testing is typically a scoped, scheduled project that ends with a static report. PTaaS delivers testing on demand or continuously through a platform, with real-time findings, direct collaboration with testers, and retesting of fixes.
04 Where does PTaaS fit in the five stages of CTEM?
PTaaS sits primarily in the validation stage, proving which exposures are exploitable and reachable. It also supports scoping, by testing what matters most, and mobilization, through retests that confirm fixes.
05 How often should we run penetration tests in a CTEM program?
Let risk drive frequency. Test after significant changes, when new exposures are prioritized, and regularly for critical business services, rather than relying only on an annual schedule.
06 Can automated testing replace human penetration testers?
Not entirely. Automated and agentic testing add speed and coverage, while human testers find business-logic flaws and chained attacks that tools miss. The strongest programs combine both.
07 How does TrollEye Security support CTEM and PTaaS?
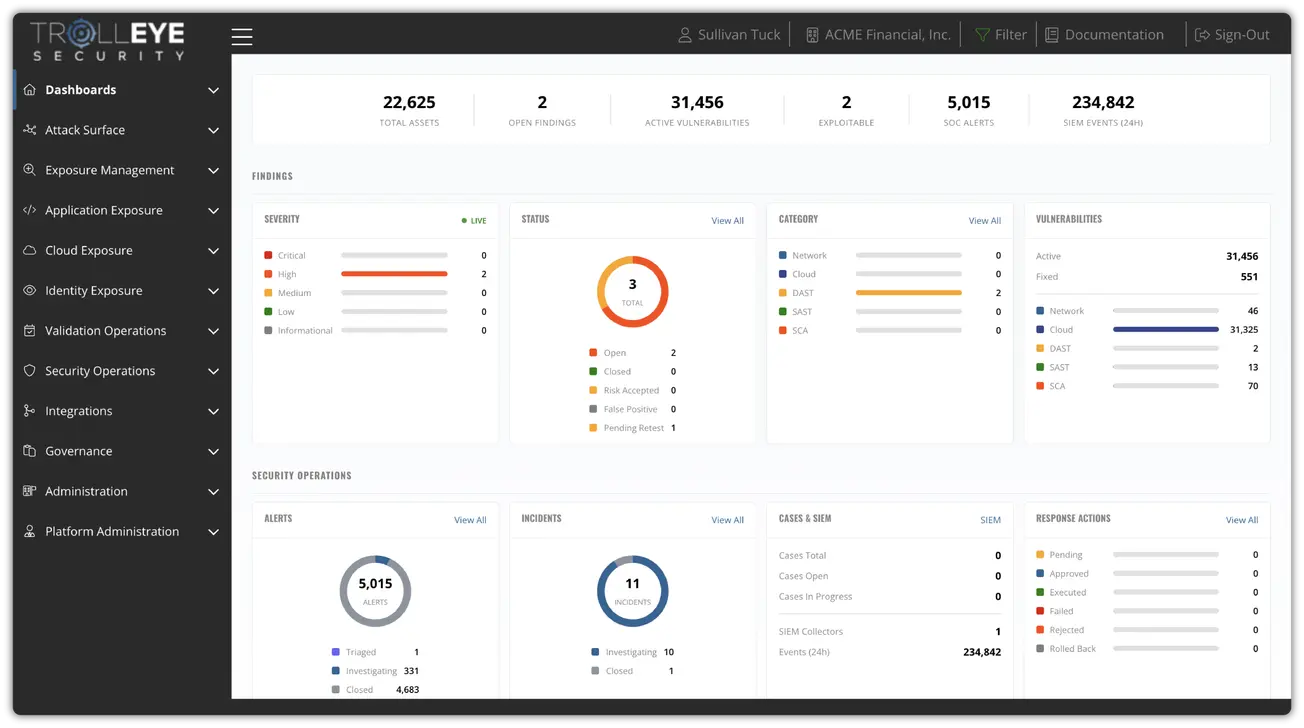
TrollEye Security combines a CTEM platform with expert services, including PTaaS delivered through agentic and human testing. Validated findings flow directly into prioritization and mobilization workflows that direct the right owners to fix root causes, all in one place.
Turn Penetration Testing Into Continuous Exposure Reduction
TrollEye Security’s CTEM solution puts penetration testing at the center of a continuous program. It brings scoping, discovery, prioritization, validation, and mobilization together, so every test targets what matters and every finding drives a fix at the root cause. One platform, backed by expert services, to put CTEM into practice.