What differentiates TrollEye Security is their level of engagement. They operate as a true partner, embedding into our DevSecOps workflows and working directly with our engineering teams to improve processes and drive remediation.
Comparison Overview
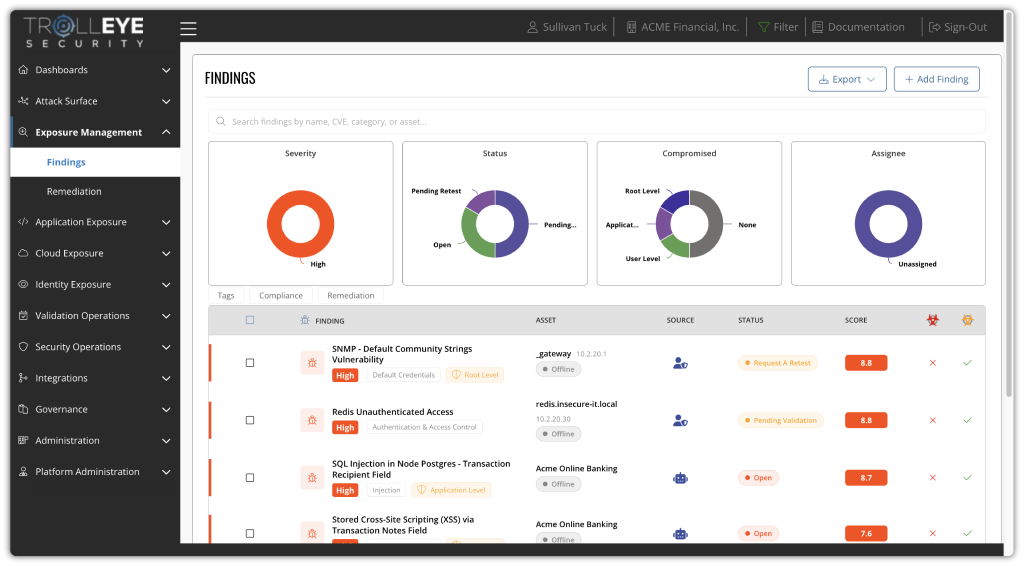
Most security teams stitch together 6-10 point solutions just to get basic coverage. TrollEye replaces the patchwork, delivering continuous pen testing, SAST, DAST, dark web monitoring, and SIEM in a single unified CTEM platform.
✓ Human-led testing ✓ CTEM-native platform
SAST, DAST, SCA, SIEM, MDR, penetration testing, BAS, dark web monitoring, and other specialized solutions each provide valuable capabilities. The challenge is that their findings often remain inside separate tools, teams, and workflows. CTEM brings that exposure together so security teams can understand how risks relate, prioritize them using shared context, and coordinate remediation around the changes that reduce the most risk.
CTEM does not make specialized security capabilities unnecessary. It gives them a shared operating model. Application findings, vulnerabilities, attack paths, penetration-test results, detection gaps, identity risks, external exposures, and other security issues can be evaluated together instead of competing for attention in separate queues. That creates better context for deciding what matters, what should be fixed first, and where one change can reduce multiple sources of risk.
TrollEye combines the CTEM platform with the security capabilities and expert services needed to move from finding risk to reducing it. We help validate whether exposures are real, connect related findings to shared root causes, organize remediation around the changes with the greatest impact, support technical and process improvements, and retest those changes to verify that risk actually went down.
Specialized products can be excellent at the problem they were built to solve. The challenge is connecting their findings, context, testing, remediation, and outcomes across the broader security program.
Bring application security, offensive validation, dark web exposure, managed detection and response, and broader exposure management into one program with shared risk context, remediation workflows, expert support, and continuous verification.
See where specialist tools provide deep capabilities, where CTEM creates a more unified approach, and how TrollEye combines broader coverage with expert security services in one solution.
| Capability | TrollEye CTEM Platform + expert services | Other CTEM Platforms Exposure management | MSSP / MDR Monitor & respond | AppSec Tools SAST + SCA + DAST | SIEM Detect & respond | Dark Web Monitoring External intelligence |
|---|
Connect application, infrastructure, identity, dark web, validation, detection, and offensive-security exposure instead of managing isolated findings across separate programs.
Use shared asset, business, threat, exploitability, and attack-path context to determine what actually deserves attention across security domains.
TrollEye security experts help identify root causes, implement technical and process improvements, and verify that the resulting risk was actually reduced.
Categories represent broad operating models rather than every individual vendor or package. Specialist platforms may provide substantially greater depth within their primary discipline. Capabilities vary by product, licensing, integrations, and professional-service scope. Hover or tap any rating for context.
See why security leaders choose TrollEye for a combination of technology, hands-on expertise, continuous collaboration, and measurable security improvement.
What differentiates TrollEye Security is their level of engagement. They operate as a true partner, embedding into our DevSecOps workflows and working directly with our engineering teams to improve processes and drive remediation.
TrollEye’s approach of employing various attack vectors, from dark web analysis to physical breach attempts, demonstrated their understanding of the complex nature of modern cybersecurity threats facing financial institutions. It’s simple, yet powerful.
I consider TrollEye to be a true hidden gem in the realm of security solutions and an invaluable technology partner. Talquin has been utilizing TrollEye’s services for over four years now, and our experience has been nothing short of exceptional.
PTaaS has been a wonderful addition to our Development Lifecycle. TrollEye’s platform provides a unique experience and excellent value!
Stop reacting. Start exposing. TrollEye’s CTEM solution unifies pen testing, application security, dark web monitoring, SIEM, and program management, so your team can see every risk and act fast.
No commitment · Talk to a real security expert
Conversations with CISOs
Four security leaders. One candid conversation about budgets, teams, security tools, and the tradeoffs CISOs face heading into 2027.
Join the Conversation With
Jeff Moore
CISO, H&M
Elizabeth Di Bene
CISO, Loudon County
JoJo D
Cyber Leader, Co-Founder of Chaos & Signal
Aby Rao
Deputy CISO, Fintech