
Turn Validated Risk Into Coordinated Remediation
Get findings to the right people, organize related work around common fixes, and verify that remediation actually reduced risk.
Prioritized and validated findings can still sit unresolved when ownership is unclear or work stalls between teams. TrollEye routes findings to the teams and individuals responsible for fixing them, syncs work into Jira, groups related findings into remediation initiatives, and enables retesting after changes are implemented.
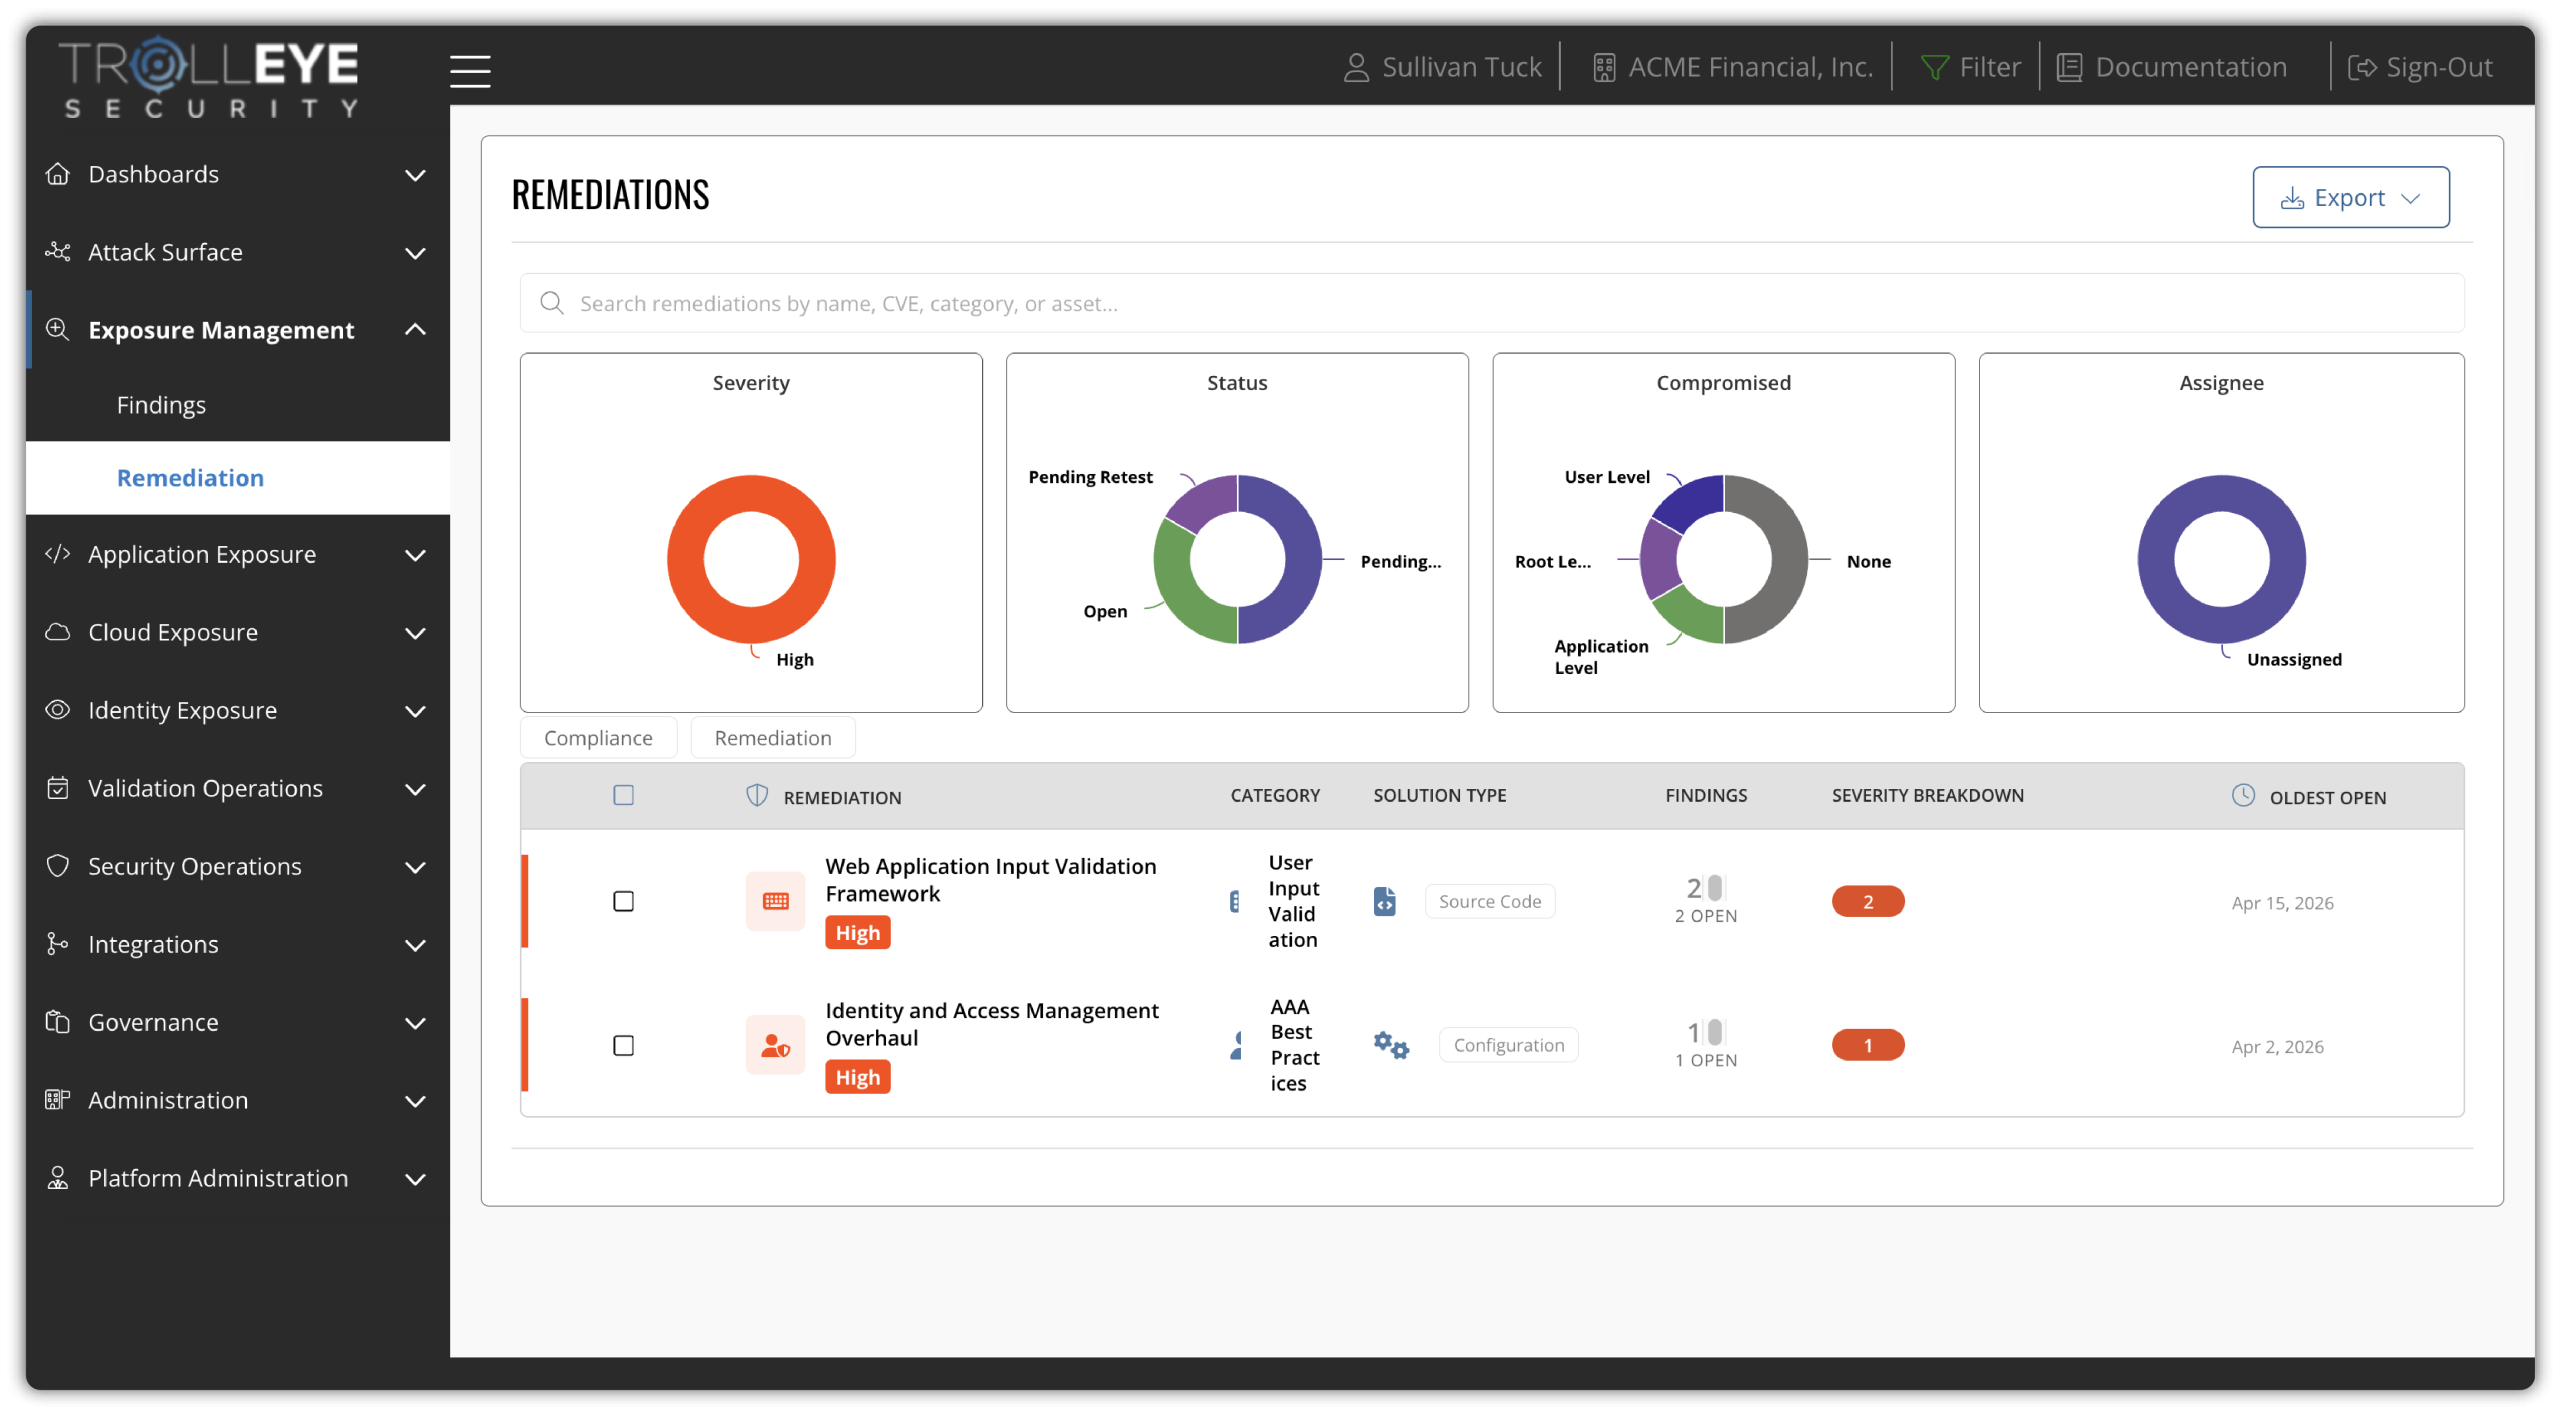
Walk Through Our Interactive Demo →
Route validated findings to the teams and individuals responsible for remediation.
Group related findings around common process or technical fixes that can eliminate multiple exposures.
Request retesting after changes are implemented to confirm the exposure was actually eliminated.
Your Backlog Never Stops Growing. Neither Should Your Mobilization.
Security teams are losing the remediation race. Validated findings pile up faster than teams can act, responsibility gets lost across departments, and the same underlying issues can create exposure again and again. Even when fixes are made, teams still need a way to verify the risk was actually reduced.
Validated Findings Pile Up Faster Than Teams Can Act
Without a structured mobilization process, findings accumulate faster than they can be resolved, leaving important risks waiting in the backlog.
Ownership Gets Lost Across Teams
When it isn’t clear which team or individual is responsible for remediation, findings can stall between security, engineering, IT, and operations.
The Same Issues Keep Creating New Exposure
Fixing findings individually can leave shared process or technical causes unresolved, allowing related exposures to continue appearing over time.
Risk Reduction Is Hard to Demonstrate
Growing backlogs and fragmented remediation make it difficult to show leadership how identified risk is moving toward resolution.
Why Buyers Choose TrollEye for CTEM Mobilization
Prioritizing risk is only the beginning. TrollEye helps move validated exposures into structured remediation by routing findings to the right owners, coordinating work in the tools teams already use, grouping related issues around common fixes, and retesting changes to verify risk was actually reduced.
Built to Move Findings Into Remediation
Once an exposure is validated, TrollEye turns it into actionable remediation work and keeps the process connected from finding creation through verification.
- Validated exposures become findings that can be tracked through remediation.
- Findings are routed to the teams and individuals responsible for fixing them.
- Jira synchronization moves remediation work into the workflows teams already use.
- Related findings are grouped into remediation initiatives so one process or technical fix can eliminate multiple exposures.
- Once changes are implemented, retesting can be requested to verify the exposure was actually eliminated.
Expert Support to Keep Remediation Moving
Technology can coordinate the workflow, but complex remediation still benefits from security expertise. TrollEye’s security team works alongside your teams to help move high-impact findings toward verified resolution.
- Remediation triage and prioritization so teams stay focused on the exposures that matter most.
- Cross-team coordination across security, engineering, IT, and operations.
- Root-cause analysis to identify fixes that can address multiple related findings.
- Guidance throughout remediation when teams need additional security expertise.
- Retesting after changes are implemented to verify the identified exposure was actually resolved.
TrollEye connects the work between identifying risk and actually reducing it. Validated exposures become findings, findings reach the people responsible for remediation, related issues can be addressed through common initiatives, and completed changes can be retested to confirm the exposure is no longer present.
See TrollEye Mobilization in Action
Get a firsthand look at how the TrollEye CTEM solution groups related exposures, identifies root causes, and turns findings into actionable remediation initiatives that help teams fix underlying issues and reduce risk over time.
What Makes CTEM Mobilization Work, and Why It Matters for Every Stage Before It
Mobilization is the payoff everything else builds toward. Here’s what structured, accountable remediation gives your security program that ad hoc fixing can’t.
Stop Reacting. Start Reducing.
Prioritization and validation help determine what matters. Mobilization makes sure that risk turns into coordinated remediation instead of another finding sitting in the backlog.
Make Ownership Clear.
Validated findings are routed to the teams and people responsible for fixing them, helping reduce the ambiguity that causes remediation to stall between departments.
Fix More Than One Finding at a Time.
Related findings can be grouped into remediation initiatives so teams can address a shared process or technical issue and eliminate multiple exposures through one coordinated fix.
Verify That Risk Was Actually Reduced.
Once remediation changes are implemented, retesting can be requested to confirm the identified exposure was actually eliminated and close the loop on the CTEM process.
Validated Risk Only Matters When It Gets Fixed.
Mobilization is where CTEM turns insight into reduced risk. Here are the questions security leaders ask about ownership, remediation workflows, retesting, and how TrollEye moves validated exposures to verified resolution.
01 What is mobilization in CTEM?
Mobilization is the fifth and final stage of Continuous Threat Exposure Management (CTEM). It turns validated exposures into coordinated remediation by assigning ownership, moving work into the teams and workflows responsible for fixing it, and verifying that each fix actually reduced risk.
Scoping, discovery, prioritization, and validation determine which exposures matter. Mobilization is where that work pays off, because risk only goes down when someone acts on it.
02 How is CTEM mobilization different from vulnerability remediation or patch management?
Remediation and patching are the fixes themselves. Mobilization is the operating process that gets those fixes done: deciding who owns each finding, coordinating work across security, engineering, IT, and operations, grouping related issues around a common fix, and confirming the exposure is gone.
Without that structure, even well-prioritized findings can stall between teams and sit in the backlog.
03 Why do validated security findings stay unresolved in the backlog?
The most common reasons are unclear ownership, disconnected workflows, and fixing findings one at a time. When no one knows which team or individual is responsible, findings stall between departments. When the same underlying process or technical issue keeps producing new exposures, the backlog grows faster than teams can close it.
Mobilization addresses each of these by establishing ownership, working in the tools teams already use, and targeting root causes.
04 How does TrollEye assign ownership for security findings?
TrollEye routes validated findings to the teams and individuals responsible for fixing them, so every exposure has a clear owner instead of waiting in a shared queue.
Each validated exposure becomes a finding that can be tracked from creation through verification, which gives security leaders visibility into who is responsible, what is in progress, and where work is stalling.
05 What is a remediation initiative?
A remediation initiative groups related findings around a common process or technical fix, so one coordinated change can eliminate multiple exposures at once.
Instead of closing the same type of issue over and over, teams address the shared root cause behind it. That reduces repeat exposure and makes remediation effort go further.
06 Does TrollEye integrate with Jira?
Yes. TrollEye synchronizes remediation work with Jira, so findings move into the workflows engineering and IT teams already use.
Security keeps the context and tracking in TrollEye, while the people doing the fix work from their existing tickets. That keeps remediation moving without asking every team to adopt a new tool.
07 How do we verify that a fix actually eliminated an exposure?
Once a change is implemented, teams can request a retest through TrollEye to confirm the identified exposure is no longer present.
Retesting closes the loop on the CTEM process. A finding is resolved because the exposure was confirmed eliminated, not simply because a ticket was marked complete.
08 Does TrollEye automatically remediate vulnerabilities?
Today, your team stays in control of remediation. TrollEye helps move validated exposures into coordinated action through ownership, remediation initiatives, Jira synchronization, expert guidance, and retesting.
Agentic remediation capabilities are on our roadmap, with the goal of helping teams move faster from validated exposure to fix while keeping the process controlled and verifiable.
09 What support does TrollEye's security team provide during remediation?
TrollEye's security team works alongside your teams to move high-impact findings toward verified resolution. That includes remediation triage and prioritization, cross-team coordination across security, engineering, IT, and operations, root-cause analysis, guidance during remediation, and retesting once changes are made.
The platform coordinates the workflow. The services add security expertise when remediation is complex.
10 How does mobilization help show leadership that risk is going down?
Mobilization connects every finding to an owner, an action, and a verified outcome, which makes risk reduction measurable instead of anecdotal.
Leadership can see validated exposures moving from finding to fix to confirmed resolution, rather than a growing backlog or a count of closed tickets that may not reflect real change.
11 How does mobilization connect to the earlier stages of CTEM?
Mobilization acts on the output of every stage before it. Scoping defines what matters to the business, discovery finds exposures, prioritization ranks them, and validation proves which are actually exploitable and reachable.
Mobilization takes those validated exposures and turns them into coordinated remediation. Without it, the earlier stages produce insight but not reduced risk.
12 How much does TrollEye cost, and can we try it first?
TrollEye CTEM starts at $995 per month, and eligible packages include a 14-day free trial.
Teams can start with the capabilities they need today and expand coverage and workflows as TrollEye becomes part of their continuous exposure management process. See the pricing page for package details.
Route ownership, group fixes by root cause, and retest to prove risk went down.
Continue to CTEM Mobilization
Validation confirms which exposures deserve action. Mobilization turns that evidence into coordinated remediation by establishing ownership, grouping related exposures, moving work into the right teams and workflows, and verifying that fixes actually reduce risk.
 Jeff Moore
 Elizabeth Di Bene
 JoJo D
 Aby Rao