IoT Penetration Testing. Secure Every Connected Device.
Our IoT penetration testing validates real-world exploitability across firmware, embedded systems, communication protocols, authentication mechanisms, and the cloud and mobile services that support your connected devices.
It is one of the core tests inside our PTaaS solution, so every device-level finding flows into the same platform, the same remediation process, and the same CTEM program as the rest of your testing.
We Test The Device. And Its Ecosystem.
IoT environments vary widely in architecture, communication protocols, and operational impact. Our testing adapts to each device’s function, connectivity model, and exposure surface, from embedded firmware to cloud APIs and mobile integrations, so testing covers the paths attackers can actually use.
Need the network around it? See Network Penetration Testing →Industrial & OT Systems
PLCs, SCADA components, industrial sensors, and OT gateways tested for insecure protocols and segmentation gaps.
Smart Building Devices
HVAC controllers, access systems, and BMS platforms that can become pivot paths into corporate networks.
Healthcare & Medical IoT
Connected medical equipment and remote monitoring systems assessed for wireless exposure and access control flaws.
Consumer & Embedded Devices
Smart devices, wearables, and embedded electronics tested for firmware and update mechanism weaknesses.
Edge & Gateway Devices
Gateways, edge nodes, and device management platforms tested for exposed services and weak encryption.
Cloud APIs & Mobile Apps
The companion apps, cloud APIs, and identity controls that connect to and manage your devices.
Recognized By The Industry. Trusted By Security Teams.
An IoT testing program should create measurable improvement, not just another report. TrollEye combines continuous testing, hands-on expertise, and remediation support in a model recognized by Gartner and trusted by security teams across multiple industries.
Representative Provider in a Recent Gartner® Report
Named a Representative Provider in Gartner research covering Penetration Testing as a Service.
Sample Vendor in Gartner’s 2025 Hype Cycle
Recognized as a Sample Vendor for Penetration Testing as a Service in Gartner’s Hype Cycle for Application Security.
Sample Vendor in Gartner’s 2025 Hype Cycle
Recognized as a Sample Vendor for Penetration Testing as a Service in Gartner’s Hype Cycle for Security Operations.
Our clients have reduced critical and high findings to almost zero within six months.
The goal is not simply to find more vulnerabilities. It is to build a repeatable testing and remediation process that continuously drives meaningful exposure down.

My speed to respond and my speed to remediate have gone down dramatically. My scalability, flexibility, and agility across the environment are much faster than with the big-box vendors.Watch Ricoh's Testimonial →

I consider TrollEye to be a true hidden gem in the realm of security solutions and an invaluable technology partner. Talquin has been utilizing TrollEye's services for over four years now, and our experience has been nothing short of exceptional. TrollEye's unwavering dedication to security has ultimately bolstered Talquin's overall security posture.
I am pleased with all the services we are receiving from the team at TrollEye Security. Being able to actively view findings from their platform gives our information security team the insight we need to ensure our security posture across the organization.
PTaaS has been a wonderful addition to our Development Lifecycle. TrollEye's platform provides a unique experience and excellent value!
Everything In PTaaS, Applied To Every Connected Device.
IoT penetration testing isn't a standalone engagement. It runs inside our PTaaS solution, alongside internal, external, network, and phishing testing, with the same platform, the same remediation workflow, and the same agentic and human testing model.
Risk-Based Prioritization
Device-level findings are prioritized by exploitability, exposure, and potential impact, not just severity scores, so teams close the gaps attackers would actually use.
Owner-Routed Remediation
Validated findings arrive with exploit evidence, reproduction detail, and clear guidance, routed to the firmware, engineering, infrastructure, or security owner who can fix them.
Managed, Continuous Testing
Our team manages execution, validation, guidance, and retesting, so you run a continuous IoT testing program without building specialized hardware and firmware expertise in-house.
From The Device To Your Network.
Every finding is validated to determine real-world exploitability and impact. We confirm which firmware weaknesses, insecure protocols, and exposed interfaces can be abused to take control of a device, extract data, or pivot into your broader network.
- Device01
Analyze the firmware
Examine firmware images, bootloaders, update mechanisms, and embedded services for hardcoded credentials and insecure storage.
- Exposed Interface02
Probe protocols and interfaces
Test communication protocols, wireless exposure, debug interfaces, cloud APIs, and companion apps, then attempt the paths an attacker would use.
- Device Compromise03
Chain weaknesses together
Show how device-level weaknesses combine into a realistic attack path, instead of relying on scanner severity alone.
- Network Impact04
Measure what access means
Understand how a compromised device could enable lateral movement, operational disruption, or data exposure across your environment.
How IoT Testing Works Inside TrollEye.
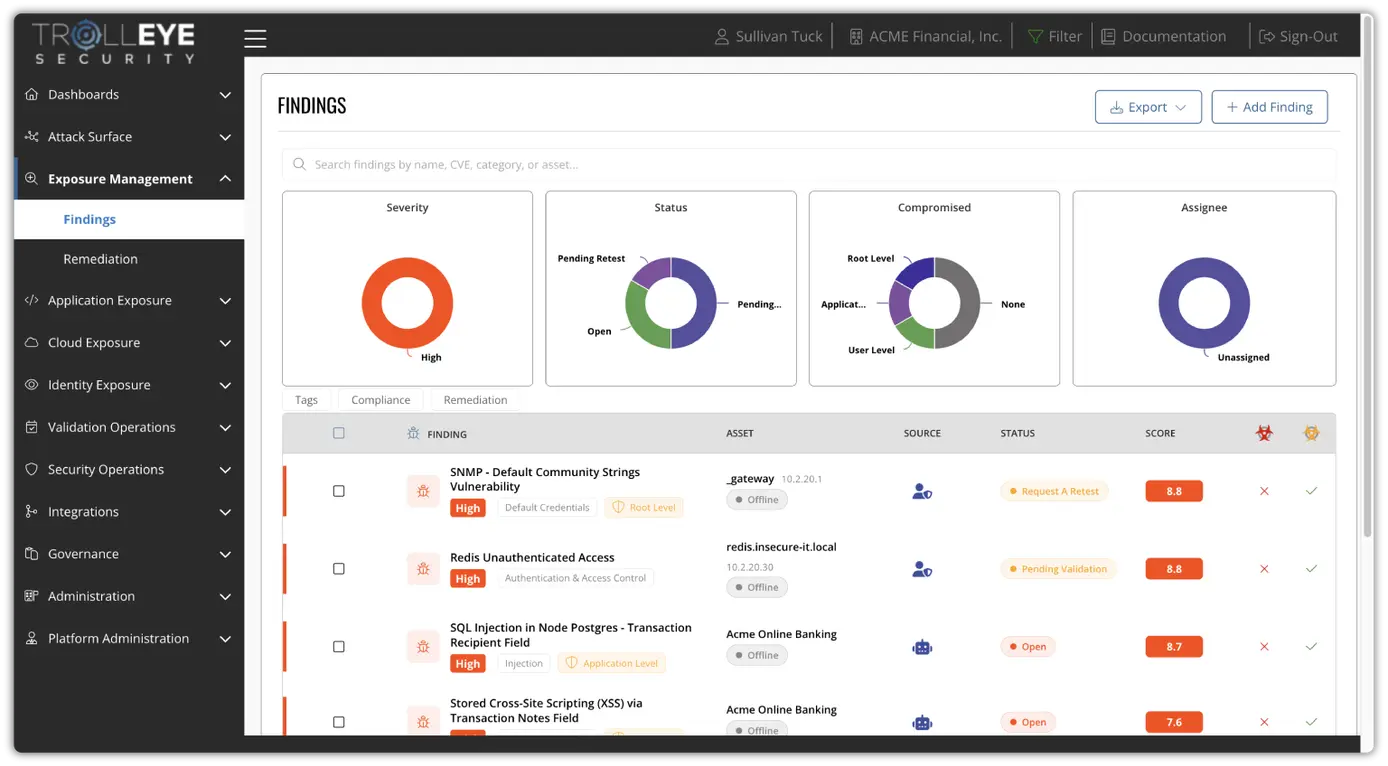
IoT findings don't arrive as a PDF. They land in the same TrollEye platform as every other PTaaS test, where your team can see what was found, what is exploitable, who owns the fix, and when it has been retested.
Device Inventory
Every device, firmware version, exposed service, and supporting integration in scope is tracked in one inventory, so your connected footprint stays current as deployments grow.
- Devices, services, and integrations in one view
- Unmanaged and forgotten devices surfaced
- Coverage that adapts as deployments change

Validated Findings
Each IoT finding arrives with exploit evidence, reproduction detail, and real-world risk context, so teams see what can actually be exploited instead of scanner severity alone.
- Exploitability confirmed by our testers
- Risk-ranked by exposure and impact
- Evidence attached to every finding
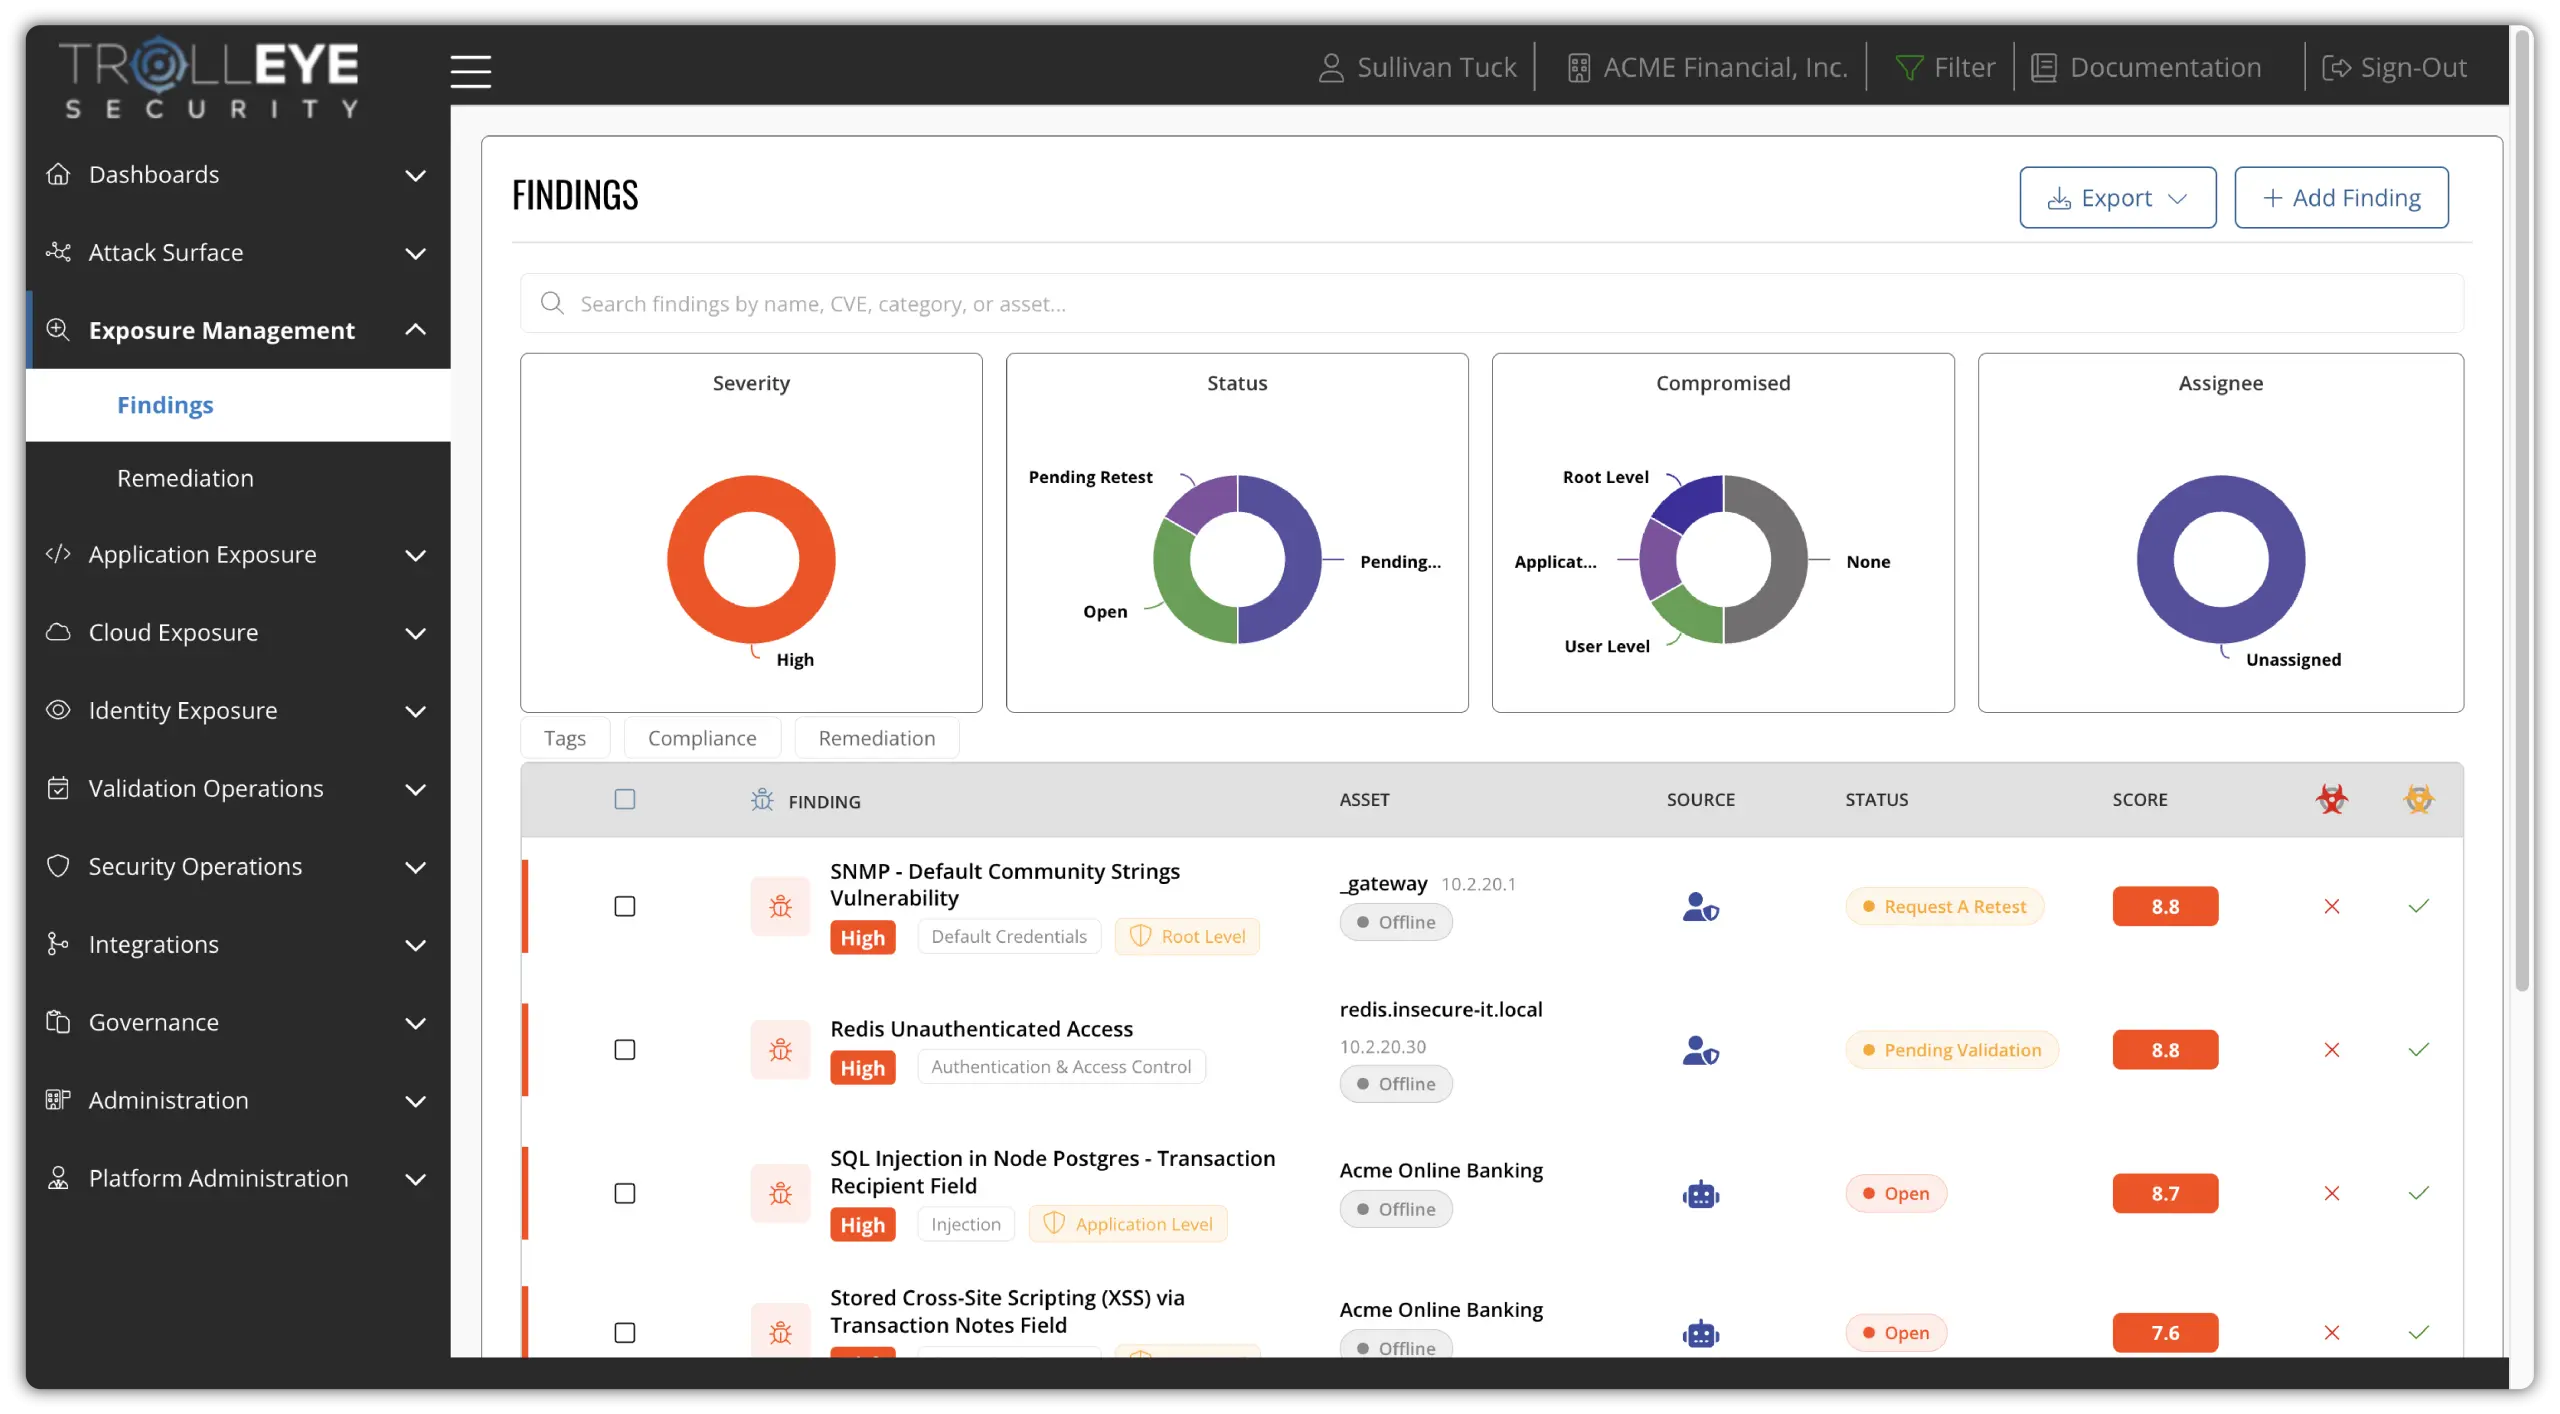
Remediation
Findings route to the firmware, engineering, infrastructure, or security owner responsible for the fix, with clear remediation guidance and progress tracked centrally.
- Role-based task distribution
- Step-by-step remediation guidance
- No validated exposure lost in a backlog
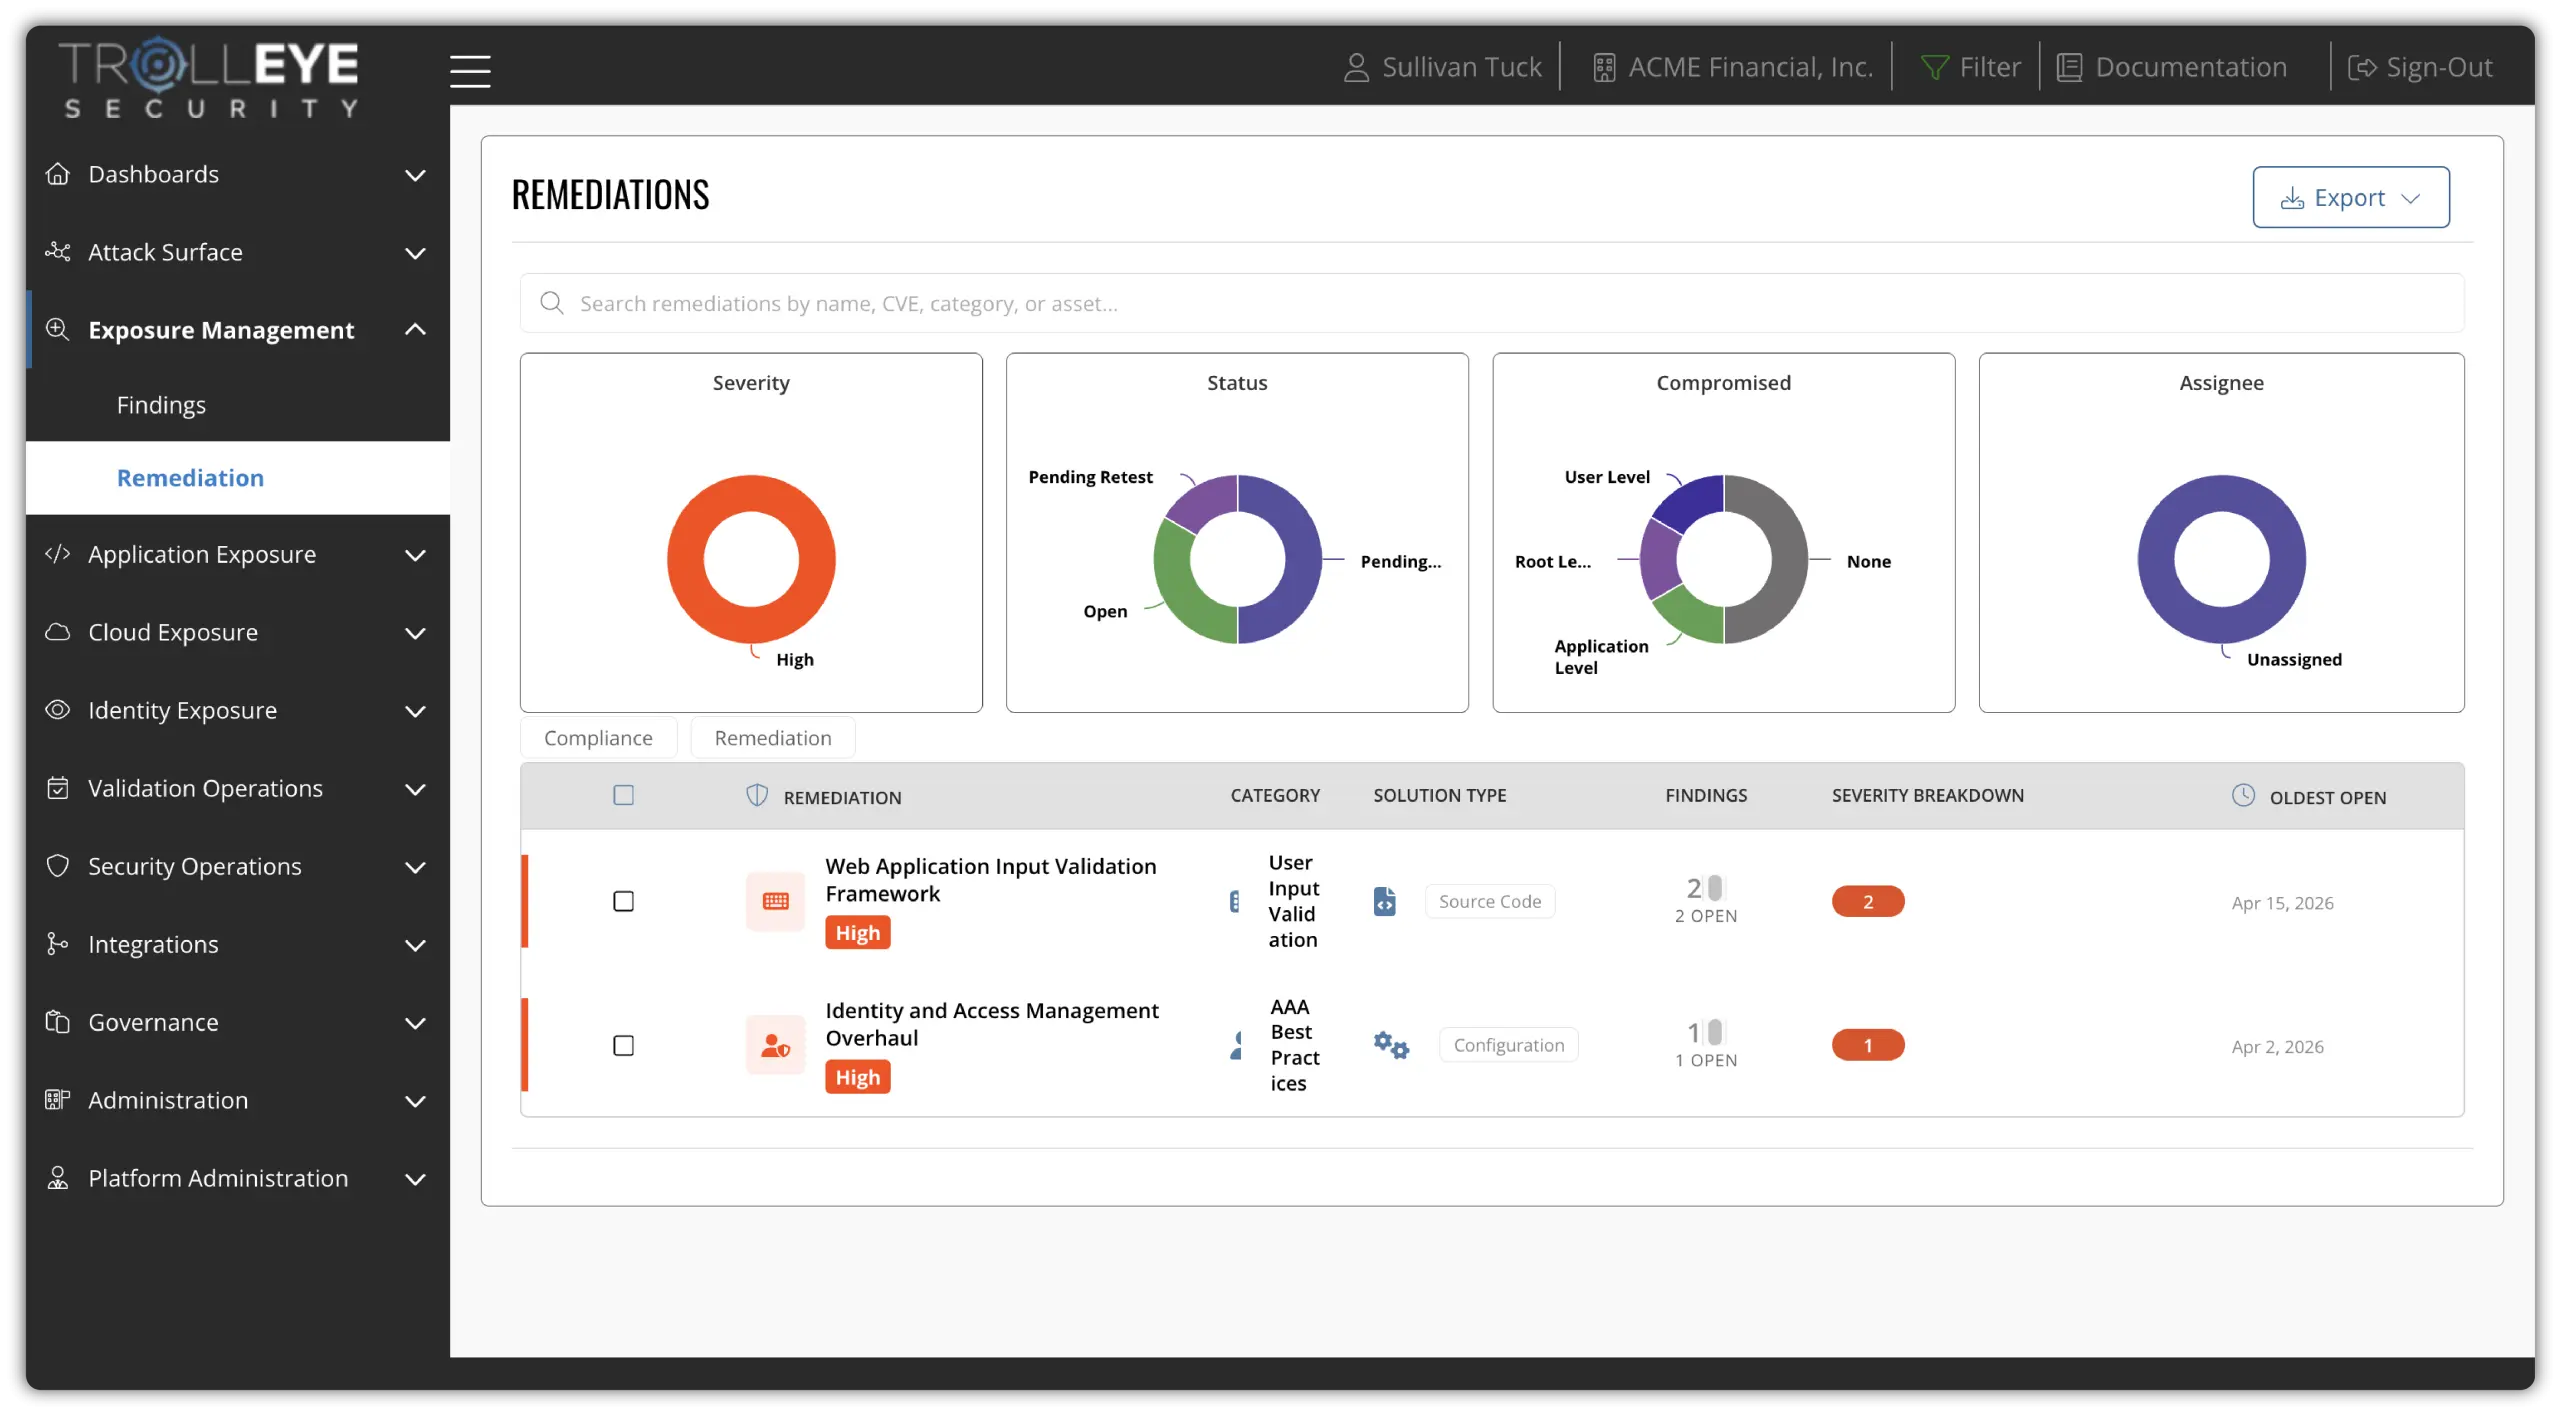
Retesting
Once a fix is in, request a retest directly from the platform and our team confirms whether the device-level exposure has been closed.
- Retests requested in one click
- Status updated on every finding
- Closure confirmed by the same team that found it
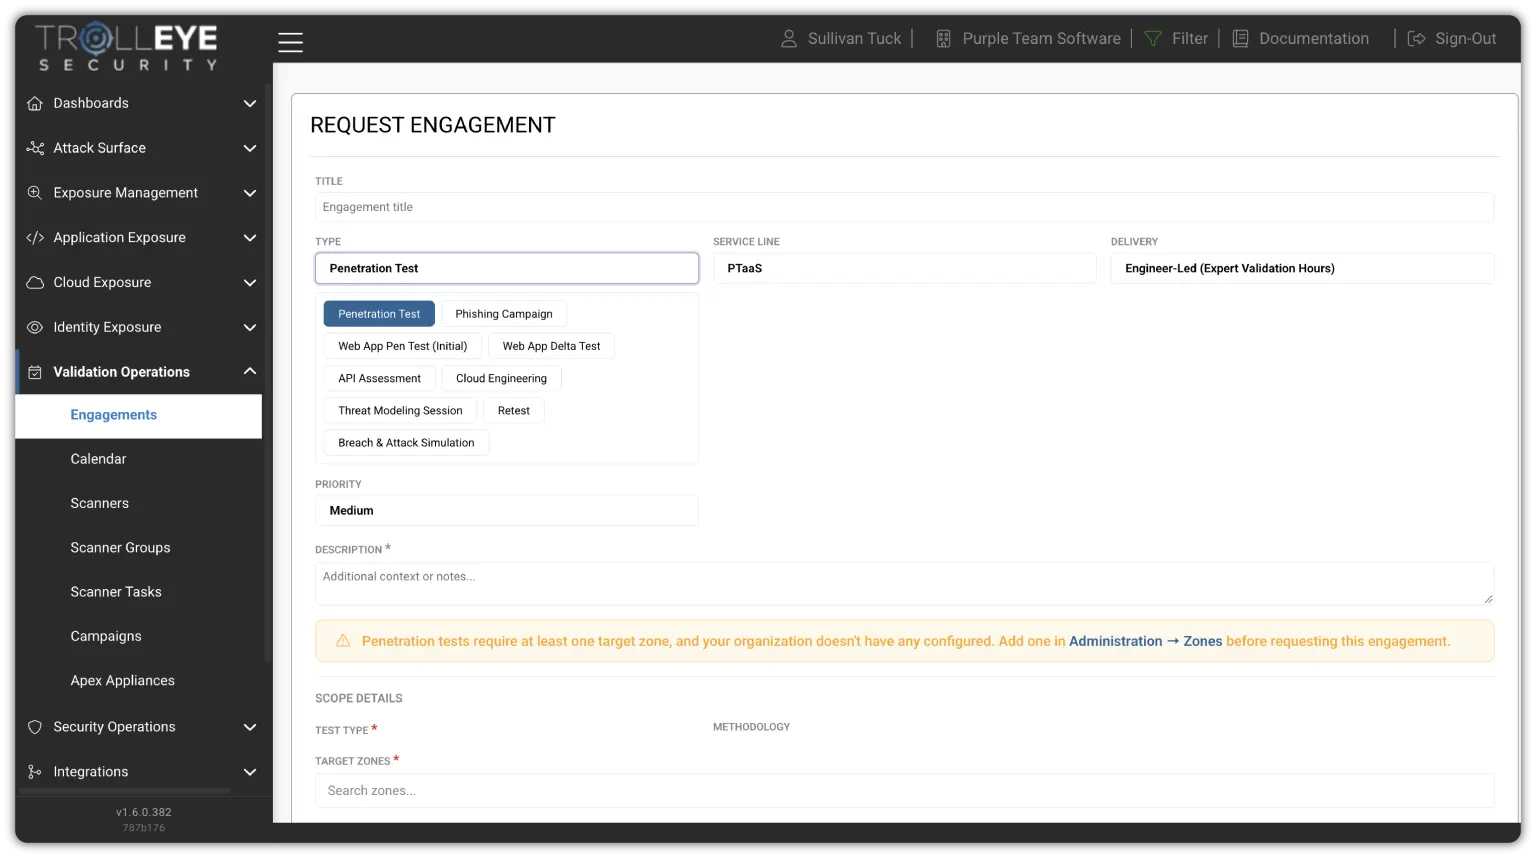
Reporting
Executive and technical reporting shows how your IoT exposure trends over time, alongside every other test in your PTaaS program.
- Executive-ready summaries
- Technical detail for engineering teams
- IoT results in the context of all PTaaS testing
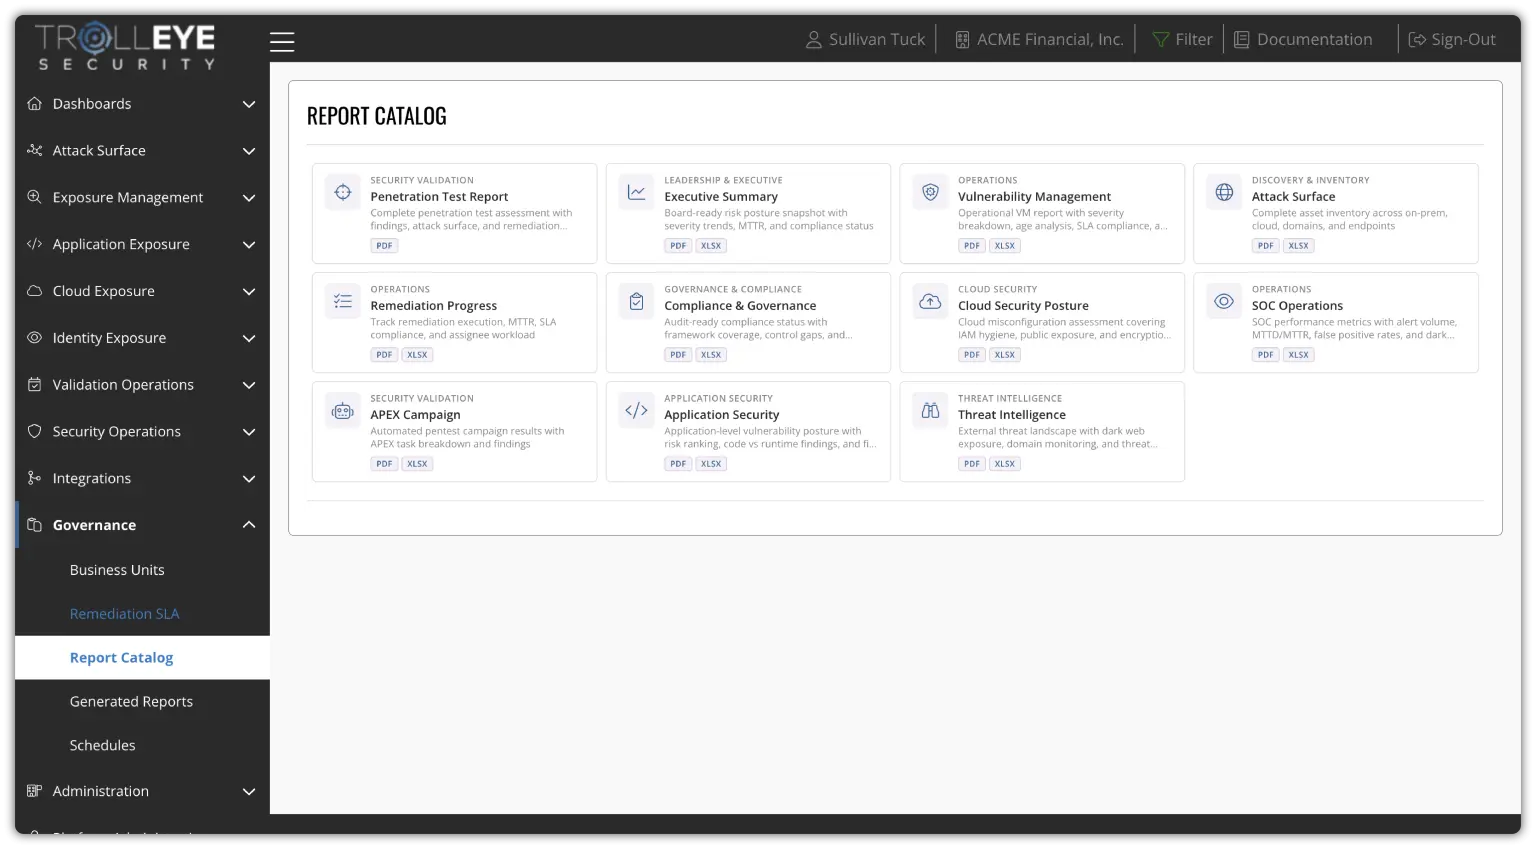

Validating Your Connected Devices Within CTEM.
IoT penetration testing is a core validation component of our Continuous Threat Exposure Management (CTEM) solution. By continuously identifying and validating exploitable weaknesses across connected devices, it shows which device-level exposures present real risk and where remediation effort should be focused.
Most organizations don’t have a visibility problem. They have an execution problem. IoT testing powers the Discovery, Validation, and Mobilization stages for your connected devices, while Scoping and Prioritization run across your entire attack surface in the same TrollEye platform.
Scoping
Define the device models, deployments, integrations, and business priorities IoT testing needs to cover.
Platform sets device scope IOT 02Discovery
Testing identifies device models, firmware versions, exposed services, backend integrations, and communication pathways.
IoT testing maps the ecosystem 03Prioritization
IoT findings are ranked by exploitability, threat context, and business impact.
Platform adds attacker context IOT CORE 04Validation
Automated and human testing proves which device-level exposures are actually exploitable and reachable.
IoT testing proves real risk IOT 05Mobilization
Validated findings route to the right owners, get tracked to closure, and are retested.
IoT testing drives the fix- Attack Surface Visibility
- Network Security
- Cloud Security
- Remediation Workflows
- Continuous Reporting
Questions About IoT Device Penetration Testing
How IoT device penetration testing works, what it covers, and how it fits into PTaaS and your CTEM program.
01 What is IoT device penetration testing?
IoT device penetration testing simulates real attacker behavior against connected devices and the firmware, protocols, cloud APIs, and mobile apps that support them. It confirms which weaknesses can actually be exploited to compromise a device, extract data, or move deeper into your environment.
02 What types of IoT devices do you test?
We test industrial control systems and OT, smart building and facilities devices, healthcare and medical IoT, consumer and embedded devices, and network and edge devices. Testing adapts to each device’s function, connectivity, and exposure.
03 Do you test more than the device itself?
Yes. We test the full ecosystem around the device, including update mechanisms, gateways, mobile apps, cloud APIs, identity controls, and network segmentation, because a vulnerable device is often a foothold into the broader network.
04 How are IoT findings prioritized?
Every finding is validated for real-world exploitability, then ranked by threat context, business impact, and its role in enabling compromise or lateral movement, not by scanner severity alone.
05 How does IoT penetration testing fit into PTaaS and CTEM?
IoT testing is delivered through PTaaS, so findings share one platform and one remediation workflow with the rest of your testing. Within CTEM, it powers the Discovery, Validation, and Mobilization stages for your connected devices.
06 How often should IoT devices be tested?
Continuously. Firmware updates, new integrations, and expanded deployments keep reshaping risk. How often expert manual testing runs depends on how you use your service credits, so you can focus it on the devices and changes that matter most.
07 What happens after IoT findings are remediated?
Findings are routed to the right owners with exploit evidence and remediation guidance. Once a fix is in, we retest to confirm the issue is resolved and hasn’t been reintroduced through firmware or configuration changes.
See how IoT, external, internal, and network testing run together in one platform and one remediation process.
Go On The Offensive. Start Securing Your IoT Devices Today.
You don’t know how secure your devices are until you put them to the test. Forward-thinking security teams are turning to continuous IoT penetration testing, delivered through Penetration Testing as a Service (PTaaS), to reduce their exposure to attacks, maintain regulatory compliance, and stay ahead of attackers. See how IoT testing fits into a complete CTEM program.
- 01Continuous testing across the device ecosystem
- 02Human validation of real device attack paths
- 03Role-based remediation workflows
- 04Retesting that confirms every fix