More findings won’t protect patients. Fixed exposures will.
Fewer paths to PHI, faster remediation, and proof leadership can see, whether you run critical hospital systems around the clock or ship health tech every week.
Experience across the systems modern care runs on.
Healthcare risk doesn’t live in one system. It lives in the EHR, imaging and connected devices, patient portals and APIs, and the identity and network paths between them, from hospital systems that can’t go down to health tech teams shipping every week. That’s where we work.
Four places healthcare gets exposed. Four outcomes we deliver.
Each area runs through the TrollEye platform, from discovery and agentic and human testing to owners, deadlines, and retesting. Select an area to see where risk is going down.
Paths to PHI get closed
The EHR is the crown jewel, and attackers rarely go at it head-on. They come in through identity, infrastructure, and connected clinical services.
Unpatchable systems get protected
Imaging systems and medical devices run legacy software on vendor timelines and can’t be rebooted on a Tuesday afternoon.
Releases stop shipping exposures
Portals, APIs, and mobile apps change constantly, so an annual pen test is stale before the next sprint closes.
Care stays online
Ransomware needs exposed remote access, reused credentials, and room to move. In healthcare, downtime means diverted ambulances and delayed procedures.
The evidence auditors ask for. Kept current all year.
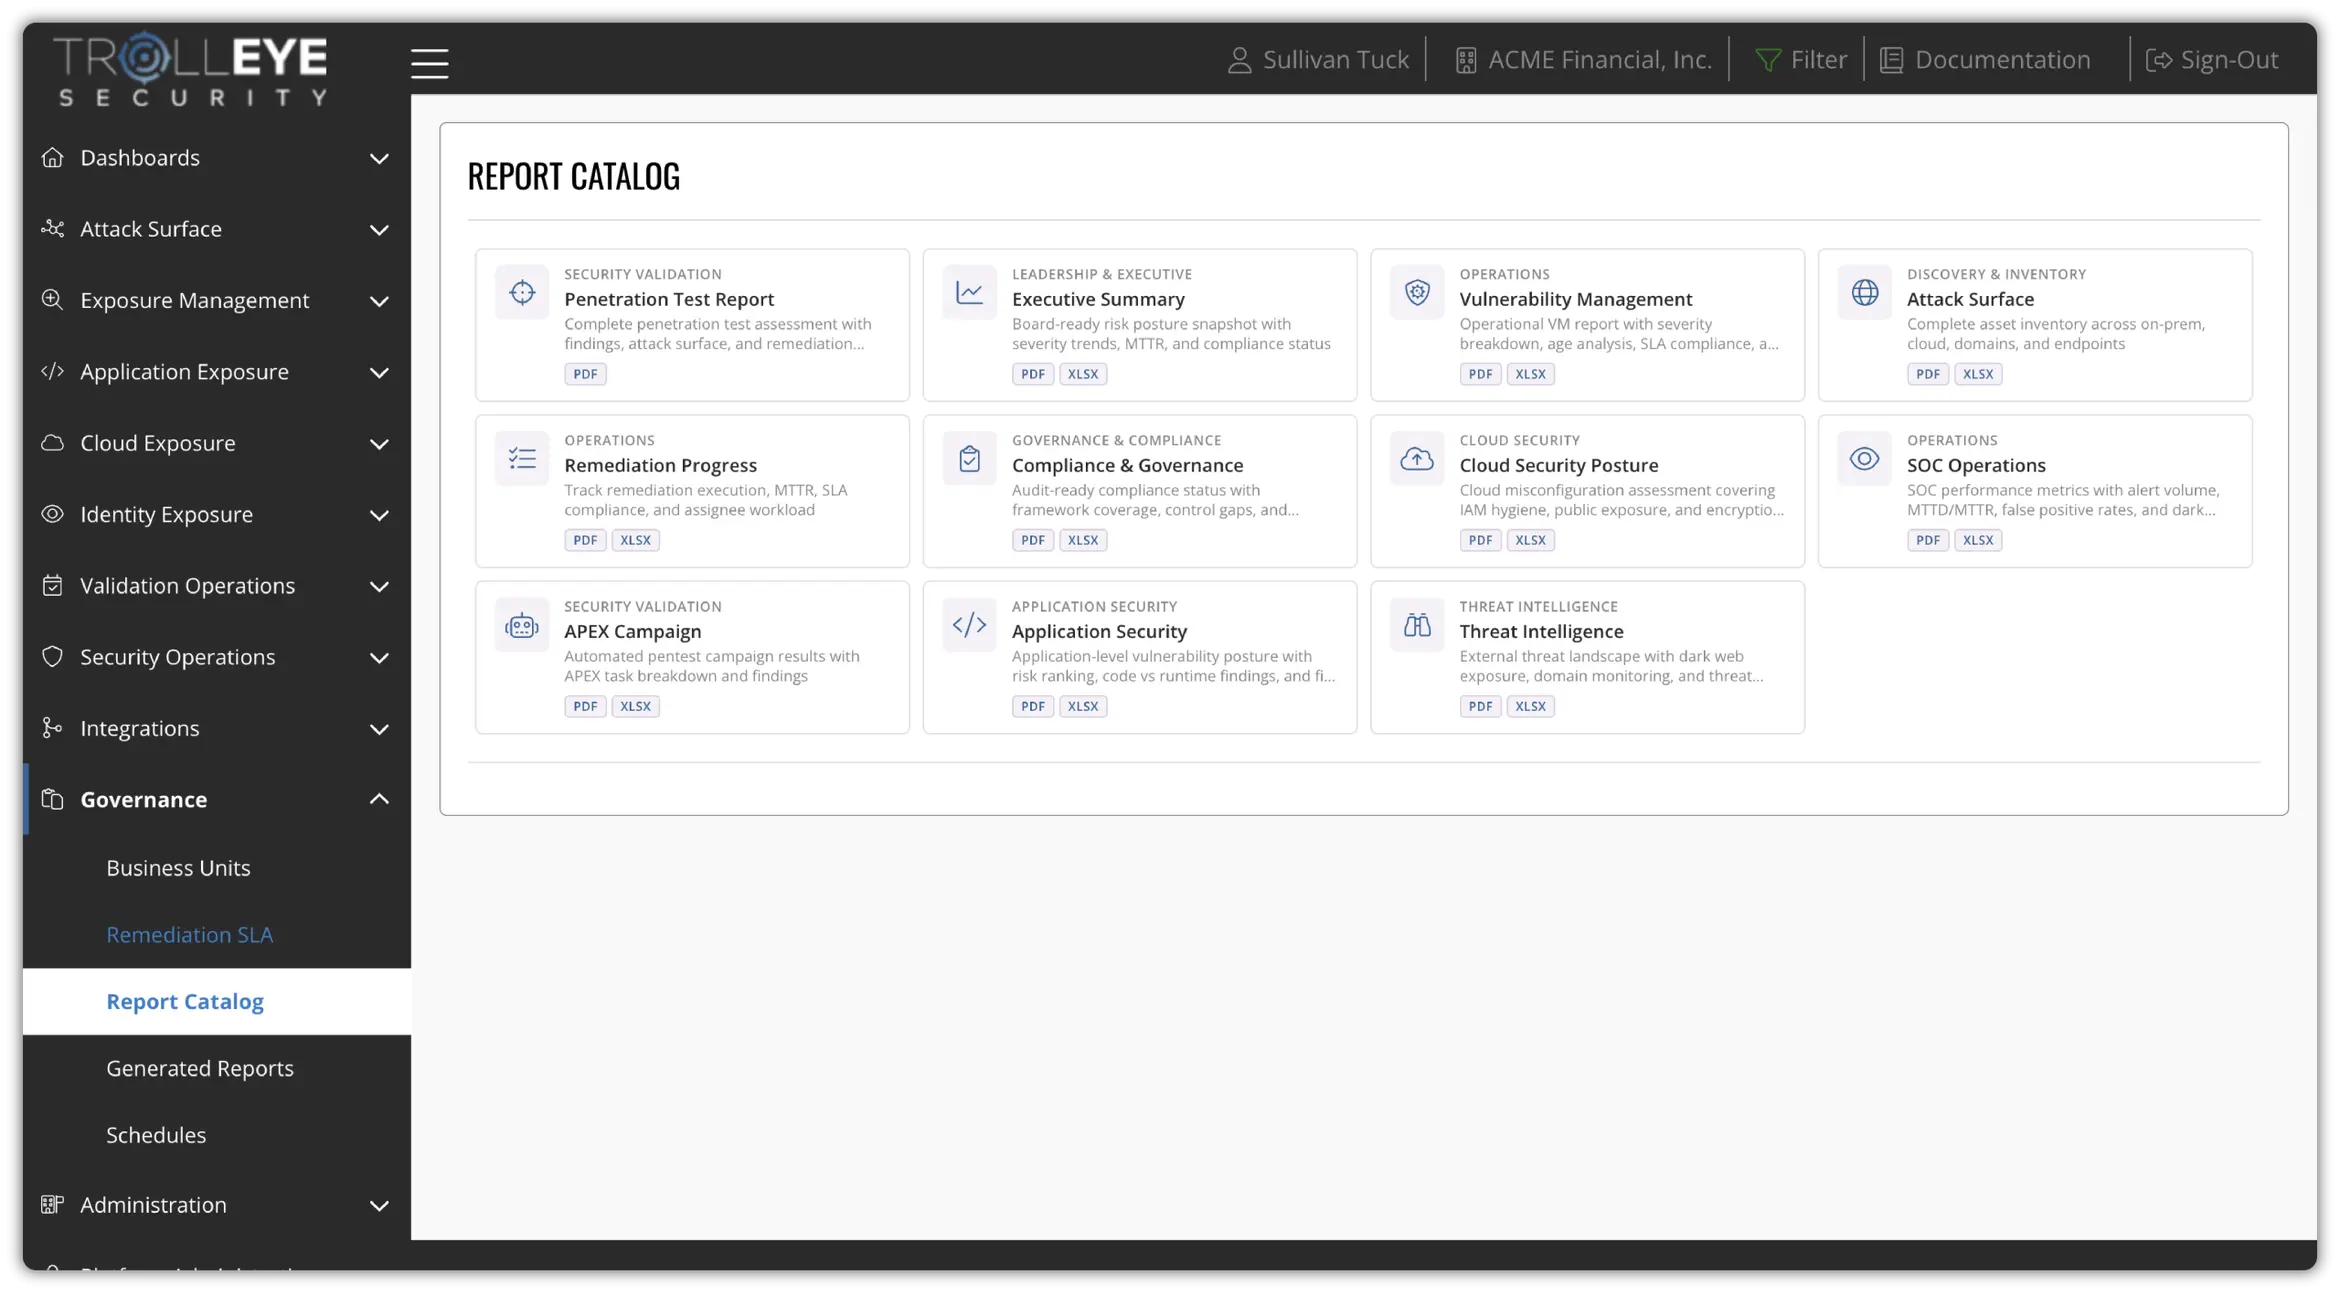
Auditors, partners, and covered entities look for testing, validated findings, clear ownership, and proof that issues were fixed. TrollEye keeps that record in one place, all year.
- HIPAASecurity Rule
- HITRUSTCSF
- HHS 405(d)HICP
- SOC 2Type II
- PCI DSSv4.0
TrollEye provides testing evidence and remediation records that support these requirements. It doesn’t replace your compliance program or an auditor’s judgment.
- Testing history for every assessment
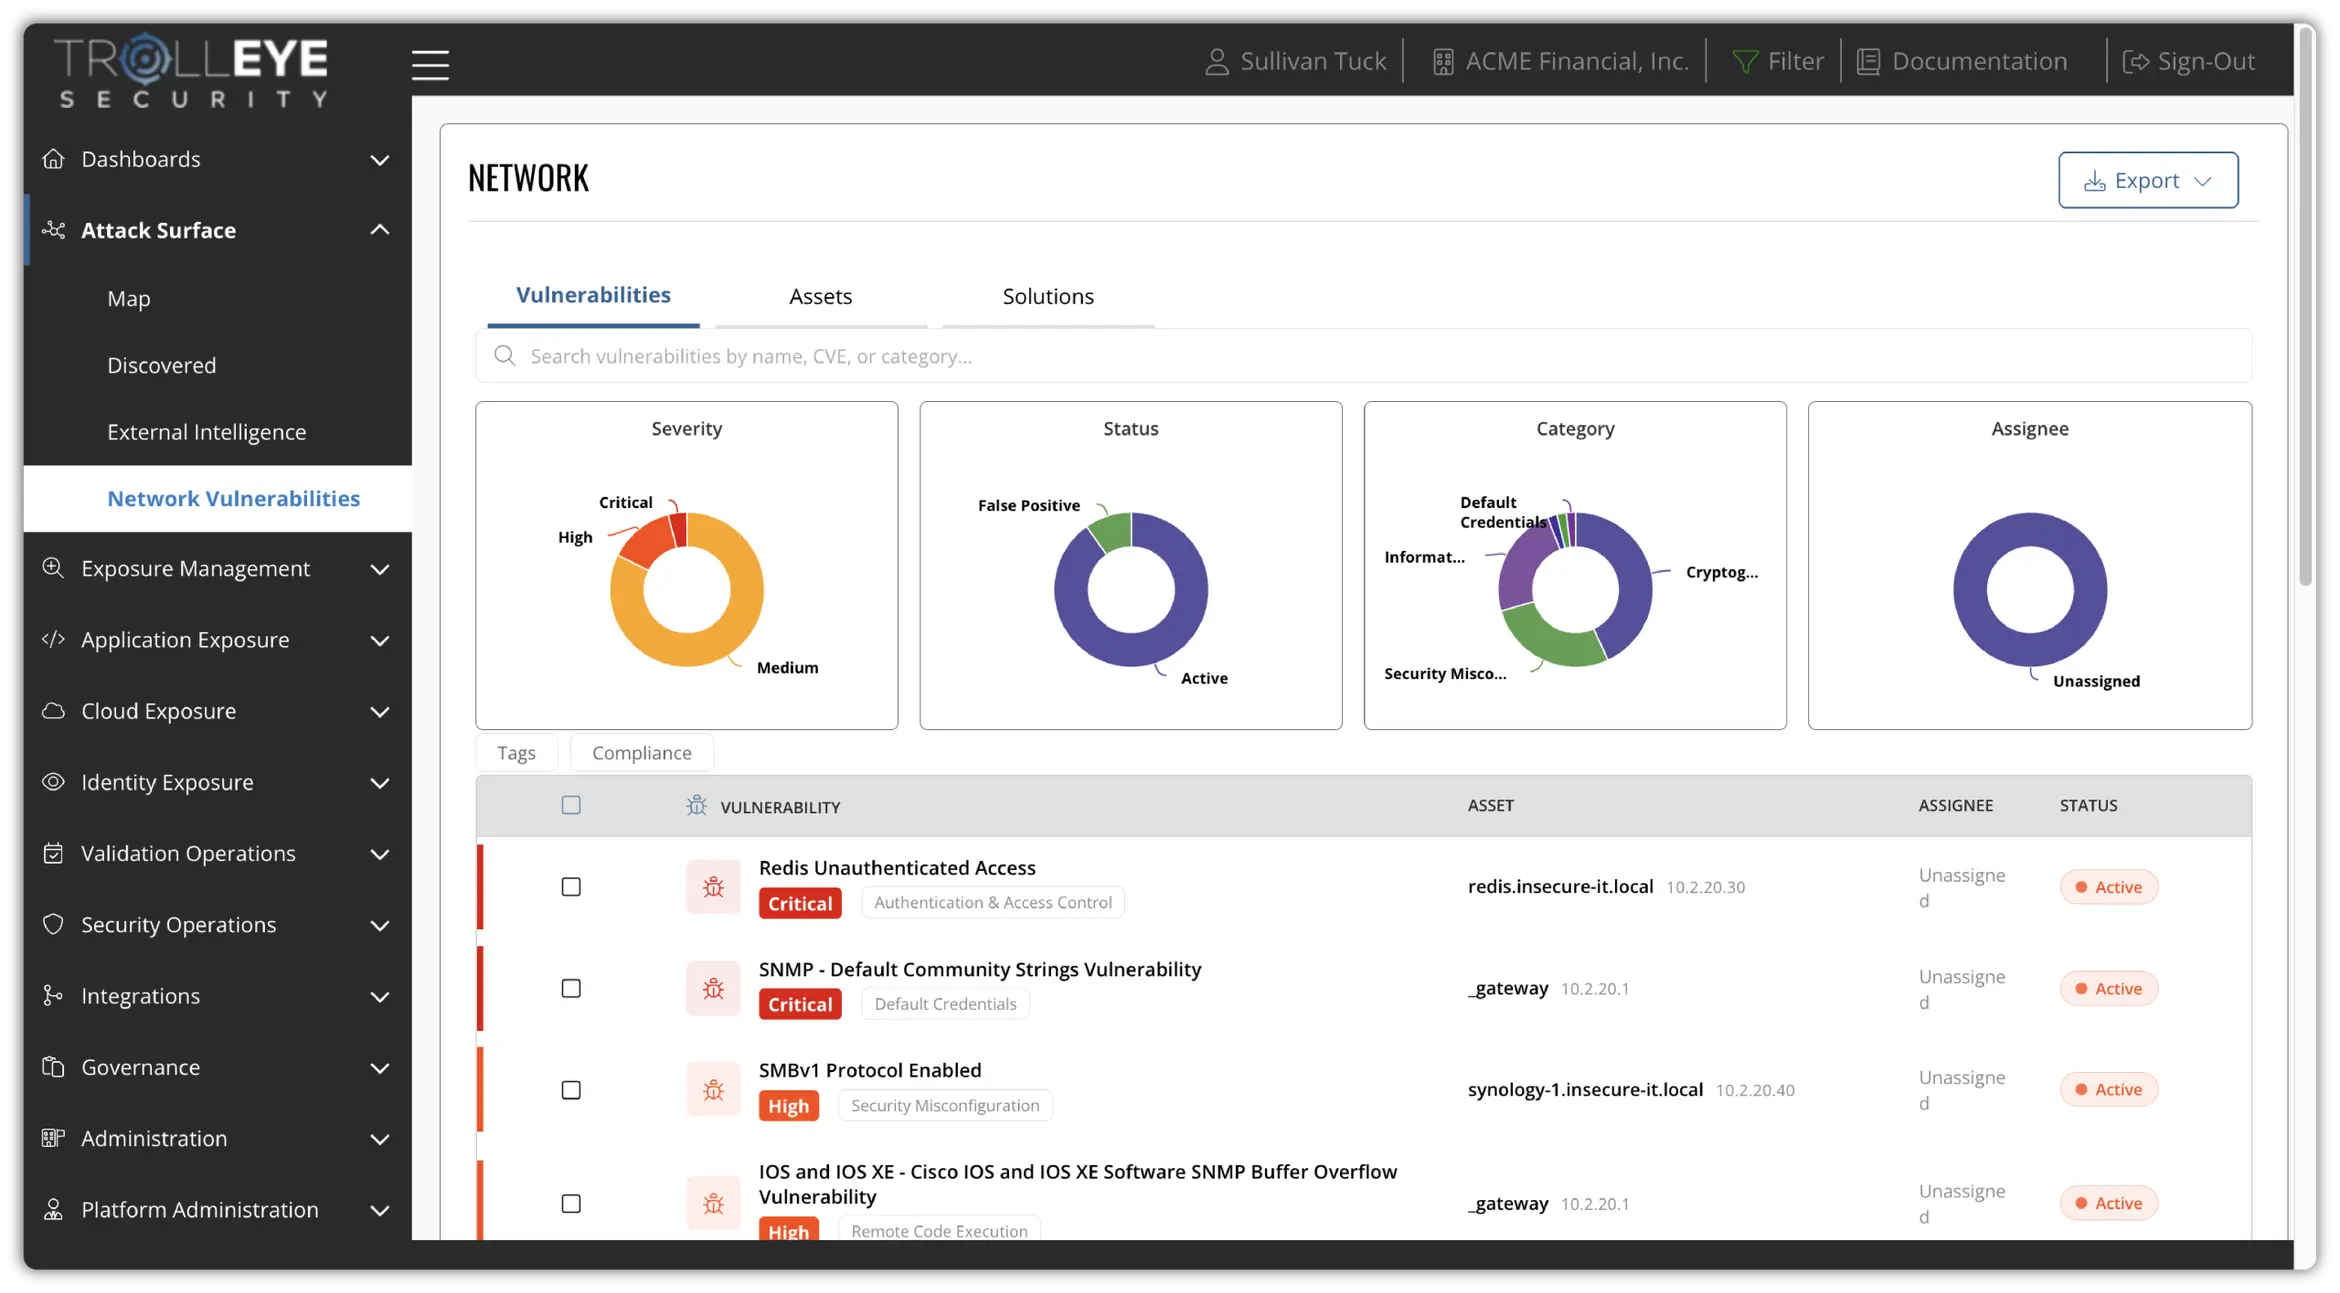
- Validated findings ranked by clinical criticality
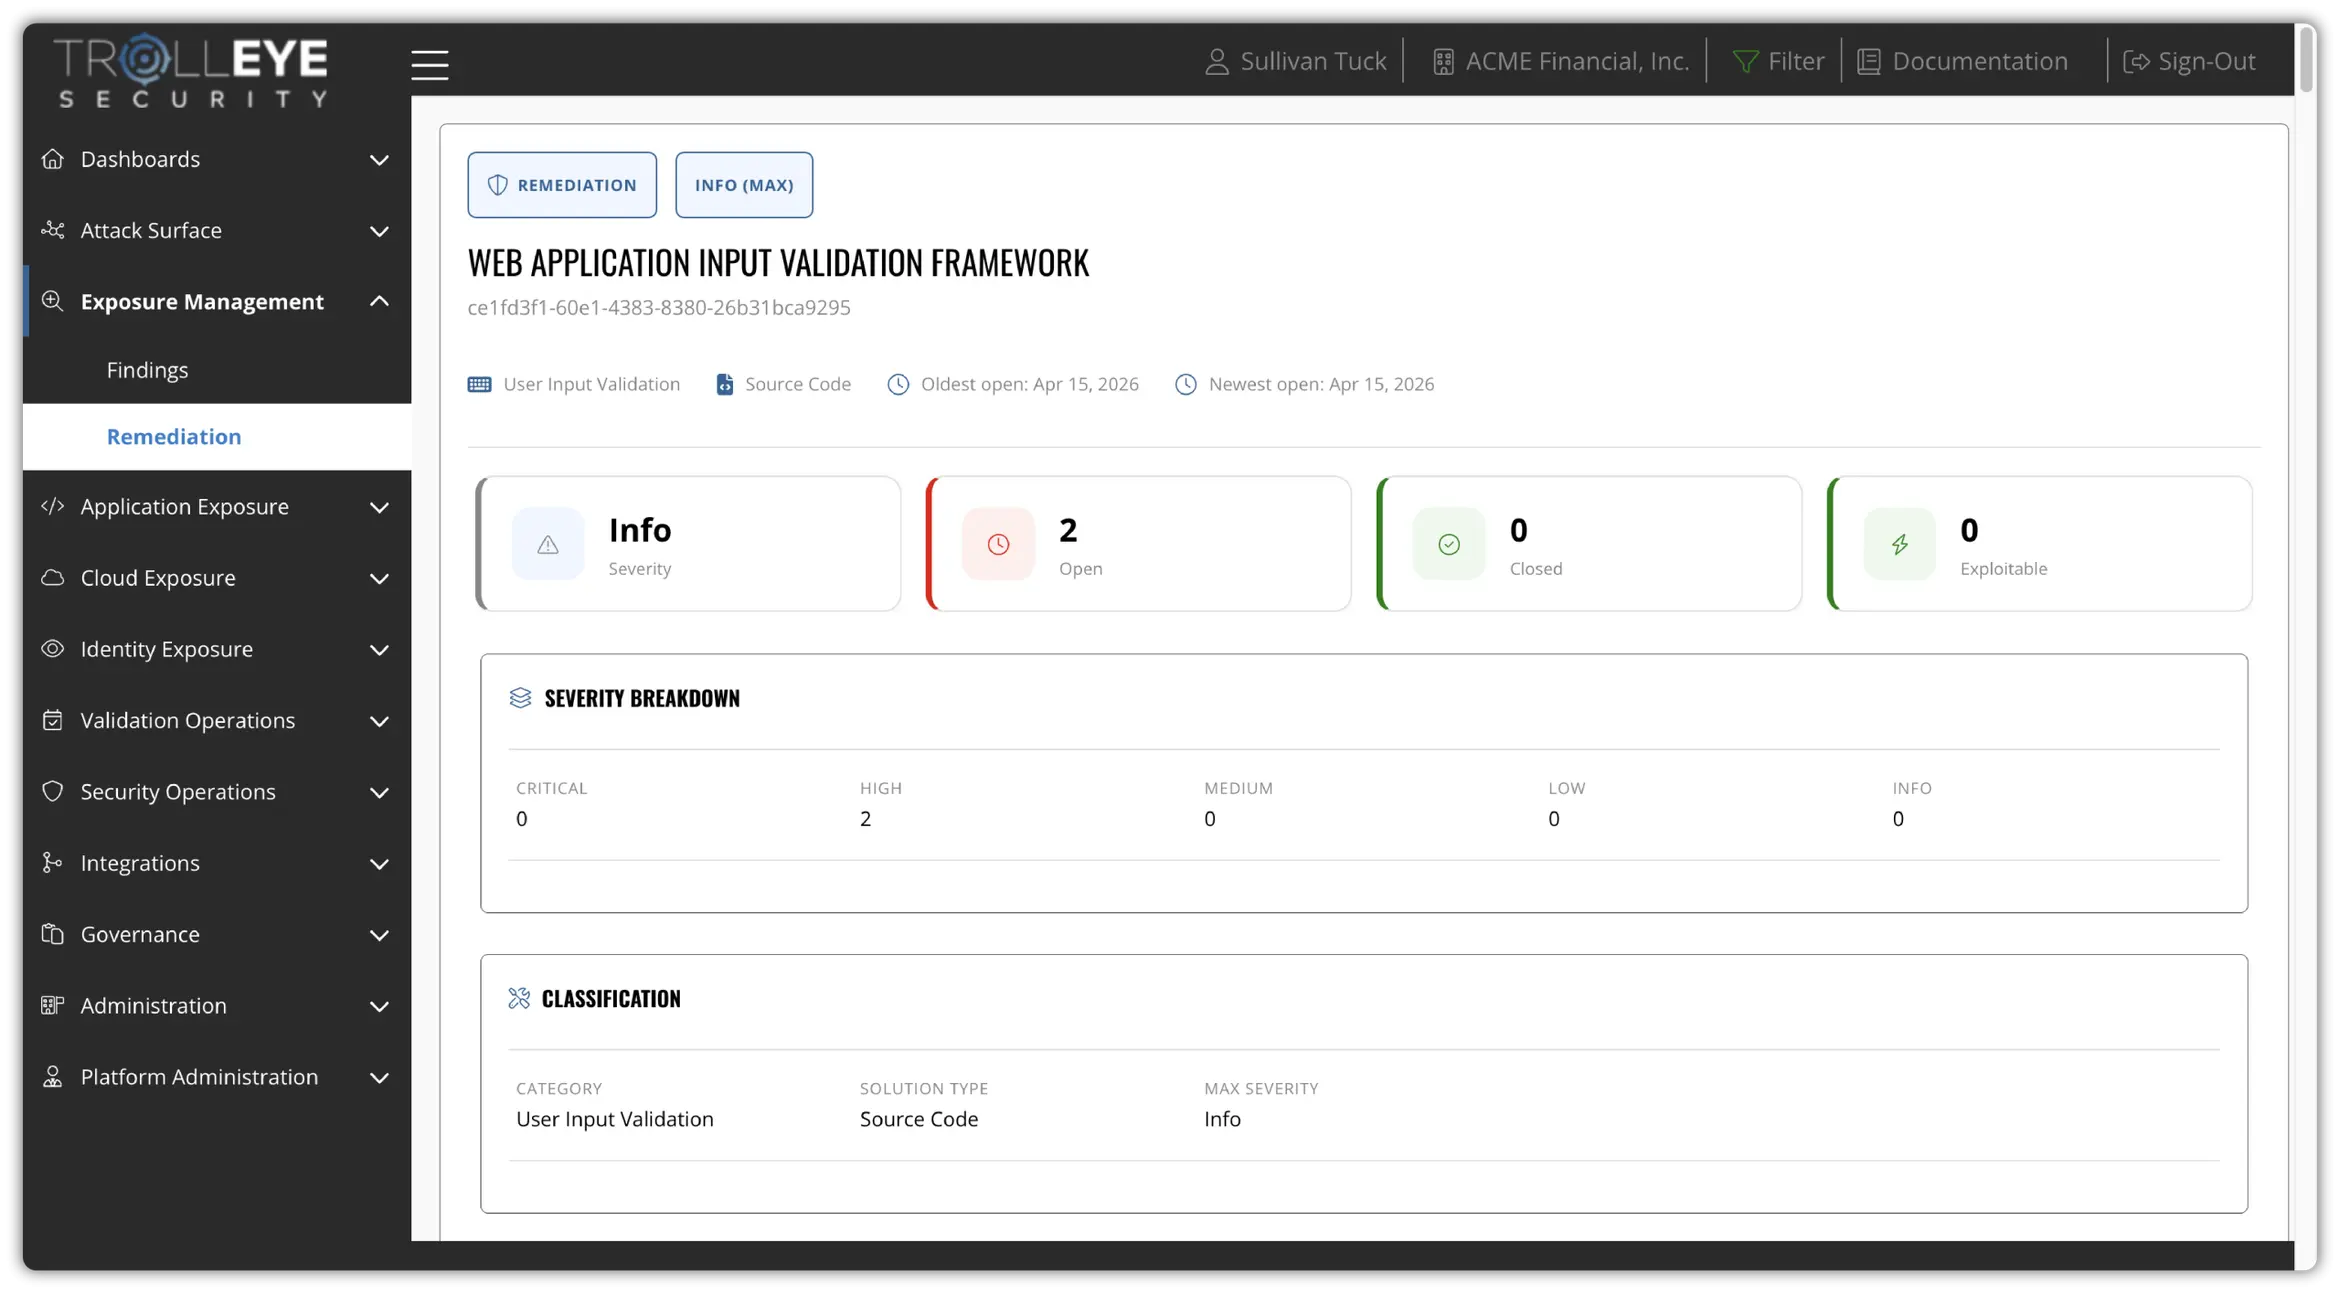
- Owners held to remediation SLAs
- Retest records that confirm closure
- Your side of every EHR, payer, and partner connection, tested
CTEM, built around how care is delivered.
Five stages that run continuously, not once a year.
Scoping
Start with what patients and auditors care aboutDiscovery
Find every path to PHIPrioritization
Rank by clinical impactValidation
Prove what’s exploitableMobilization
Drive it to closureSee How TrollEye Protects the Paths to PHI
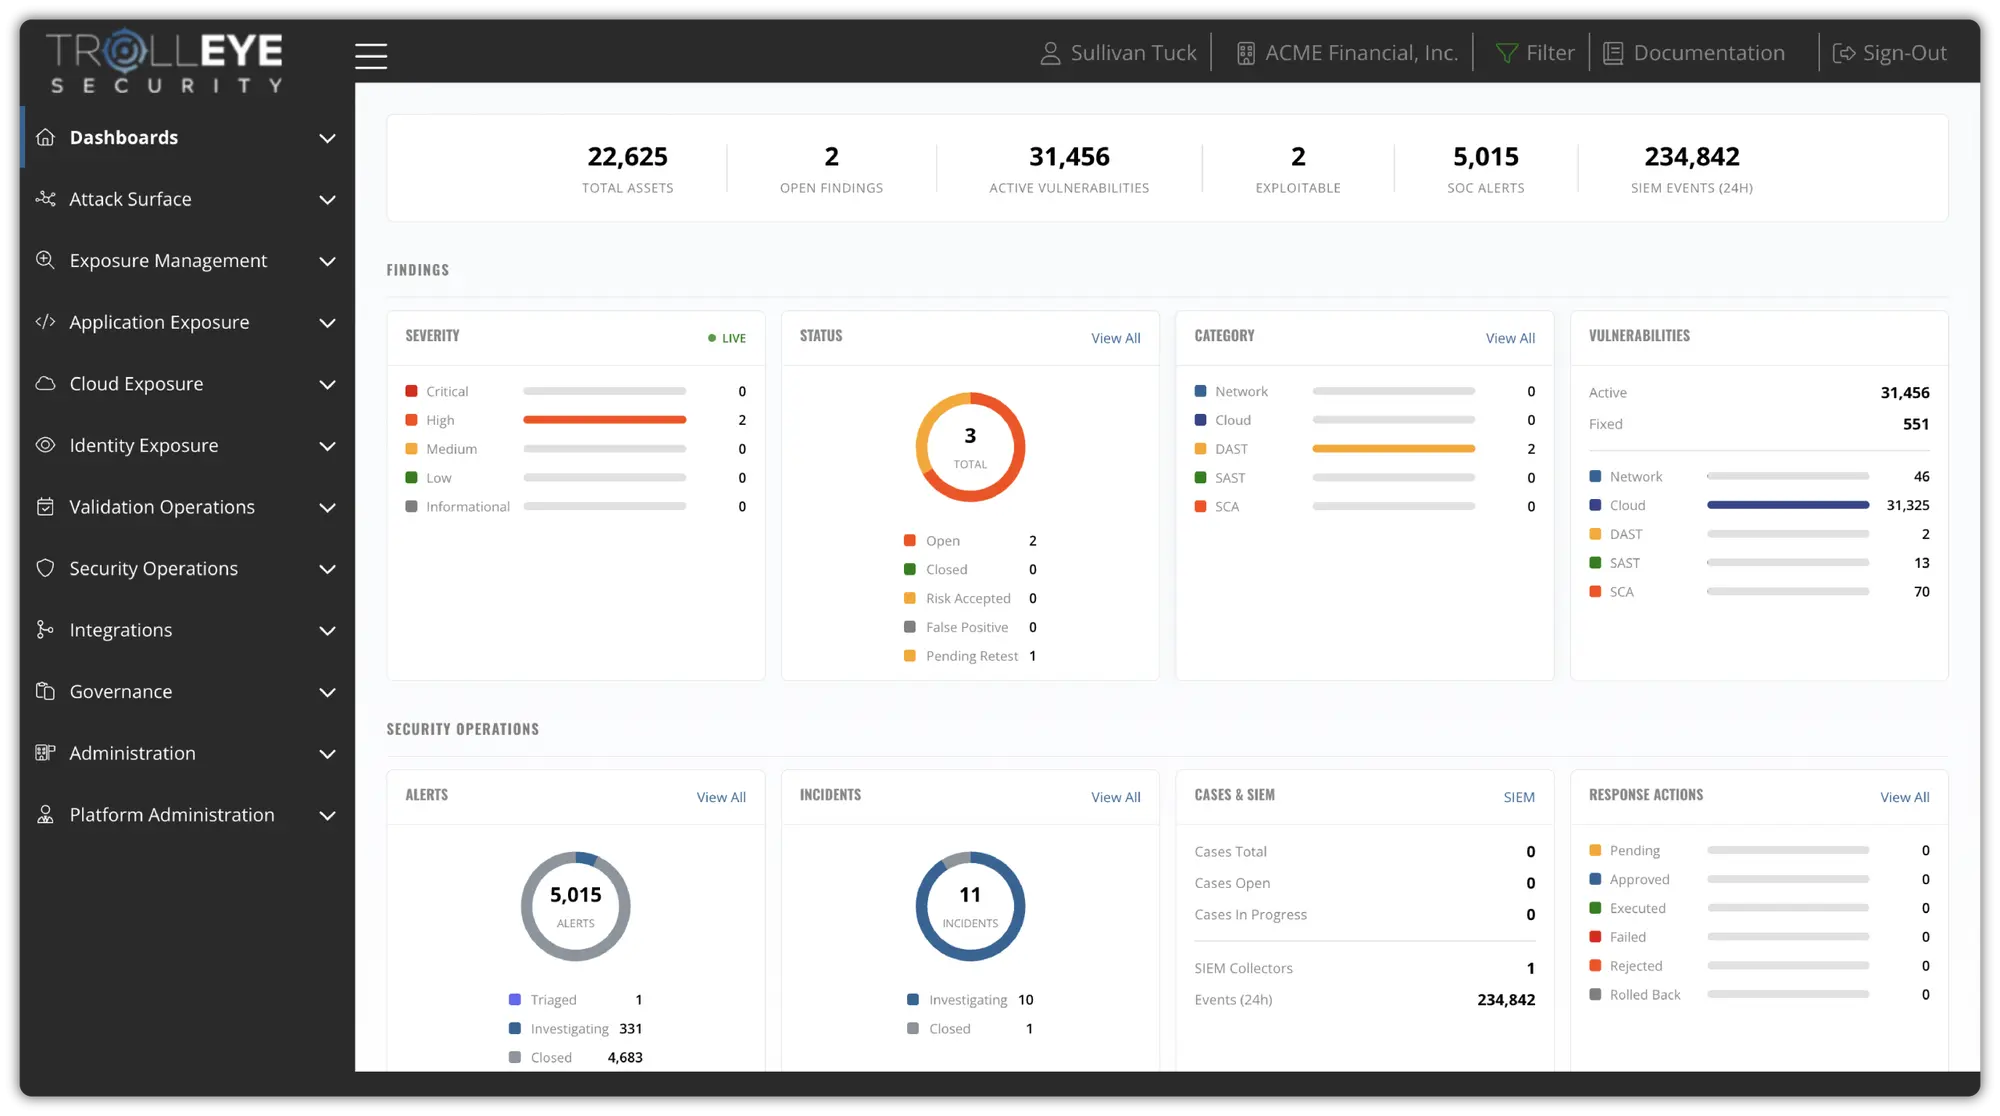
Choose a demo to see how audit readiness, validation, and remediation work inside the TrollEye platform.
Faster response. Faster remediation.
CorroHealth’s Enterprise CISO needed practitioners, speed, and findings his teams could act on, not another big-box vendor.
Practitioners, speed, and findings teams can act on.
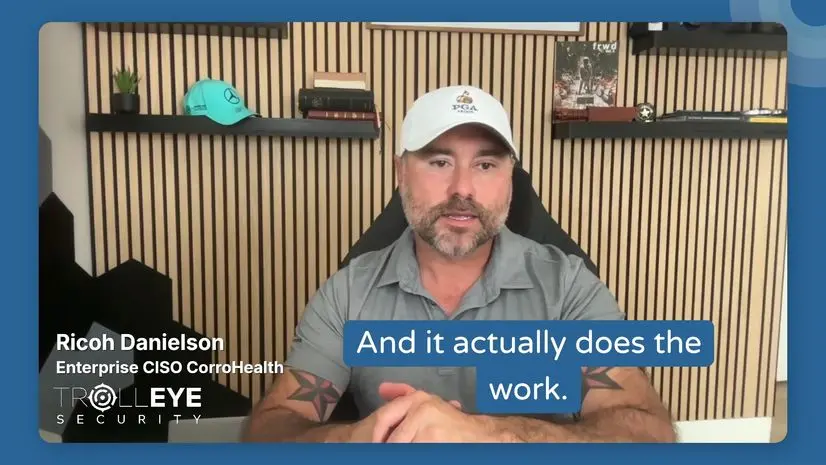
“My speed to respond and my speed to remediate have gone down dramatically.”
- Direct access to experienced security practitioners
- Responsive support built around the customer’s needs
- A long-term partnership, not a transactional vendor model
Questions About Securing Healthcare Organizations
A closer look at how TrollEye works for providers, health systems, and health tech companies: testing, HIPAA, clinical uptime, partner connections, and how it all fits your CTEM program.
01Does HIPAA require penetration testing?
The HIPAA Security Rule requires a risk analysis and regular technical evaluation of your safeguards. Penetration testing is one of the most direct ways to show those safeguards actually hold.
Read more in our article, Does HIPAA Require Penetration Testing?
02Can testing run without disrupting clinical operations?
Yes. Testing is scoped and scheduled around clinical and operational windows, and remediation is weighed against availability and patient care, not just severity.
03Will this help with audits and customer security reviews?
TrollEye doesn’t replace your compliance program, but it gives you the evidence auditors and partners ask for: testing history, validated findings, ownership, remediation SLAs, and retest records, kept current all year.
That record supports HIPAA, HITRUST, and SOC 2 requirements.
04How does this help with third-party risk?
Vendor assessments tell you how a partner manages its own security. TrollEye tests your side of each connection: the integrations, APIs, access paths, and configurations you control.
Learn more in our CTEM vs. TPRM guide.
05Can our in-house team use the platform?
Yes. In-house security and red teams can use the TrollEye platform themselves, so their findings sit alongside ours with the same validation, ownership, SLAs, and retesting.
06How does this fit into a CTEM program?
TrollEye applies each CTEM stage to your organization: scoping the systems that hold and move PHI, discovering every access path across the EHR, portals, APIs, and identity, prioritizing by clinical criticality and attack path, validating what is actually exploitable and reachable, and mobilizing owners to close it.
Explore audit readiness, continuous testing, validation, and remediation before starting your evaluation.
Your next audit will ask what you fixed. Have the answer.
See how TrollEye validates what matters across your clinical and patient-facing systems, and tracks every fix to closure.