TrollEye Security

Attack Surface Management

PART OF PTAASPenetration Testing as a Service→

Attack Surface Management. Manage Exposure, Not Inventory.

Our attack surface management continuously discovers assets across your external footprint, internal networks, cloud environments, and on-prem infrastructure, including the shadow IT your team doesn’t know exists.

It is the discovery engine of our PTaaS solution, so every discovered asset feeds the same platform, the same testing scope, and the same remediation process, moving from discovered to prioritized, validated, and fixed instead of sitting in another inventory.
Continuous Discovery Shadow IT Exploitability Context Feeds PTaaS Testing
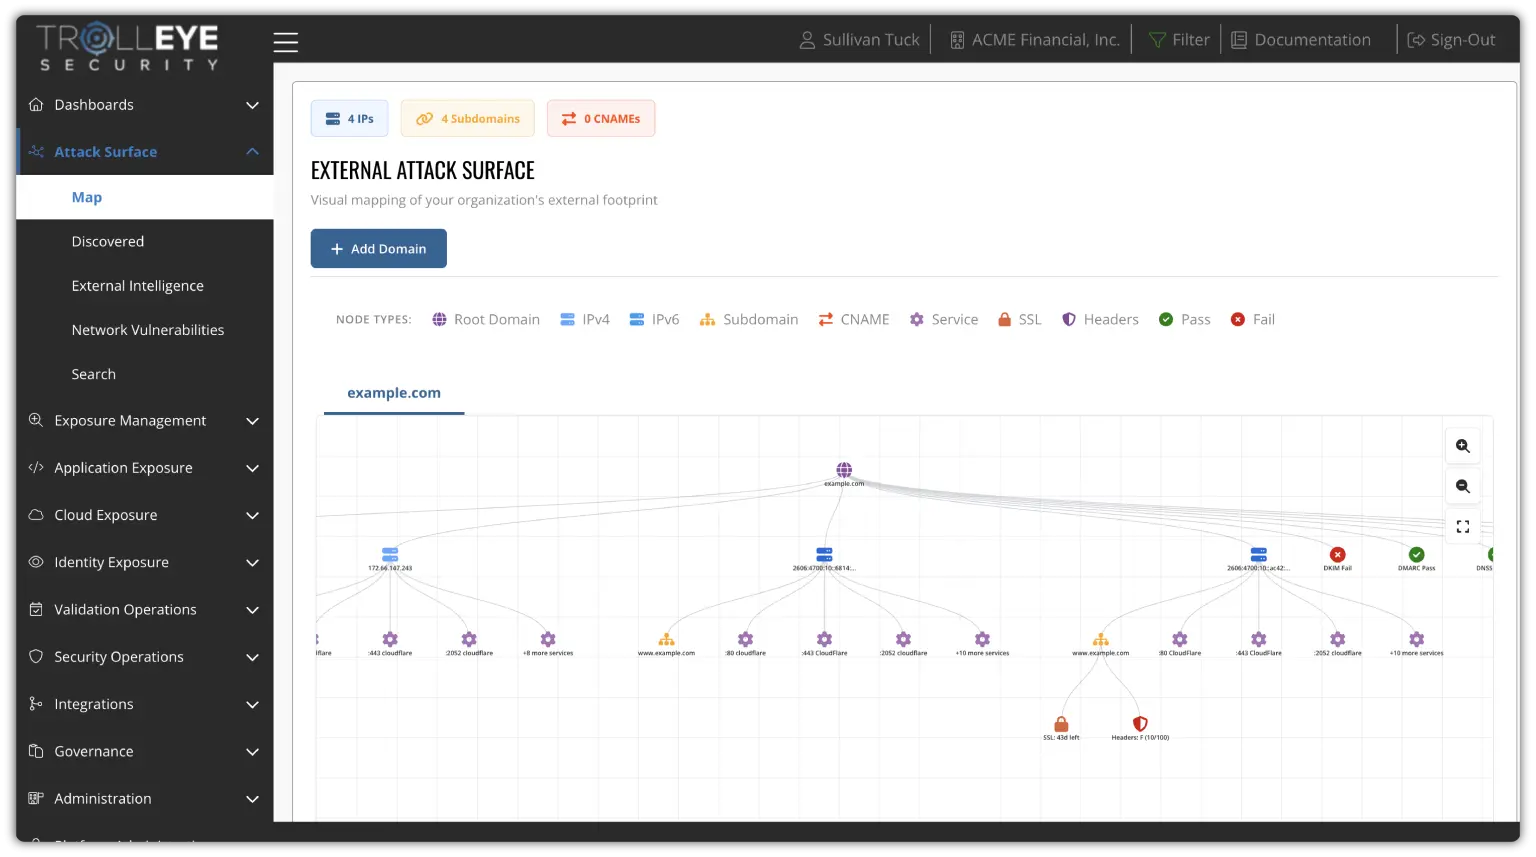
TrollEye platform mapping an organization's attack surface across every environment
CONTINUOUS ASMEvery asset feeds your CTEM program
PART OF PTAASDiscovery that feeds every PTaaS test
WHAT WE DISCOVER

Every Asset. Every Environment.

Your attack surface spans networks, applications, cloud, and identity. We continuously discover assets across each of them, from internet-facing infrastructure to on-prem systems and the shadow IT no one has inventoried, with owner and business context attached from the start.

Ready to test what we find? See External Penetration Testing →
01

Internet-Facing Assets

Domains, subdomains, IP ranges, exposed services, open ports, and certificates continuously discovered and evaluated for exploitability.

02

Internal Networks

Internal hosts, authentication flows, privilege relationships, and segmentation gaps mapped to surface lateral movement risk.

03

Multi-Cloud Workloads

AWS, Azure, and GCP workloads, storage, and exposed APIs evaluated so cloud growth doesn’t silently expand exposure.

04

Identity and Access

Identity permissions and hybrid trust relationships assessed to surface escalation paths before they’re abused.

05

On-Prem and Legacy Systems

Internal servers, network devices, Active Directory, and legacy systems assessed for misconfigurations and exploitable weaknesses.

06

Shadow IT and Unmanaged Assets

Discovered assets reconciled against known inventories to eliminate the blind spots attackers rely on.

PROVEN IN PRACTICE

Recognized By The Industry. Trusted By Security Teams.

An attack surface program should create measurable improvement, not just another report. TrollEye combines continuous testing, hands-on expertise, and remediation support in a model recognized by Gartner and trusted by security teams across multiple industries.

INDUSTRY RECOGNITION
01
GARTNER RESEARCH

Representative Provider in a Recent Gartner® Report

Named a Representative Provider in Gartner research covering Penetration Testing as a Service.

02
APPLICATION SECURITY

Sample Vendor in Gartner’s 2025 Hype Cycle

Recognized as a Sample Vendor for Penetration Testing as a Service in Gartner’s Hype Cycle for Application Security.

03
SECURITY OPERATIONS

Sample Vendor in Gartner’s 2025 Hype Cycle

Recognized as a Sample Vendor for Penetration Testing as a Service in Gartner’s Hype Cycle for Security Operations.

CUSTOMER OUTCOMES
“

Our clients have reduced critical and high findings to almost zero within six months.

The goal is not simply to find more vulnerabilities. It is to build a repeatable testing and remediation process that continuously drives meaningful exposure down.

Ricoh Danielson
Ricoh Danielson
★★★★★
Enterprise CISO at CorroHealth
My speed to respond and my speed to remediate have gone down dramatically. My scalability, flexibility, and agility across the environment are much faster than with the big-box vendors.
Watch Ricoh's Testimonial →
Dane Clemons
Dane Clemons
★★★★★
Director of Information Technology at Talquin Electric
I consider TrollEye to be a true hidden gem in the realm of security solutions and an invaluable technology partner. Talquin has been utilizing TrollEye's services for over four years now, and our experience has been nothing short of exceptional. TrollEye's unwavering dedication to security has ultimately bolstered Talquin's overall security posture.
Mario Andino
Mario Andino
★★★★★
Former Security Analyst at SMC3
I am pleased with all the services we are receiving from the team at TrollEye Security. Being able to actively view findings from their platform gives our information security team the insight we need to ensure our security posture across the organization.
Cyrus Yazdanpanah
Cyrus Yazdanpanah
★★★★★
Director of Information Technology at FSLSO
PTaaS has been a wonderful addition to our Development Lifecycle. TrollEye's platform provides a unique experience and excellent value!
INHERITED FROM PTAAS

Everything In PTaaS, Applied To Discovery.

Attack surface management isn't a standalone inventory tool. It runs inside our PTaaS solution, feeding internal, external, network, web application, and IoT testing with the same platform, the same remediation workflow, and the same agentic and human testing model.

01

Risk-Based Prioritization

Discovered exposures are prioritized by exploitability, threat context, and business impact, not just severity scores, so teams focus on the gaps attackers would actually use.

02

Owner-Routed Remediation

Assets and exposures arrive with owner and business context, routed to the infrastructure, cloud, or security team responsible for them, with clear guidance to act.

03

Managed, Continuous Testing

New assets join testing scope as they appear, and our team manages validation, guidance, and retesting, so discovery turns into measurable risk reduction.

FROM DISCOVERY TO ACTION

From Unknown Asset To Validated Exposure.

Discovery only matters if it changes what your team does next. Every asset we find moves through the same path, inventoried, owned, prioritized, and validated through PTaaS, so exposure gets acted on instead of added to another list.

INSIDE THE PLATFORM

How ASM Works Inside TrollEye.

Discovered assets don't land in a spreadsheet. They live in the same TrollEye platform as every PTaaS test, where your team can see what exists, what is exploitable, who owns it, and when it has been retested.

Asset Inventory

Every discovered domain, host, cloud workload, and exposed service sits in one continuously updated inventory, reconciled against what your team already tracks.

  • Hosts, domains, and cloud assets in one view
  • Shadow IT and unmanaged assets surfaced
  • Inventory that updates as the environment changes
TrollEye platform asset inventory view

Validated Findings

Exposures discovered through ASM flow into PTaaS testing and arrive with exploit evidence, reproduction detail, and business context once they are proven exploitable.

  • Exploitability confirmed by our testers
  • Risk-ranked by exposure and impact
  • Evidence attached to every finding
TrollEye platform validated findings view

Remediation

Exposures route to the infrastructure, cloud, or security owner responsible for each asset, with clear guidance to fix the root cause, not just the symptom.

  • Role-based task distribution
  • Step-by-step remediation guidance
  • No validated exposure lost in a backlog
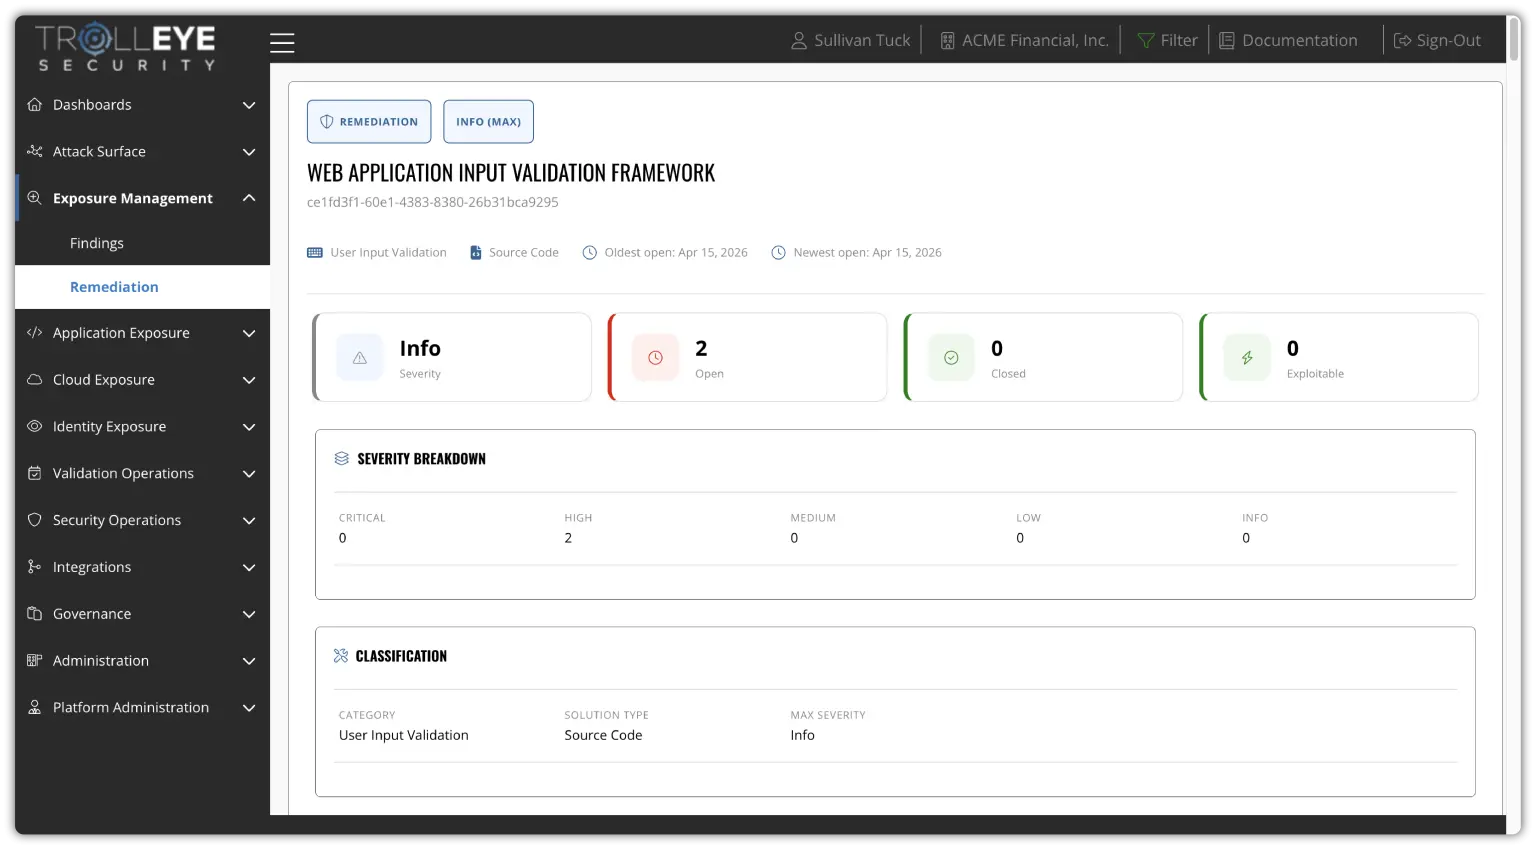
TrollEye platform remediation view

Retesting

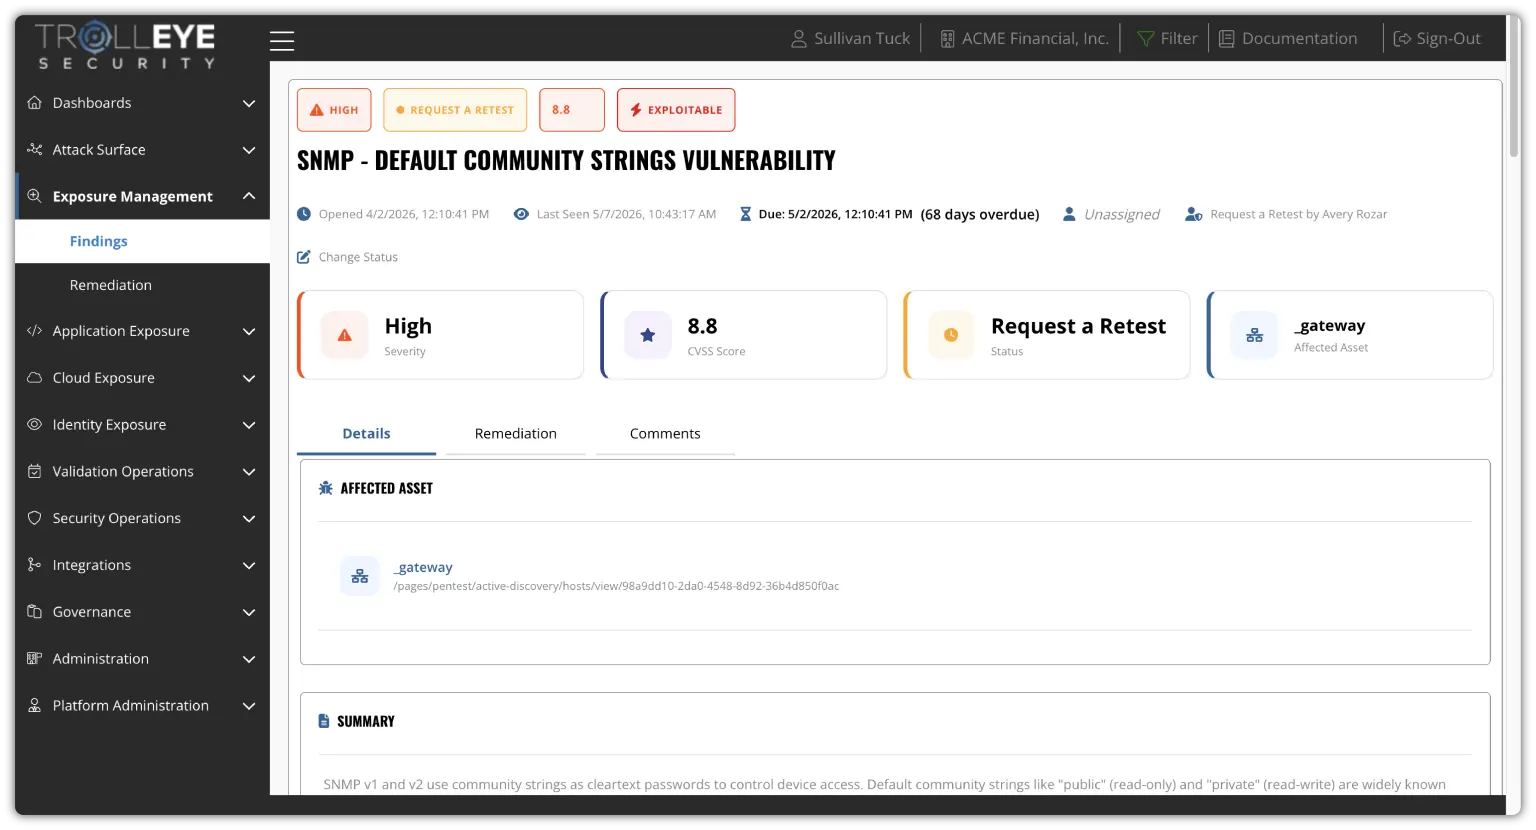
Once a fix is in, request a retest directly from the platform and our team confirms whether the exposure has been closed.

  • Retests requested in one click
  • Status updated on every finding
  • Closure confirmed by the same team that found it
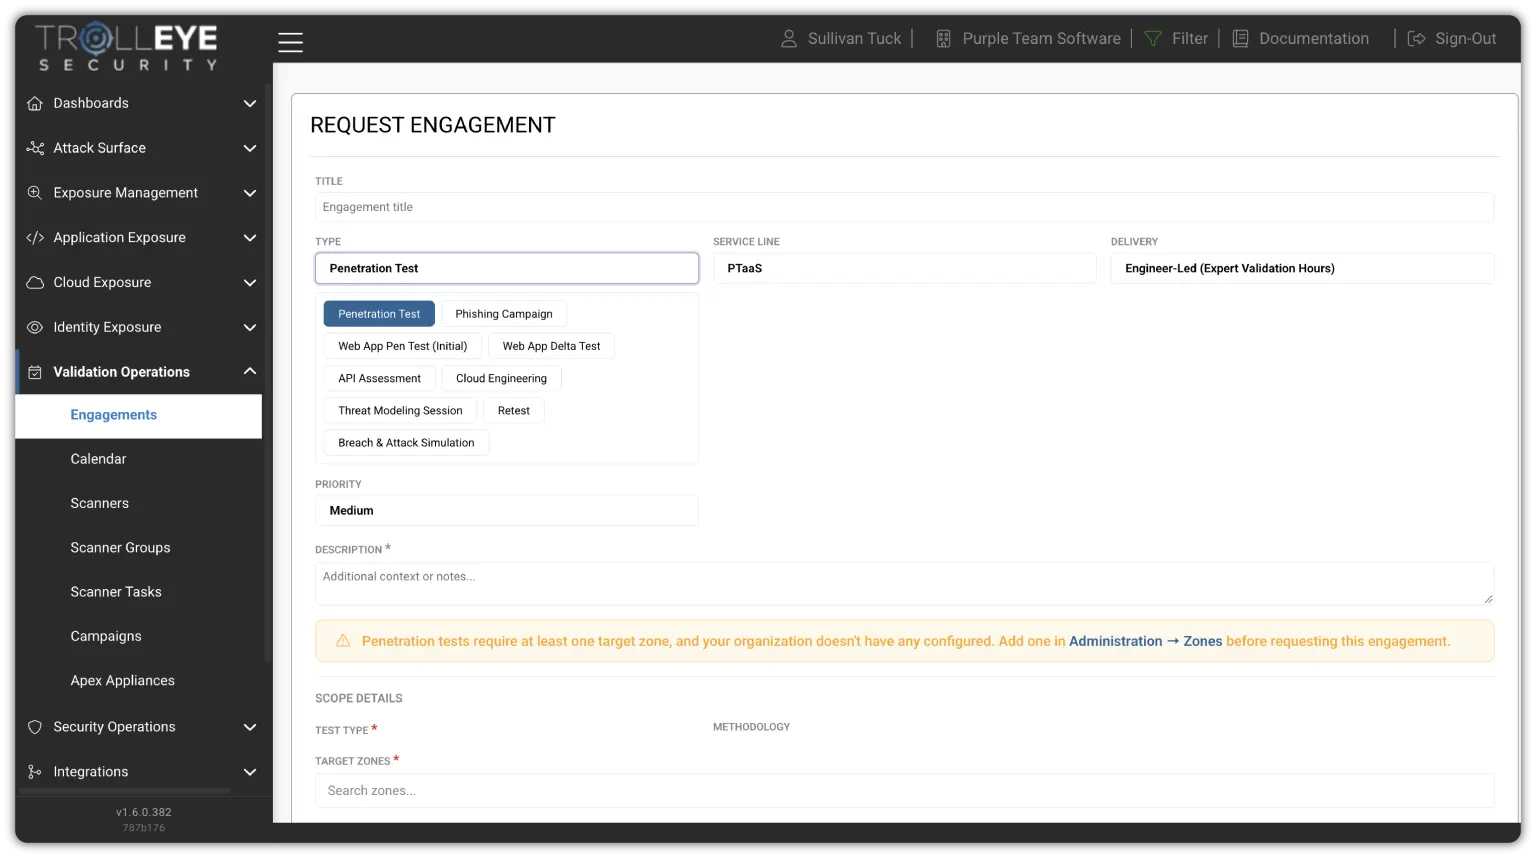
TrollEye platform retesting view

Reporting

Executive and technical reporting shows how your attack surface and exposure trend over time, alongside every other test in your PTaaS program.

  • Executive-ready summaries
  • Technical detail for engineering teams
  • Attack surface results in the context of all PTaaS testing
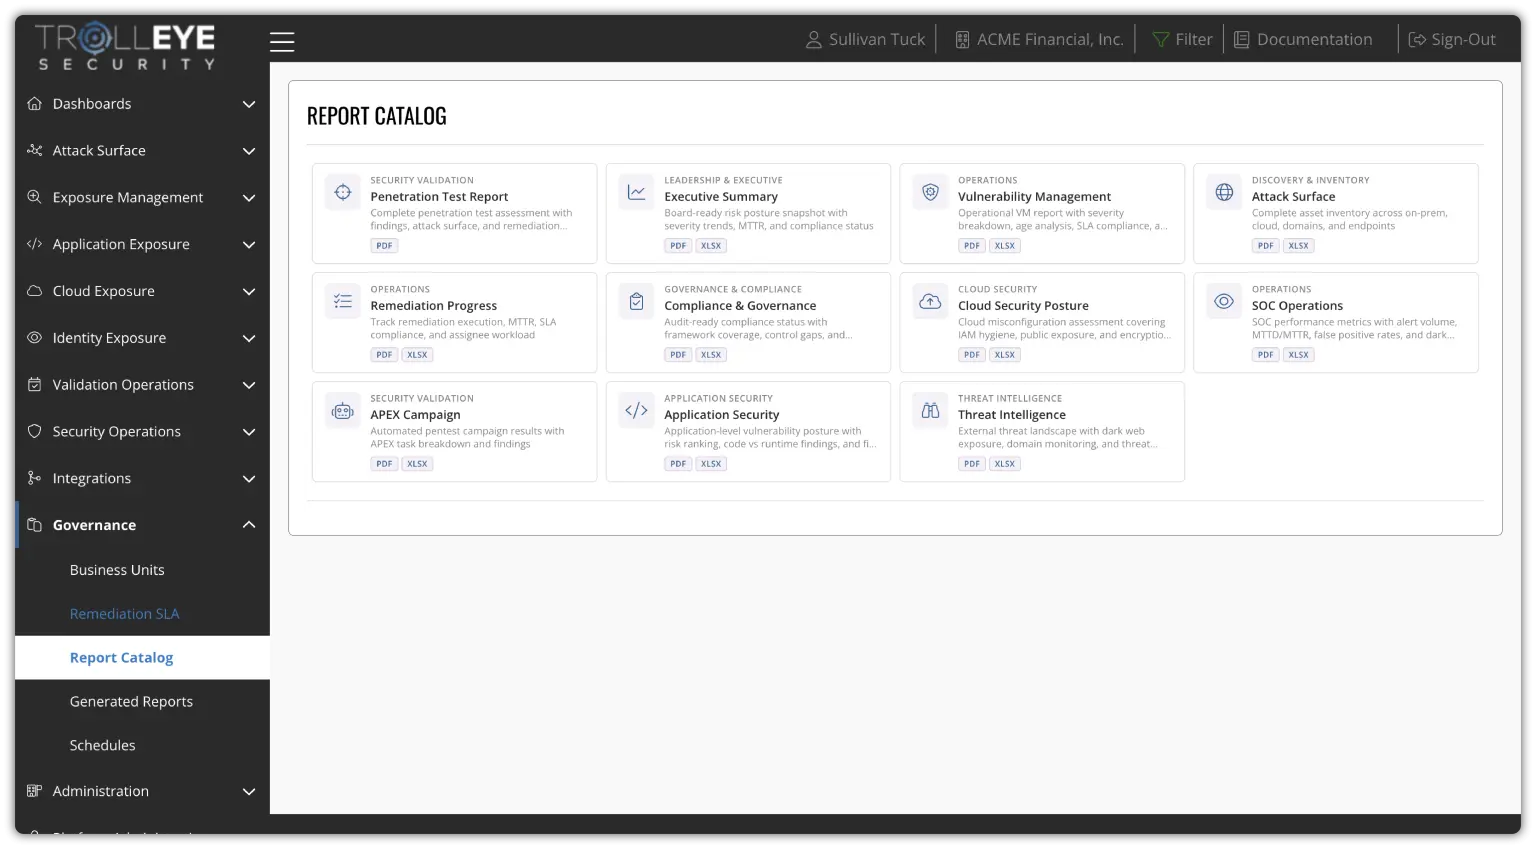
TrollEye platform reporting view
ASM WITHIN CTEM

The Discovery Engine Of Continuous Threat Exposure Management.

Attack Surface Management (ASM) is the foundation of our Continuous Threat Exposure Management (CTEM) solution. By continuously scoping and discovering assets across every environment, ASM defines what the rest of the program protects, tests, and fixes.

Most organizations don’t have a visibility problem. They have an execution problem. ASM connects discovery to every stage of CTEM, so newly found exposure is prioritized, validated, and fixed instead of added to another inventory.

WITHIN OUR CTEM PACKAGES, ASM DATA COMBINES WITH
  • Penetration Testing as a Service
  • Cloud Security
  • Identity Exposure
  • Remediation Workflows
  • Continuous Reporting
ASM FAQ

Questions About Attack Surface Management

How attack surface management works, what it covers, how exposures are prioritized and validated, and how ASM powers the early stages of a Continuous Threat Exposure Management (CTEM) program.

01 · SCOPE02 · DISCOVER03 · PRIORITIZE04 · VALIDATE05 · MOBILIZE
01
SCOPEDefine the Boundaries
02
DISCOVERFind Every Asset
03
PRIORITIZERank by Real Risk
04
VALIDATEProve Exploitability
05
MOBILIZEFix and Retest
01 What is Attack Surface Management (ASM)?

Attack Surface Management (ASM) is the continuous process of discovering, inventorying, and assessing the assets that make up your attack surface, across internet-facing infrastructure, internal networks, cloud environments, identity, and on-prem systems.

TrollEye’s ASM goes beyond discovery by connecting every asset to prioritization, testing, and remediation inside our centralized platform.

02 How is TrollEye’s ASM different from external attack surface tools?

Most attack surface tools map what’s visible from the internet and hand you a list. TrollEye covers external, internal, cloud, and on-prem environments, and evaluates which exposures are actually exploitable instead of treating every open port as a crisis.

Discovered exposures flow into the same remediation workflow as the rest of your findings, so your team gets action, not another inventory.

03 How does ASM fit into Continuous Threat Exposure Management (CTEM)?

ASM powers the scoping, discovery, and prioritization stages of our CTEM solution. It defines what your program protects and keeps that picture current as your environment changes.

Within our CTEM packages, ASM data is combined with penetration testing, cloud security, identity exposure, remediation workflows, and continuous reporting to support ongoing risk reduction.

04 How does ASM work with Penetration Testing as a Service (PTaaS)?

ASM feeds discovered exposure data directly into our PTaaS workflow. New assets, configuration changes, and environment expansions are incorporated into testing scope automatically.

Agentic and human testing then proves which exposures are exploitable and reachable, so remediation effort goes where it reduces the most risk.

05 What environments does ASM cover?

Coverage includes internet-facing assets and domains, internal networks, multi-cloud workloads across AWS, Azure, and GCP, identity permissions and trust relationships, and on-prem and legacy infrastructure.

Scope varies by package and can be expanded as organizational requirements grow.

06 How often is my attack surface assessed?

Discovery runs continuously, so new assets and changes are identified as they appear rather than at the next annual assessment.

How often deeper, expert testing happens depends on how you use the service credits included in every CTEM package, so you decide how often that testing happens and where it is focused.

07 How are exposures prioritized and remediated?

Exposures are ranked by exploitability, threat context, asset criticality, and business impact, helping teams focus on the most critical risks first.

Through the platform, organizations can track remediation progress, assign owners, document accepted risks, and verify fixes over time.

TALK TO OUR TEAM See what ASM would find in your environment.

Walk through your scope, your known and unknown assets, and how discovery connects to the rest of your CTEM program with our team.

GET STARTED

See Your Attack Surface The Way Attackers Do. Then Close Every Gap.

Attackers look for the path of least resistance across your entire environment. TrollEye’s Attack Surface Management ensures that path leads nowhere by continuously discovering, prioritizing, and validating exposure, then driving it to resolution as part of a complete CTEM program.

  • 01Continuous asset discovery
  • 02Shadow IT and unmanaged asset detection
  • 03Exposure validated through PTaaS
  • 04Role-based remediation workflows
Live Product Update

Meet the Future of
Risk & Remediation

Introducing two major additions to the TrollEye CTEM platform, designed to help teams move from exposure to action.

AI Remediation Agent

AI assistance to help security teams move from findings to fixes faster.

Business Risk Dashboard

New visibility into breach probability, financial risk, and compliance.

Hosted By

Avery Rozar Avery Rozar CEO, TrollEye Security
Sullivan Tuck Sullivan Tuck Head of Growth & Marketing
December 17, 2026 • 2:00 PM ET • Live Online
Reserve Your Spot →

This Content Is Gated