TrollEye Security

MANAGED SIEM & PURPLE TEAMING

Prove Your Defenses Work Before an Attacker Tests Them.

Most security operations can tell you how many alerts they generated. Few can prove their detections fire when a real adversary moves through the environment.

TrollEye pairs 24/7 managed SIEM with continuous purple team exercises, so every detection is tested against real attacker behavior, tuned when it falls short, and carried into your Continuous Threat Exposure Management (CTEM) program.
24/7 Monitoring
Adversary-Tested
Expert Response
CTEM-Aligned
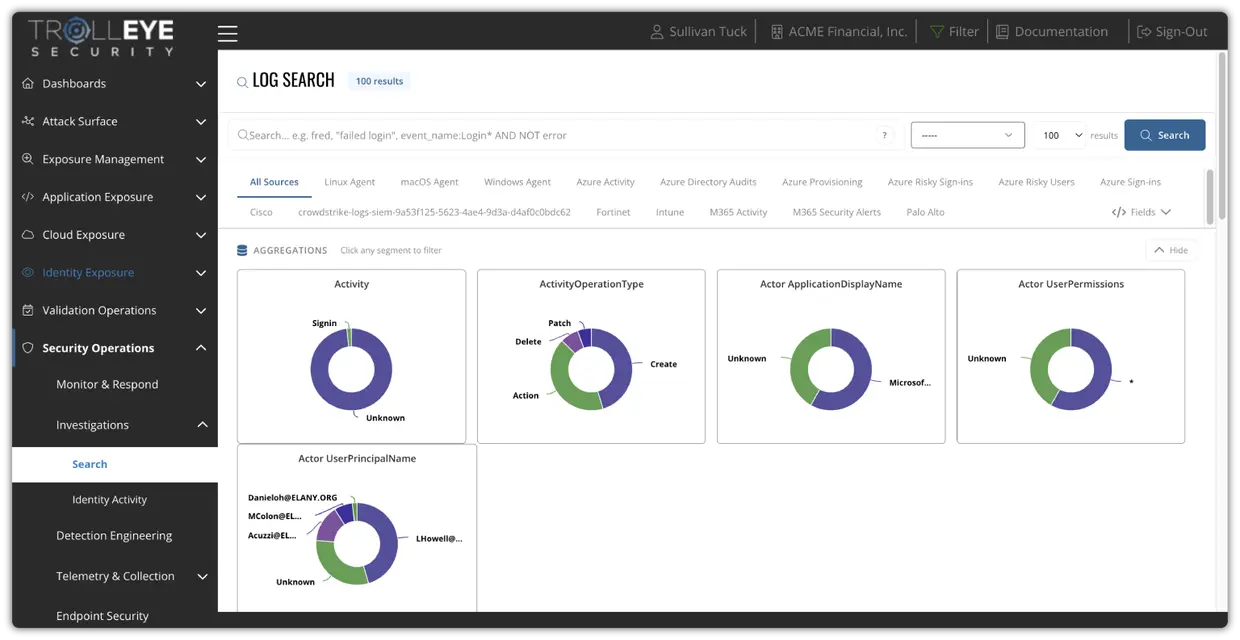
TrollEye platform security operations log search
CONTINUOUS DETECTION & RESPONSEEvery detection tested against real attacker behavior
THE OUTCOME 24/7 Monitoring backed by detections proven in purple team exercises
PROVEN DETECTION, NOT ASSUMED COVERAGE

Managed SIEM Should Prove Detection Works, Not Just Generate Alerts.

Most organizations don't have a visibility problem. They have plenty of logs, dashboards, and alerts. What they lack is proof that those detections catch a real attacker, and a team to act when they do.

Our Managed SIEM & Purple Teaming solution operates a continuous detection and validation program. Analysts monitor your environment around the clock while purple team exercises emulate real adversary techniques, exposing blind spots and feeding every gap back into detection engineering.

01

Detect Threats in Real Time

24/7 monitoring across endpoints, identities, network, and cloud surfaces active threats as they emerge.

02

Prove Your Program Works

Ongoing adversary emulation tests whether alerts, controls, and response processes perform under real attack conditions.

03

Respond Faster with Expert Support

Security experts triage alerts, confirm incidents, and guide response so your team acts decisively when it matters.

OUTCOME 01

Detect and Respond Faster, Without Alert Fatigue.

We continuously monitor your environment and investigate what our detections surface. Alerts are correlated, enriched with threat intelligence and asset context, and triaged by analysts before they reach your team, so you spend time on incidents that matter instead of chasing false positives.

01

Correlate across sourcesTelemetry from endpoints, identities, network devices, and cloud workloads is normalized and analyzed together.

02

Triage before escalationAnalysts, supported by TrollEye’s SOC Agent, classify and investigate alerts so only confirmed activity reaches you.

03

Enrich with contextThreat intelligence and asset criticality show which alerts point at what the business can’t afford to lose.
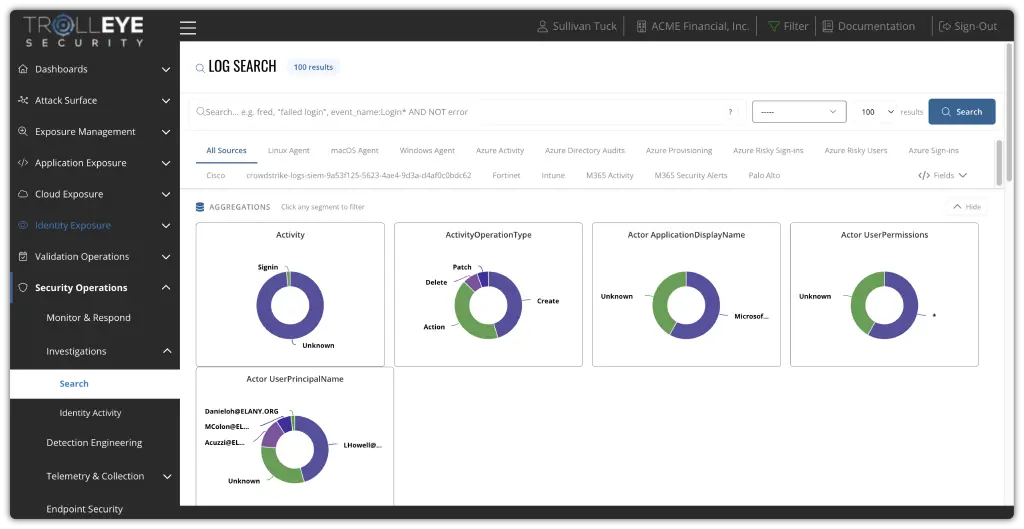
TrollEye security operations log search
OUTCOME 02

Test Security Controls Before an Attacker Does.

Rather than assuming detections work, we test them. Purple team exercises emulate real-world adversary tactics, techniques, and procedures (TTPs) to confirm that controls, alerts, and response workflows perform as expected across endpoints, identities, networks, and cloud infrastructure.

01

Emulate real adversariesScenarios are built from the threat actors and techniques most relevant to your industry and environment.

02

Measure what firedEvery technique is checked for whether it was logged, alerted on, escalated, and contained.

03

Agentic and human testingAutomated emulation runs at scale while experienced operators chain techniques the way real attackers do.
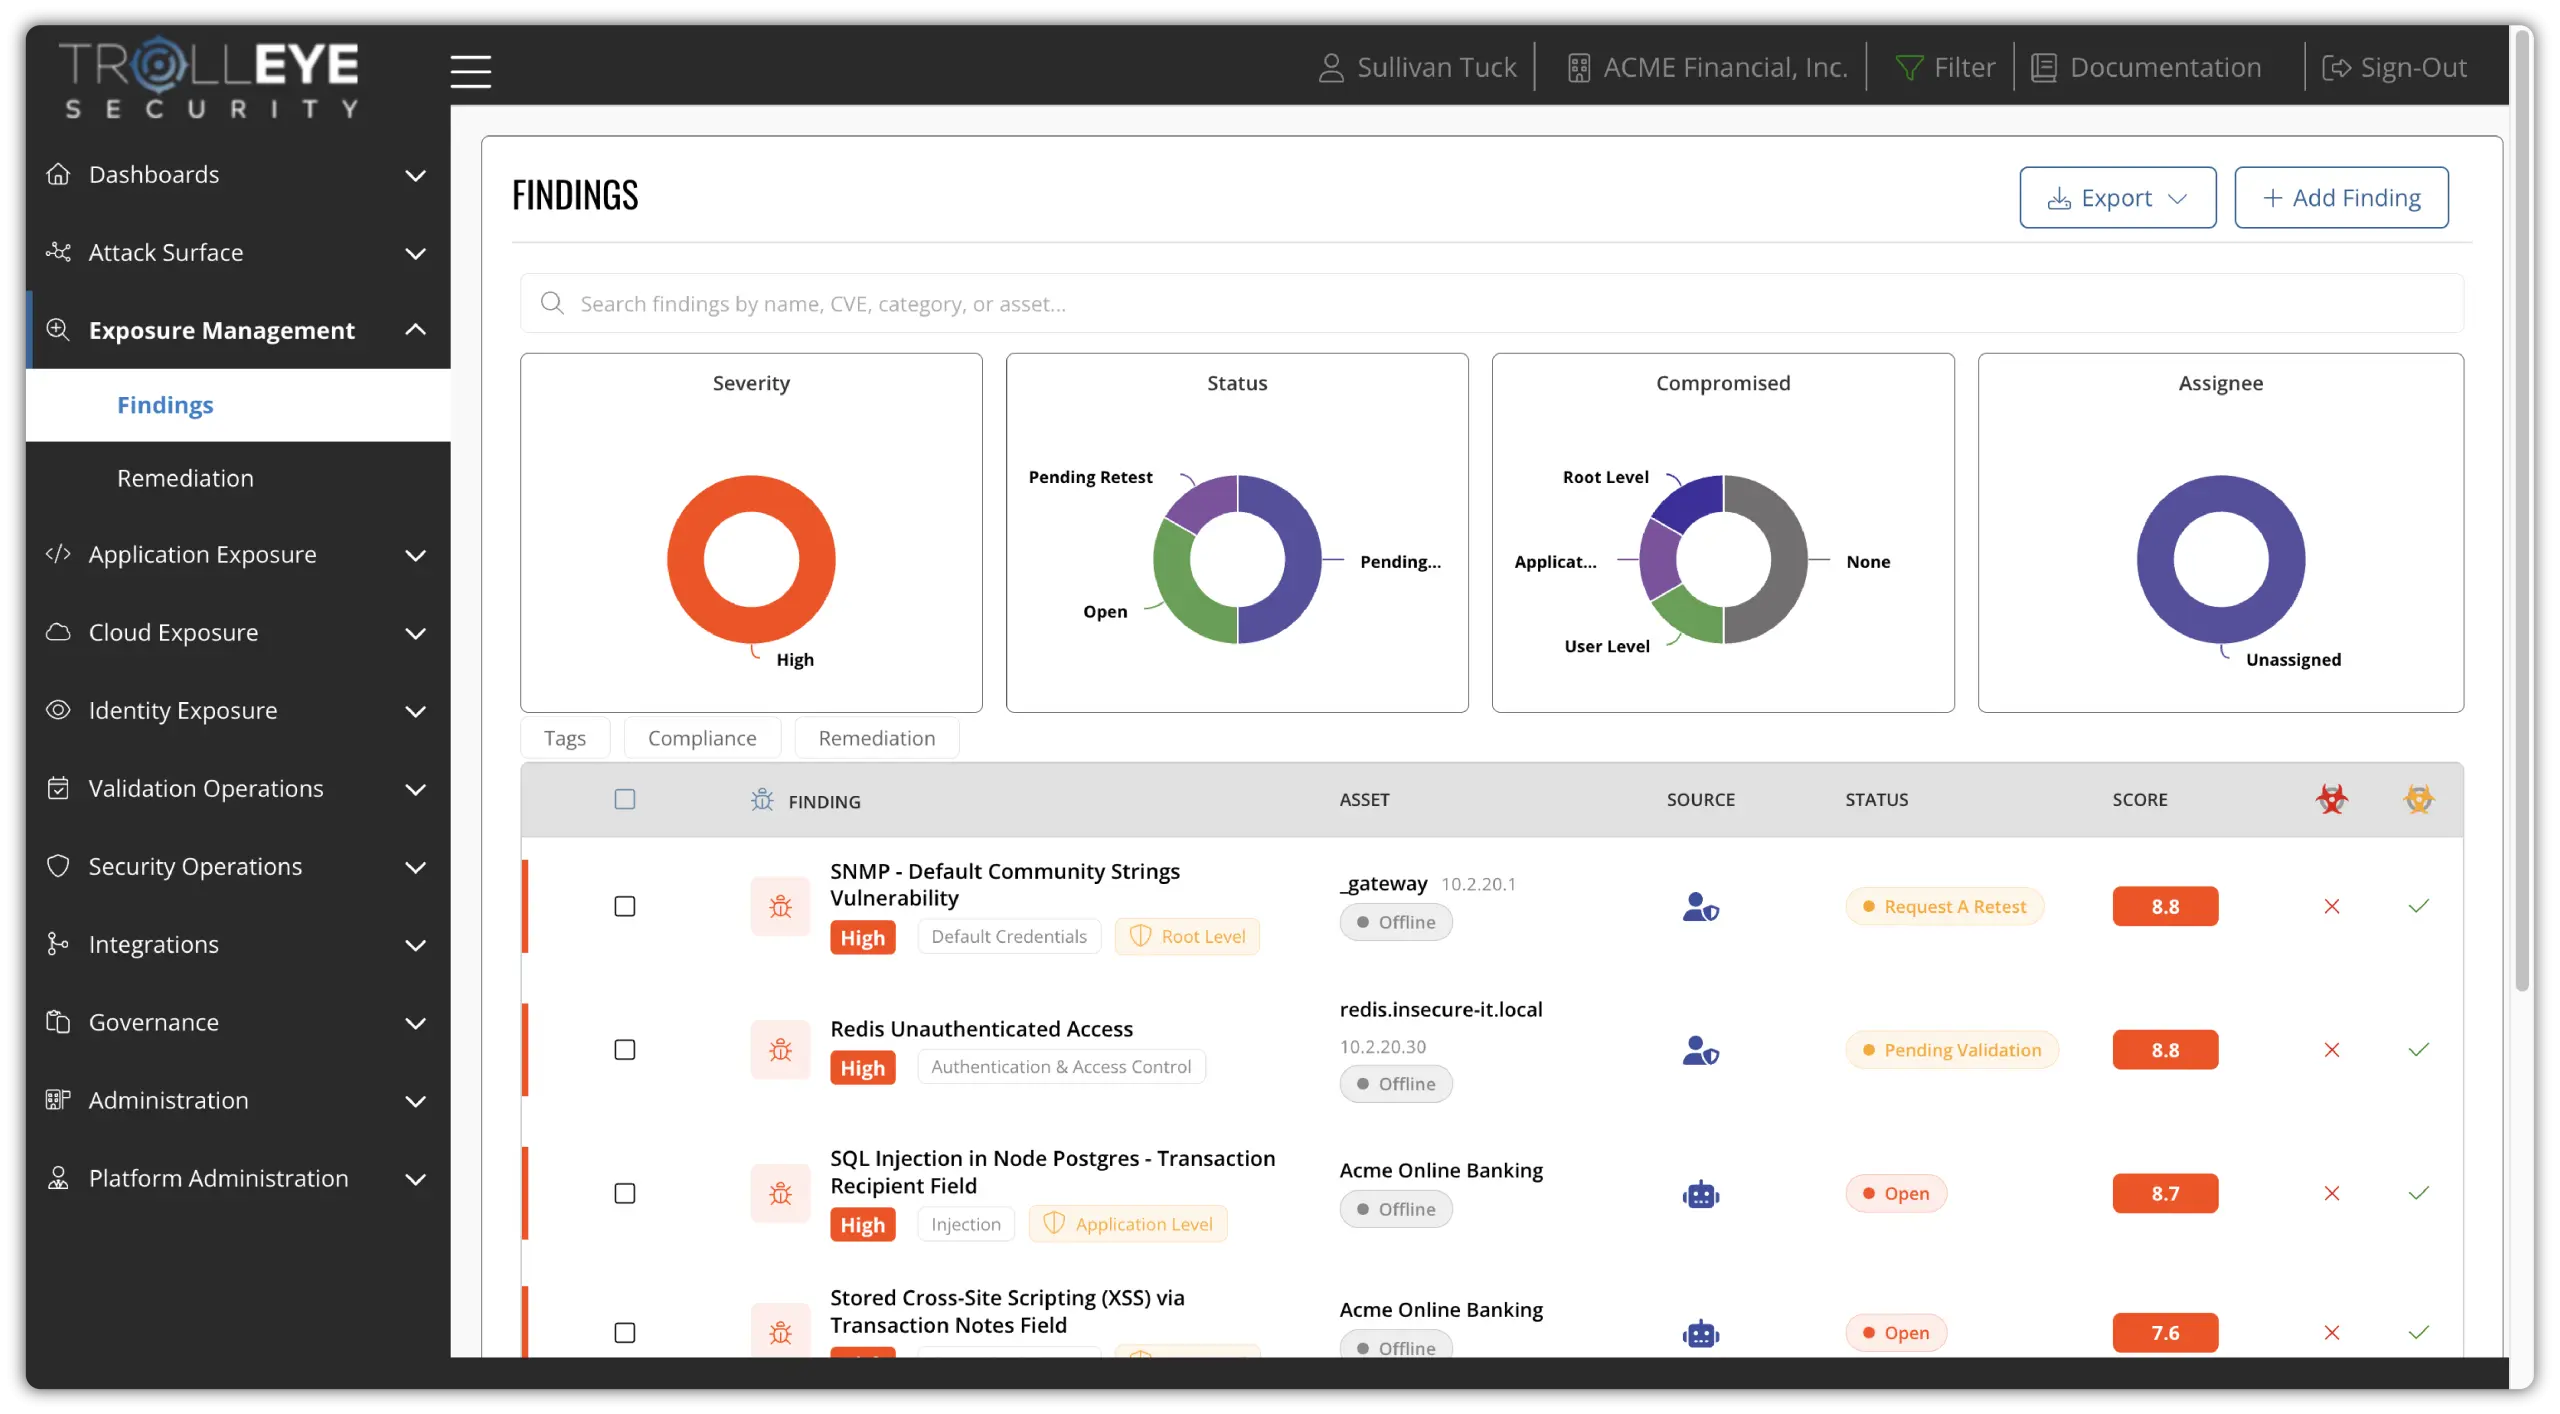
TrollEye findings view of validated security control gaps
OUTCOME 03

Close Detection Blind Spots With Adversarial Tuning.

Operational tuning makes a SIEM quieter. Adversarial tuning makes it better. Gaps found in purple team exercises feed directly into detection engineering, so rules, correlations, and data sources are improved based on what an attacker actually did, not just what generated noise last week.

01

Find what was missedIdentify techniques that executed without a log, an alert, or an escalation.

02

Engineer new detectionsBuild and refine rules mapped to MITRE ATT&CK to cover the gaps exercises expose.

03

Re-run to confirmRepeat the technique after tuning to confirm the new detection now fires.
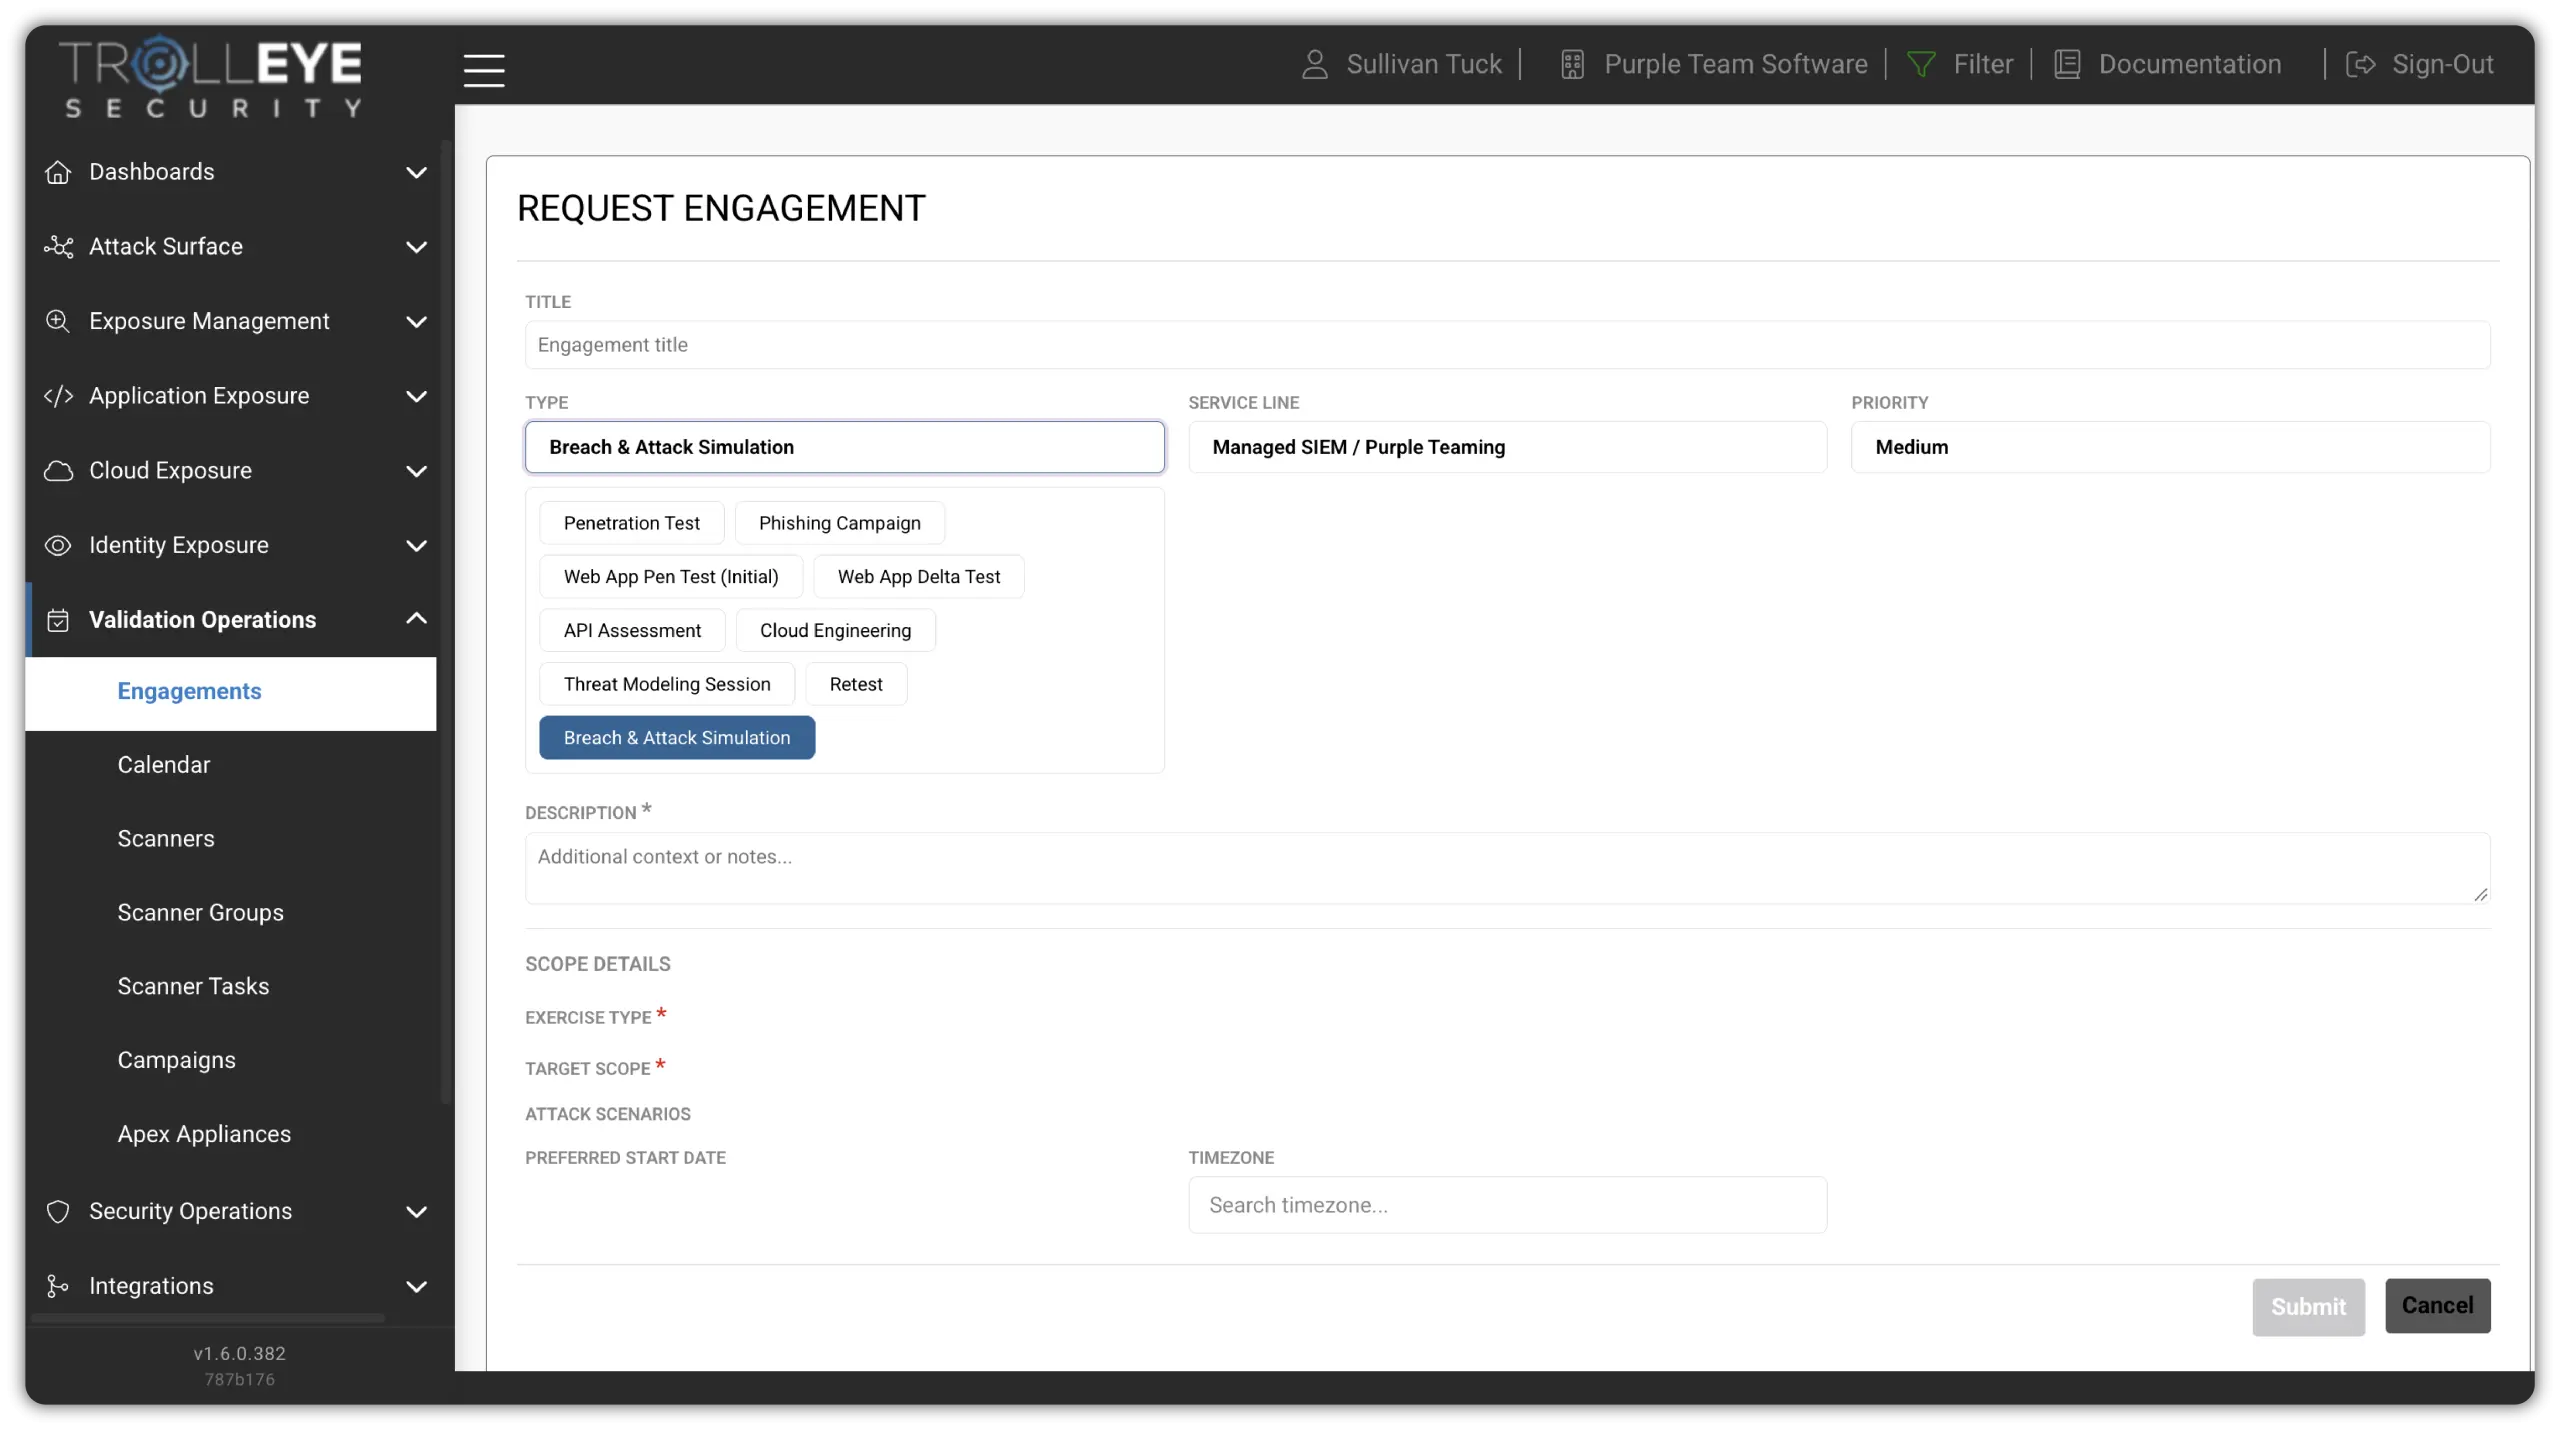
TrollEye breach and attack simulation results
OUTCOME 04

Align Detection, Response, and Ownership Across Teams.

We integrate into the workflows your teams already use, so incidents and detection gaps reach the right owners with clear context and accountability. The result is faster triage, coordinated response, and measurable improvement in detection and response maturity over time.

01

Route to the right ownerIncidents and gaps are assigned to the teams that can act on them, with the evidence they need.

02

Investigate to root causeAnalysts classify incidents, perform root cause analysis, and preserve forensic evidence.

03

Fix it so it doesn’t recurResponse actions address the underlying cause, not just the alert that surfaced it.
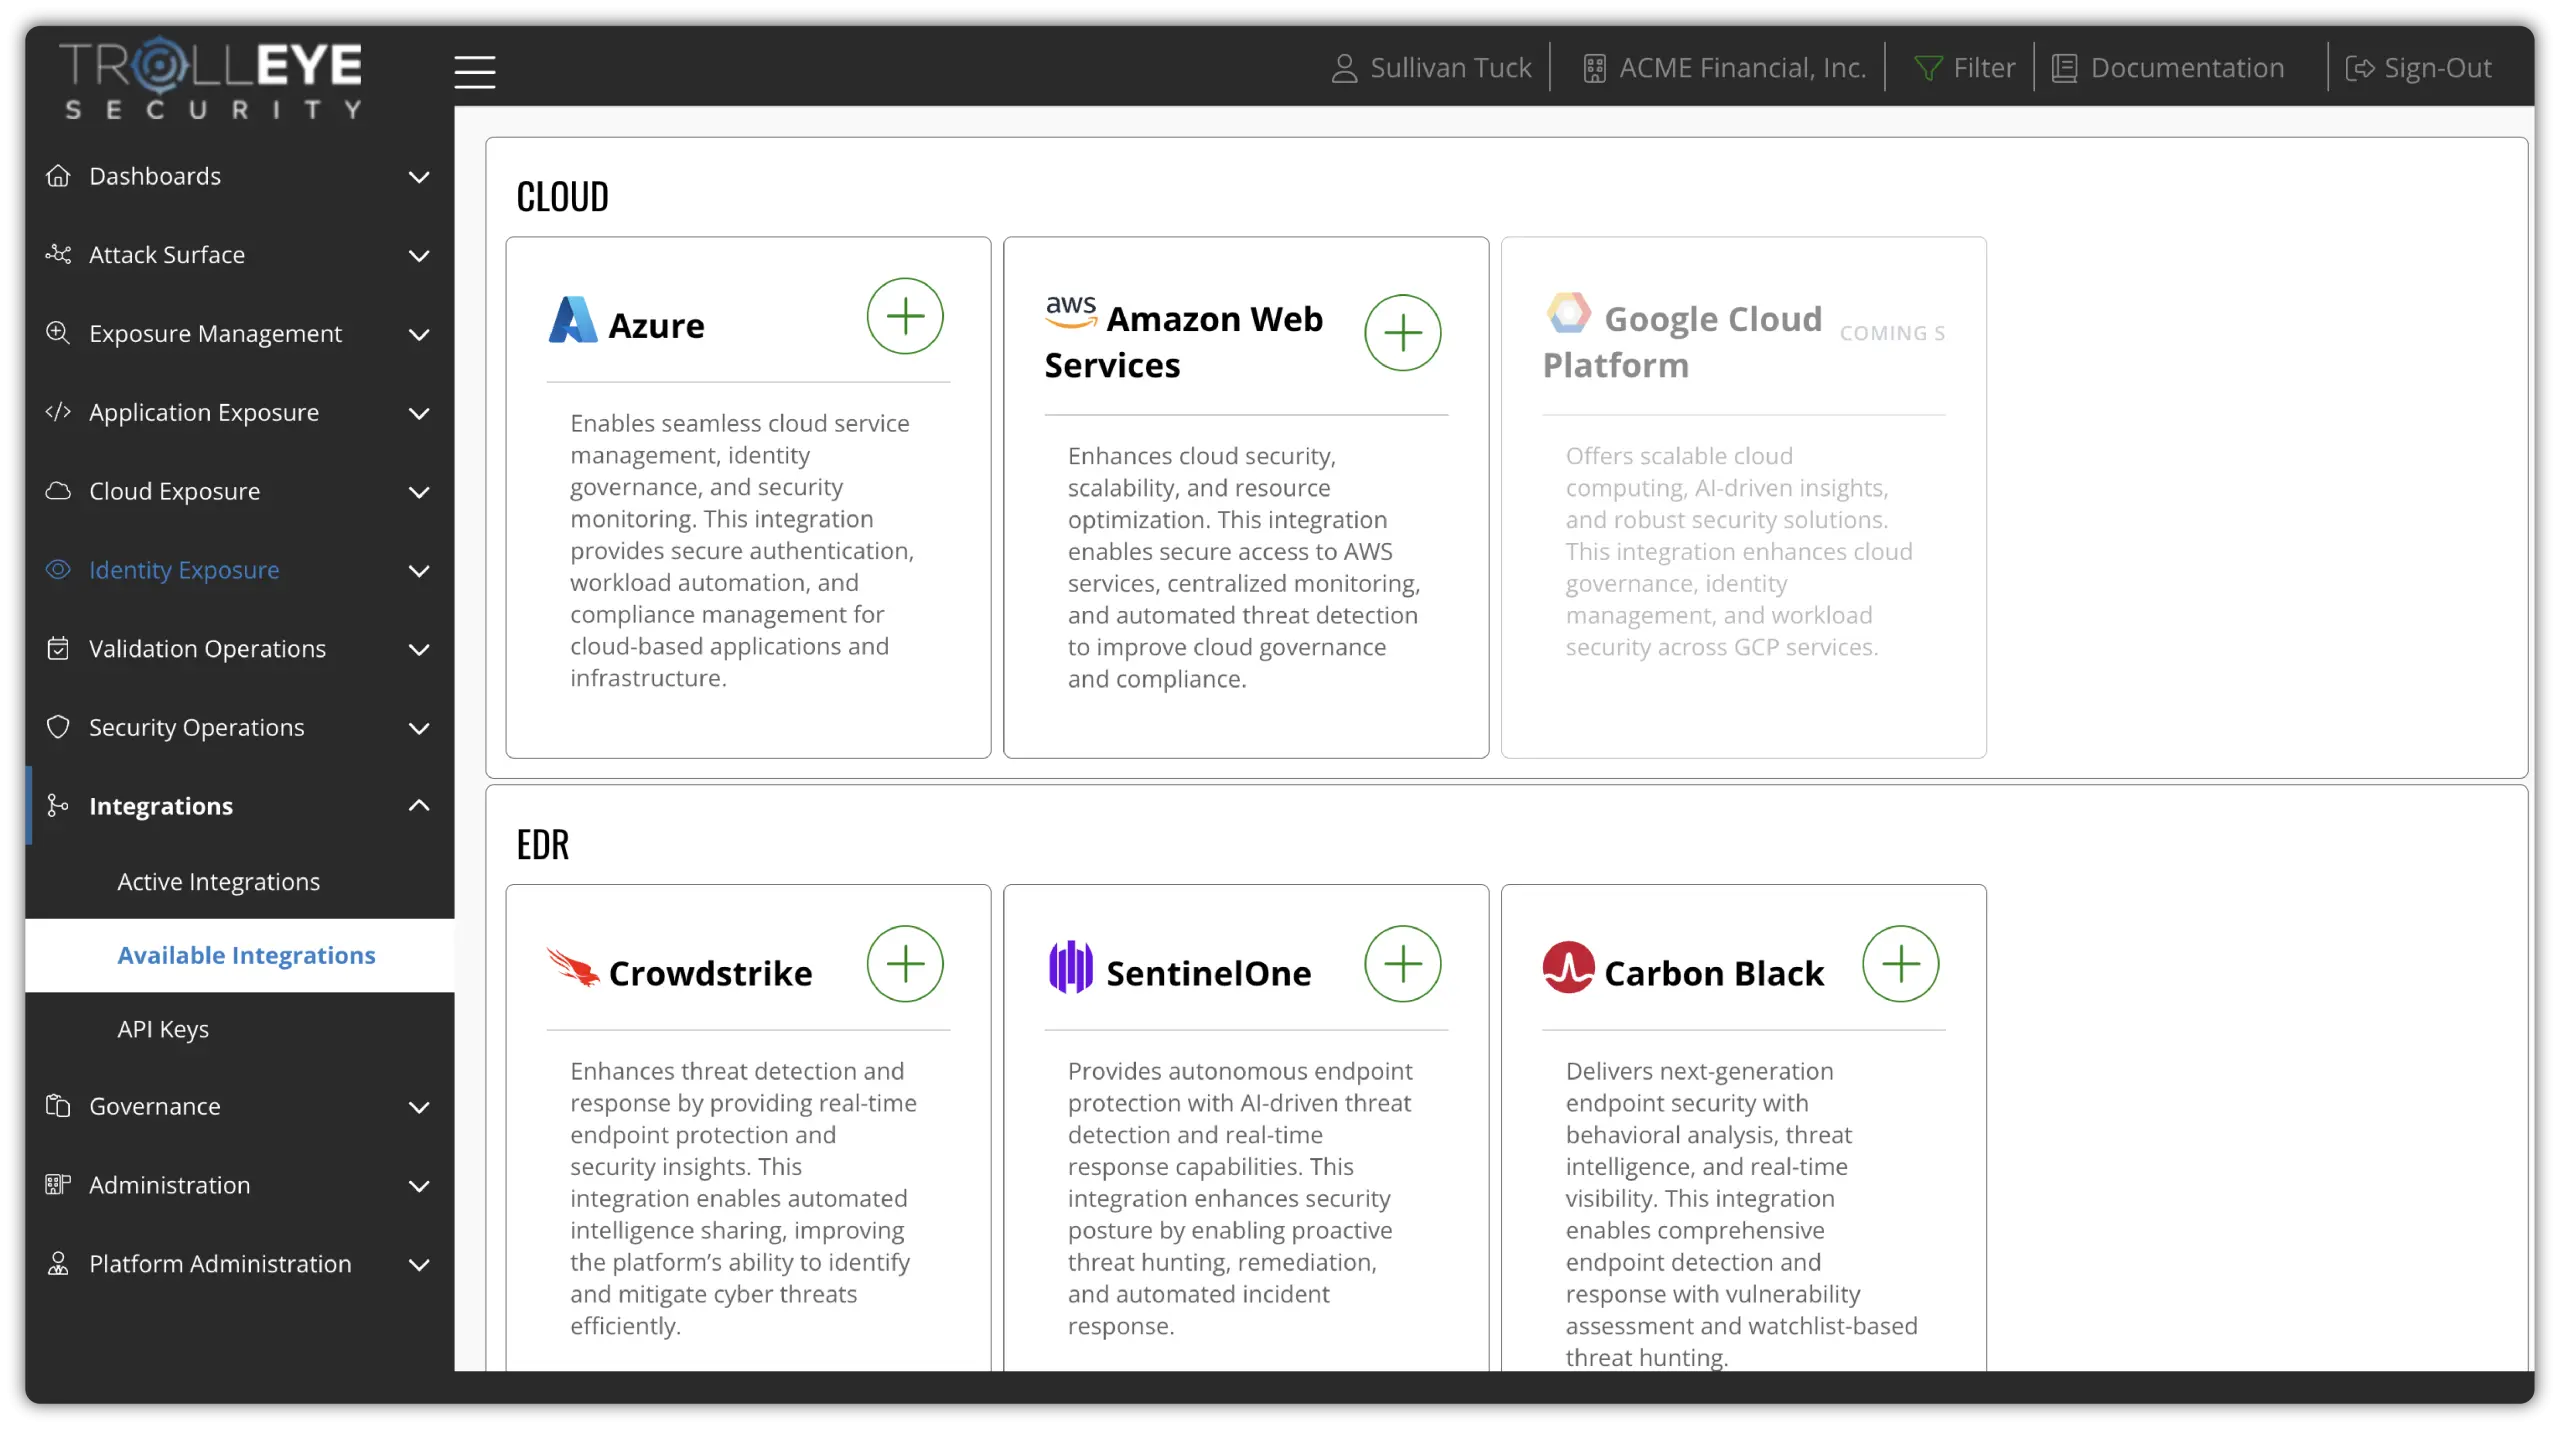
TrollEye platform integrations across security and ticketing tools
OUTCOME 05

Operate a Mature SOC Without Building One Internally.

Our experts manage the day-to-day operation, tuning, testing, and improvement of your SIEM and detection program. You get continuous coverage, expert-led validation, and clear outcomes without the cost and complexity of staffing a full internal SOC.

01

A platform backed by expertsSecurity engineers operate the program with you inside the TrollEye platform.

02

Evolves with your environmentMonitoring and exercises adapt as you add cloud workloads, identities, and business units.

03

Clear executive reportingBusiness-aligned metrics show leadership how detection coverage and response maturity are trending.
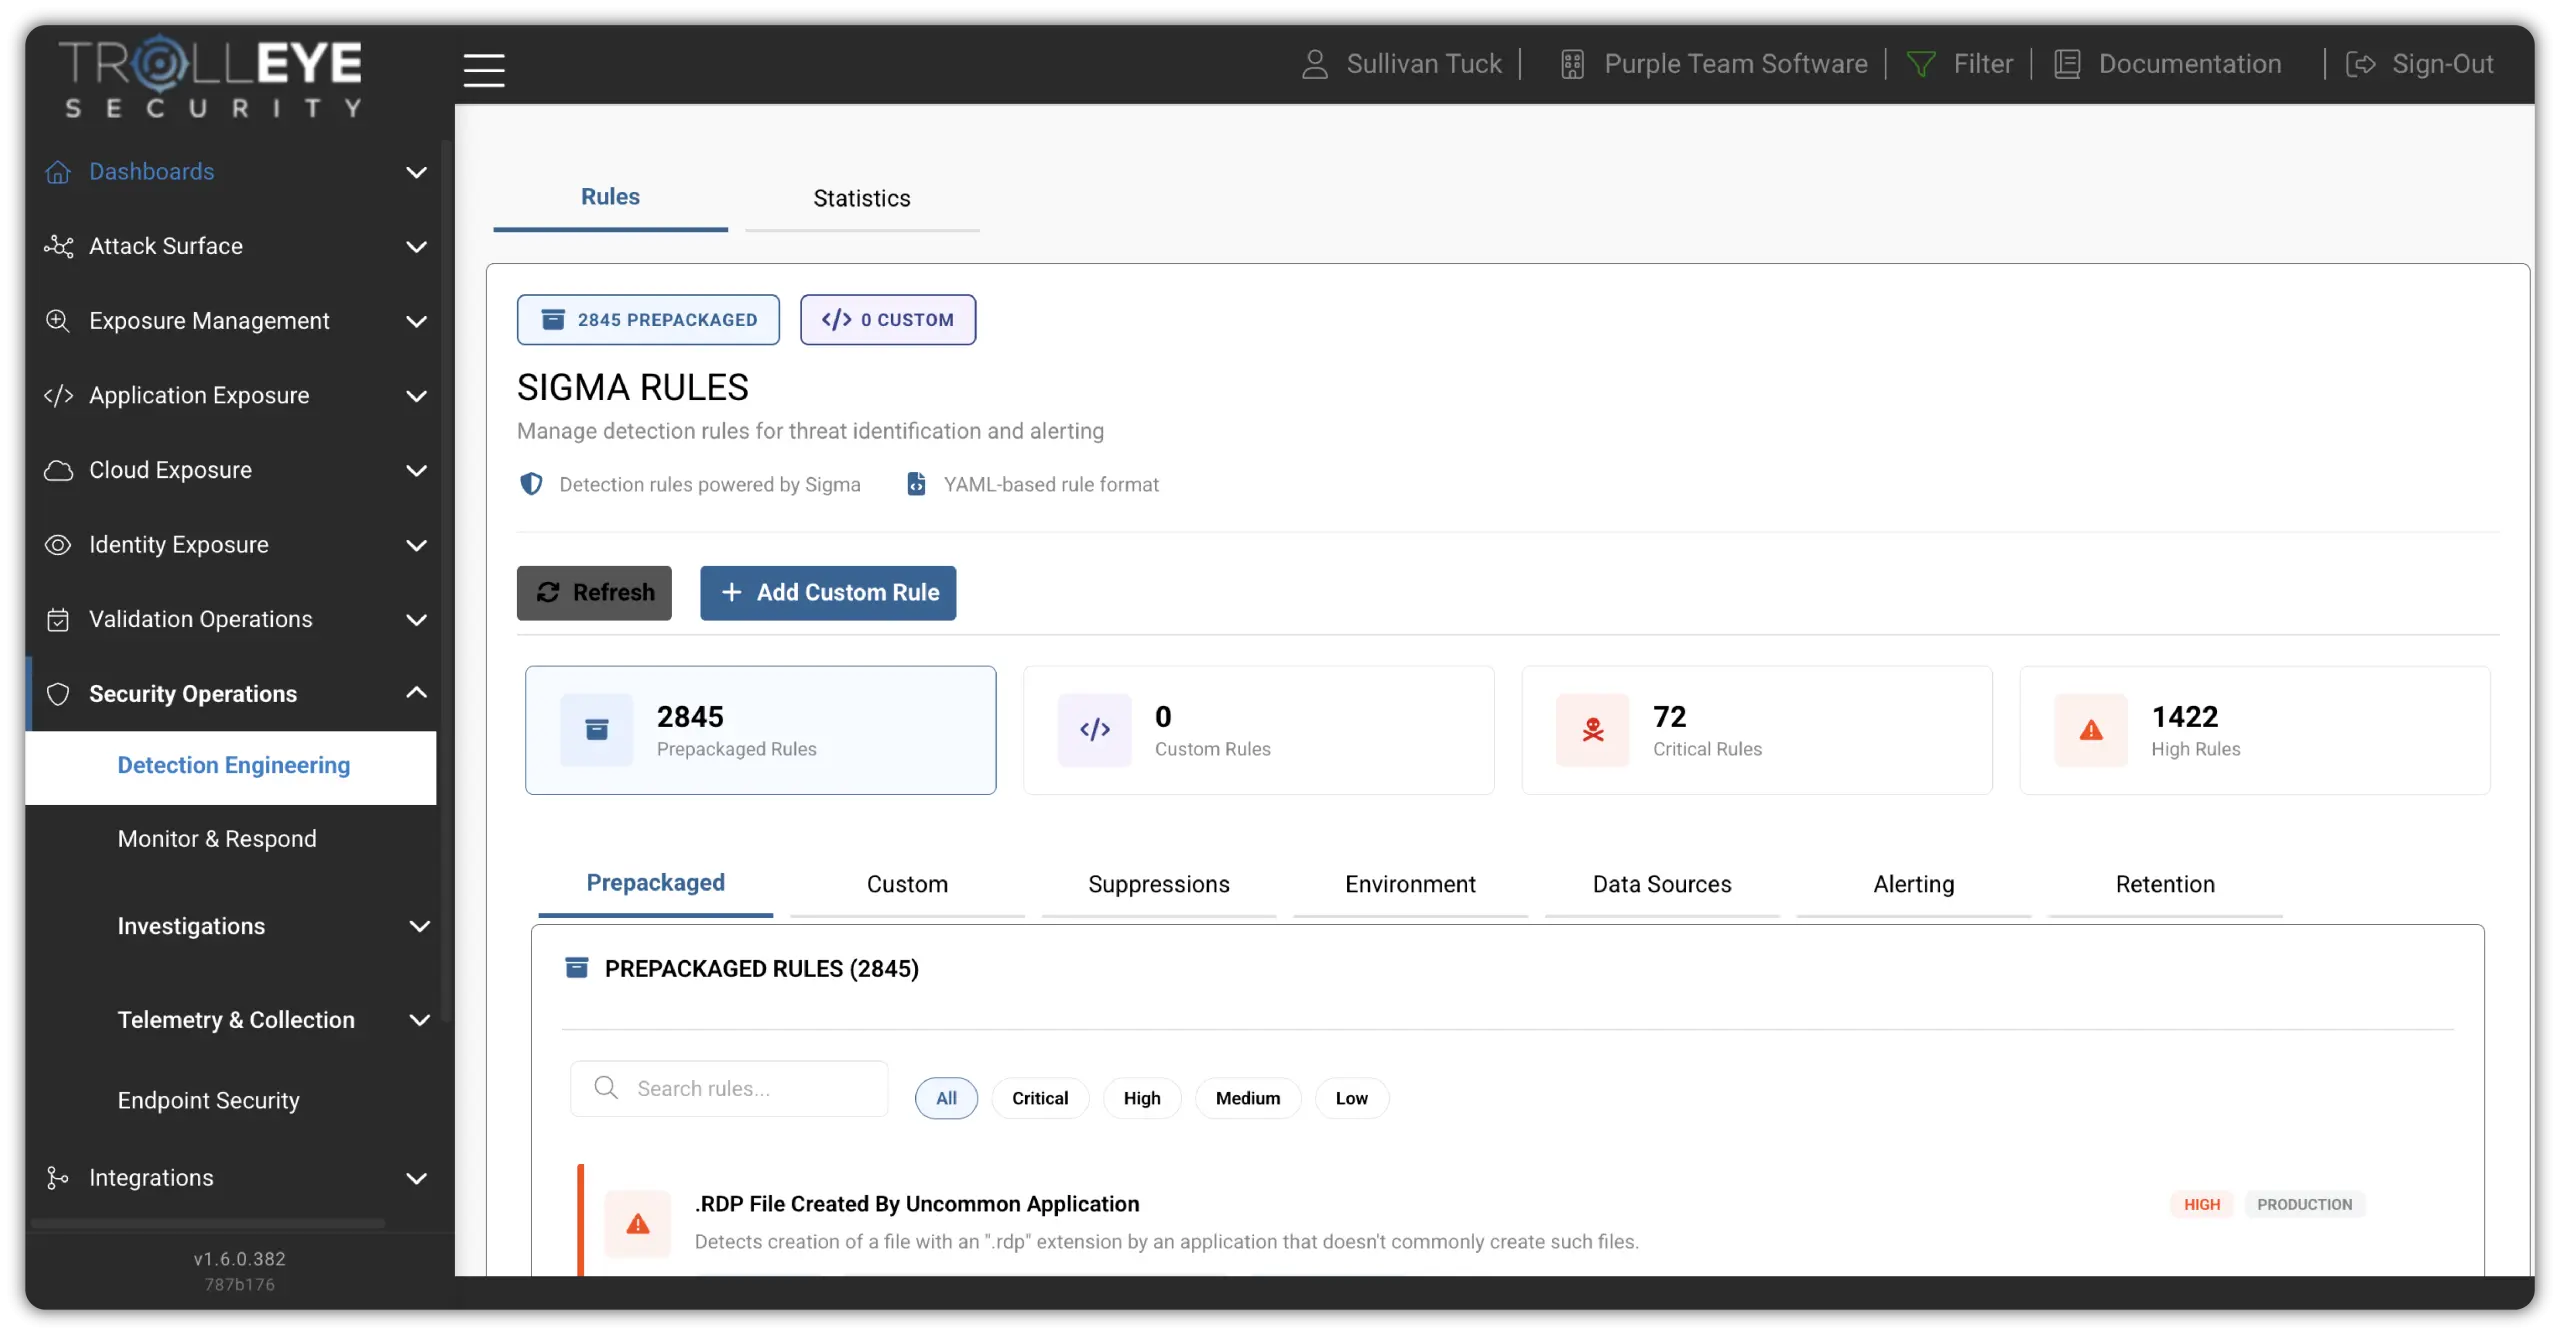
TrollEye managed Sigma detection rules
See Detection & Response in Action

Explore How TrollEye Detects, Validates, and Responds to Threats

See how security operations, purple team validation, and remediation work together in one platform, from log search and alert triage to coordinated response.
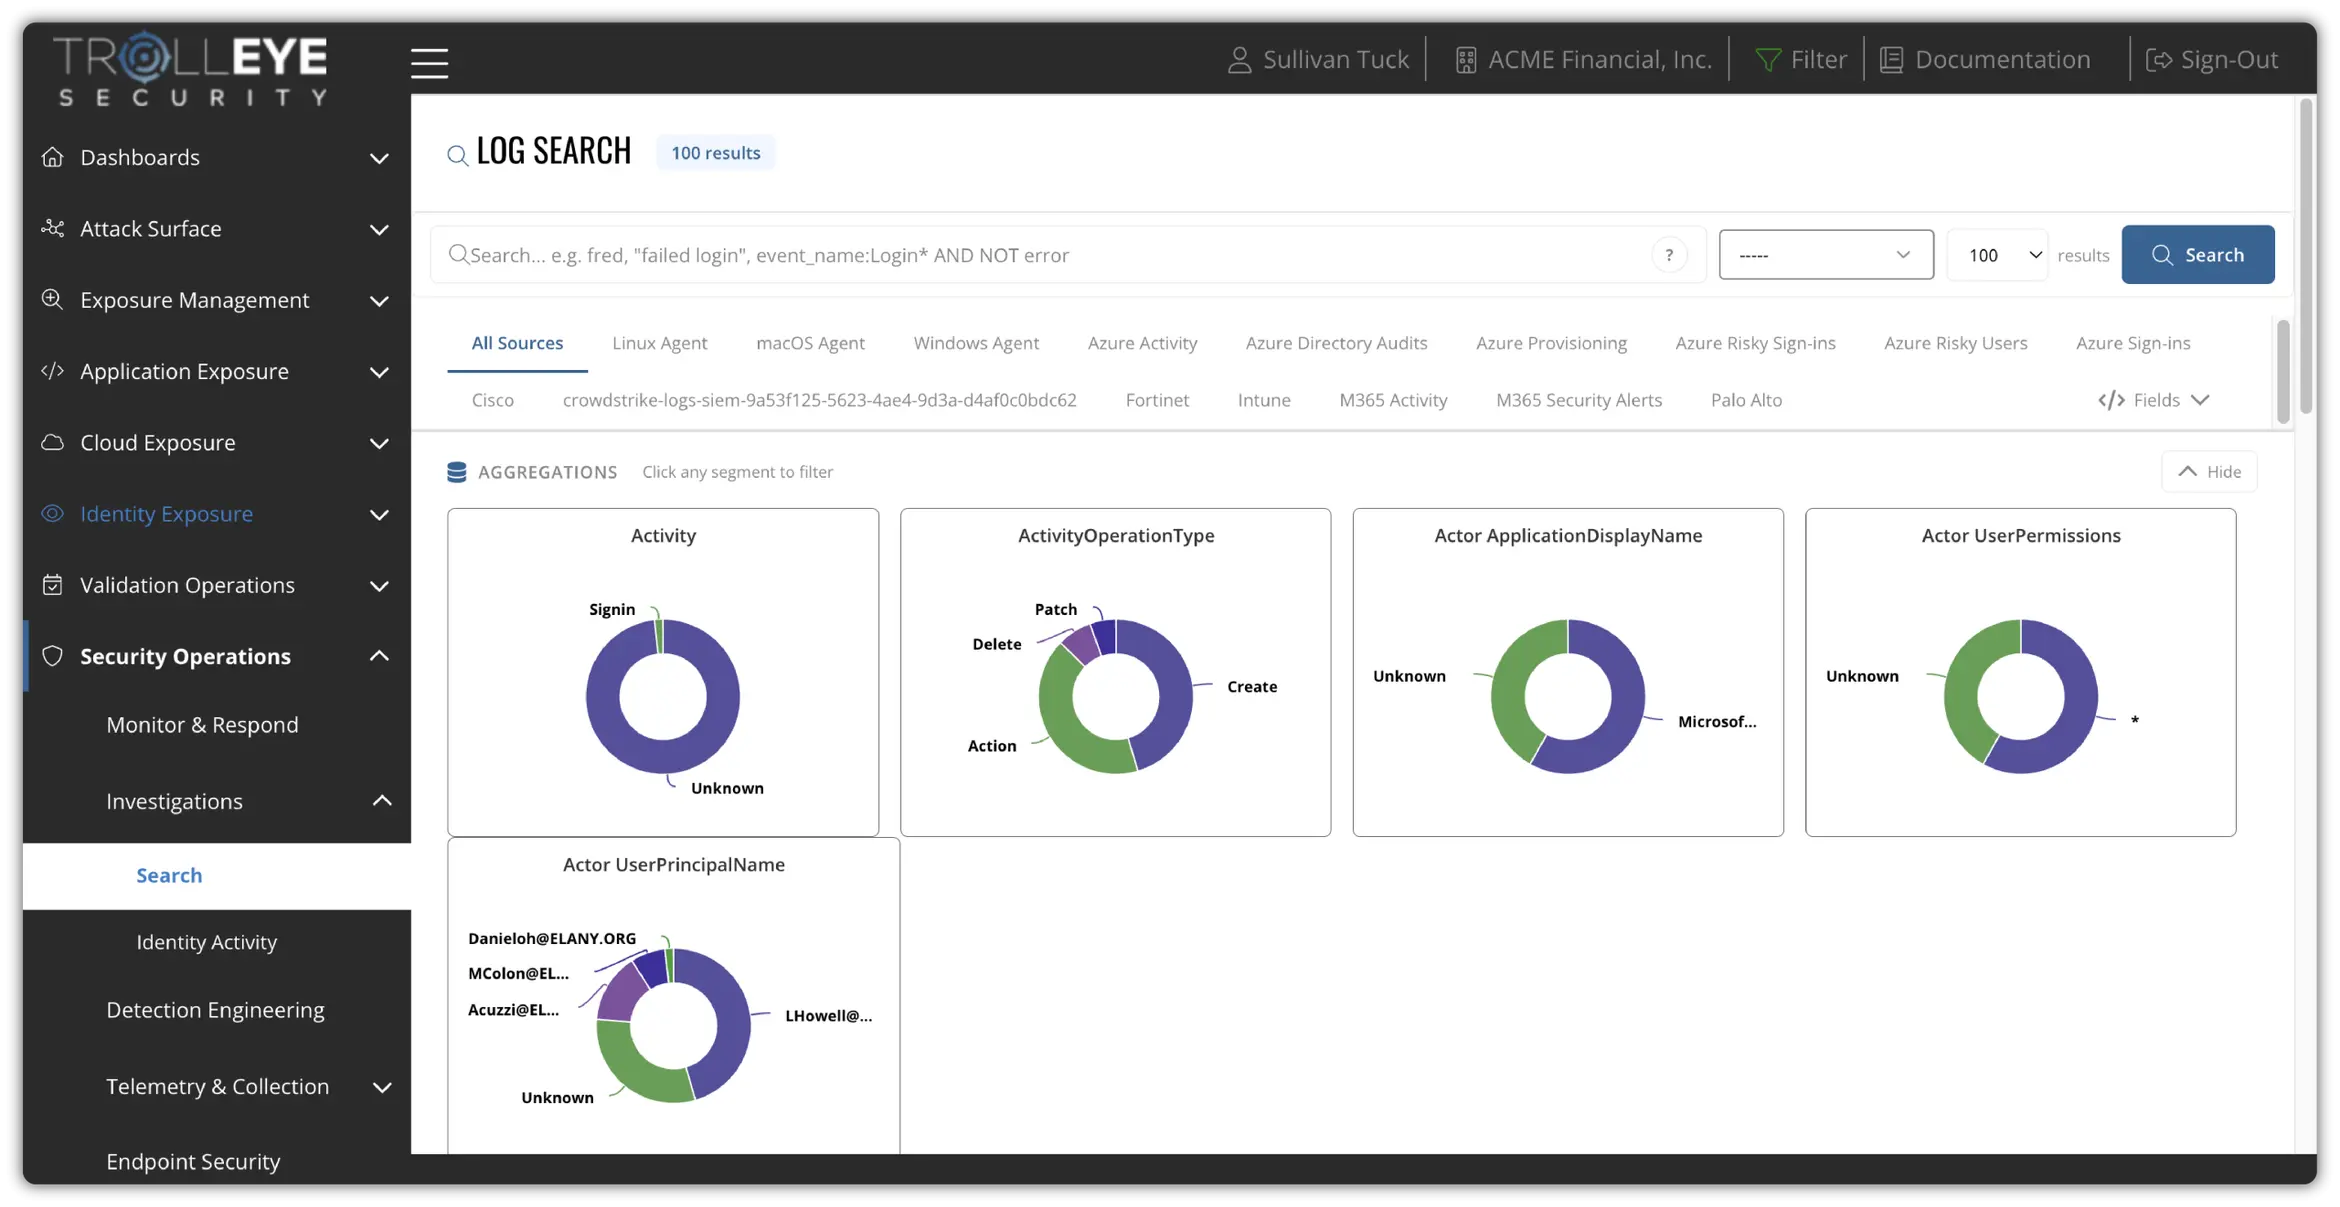
TrollEye security operations log search showing activity across endpoints, identities, and cloud
PROVEN IN PRACTICE

Tested Under Real Attack Conditions. Tuned to Close the Gaps.

A detection program should be judged by what it catches, not by how many alerts it produces. TrollEye combines continuous monitoring with adversarial validation, so you know which controls hold up against a real threat actor and which ones need work.

CASE STUDY

How General Bank of Canada Validated Years of Security Investment Against Real-World Attacks.

See how TrollEye tested whether technical, human, physical, and response controls could withstand a sophisticated threat actor, including how detection, containment, and recovery held up under realistic pressure.

Read This Case Study →
4Control layers tested together: technical, human, physical, and response
3Related organizations included in the engagement
ValidatedDetection, containment, and recovery processes worked under realistic pressure
01
OPERATIONAL TUNING ALONE

Suppresses noisy rules so the SIEM gets quieter, but never shows what an attacker could do undetected.

02
ADVERSARIAL TUNING WITH TROLLEYE

Emulates real techniques, finds the blind spots, and engineers detections until they fire.

DETECTION & RESPONSE FOR CTEM

Managed SIEM Is How Detection Enters Your CTEM Program.

Continuous Threat Exposure Management requires more than identifying exposures. You also need to know whether attackers are actively trying to exploit them, and whether your controls would detect and stop them if they did.

Managed SIEM & Purple Teaming is the detection and response component of TrollEye’s CTEM solution. Its core work happens in Validation, proving whether your controls detect real attack techniques, and Mobilization, driving response and detection fixes. It also supports scoping, discovery, and prioritization inside the same platform you use for the rest of your exposure.

THE FIVE CTEM STAGES, APPLIED TO DETECTION & RESPONSECORE STAGES FOR MANAGED SIEM & PURPLE TEAMING
STAGE 01

Scoping

Define the critical assets, log sources, business functions, and threat actors your detection and response program must cover.

Defines log sources & threat scenarios Explore Scoping →
STAGE 02

Discovery

Continuously surface active threats, misconfigured controls, and missing telemetry across endpoints, identities, network, and cloud.

Surfaces active threats & telemetry gaps Explore Discovery →
STAGE 03

Prioritization

Rank alerts and exposures by active threat, asset criticality, and business impact, in context with the rest of your attack surface.

Ranks alerts by active threat Explore Prioritization →
CORE STAGE STAGE 04

Validation

Prove which attack paths are actually exploitable and reachable, and whether your controls detect them, through purple team exercises.

Proves what detection would miss Explore Validation →
CORE STAGE STAGE 05

Mobilization

Route incidents and detection gaps to the teams that own them, tune detections and playbooks, and fix root causes so gaps don’t recur.

Drives response & detection fixes Explore Mobilization →
INSIDE OUR CTEM PACKAGES

Detection Gaps Don’t Exist In Isolation.

Within our CTEM packages, detection gaps and active threats are correlated with application, cloud, identity, and network exposures, helping your team focus on the remediation activities that will have the greatest impact on overall risk reduction.

QUESTIONS SECURITY LEADERS ASK

Before You Outsource Your SOC, Ask Better Questions.

A managed SIEM should do more than forward alerts. Here are the questions buyers ask when evaluating Managed SIEM & Purple Teaming, how TrollEye proves detection works, and how it fits into a CTEM program.

MONITORINGPURPLE TEAMINGRESPONSECTEM
01 How is this different from a traditional managed SIEM service?

Most managed SIEM providers focus on log aggregation and alerting, and tune rules mainly to reduce noise. TrollEye manages ingestion, correlation, and response too, but we also emulate real attacker behavior to test whether your detections and response processes actually work.

Gaps found in those exercises feed directly into detection engineering. The result is fewer missed threats, faster response, and detections that get better over time instead of just quieter.

02 What is the role of purple teaming in this service?

Purple teaming brings offensive (red) and defensive (blue) work together. Our operators emulate current threat actor tactics, techniques, and procedures (TTPs), then measure how well your tools, playbooks, and people detect and respond.

Every technique is checked for whether it was logged, alerted on, escalated, and contained. Those results drive detection rule tuning and incident response refinement, making your defenses more resilient with every exercise.

03 How does Managed SIEM & Purple Teaming fit into a CTEM program?

It provides the detection and response component of TrollEye's CTEM solution, applying each stage to your defensive controls: scoping, discovery, prioritization, validation, and mobilization.

That means scoping the assets and log sources that matter, discovering active threats and missing telemetry, prioritizing by active threat and business impact, validating which attack paths are exploitable and reachable and whether controls detect them, and mobilizing teams to close the gaps.

04 Do we need to replace our existing security tools?

No. The service is designed to work with the tools you already rely on. The TrollEye platform integrates with EDR tools such as CrowdStrike, SentinelOne, and Carbon Black, and with cloud providers including AWS, Azure, and Google Cloud.

During onboarding, we scope which data sources to bring in based on your environment, critical assets, and detection priorities.

05 Will this add work for our internal team?

It is designed to do the opposite. Our analysts handle 24/7 monitoring, triage, and investigation, and our experts run purple team exercises and detection tuning.

Your team receives confirmed incidents and clear, prioritized actions, without having to staff and manage a full internal SOC.

06 How often are purple team exercises run?

Exercise cadence is scoped to your environment, threat profile, and goals. Because attackers and environments change, exercises run on an ongoing basis rather than once a year.

Techniques are re-run after tuning to confirm new detections fire, so improvements are proven, not assumed.

STILL EVALUATING? See how your detections hold up against a real adversary.

Walk through your environment, tooling, and detection goals with our team.

EXPERIENCE MANAGED SIEM & PURPLE TEAMING

Detect Faster. Prove Your Defenses Work.

Our team operates your detection and response program alongside you, monitoring around the clock, testing your defenses against real adversary techniques, and turning every gap into a stronger detection. Reach out to see how Managed SIEM & Purple Teaming strengthens your CTEM program.

  1. 0124/7 SIEM monitoring and alert triage
  2. 02Purple team exercises against real adversary TTPs
  3. 03Detection engineering that closes every gap
  4. 04Continuous validation of detection coverage

Conversations with CISOs

Live CISO Roundtable & AMA

Doing More with Less

Four security leaders. One candid conversation about budgets, teams, security tools, and the tradeoffs CISOs face heading into 2027.

October 29, 2026 • 2:00 PM ET • Live Online

Join the Conversation With

Jeff Moore Jeff Moore CISO, H&M
Elizabeth Di Bene Elizabeth Di Bene CISO, Loudon County
JoJo D JoJo D Cyber Leader, Co-Founder of Chaos & Signal
Aby Rao Aby Rao Deputy CISO, Fintech
Register & Submit Your Questions →

This Content Is Gated