TrollEye Security

CONTINUOUS THREAT EXPOSURE MANAGEMENT

Manage Exposure in One Place. Reduce Risk Continuously.

Centralize exposure management and streamline risk reduction through a native CTEM platform backed by expert security services.

STARTING AT $995 /month Native CTEM Platform • 14-day free trial
NATIVE CTEM PLATFORM SCOPING • DISCOVERY • PRIORITIZATION • VALIDATION • MOBILIZATION
EXPERT SECURITY SERVICES TESTING • VALIDATION • EXPERTISE
Cloud
Identity
Infrastructure
Applications
External
Threat Data
Third Party
TROLLEYE Unified Exposure
Management

Native CTEM Platform
+ Expert Security Services

Prioritized Risk
Validated Exposure
Coordinated Remediation
Measurable Progress
Continuous Risk Reduction

TRUSTED ACROSS FINANCIAL SERVICES, HEALTHCARE, TECHNOLOGY & UTILITIES
FROM EXPOSURE MANAGEMENT TO OUTCOMES

One Solution. Three Outcomes.

TrollEye combines a unified CTEM platform with expert services to help security teams operate more efficiently, reduce risk, and continuously prove improvement.

01
OPERATE

Integrated Security Operations

Manage exposure across your attack surface through one continuous CTEM solution.

Full Attack Surface Infrastructure, apps, cloud, identities, external assets, people & third parties.
Native CTEM Capabilities Discovery, testing, prioritization, validation, remediation & measurement.
Operational Integrations Connect cloud, EDR, code, firewall & remediation workflows.
02
REDUCE

Reduced Risk

Focus teams on the exposures that matter and drive them toward verified resolution.

Validate Exposure Confirm what is real, exploitable and relevant.
Prioritize Risk Exploitability, attack paths, threats & business context.
Fix + Verify Ownership, expert guidance, retesting & root-cause resolution.
03
PROVE

Measurable Security Improvement

Track progress over time and demonstrate measurable security improvement.

Continuous Evidence Testing, remediation and validation history.
Compliance Support SOC 2, HIPAA and PCI DSS testing requirements.
Verified Improvement Retesting and historical results help show that security improvements are working.
CTEM PLANS STARTING AT $995 / month
Ready to operationalize CTEM? Start with the platform and add expert services based on your security needs.
Explore Pricing
CUSTOMER PERSPECTIVE
“They operate as a true partner, embedding into our DevSecOps workflows and working directly with our engineering teams to improve processes and drive remediation.”
Ricoh Danielson Enterprise CISO at CorroHealth
HEAR FROM RICOH How CorroHealth approaches continuous security.
Watch Full Interview
THE TROLLEYE CTEM PLATFORM

One Platform to Manage Every Exposure

Manage exposure across your attack surface from one place. TrollEye brings scoping, discovery, prioritization, validation, and mobilization together so your team can move from defining what matters to continuously reducing risk.
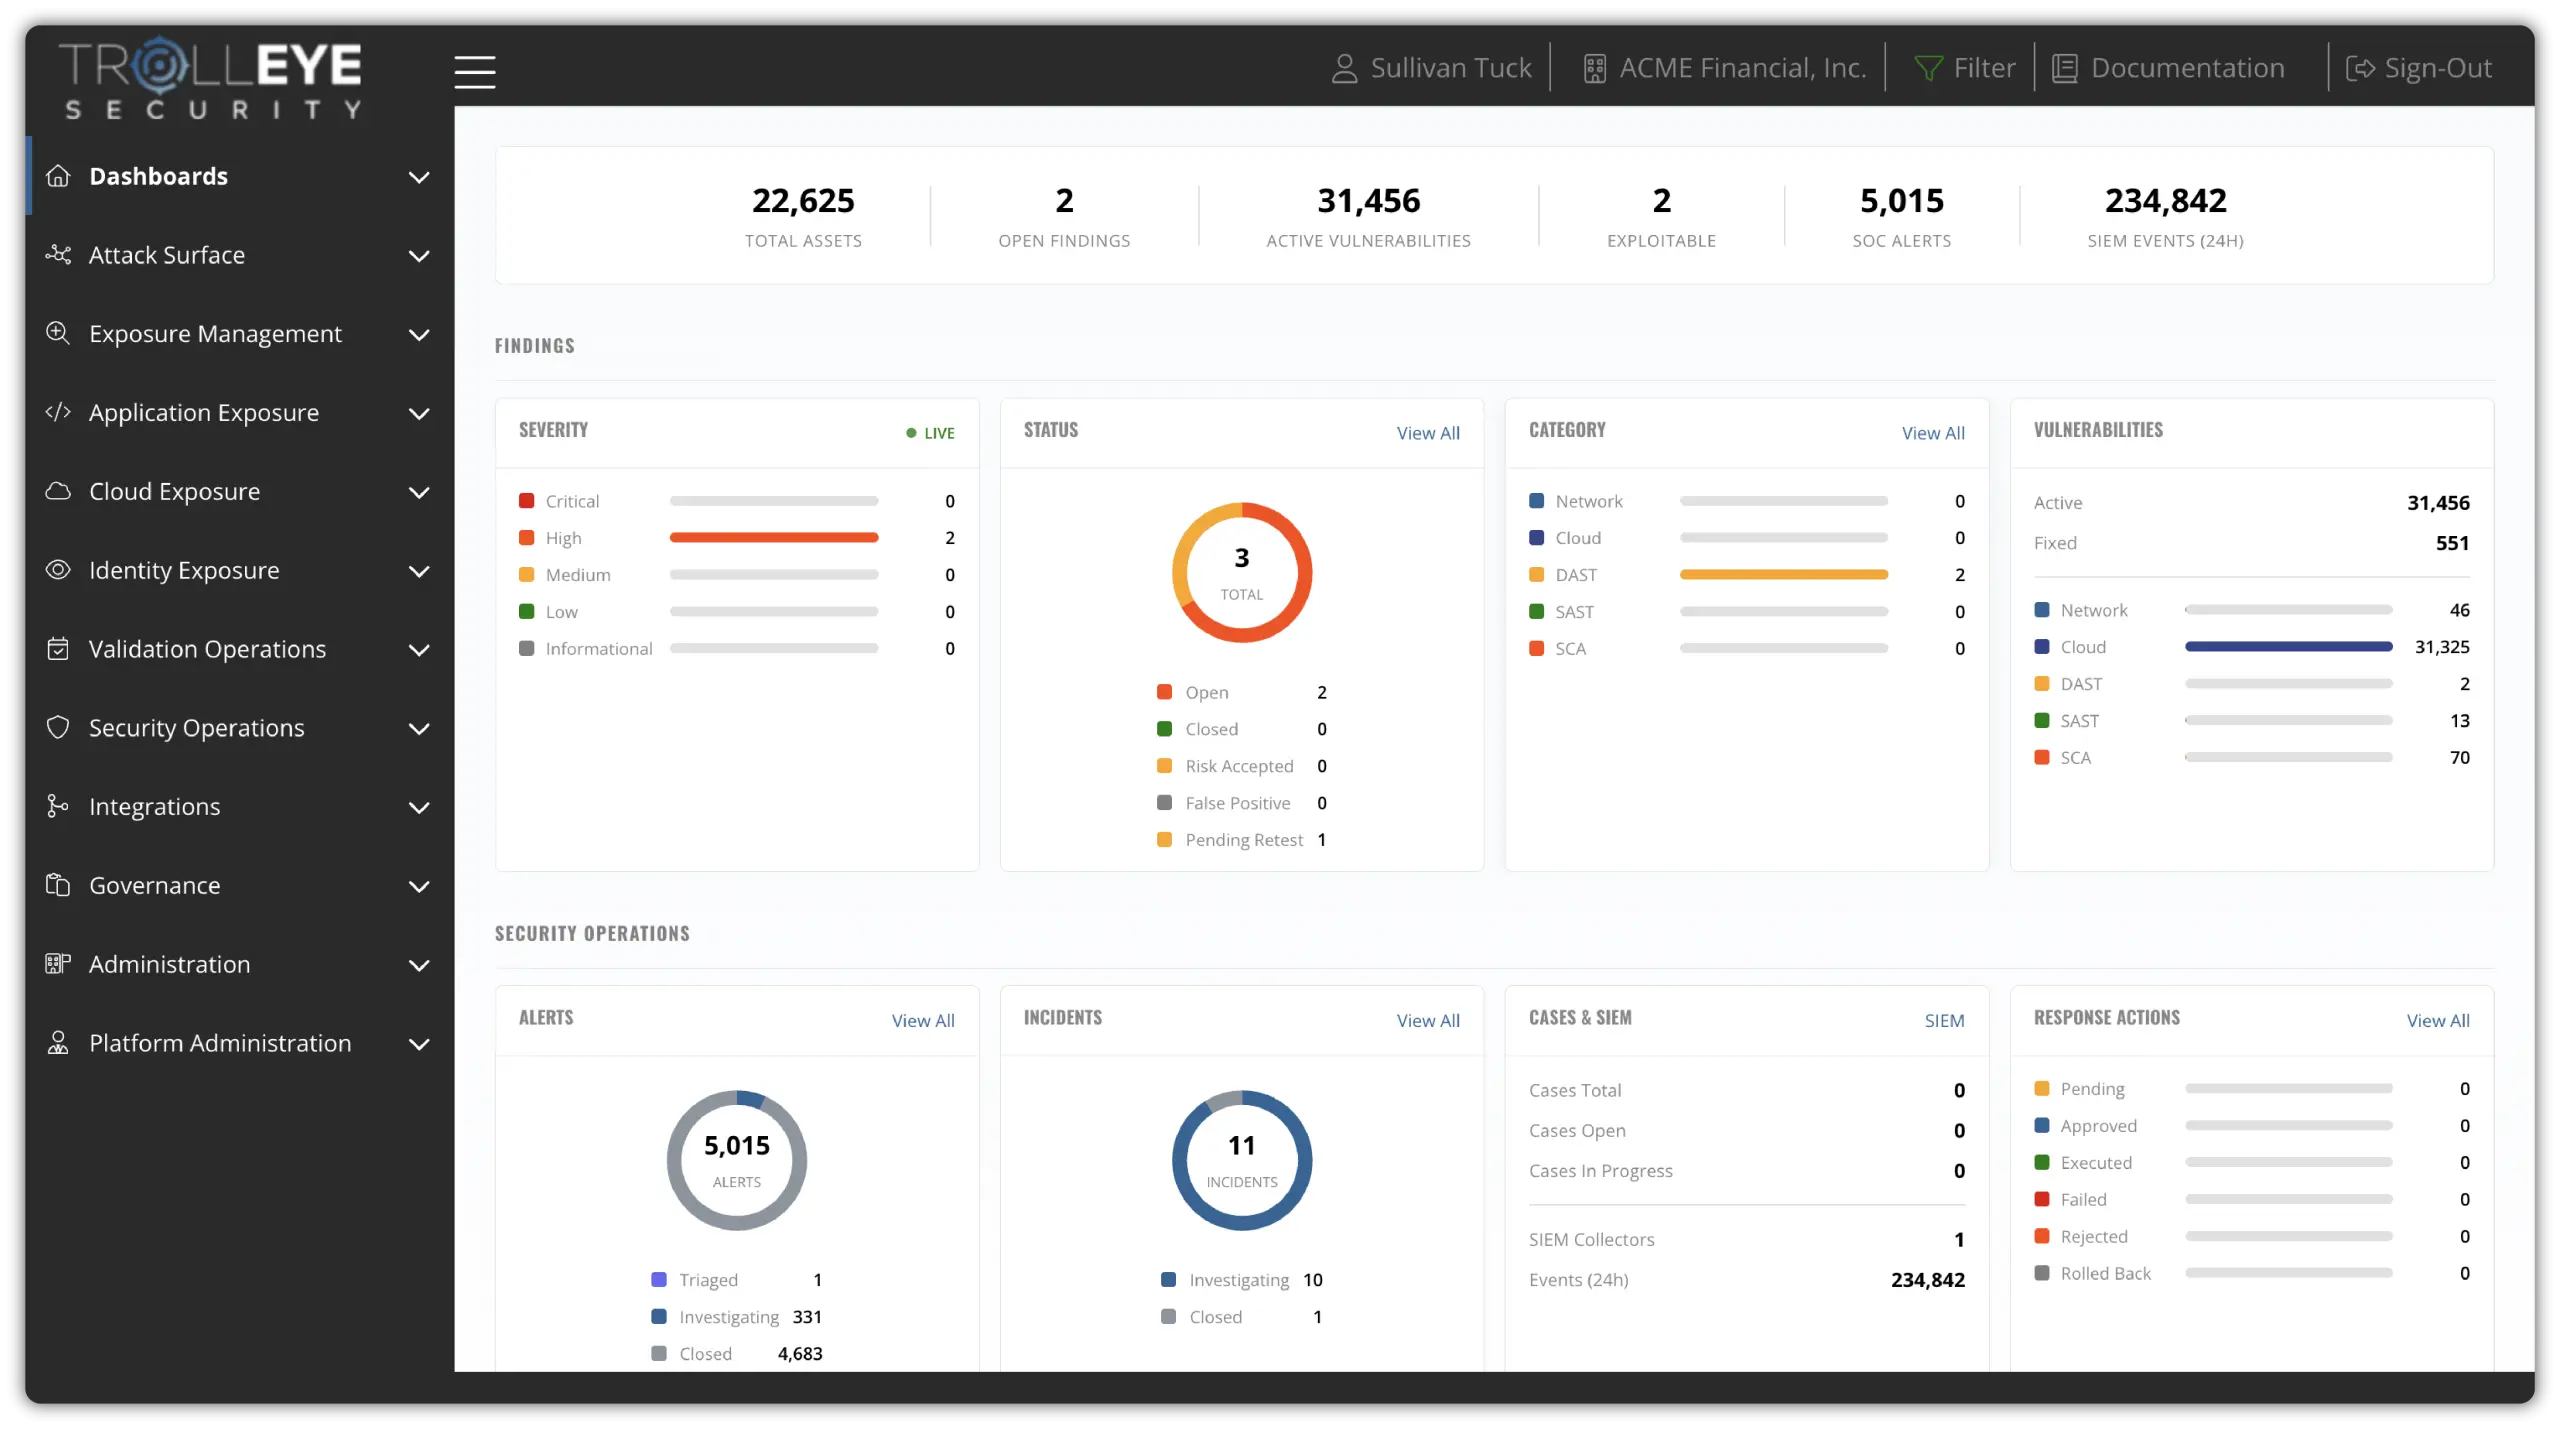
TrollEye CTEM Platform dashboard
FROM EXPOSURE TO RESOLUTION

Manage the Full Exposure Lifecycle

Give your team the visibility, context, validation, and workflows to continuously move exposures toward resolution and measurable risk reduction.

01 · SCOPE

Define What Matters

Establish the assets, business priorities, attack surface, and security context that should shape your exposure strategy.

02 · DISCOVER

See the Attack Surface

Continuously identify exposures across infrastructure, applications, cloud, identities, external assets, people, and third parties.

03 · PRIORITIZE

Know What Matters

Focus on exposures using exploitability, attack paths, threat intelligence, asset criticality, and business context.

04 · VALIDATE

Confirm Real Risk

Determine what attackers can actually exploit through automated validation and expert-led security testing.

05 · MOBILIZE

Drive Resolution

Assign ownership, coordinate remediation, address root causes, retest fixes, and track exposure through resolution.

EXPERT SECURITY SERVICES

Expert Services That Turn Exposure Into Action

Extend the TrollEye CTEM Platform with hands-on security expertise to validate risk, uncover complex attack paths, strengthen defenses, and help your team drive remediation.

PLATFORM + EXPERTISE Your team stays in control. Our experts help you move faster.
Explore CTEM Services
PROVEN IN REAL SECURITY PROGRAMS

Measurable Results. Not More Security Activity.

TrollEye helps security teams turn continuous exposure management into measurable improvement, reducing risk, increasing testing coverage, and building security programs that improve over time.

97.5%
MEASURABLE RISK REDUCTION Fewer Vulnerabilities

Achieved by an Austin fintech through continuous CTEM validation and remediation.

12×
MORE CONTINUOUS TESTING

Up to 12× more testing for less than 2× the cost of traditional annual penetration testing.

7+ yrs
LONG-TERM PARTNERSHIPS

Some of our longest-serving clients have trusted TrollEye for more than seven years.

SEVEN YEARS OF SECURITY LEADERSHIP We’ve never had a CISO or security leader we work with lose their job as the result of a security incident.

Long-term partnerships built around measurable risk reduction, continuous validation, and helping security leaders show meaningful progress over time.

They operate as a true partner, embedding into our DevSecOps workflows and working directly with our engineering teams to improve processes and drive remediation.
Ricoh Danielson
Ricoh Danielson Enterprise CISO, CorroHealth
TrollEye's approach of employing various attack vectors, from dark web analysis to physical breach attempts, demonstrated their understanding of the complex nature of modern cybersecurity threats facing financial institutions. It's simple, yet powerful.
Adam Ennamli
Adam Ennamli Chief Risk Officer, General Bank of Canada
SEE HOW IT WORKS TOGETHER

Platform + Expertise. One Continuous CTEM Program.

See how TrollEye combines the CTEM Platform with expert security services to continuously identify, prioritize, validate, and reduce exposure across your attack surface.

QUESTIONS SECURITY LEADERS ASK

Before You Add Another Security Tool, Ask Better Questions.

CTEM should do more than create another place to review findings. Here are the questions buyers ask when evaluating TrollEye, continuous exposure management, and the role expert services play alongside the platform.

PLATFORM SERVICES VALIDATION PRICING
01 How is TrollEye different from a vulnerability management platform?

Vulnerability management typically centers on identifying and tracking vulnerabilities. TrollEye is built around the broader CTEM lifecycle: scoping, discovery, prioritization, validation, and mobilization.

That means the goal is not simply to generate a larger findings list. TrollEye brings together exposure discovery, business and asset context, exploitability, attack paths, validation, ownership, remediation initiatives, retesting, and measurement so teams can continuously move from exposure to verified risk reduction.

02 Is TrollEye an aggregator that pulls findings from our existing tools?

No. TrollEye is a native CTEM solution, not a dashboard layered on top of a collection of scanners. The platform includes native capabilities for identifying, prioritizing, validating, managing, and measuring exposures.

TrollEye can connect to parts of your environment for additional asset and security context, but its value does not depend on aggregating findings from a stack of separate exposure products.

03 What does implementation require from our team?

TrollEye is designed to start producing useful exposure context without turning implementation into a major security project. Teams can begin by verifying their domain, reviewing their external attack surface and identity exposure, and then expand coverage based on the environment and the CTEM capabilities they need.

From there, cloud, code, endpoint, firewall, collaboration, and remediation workflow connections can add context and help fit TrollEye into existing security and engineering operations.

04 How does TrollEye decide which exposures actually matter?

Severity is only one input. TrollEye can add context such as exploitability, threat intelligence, attack paths, compensating controls, asset ownership, business criticality, and confidentiality, integrity, and availability impact.

The result is a more useful decision model: not simply “what is technically severe?” but “what creates meaningful exposure in this environment, and what should the team address first?”

05 What happens after TrollEye finds an exposure?

Discovery is the beginning, not the outcome. TrollEye adds the context needed to determine what matters, validates risk, and helps move prioritized exposures to the people who can act on them.

The operating flow is straightforward: Finding → Context → Priority → Owner → Action → Verification. Teams can coordinate remediation initiatives, track ownership and timelines, request retesting, and maintain evidence that the exposure was actually reduced rather than simply marked complete.

06 What does “validation” mean in practice?

Validation is about determining whether an exposure represents real, relevant risk rather than treating every finding as equal. TrollEye combines automated validation with human-led testing where deeper expertise is needed.

Expert services such as penetration testing, purple teaming, DevSecOps, and other hands-on testing can provide additional evidence around exploitability, attack paths, control effectiveness, and remediation decisions.

07 Does TrollEye automatically remediate vulnerabilities for us?

Today, your team stays in control of remediation. TrollEye helps move validated exposures into coordinated action through ownership, role-based workflows, remediation initiatives, timelines, Jira-supported workflows, expert guidance, and retesting.

Agentic remediation capabilities are on our roadmap. The direction is to help teams move even faster from validated exposure to remediation while keeping the process controlled and verifiable.

08 Do we need to buy the expert services to use the CTEM platform?

The platform and expert services are designed to work together, but services can be added based on the depth of expertise and testing your organization needs.

Some teams primarily need the technology to continuously manage exposure. Others use TrollEye experts for deeper validation, penetration testing, application security, dark web analysis, detection testing, or remediation guidance. The combination can expand as your needs change.

09 Can TrollEye replace security tools we already pay for?

In some environments, yes. TrollEye is designed to consolidate capabilities across exposure management and validation rather than become another layer on top of them.

Depending on your current stack and requirements, organizations may be able to consolidate capabilities associated with SAST, DAST, SCA, penetration testing, breach and attack simulation, dark web analysis, and SIEM. The right answer depends on what each existing product is doing in your environment, so replacement should be evaluated capability by capability.

10 How do we show leadership that risk is actually going down?

Closing a ticket is not the same as proving risk reduction. TrollEye maintains exposure history and supports retesting so teams can connect completed work back to measurable changes in the security environment.

That gives security leaders a clearer story around what mattered, what was addressed, what was verified, and how exposure is changing over time rather than reporting activity alone.

11 How much does TrollEye cost, and can we try it before buying?

Automated CTEM plans start at $995 per month. Eligible packages include a 14-day free trial so teams can begin reviewing their own attack surface and exposure data before committing.

Expert services can be added based on scope and need, allowing organizations to start with the level of platform and expertise that makes sense for their security environment.

12 How quickly can we start getting value from TrollEye?

You do not have to wait for a long implementation cycle to begin seeing useful exposure data. The initial experience is designed to get teams into their own environment quickly: start the trial, verify your domain, review your attack surface, and check identity exposure.

Eligible packages include a 14-day free trial. From there, coverage and workflows can expand as TrollEye becomes part of the organization's continuous exposure management process.

STILL EVALUATING? See the platform in your environment, not just on a slide.

Start with your attack surface and see how TrollEye moves exposure toward action.

Take the Next Step

See How TrollEye Can Support Your Exposure Management Program

Start with a conversation about your attack surface, current security stack, and remediation challenges. We’ll show you how the TrollEye platform can unify exposure management and help your team continuously reduce risk.

What to Expect

A Clear Path From Introduction to Implementation

01

Discovery Call and Platform Demo

We’ll learn about your environment, priorities, existing tools, and remediation challenges, then demonstrate how TrollEye can support your program.

02

Get Access to the Platform

Explore the platform directly and see how your team can centralize exposures, prioritize risk, and coordinate remediation in one place.

03

Finalize the Scope and Launch

Together, we’ll finalize the right platform capabilities, services, integrations, and scope for your organization.

Begin continuously identifying, prioritizing, validating, and reducing exposure
Live Webinar

From Discovery to
Risk Reduction

Operationalizing CTEM in Modern Security Programs

Date September 24, 2026
Time 2:00 PM Eastern

Learn how modern security teams can move beyond finding exposures and operationalize every stage of Continuous Threat Exposure Management.

01 Scope
02 Discover
03 Prioritize
04 Validate
05 Mobilize
Reserve Your Spot

Free registration · Live discussion and Q&A

This Content Is Gated