TrollEye Security

THREAT MODELING

Identify Security Risks Early With Threat Modeling.

Stop paying to fix in production what you could have prevented in design. Security flaws are often introduced long before testing begins, when architectural decisions quietly create attack paths that are difficult and costly to fix later.

TrollEye evaluates your architecture, data flows, trust boundaries, and user interactions to eliminate exploitable flaws before a single line of code is written, then carries every design-level exposure into your Continuous Threat Exposure Management (CTEM) program.
Secure by Design
STRIDE-Based Analysis
Fewer Downstream Fixes
CTEM-Aligned
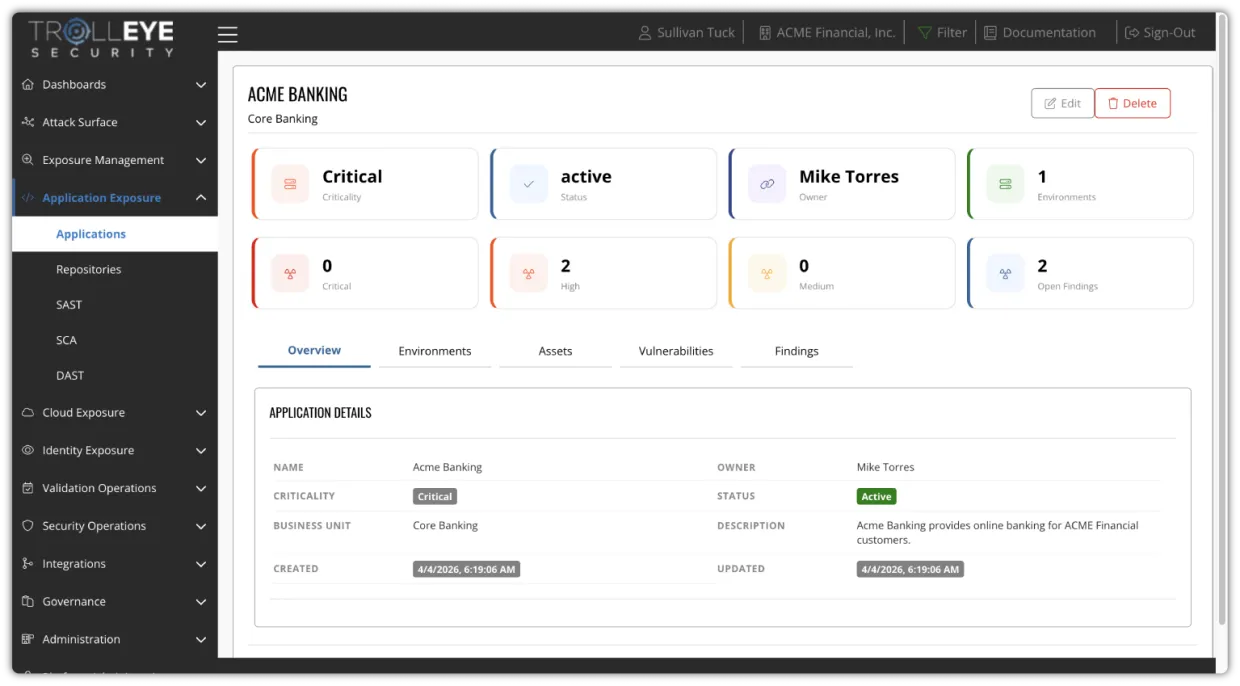
TrollEye platform application exposure view
THREAT MODELINGDesign risk feeds your CTEM program
THE OUTCOME 97.5% Reduction in vulnerabilities with DevSecOps
SECURE BY DESIGN, NOT BY RETROFIT

Design Secure Systems Before the First Line of Code.

Security isn't just about fixing issues, it's about designing systems that avoid them from the start. As part of our DevSecOps solution, Threat Modeling helps your teams identify, prioritize, and mitigate potential threats during the design and architecture phase.

Using proven frameworks such as STRIDE, we categorize and prioritize threats so your teams can make informed, risk-based design decisions, reduce downstream vulnerabilities, and build more resilient applications from day one.

01

Stronger Security Architecture

Identify design weaknesses early so security controls are built into system architecture rather than added after development.

02

Fewer Downstream Vulnerabilities

Address risks during the design phase to reduce the number of security issues discovered later in testing or production.

03

Proactive Risk Identification

Analyze potential attack paths and abuse scenarios early to prevent exploitable weaknesses before development progresses.

OUTCOME 01

Understand Attack Paths Before Development Progresses.

Threat modeling provides structured visibility into how attackers might interact with a system’s architecture, integrations, and data flows. This early perspective helps teams evaluate risk before design decisions become difficult to change.

01

Map data flows and trust boundariesSee where sensitive data moves and where trust changes hands across your architecture.

02

Surface abuse scenariosIdentify how real attackers could misuse features, integrations, and user interactions.

03

Act while designs are flexibleAddress risk when changes cost hours, not release cycles.
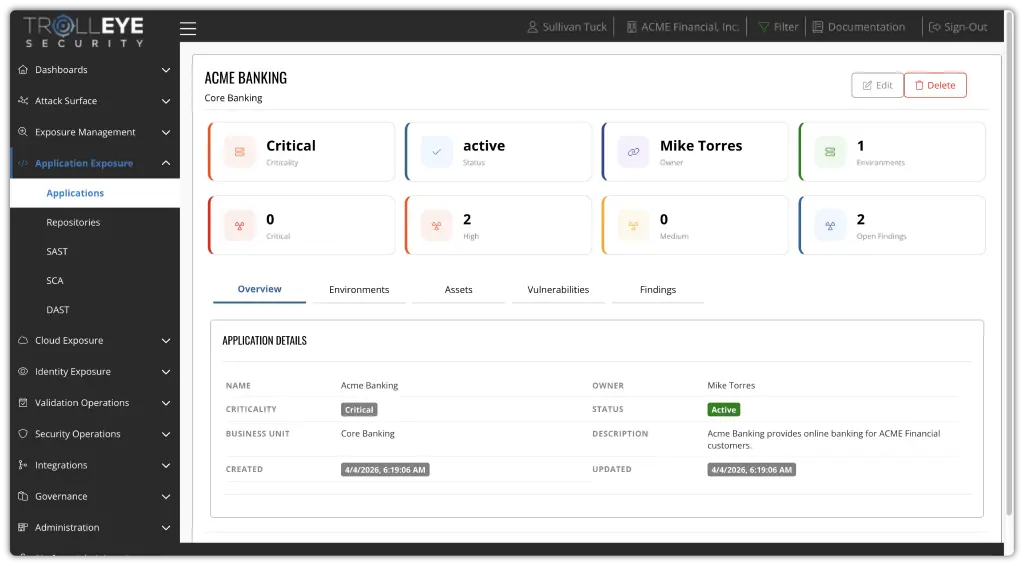
TrollEye application exposure view
OUTCOME 02

Guide Architectural Choices With a Clear Understanding of Risk.

Security considerations are incorporated directly into system planning, helping teams choose appropriate controls, authentication models, and data protections while designs are still flexible.

01

Categorize threats with STRIDEClassify risks across spoofing, tampering, repudiation, information disclosure, denial of service, and elevation of privilege.

02

Prioritize by impactRank threats by likelihood and business impact instead of treating every risk the same.

03

Define the right controlsTranslate prioritized threats into clear security requirements and mitigations.
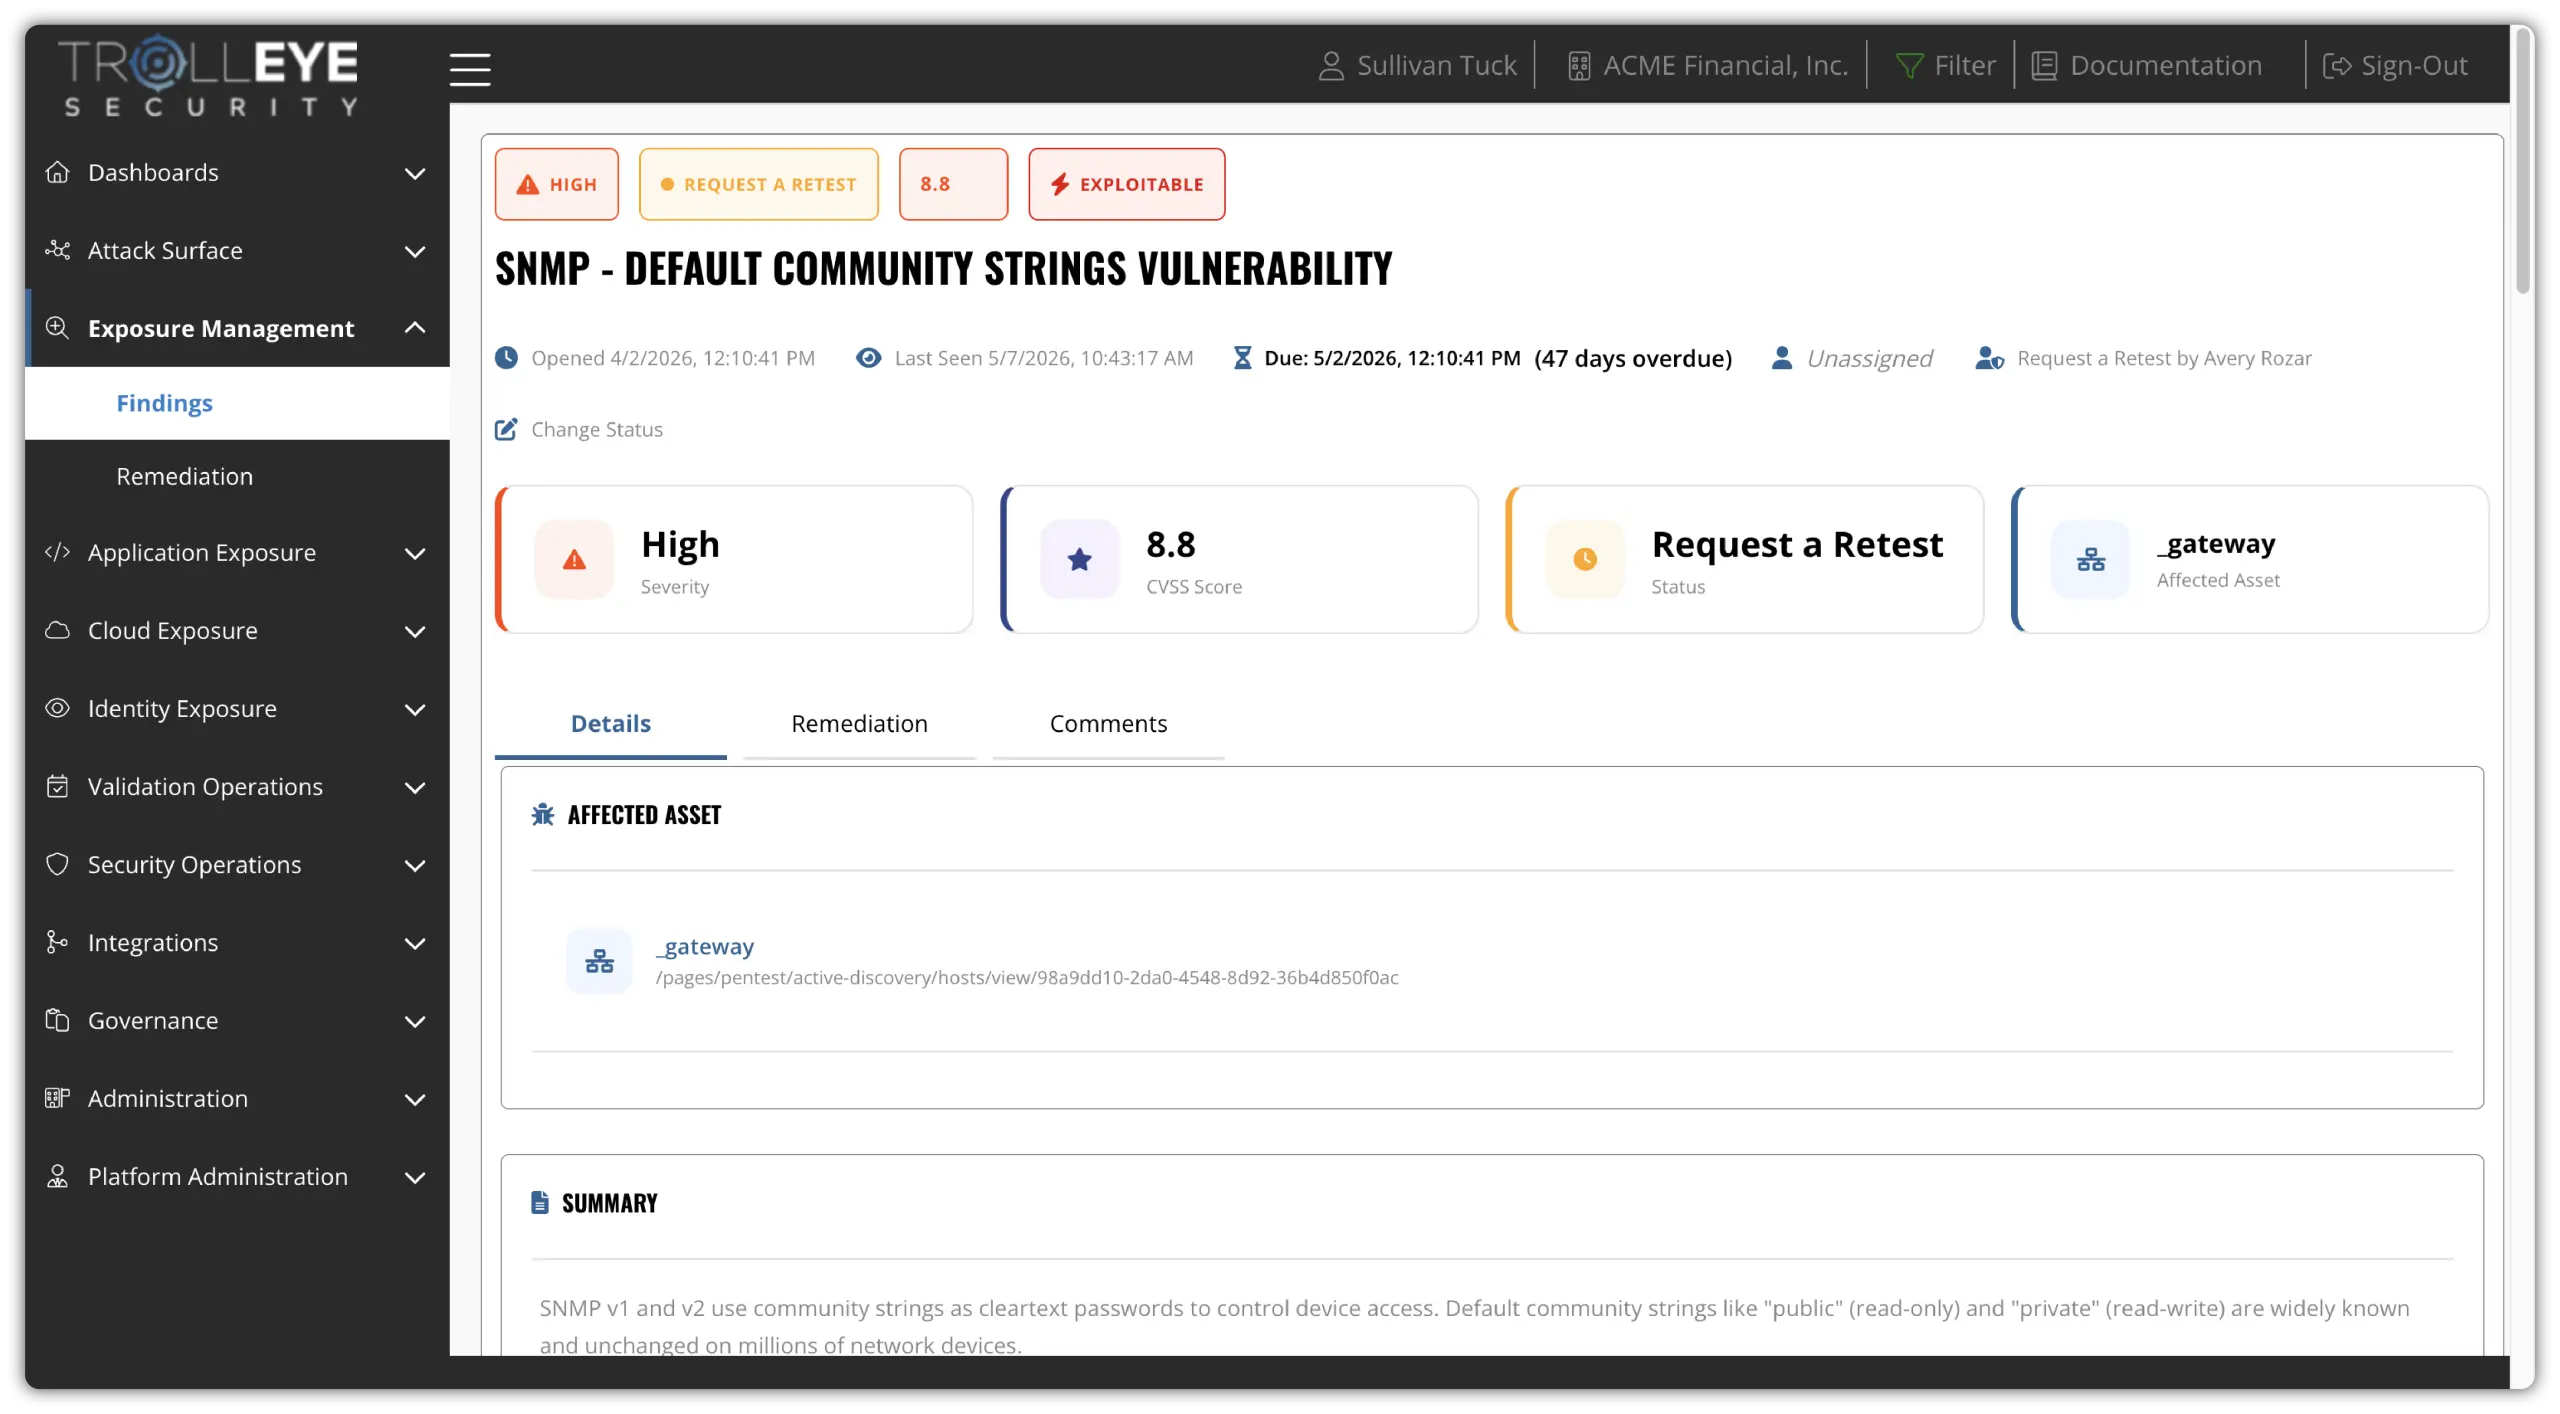
TrollEye detailed finding view
OUTCOME 03

Align Developers, Architects, and Security Teams Early.

Threat modeling creates a shared understanding of system behavior and potential abuse scenarios. This encourages productive collaboration during planning rather than reactive discussions when issues surface later in development.

01

One shared view of riskGive every team the same picture of how the system can be attacked.

02

Collaborate during planningResolve security questions in design reviews, not release-day escalations.

03

Hand off clear requirementsRoute mitigations into the workflows your developers already use.
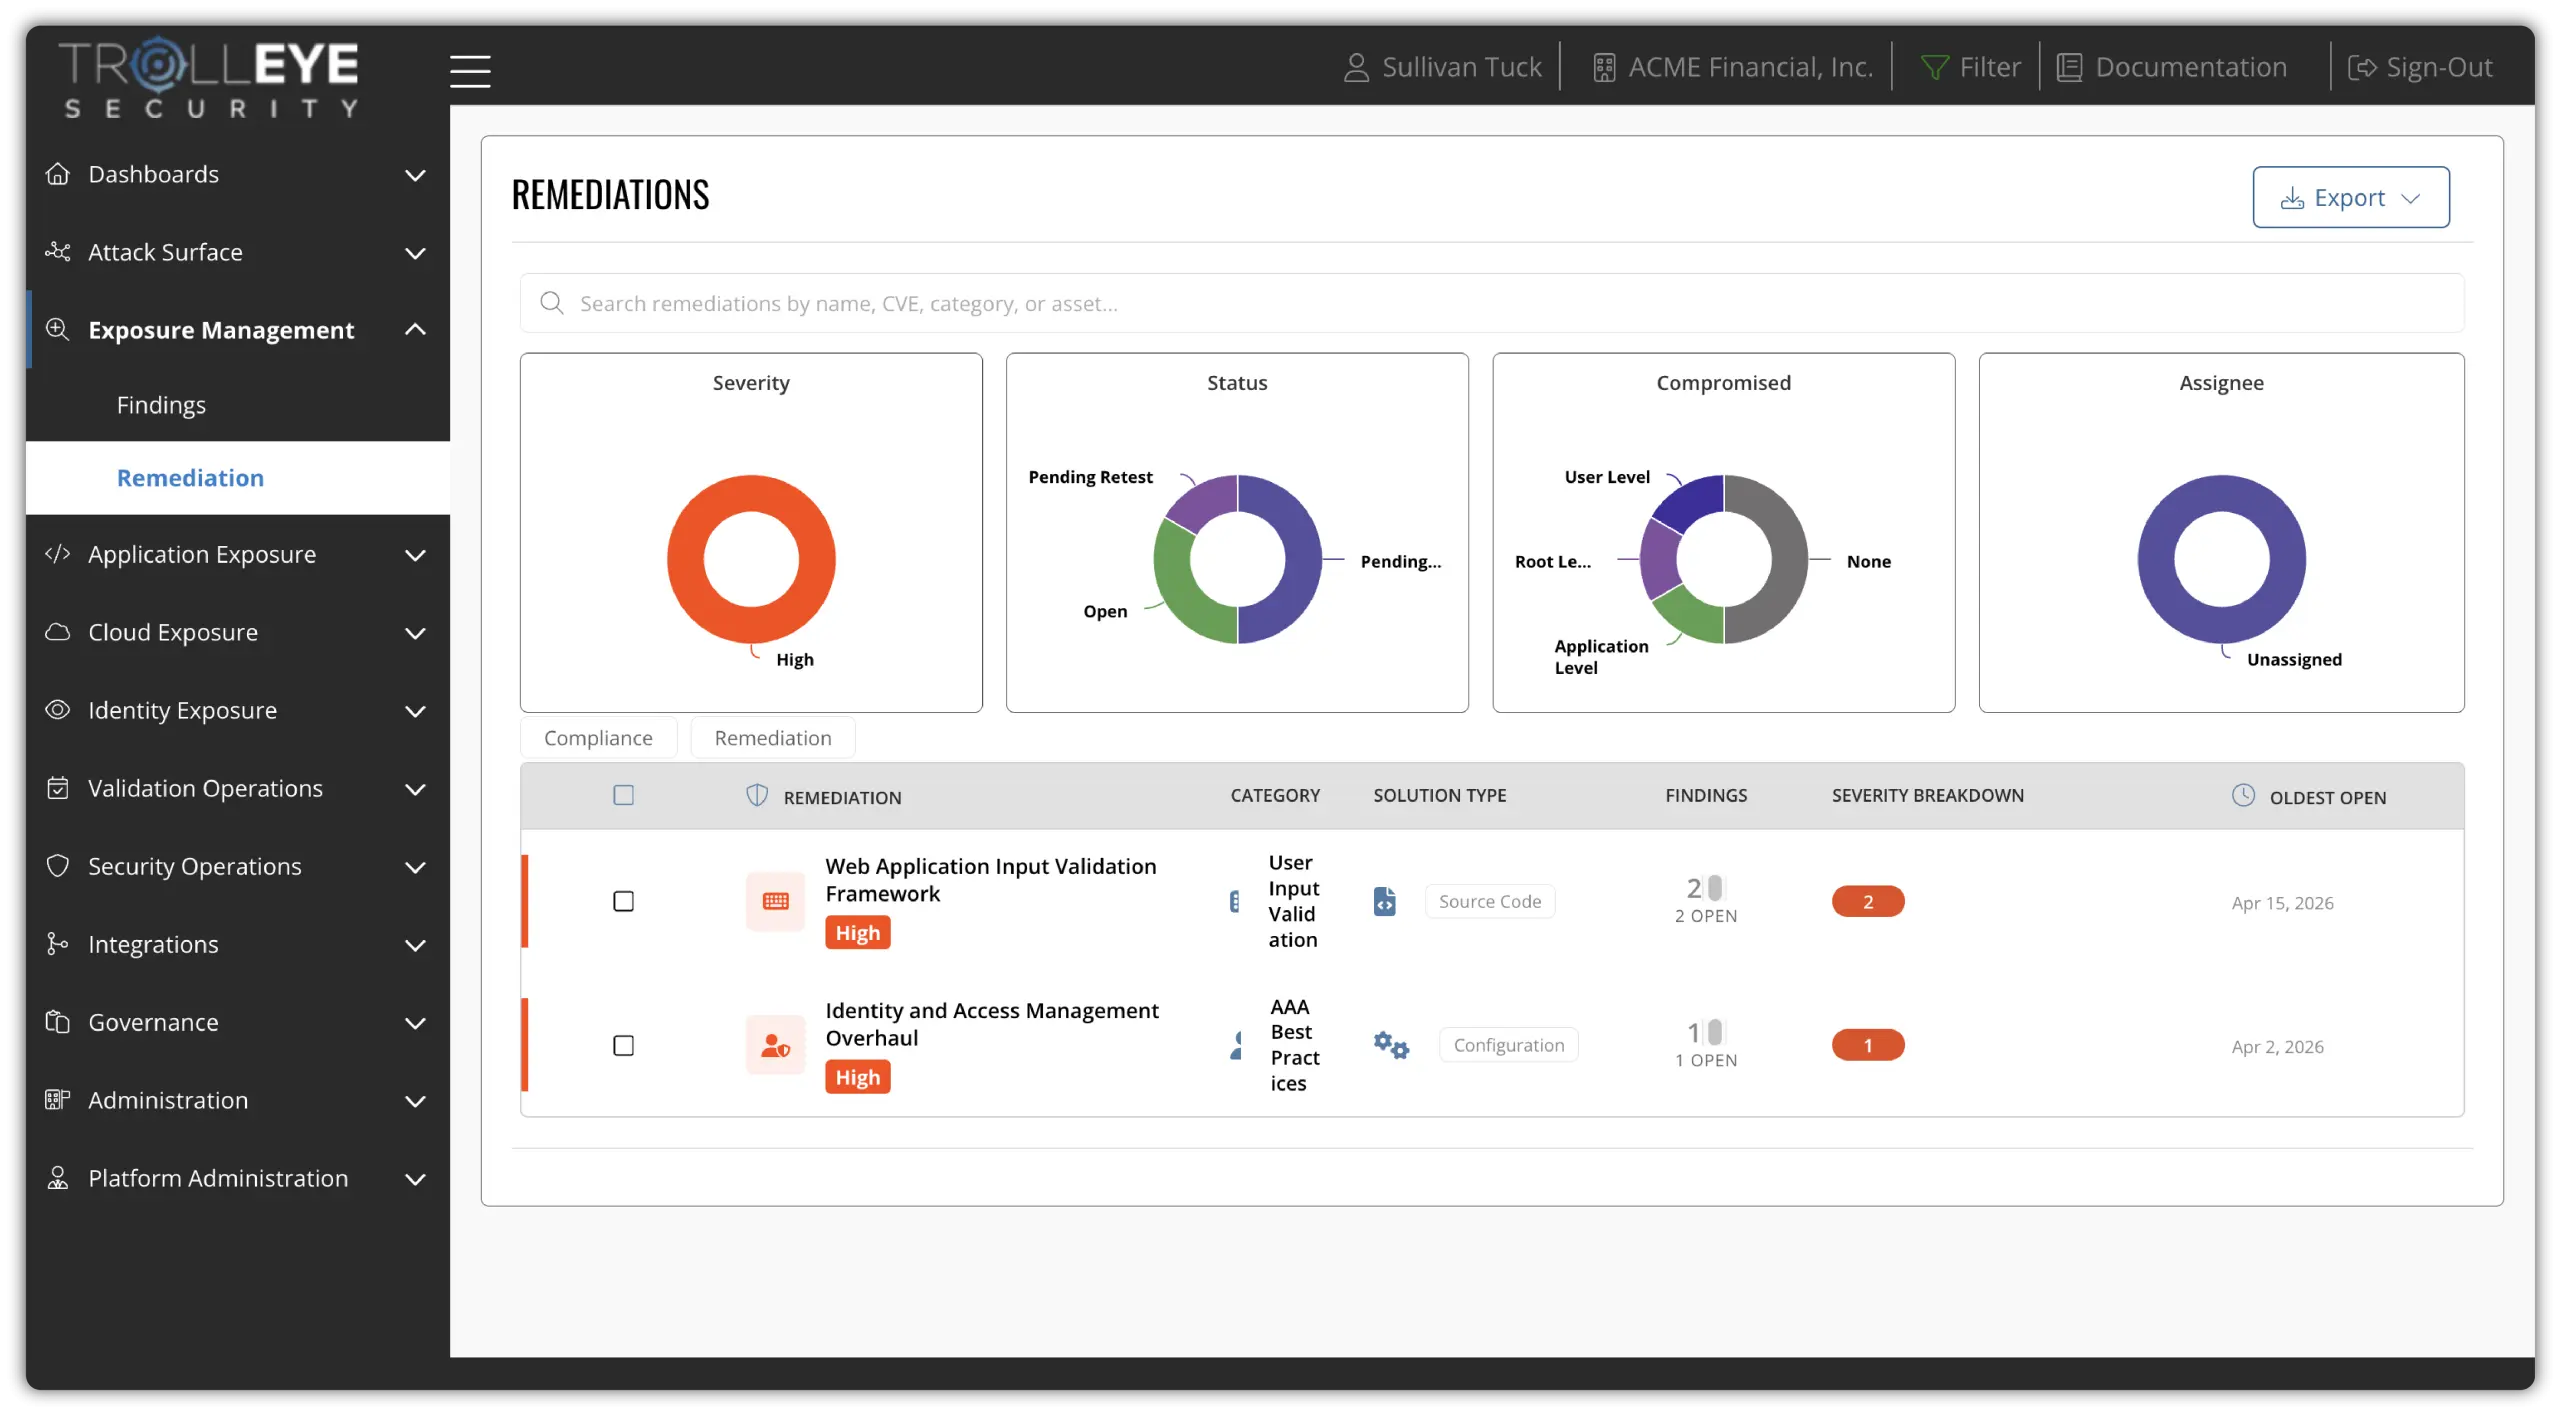
TrollEye remediation initiatives
OUTCOME 04

Reduce Systemic Weaknesses Across Future Releases.

Addressing architectural risks early helps prevent recurring design flaws from appearing across new features, services, and integrations, strengthening overall application resilience as systems evolve.

01

Fix root causes in designEliminate flaw patterns at the source so they don’t recur in every release.

02

Revisit as systems changeUpdate the threat model as new features, services, and integrations are introduced.

03

Measure progress over timeTrack design-level risk alongside the rest of your exposure in one platform.
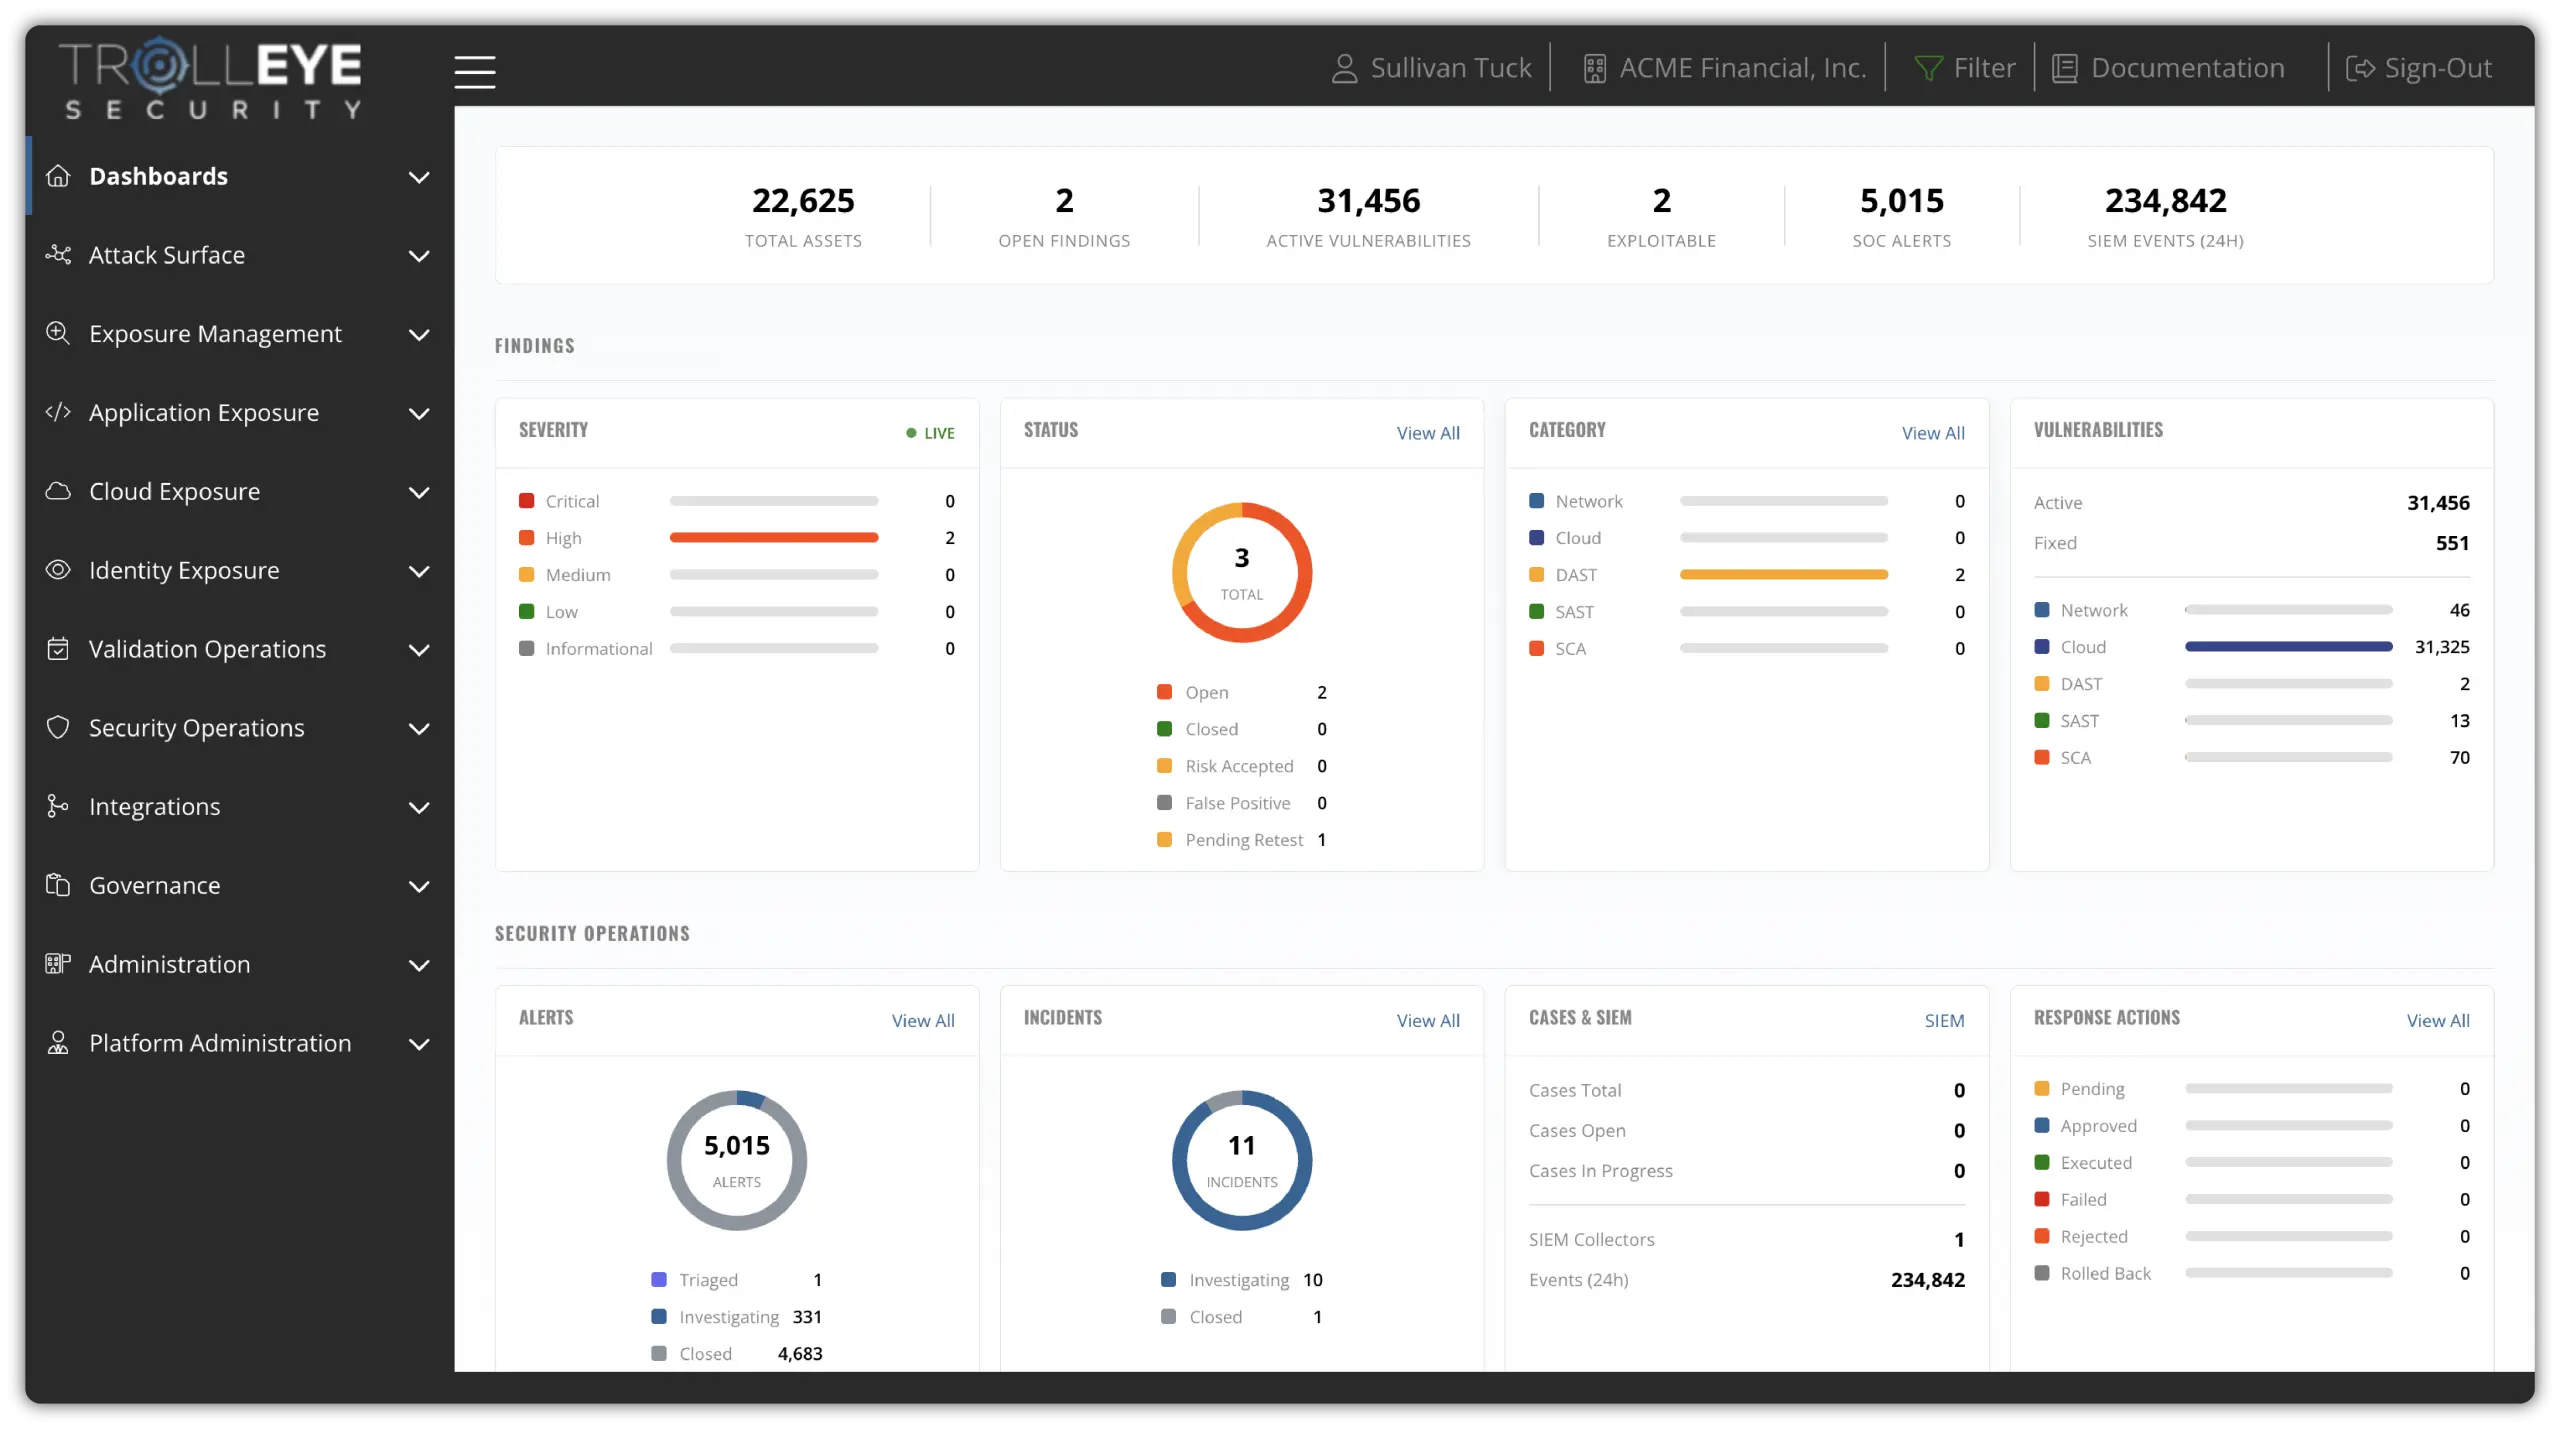
TrollEye exposure management dashboard
PROVEN IN PRACTICE

Recognized by the Industry. Trusted by Engineering Teams.

Threat modeling is the first step in a DevSecOps model recognized by Gartner and trusted by security and engineering teams to deliver measurable improvement, not just another backlog.

CASE STUDY · SOFTWARE COMPANY

How a Software Company Reduced Vulnerabilities by Over 97% with DevSecOps.

97.5%Fewer vulnerabilities
0Critical & high findings
0Known vulnerabilities at release
“We chose DevSecOps because the traditional annual testing model just wasn’t enough. With multiple fintech applications in production, we needed a way to embed security into our development lifecycle, something continuous, scalable, and built to catch issues before they ever made it to production.”
Vice President of Information Security, Software Company Read the Case Study →
What differentiates TrollEye Security is their level of engagement. They operate as a true partner, embedding into our DevSecOps workflows and working directly with our engineering teams to improve processes and drive remediation. Their ‘white glove’ support model is something we didn’t have with previous vendors. They’re responsive, accessible, and willing to engage in real time when needed.
Ricoh Danielson
Ricoh DanielsonEnterprise CISO, CorroHealth
Watch Video
WHERE THREAT MODELING FITS

The Starting Point of a DevSecOps Strategy.

Threat modeling sits at the beginning of the DevSecOps lifecycle, where its impact is greatest. By identifying attack paths, insecure design decisions, and high-risk trust boundaries before code is written, it prevents vulnerabilities from being built into the system, and its outputs guide every practice that follows, from code-level scanning to runtime validation.

01Architecture & Data Flow Decomposition
02Trust Boundary Mapping
03STRIDE Threat Identification
04Abuse Scenario Analysis
05Risk-Based Threat Prioritization
06Security Requirements & Mitigation Guidance
SELECT A STAGE TO SEE HOW THREAT MODELING SHAPES IT Talk with a Threat Modeling Expert →
Dev Ops SEC PLAN Threat Modeling CODE Static Analysis BUILD Build Integrity TEST Penetration Testing RELEASE Release Readiness DEPLOY Code Signing OPERATE Monitor & Detect MONITOR Measure & Report
STAGE 01 OF 08 · PLAN · DEV

Model Threats During Design.

Our Threat Modeling approach evaluates application architecture, data flows, trust boundaries, and user interactions to identify potential abuse scenarios early in the design phase, when changes are fastest and least expensive to make.

01

Architecture Decomposition

Breaks applications into components, integrations, and data flows to understand how the system really works.

02

Trust Boundary Analysis

Identifies where data and privileges cross boundaries that attackers will target.

03

STRIDE Threat Identification

Categorizes threats across spoofing, tampering, repudiation, disclosure, denial of service, and privilege escalation.

04

Abuse Scenario Analysis

Maps how real attackers could misuse features, user interactions, and integrations.

05

Risk-Based Prioritization

Ranks threats by likelihood and business impact so teams focus on what matters.

06

Security Requirements & Mitigations

Turns prioritized threats into clear design controls before development begins.

STAGE 02 OF 08 · CODE · DEV

Point Code Analysis at the Risks That Matter.

Threat modeling surfaces the code-level risks to watch for, such as where user inputs touch sensitive logic, where authentication decisions are made, and where third-party components sit within trust boundaries.

01

SAST

Analyzes source code to validate the specific concerns threat modeling identified, catching insecure patterns before production.

02

SCA

Scans the dependencies threat modeling flagged for known vulnerabilities, outdated packages, and licensing concerns.

03

Secrets Detection

Detects exposed credentials, API keys, and sensitive information where the model shows they could leak.

04

Secure Coding Standards

Verifies code follows the security requirements defined during design.

CTEM ALIGNMENT
STAGE 03 OF 08 · BUILD · DEV

Enforce Critical Controls in Every Build.

Threat modeling defines what must be validated at each stage of development, from code quality to dependency hygiene to infrastructure compliance. Pipeline security embeds those checks directly into CI/CD workflows.

01

CI/CD Security Integration

Ensures every build automatically enforces the controls threat modeling identified as critical.

02

Security Gates

Blocks builds that violate the security requirements defined in design.

03

Pipeline Security Validation

Protects CI/CD workflows against unauthorized modifications and injection attacks.

04

Container Image Scanning

Analyzes container images for vulnerabilities and insecure configurations.

CTEM ALIGNMENT
STAGE 04 OF 08 · TEST · DEV

Test the Attack Paths Threat Modeling Predicts.

Threat modeling maps how attackers could interact with a running system and surfaces the attack paths that matter most. Testing then proves which of those paths are actually exploitable and reachable.

01

DAST

Tests authentication flows, session handling, and exposed endpoints against the scenarios threat modeling predicted.

02

Penetration Testing as a Service (PTaaS)

Agentic and human testing puts chained vulnerabilities, privilege escalation routes, and high-impact entry points to the test.

03

API Security Testing

Validates APIs for authentication flaws, excessive exposure, and insecure endpoints.

04

Business Logic Testing

Targets the abuse scenarios that traditional scanners often miss.

CTEM ALIGNMENT
STAGE 05 OF 08 · RELEASE · OPS

Release With a Clear View of Remaining Risk.

Before release, the threats identified in design are reviewed against what was built, so stakeholders understand remaining exposure and release decisions are properly documented.

01

Mitigation Review

Confirms the design controls defined in the threat model were implemented.

02

Risk Acceptance Review

Documents accepted risks and approved exceptions before release.

03

Compliance Alignment

Supports frameworks such as SOC 2, HIPAA, PCI DSS, and ISO 27001.

04

Security Gate Approval

Confirms security requirements have been met before production deployment.

CTEM ALIGNMENT
STAGE 06 OF 08 · DEPLOY · OPS

Deploy Infrastructure the Way It Was Designed.

Threat modeling examines the infrastructure layer, identifying risks like overly permissive roles, exposed services, and insecure network boundaries before they are provisioned.

01

IaC Security Analysis

Validates infrastructure templates against the intended security posture before deployment.

02

Configuration Hardening

Checks systems against security hardening benchmarks and best practices.

03

Attack Surface Verification

Reviews externally exposed assets and services before they reach production.

CTEM ALIGNMENT
STAGE 07 OF 08 · OPERATE · OPS

Keep the Threat Model Current as Systems Evolve.

Architecture doesn’t stand still. As new features, services, and integrations are introduced, the threat model is revisited so new attack paths are identified before they reach production.

01

Threat Model Updates

Re-evaluates design risk as architecture, integrations, and data flows change.

02

Attack Surface Management (ASM)

Tracks externally exposed assets and attack surface changes in production.

03

Threat Intelligence Context

Incorporates active threats to keep prioritization grounded in real attacker behavior.

CTEM ALIGNMENT
STAGE 08 OF 08 · MONITOR · OPS

Fix Root Causes, Not Just Symptoms.

Design-level findings are tracked through remediation in the TrollEye platform, routed to the teams that own them, and reported to leadership, preventing recurring flaws across future releases.

01

Remediation Tracking

Tracks mitigations from design decision through implementation.

02

Jira / Ticketing Integration

Routes security requirements and findings into existing developer workflows.

03

Recurring Flaw Prevention

Addresses systemic design weaknesses so they don’t reappear in new features.

04

Executive Reporting

Delivers clear, business-aligned metrics on how application risk is trending.

CTEM ALIGNMENT
THREAT MODELING WITHIN CTEM

Threat Modeling Is Where Exposure Management Starts.

Most exposures are fixed after they exist. Threat modeling prevents them from being built in the first place, giving your Continuous Threat Exposure Management (CTEM) program visibility into application risk before a single line of code is written.

Applications are one domain of your attack surface, alongside network, cloud, and identity. Threat modeling powers the Scoping, Discovery, and Prioritization stages at the design level, then hands the attack paths it identifies to testing for Validation and to developers for Mobilization.

WHERE THREAT MODELING FITS IN THE FIVE CTEM STAGES
STAGE 01THREAT MODELING

Scoping

Map application architecture, data flows, and trust boundaries to define which systems and assets matter most and the security requirements each must meet.

Explore Scoping →
STAGE 02THREAT MODELING

Discovery

Surface design-level exposures, including attack paths, abuse scenarios, and insecure architectural decisions, before they are built into the system.

Explore Discovery →
STAGE 03THREAT MODELING

Prioritization

Categorize threats with STRIDE and rank them by likelihood and business impact, in context with cloud, identity, and operational risk.

Explore Prioritization →
STAGE 04DEVSECOPS + PTaaS

Validation

DAST and PTaaS prove which of the attack paths threat modeling predicted are actually exploitable and reachable.

Explore Validation →
STAGE 05DEVSECOPS

Mobilization

Mitigations and security requirements are routed to the teams that own them, fixing root causes so design flaws don’t recur.

Explore Mobilization →
INSIDE OUR CTEM PACKAGES

Design Risk Doesn’t Exist In Isolation.

Within our CTEM packages, the threats identified during design are correlated with application, cloud, identity, and operational exposures, helping security and engineering teams focus on the remediation activities that will have the greatest impact on overall risk reduction.

THREAT MODELING FAQ

Questions About Threat Modeling and Your CTEM Program

A closer look at how our Threat Modeling service works: when it happens, the frameworks we use, who is involved, how it guides the rest of your DevSecOps testing, and how design-level risk feeds your CTEM program.

SERVICEFRAMEWORKSDEVSECOPSCTEM
01 What is threat modeling, and when should it happen?

Threat modeling is a structured analysis of how an application could be attacked, based on its architecture, data flows, trust boundaries, and user interactions.

It delivers the most value during the design and architecture phase, before code is written, when security decisions are fastest and least expensive to change. It should be revisited as new features, services, and integrations are introduced.

02 What frameworks do you use?

We use proven frameworks such as STRIDE to categorize threats across spoofing, tampering, repudiation, information disclosure, denial of service, and elevation of privilege.

Threats are then prioritized by likelihood and business impact, so your teams can make informed, risk-based design decisions.

03 How does threat modeling fit into a CTEM program?

Threat modeling applies the first CTEM stages to your applications at the design level: scoping the architecture and assets that matter, discovering design-level exposures, and prioritizing threats by impact.

The attack paths it identifies are then validated through testing and mobilized to the teams that own them. Within our CTEM packages, that design risk is correlated with cloud, identity, and operational exposure.

04 Who needs to be involved?

Threat modeling works best when developers, architects, and security teams participate together. It creates a shared understanding of system behavior and potential abuse scenarios.

That encourages productive collaboration during planning, rather than reactive discussions when issues surface later in development.

05 How does threat modeling guide other DevSecOps testing?

Threat modeling defines what to look for at every later stage. It points SAST and SCA at the riskiest code and components, sets the controls pipeline security enforces, informs IaC reviews, and gives DAST and PTaaS the attack paths to put to the test.

Together, they form a coherent security strategy that spans the entire software lifecycle.

06 Is threat modeling available on its own?

Threat modeling is delivered as part of our DevSecOps solution, a platform backed by security engineers who work alongside your teams.

Talk with our team about your applications and development process to scope the right approach for your environment.

SEE IT IN PRACTICE See how DevSecOps works inside TrollEye.

Explore application exposure, code and dependency scanning, validated findings, and remediation workflows before starting your evaluation.

EXPERIENCE THREAT MODELING

Design Secure Systems. Reduce Exposure From the Start.

Threat modeling gives you the power to reduce risk before it’s built in. With TrollEye Security’s Threat Modeling service, you identify threats early, align teams around risk, and make informed decisions that lead to more secure, resilient software, all feeding a CTEM program that keeps exposure from coming back.

  1. 01Threats identified before code is written
  2. 02STRIDE-based, risk-ranked analysis
  3. 03Clear requirements for every DevSecOps stage
  4. 04Design-level risk fed into CTEM
Live Product Update

Meet the Future of
Risk & Remediation

Introducing two major additions to the TrollEye CTEM platform, designed to help teams move from exposure to action.

AI Remediation Agent

AI assistance to help security teams move from findings to fixes faster.

Business Risk Dashboard

New visibility into breach probability, financial risk, and compliance.

Hosted By

Avery Rozar Avery Rozar CEO, TrollEye Security
Sullivan Tuck Sullivan Tuck Head of Growth & Marketing
December 17, 2026 • 2:00 PM ET • Live Online
Reserve Your Spot →

This Content Is Gated