Another annual test won’t protect policyholder data. Continuously closed exposures will.
Fewer exploitable access paths, filings that stay on schedule, and a record regulators trust, whether you run long-lived filing platforms or build new digital products every sprint.
Experience inside the surplus & excess lines ecosystem.
Insurance risk doesn’t live in one system. It lives in the filing platforms, broker and insurer portals, APIs, batch jobs, and transaction workflows that connect every stakeholder to your data. That’s where we work.
2025 premium reported by the 15 U.S. stamping offices (WSIA via Surplus Lines Reporting).
Four places insurers get exposed. Four outcomes we deliver.
Each area runs through the TrollEye platform, from discovery and agentic and human testing to owners, deadlines, and retesting. Select an area to see where risk is going down.
Filings stay on schedule
Filing and reporting applications that can’t go down near a deadline, so testing gets pushed to a once-a-year window.
Every portal is accounted for
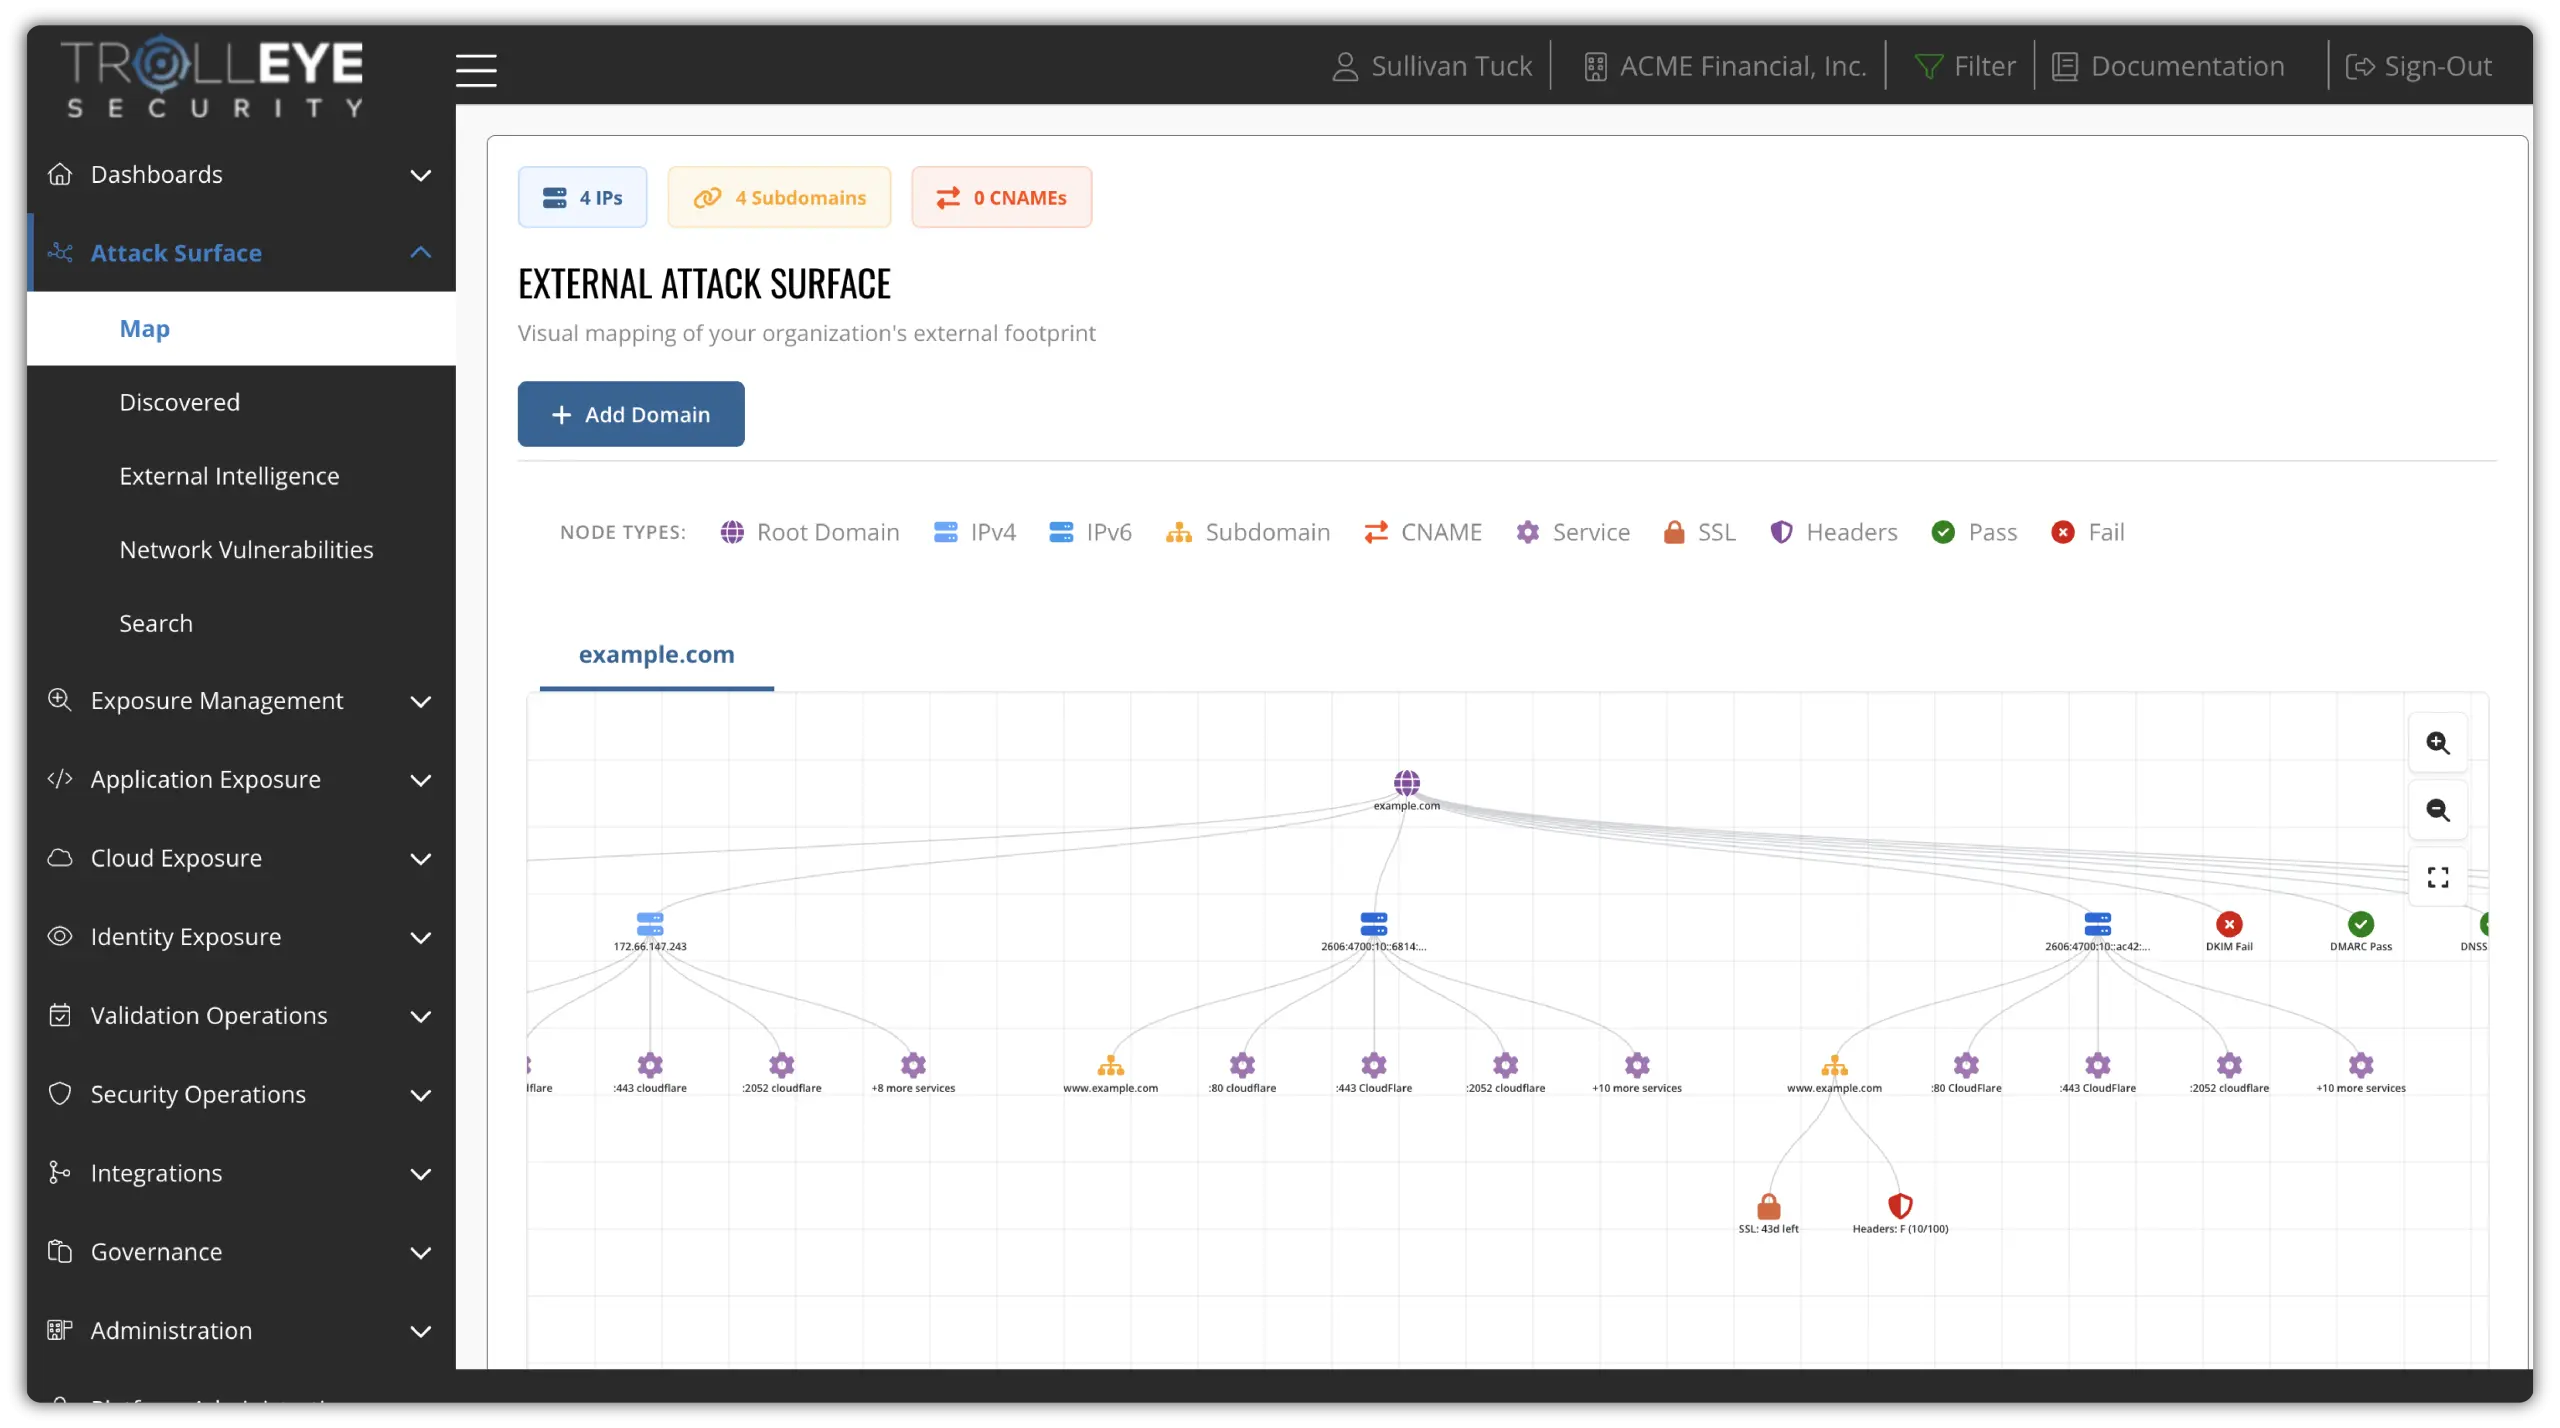
Broker and insurer portals, external apps, and shared logins multiply faster than anyone can inventory them.
Integrations stop leaking risk
APIs, web services, and batch file exchanges carry regulatory data between organizations, often with little scrutiny.
Examiners get evidence, not effort
Proving due diligence means stitching together PDFs, email threads, and spreadsheets every exam cycle.
The evidence regulators ask for. Kept current all year.
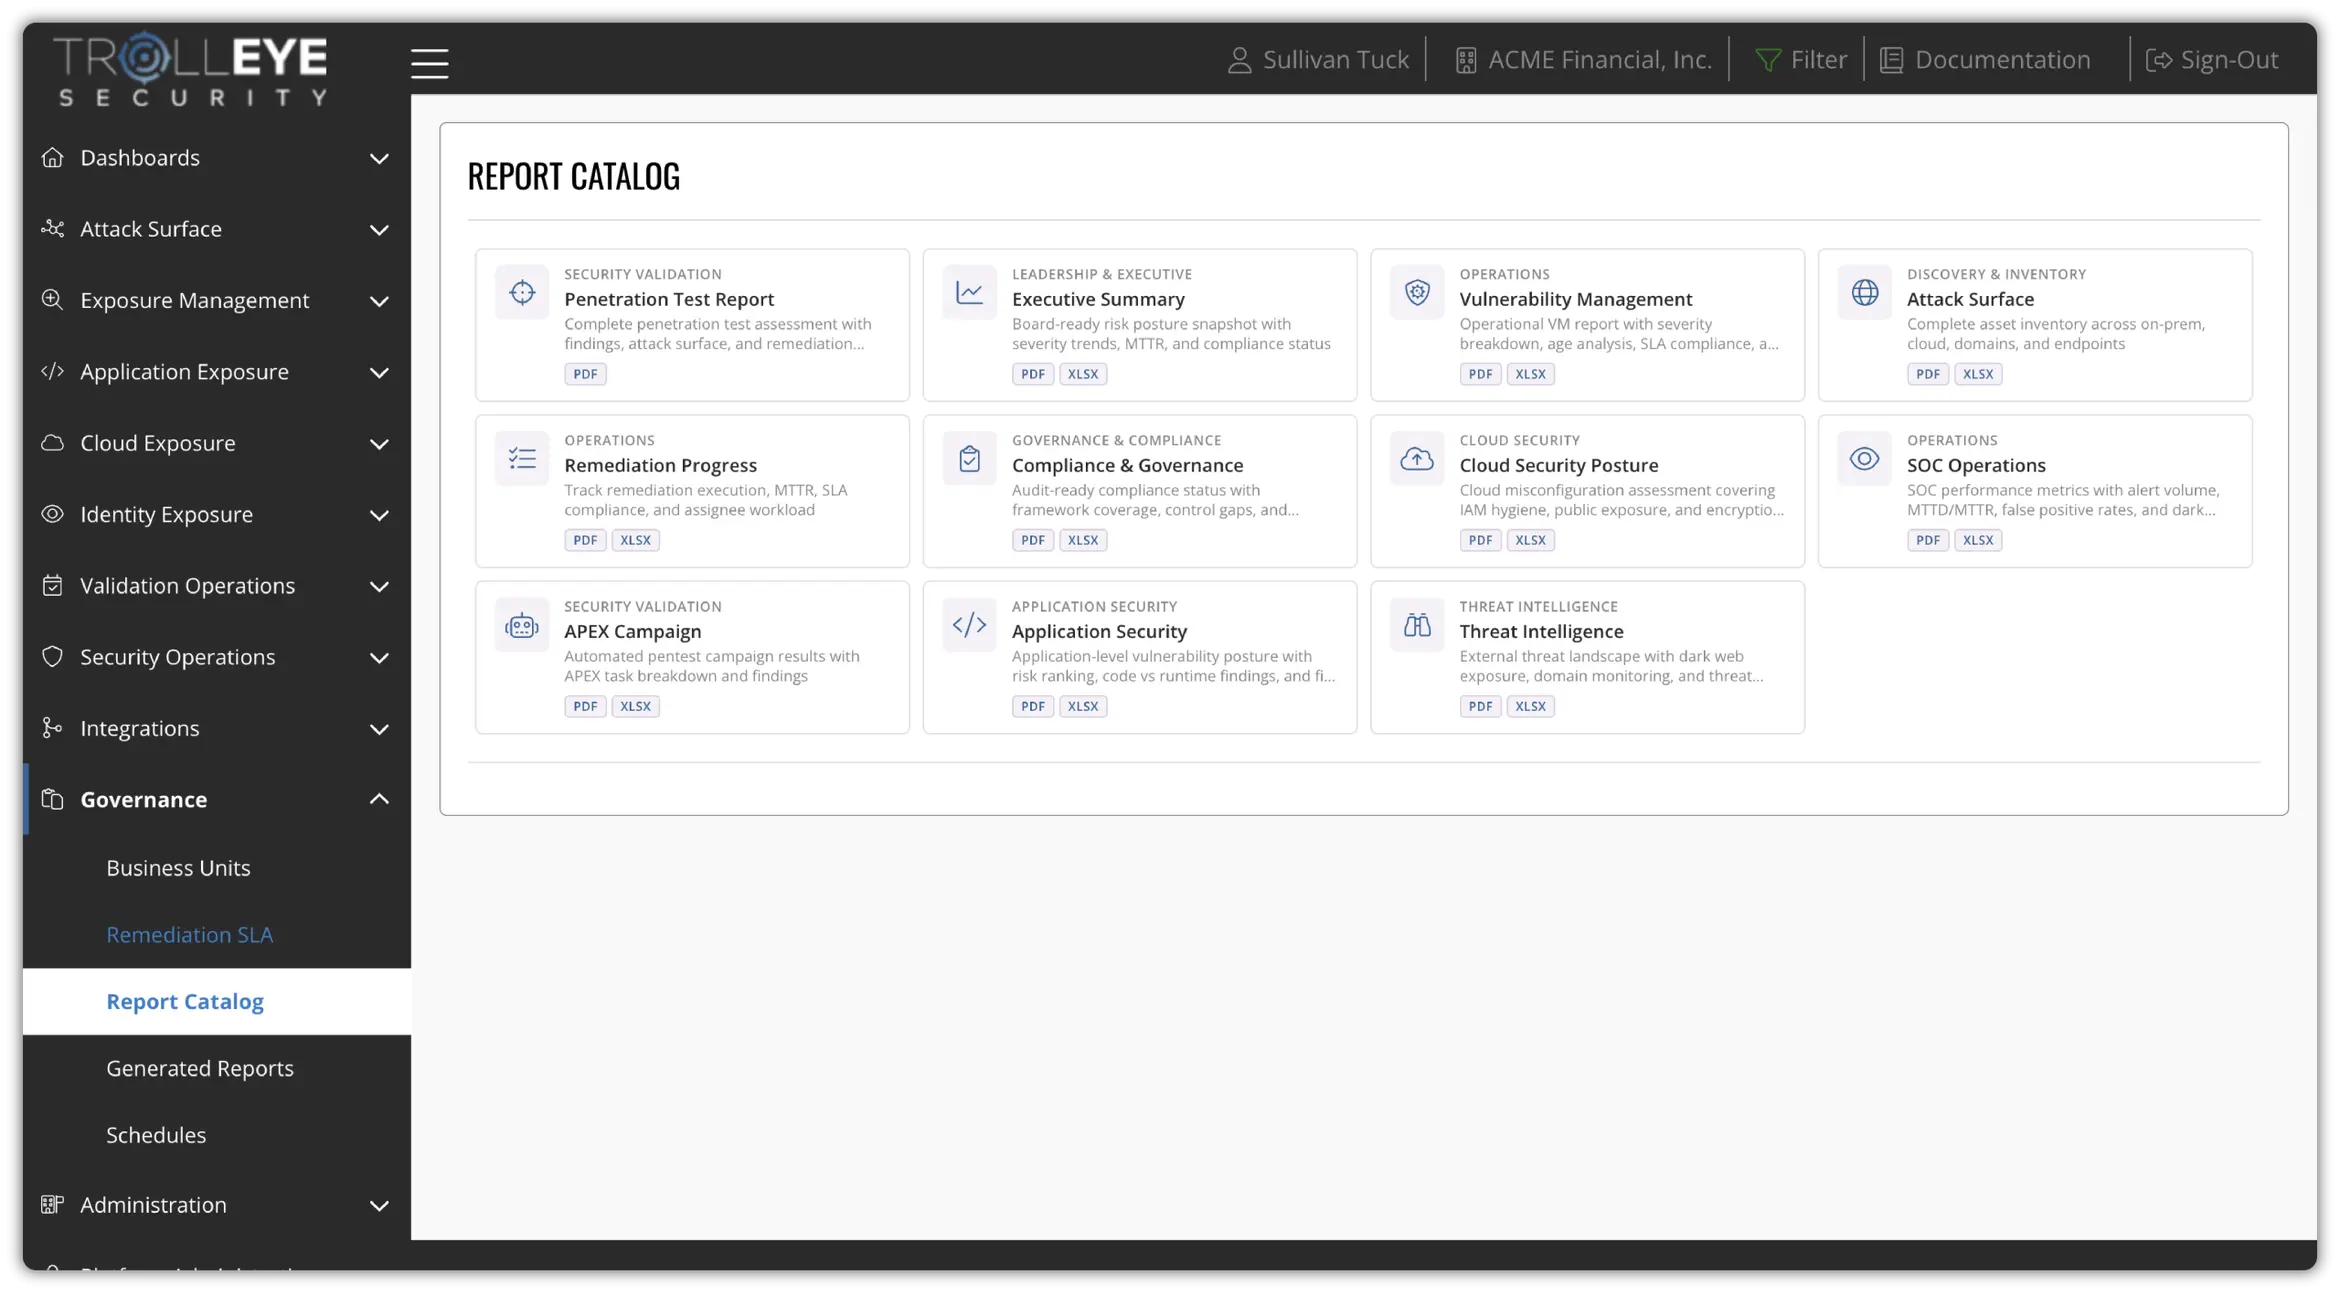
Regulators and examiners look for testing, validated findings, clear ownership, and proof that issues were fixed. TrollEye keeps that record in one place, all year.
- NAICInsurance Data Security Model Law
- NYDFS23 NYCRR Part 500
- State ExamsIT examination reviews
- PCI DSSv4.0
- SOC 2Type II
TrollEye provides testing evidence and remediation records that support these requirements. It doesn’t replace your compliance program or an examiner’s judgment.
- Testing history for every assessment
- Validated, prioritized findings
- Owners held to remediation SLAs
- Retest records that confirm closure
- Your side of every broker, carrier, and partner connection, tested
CTEM, built around how insurers operate.
Five stages that run continuously, not once a year.
Scoping
Start with what regulators care aboutDiscovery
Find every access pathPrioritization
Rank by real impactValidation
Prove what’s exploitableMobilization
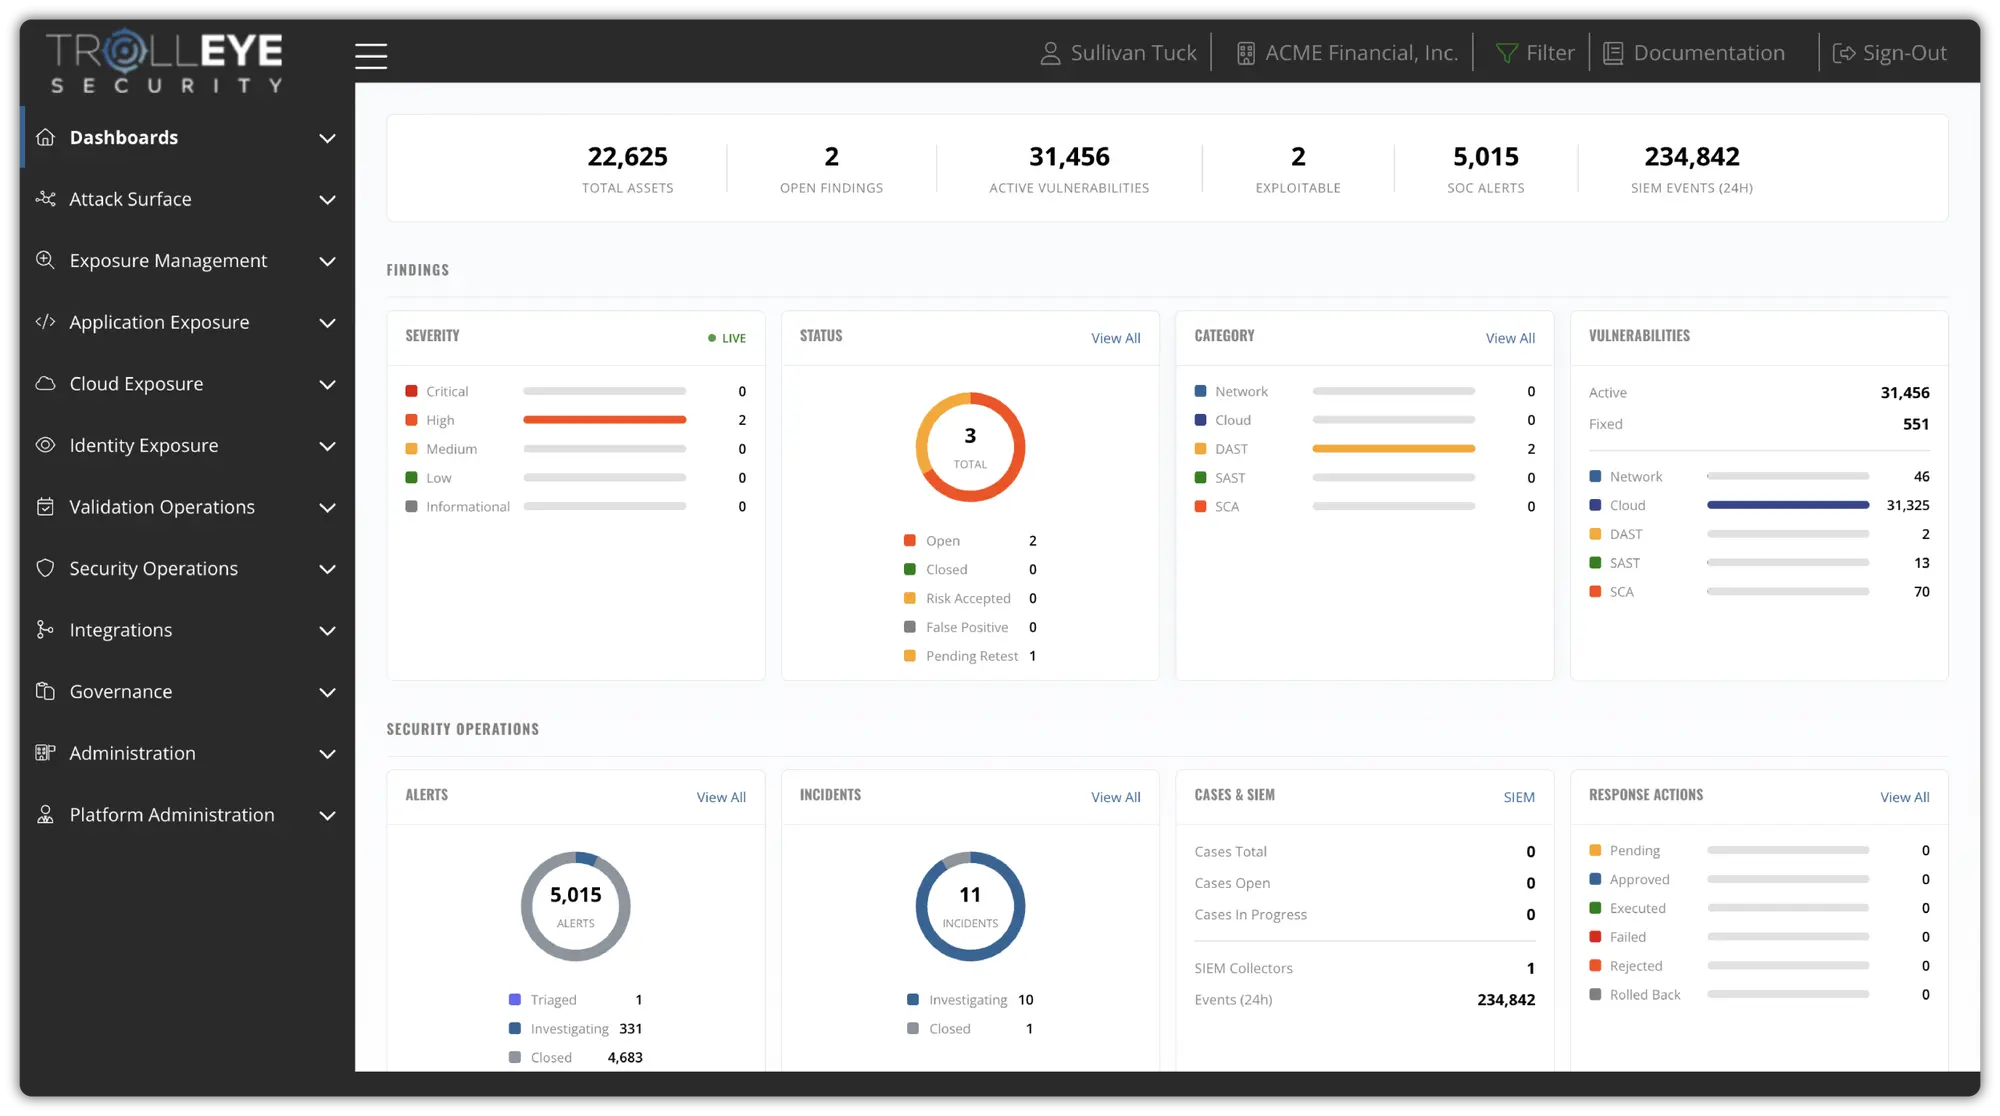
Drive it to closureSee How TrollEye Keeps Filing Platforms Secure
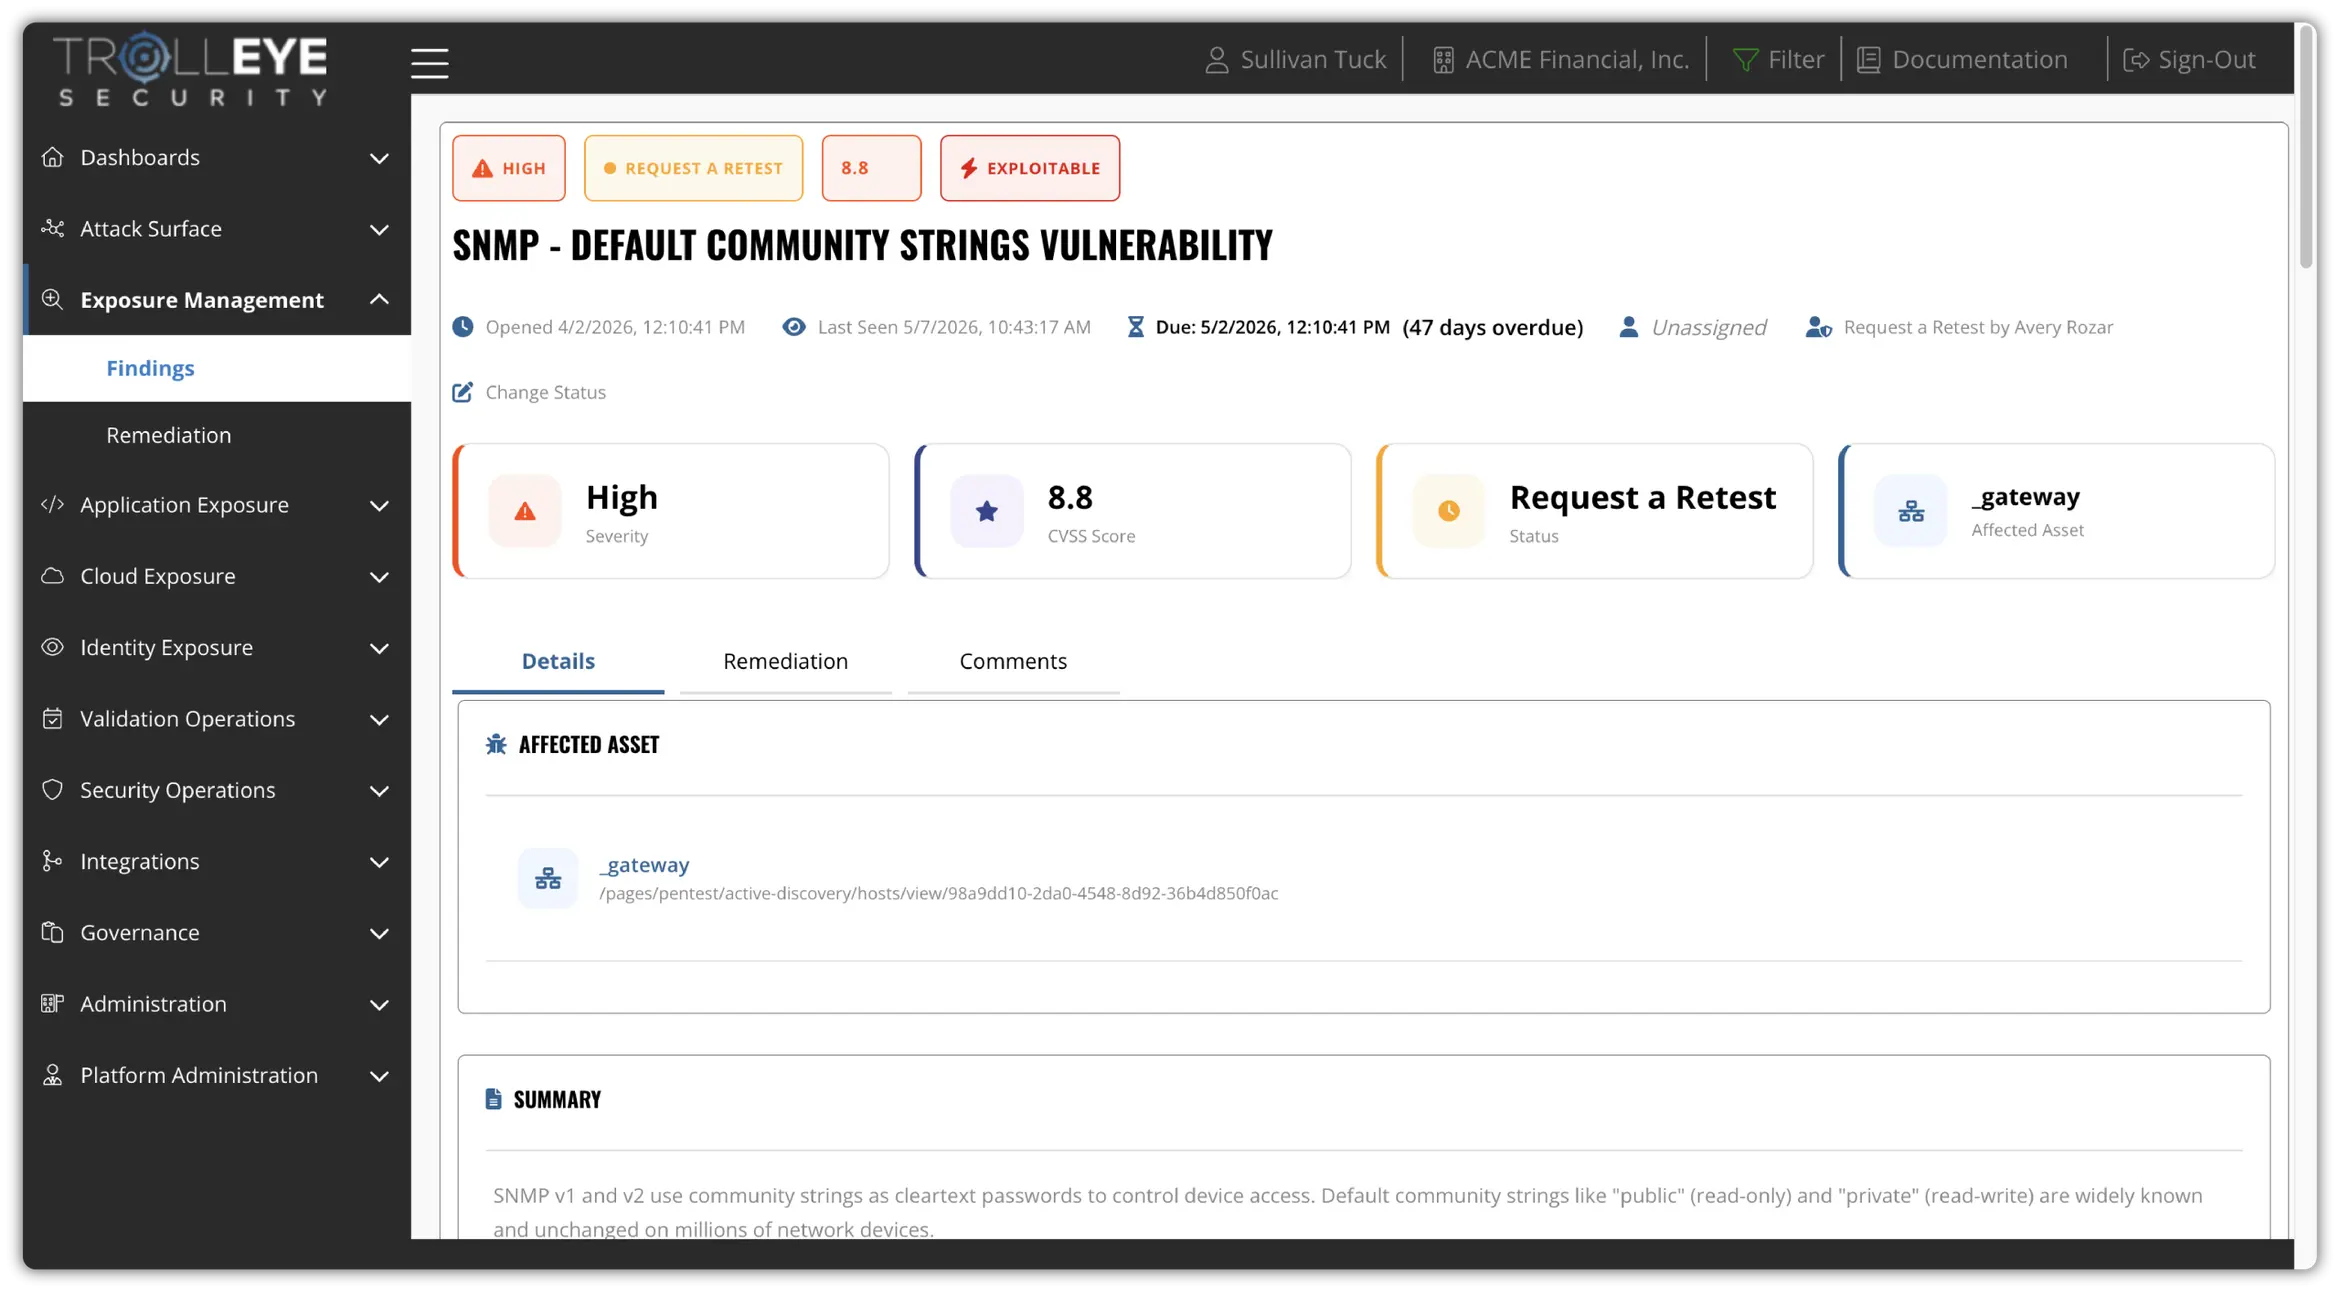
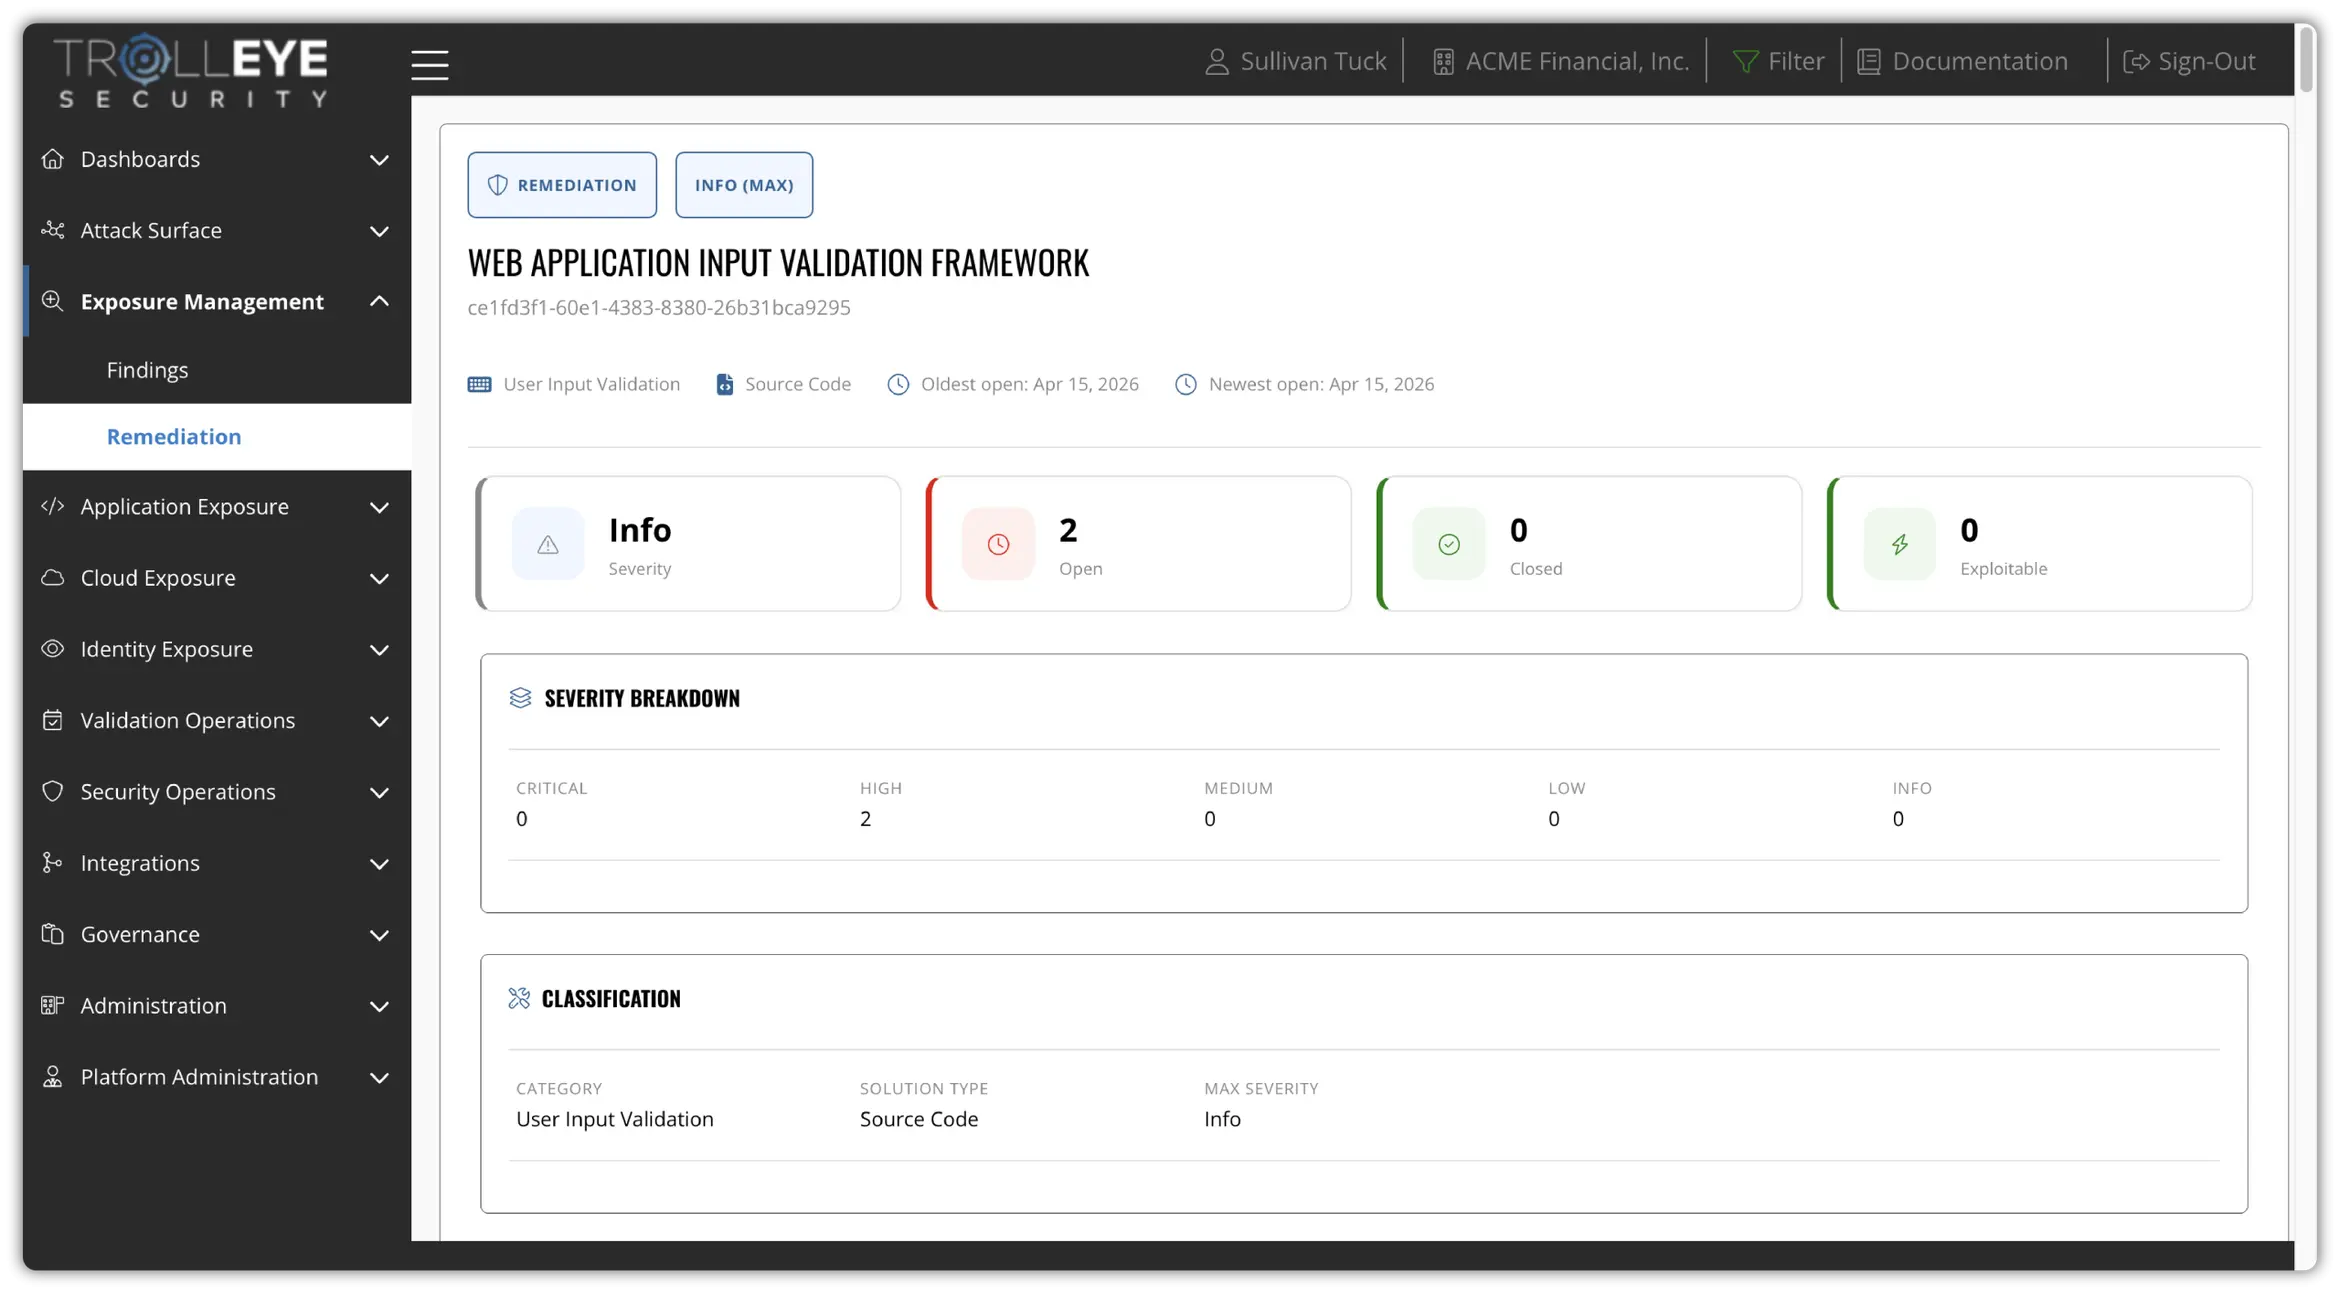
Choose a demo to see how audit readiness, continuous testing, attack surface discovery, and remediation work inside the TrollEye platform.
Testing that keeps pace with development.
TrollEye helps secure state excess and surplus lines offices that oversee $27.8B in annual premium and serve filers in 12 states. Here’s how the Florida Surplus Lines Service Office built continuous penetration testing directly into its development lifecycle.
Security inside the development lifecycle, not bolted on after it.
- PTaaS embedded in the development lifecycle
- On-demand and continuous testing in place of a fixed annual window
- Agentic and human testing delivered through the TrollEye platform
“PTaaS has been a wonderful addition to our Development Lifecycle. TrollEye’s platform provides a unique experience and excellent value!”
Questions About Securing Insurance Organizations
A closer look at how TrollEye works for carriers, regulatory bodies, and insurtechs: testing, filing deadlines, regulatory exams, portals, and how it all fits your CTEM program.
01How is this different from our annual penetration test?
An annual test shows your exposure on one day. Your filing platforms, portals, APIs, and releases keep changing after it.
TrollEye delivers agentic and human testing on demand and continuously through PTaaS, validates what is actually exploitable and reachable, routes fixes to owners, and retests to confirm closure.
02Can testing work around our filing deadlines?
Yes. Testing is scheduled around your filing and reporting calendar, so the applications behind filings, reporting, and transactions stay available when it matters most.
Remediation is weighed against uptime and operational impact, not just severity.
03Will this help with regulatory exams?
TrollEye doesn’t replace your compliance program, but it gives you the evidence examiners ask for: testing history, validated findings, ownership, remediation SLAs, and retest records, kept current all year.
That record supports requirements under the NAIC Insurance Data Security Model Law, NYDFS Part 500, and state IT examination reviews.
04Do you test broker and insurer portals?
Yes. We map and test the portals, authentication, external applications, and stakeholder workflows your organization controls, so nothing internet-facing goes unseen.
Learn how this differs from vendor assessments in our CTEM vs. TPRM guide.
05Can our in-house team use the platform?
Yes. In-house security and red teams can use the TrollEye platform themselves, so their findings sit alongside ours with the same validation, ownership, SLAs, and retesting.
06How does this fit into a CTEM program?
TrollEye applies each CTEM stage to your organization: scoping the filing platforms, portals, and APIs that matter, discovering every access path between brokers, insurers, and regulators, prioritizing by policyholder and regulatory impact, validating what is actually exploitable and reachable, and mobilizing owners to close it.
Explore audit readiness, continuous testing, attack surface discovery, and remediation before starting your evaluation.
Stop proving you looked. Start proving it’s closed.
See how TrollEye helps insurance organizations validate what matters, coordinate remediation, and build a record regulators trust.