TrollEye Security

PART OF DARK WEB ANALYSISCredential, Executive, and Vendor Exposure→

Executive Monitoring. Find Leadership Exposure Before Attackers Use It.

Executives are prime targets for phishing, credential theft, and impersonation because of their access to sensitive systems and information. Our Executive Monitoring capability continuously analyzes breach data and dark web sources for records tied to your leadership, so your security team can identify exposure early and respond before it is exploited.

It is one of three monitoring areas inside our Dark Web Analysis solution, so every executive finding is validated, prioritized, and acted on in the same platform and the same CTEM program as the rest of your identity exposure.
Leadership Exposure DetectionCredential ValidationTargeted Attack PreventionGuided Risk Mitigation
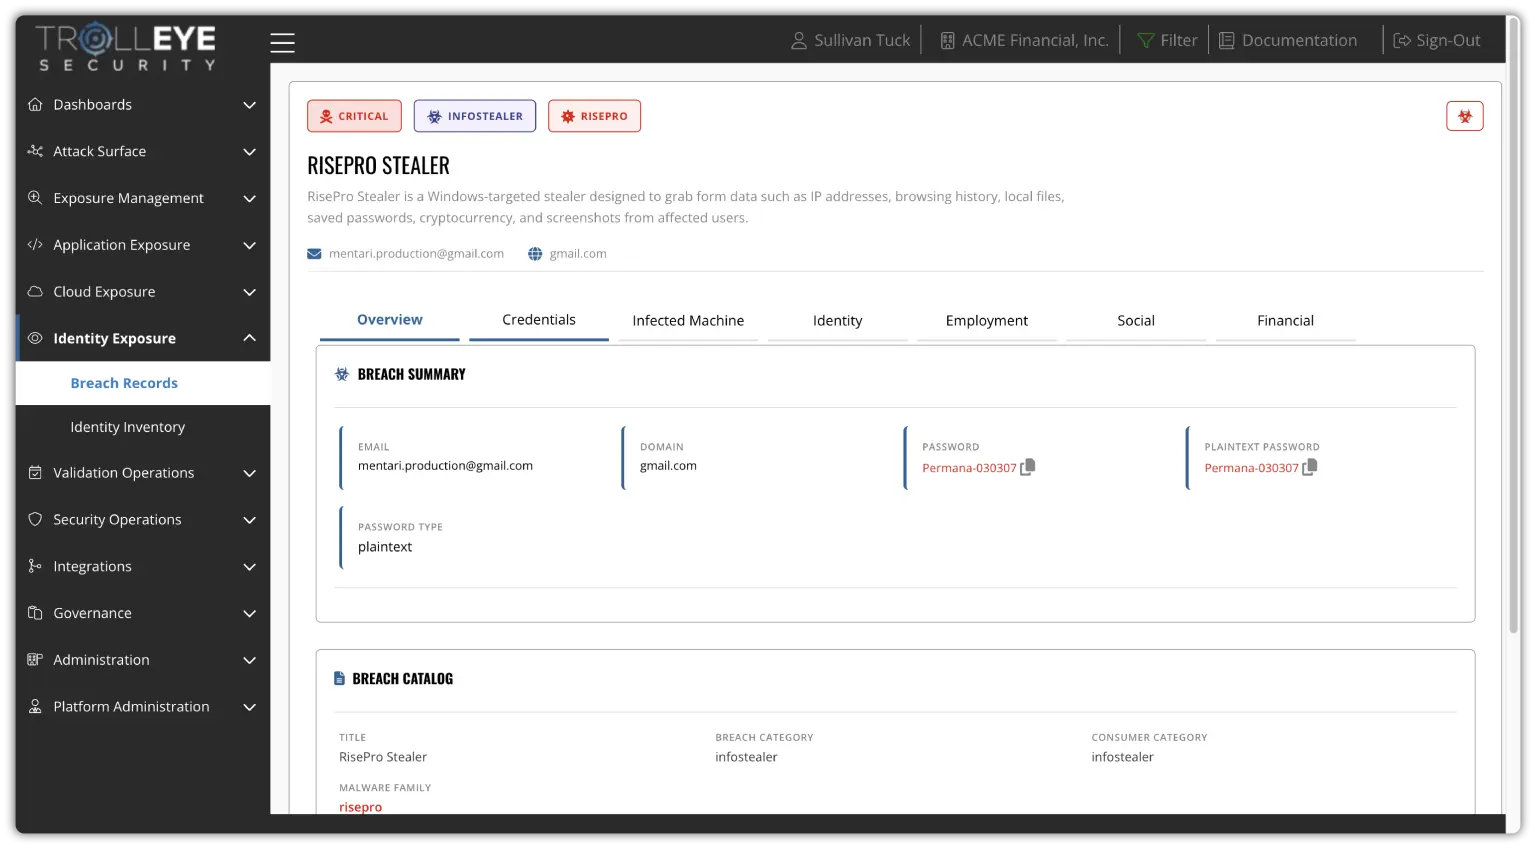
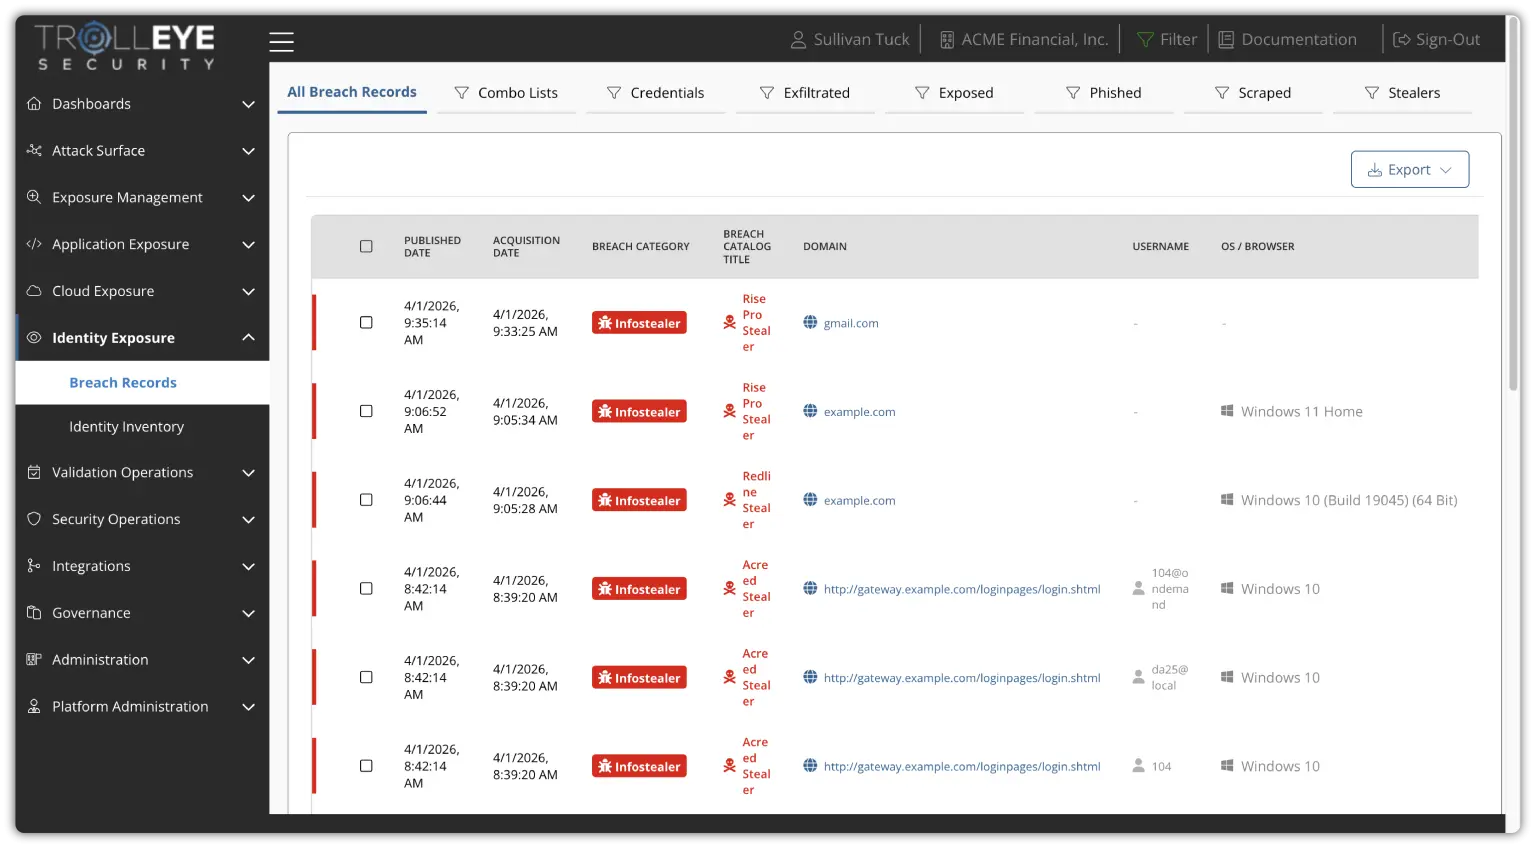
TrollEye platform breach records view of exposure tied to monitored individuals
EXECUTIVE MONITORINGLeadership exposure, found early
PART OF DARK WEB ANALYSISSame platform, same response workflow
WHAT WE MONITOR

Every Exposure Tied To Your Leadership.

Executives often appear in breach datasets because of compromised personal or professional accounts. Monitoring covers the corporate and personal footprint of each enrolled leader, so security teams can detect leaked credentials and sensitive information before attackers turn them into a targeted campaign.

Protecting your whole workforce? See Credential Monitoring →
01

Corporate Credentials

Usernames and passwords tied to executive accounts on your corporate domains, found in breach dumps and credential-harvesting operations.

02

Personal Accounts

Breached personal email and third-party service accounts, where password reuse can give attackers a path into corporate systems.

03

Personal Information

Exposed personal data, such as phone numbers, home addresses, and other details attackers use to make phishing and impersonation convincing.

04

Infostealer Activity

Saved passwords, session data, and credentials harvested from compromised devices and posted to underground marketplaces.

THE ATTACK PATH WE INTERRUPT

From Breach Record To Targeted Attack.

Exposed executive data rarely goes unused. Attackers combine leaked credentials and personal details into phishing, impersonation, and account takeover campaigns. Executive Monitoring identifies the exposure at the first link, so your team can break the chain before it reaches your environment.

INHERITED FROM DARK WEB ANALYSIS

Built On Dark Web Analysis. Applied To Your Leadership.

Executive Monitoring isn't a standalone alerting feed. It runs inside our Dark Web Analysis solution, alongside credential and third-party vendor exposure monitoring, with the same platform, the same validation by our penetration testers, and the same coordinated response.

01

Expert Validation

Analysts and penetration testers confirm which exposed credentials and access paths are active and exploitable, so teams act before attackers do.

02

Complete Finding Context

Every validated finding includes when the data was leaked, how it was obtained, whether credentials are still active, a risk-based priority, and clear remediation guidance.

03

Coordinated Response

Our team adds context and routes remediation to the right owners, so compromised access is revoked and leadership risk is reduced quickly.

INSIDE THE PLATFORM

How Executive Monitoring Works Inside TrollEye.

Executive exposure doesn't arrive as a one-off email alert. It lands in the same TrollEye platform as the rest of your Dark Web Analysis, where your team can see what was exposed, whether it is still usable, who owns the response, and how risk is trending.

Enrollment & Scanning

Your security team identifies the executives to monitor and registers them directly, with no executive involvement required. From there, breach datasets, dark web forums, and underground marketplaces are continuously analyzed for records tied to each person.

  • Enrollment handled by your security team
  • Corporate and personal exposure tracked together
  • Breach records for every monitored executive in one view
TrollEye platform breach records view

Validated Exposure

Each finding shows when the data was leaked, how it was obtained, and whether the credentials are still active. Our penetration testers confirm which exposures are actually exploitable and reachable, so your team acts on real risk instead of raw alerts.

  • Leak date, source, and credential status on every record
  • Exploitability confirmed by our testers
  • Risk-based priority for each finding
TrollEye platform breach record detail with exposed credential status

Alerts & Reporting

When executive data appears in a breach or dark web source, your team is alerted. Live reporting provides ongoing visibility into exposure status, risk levels, and detection history for each monitored individual.

  • Alerts delivered directly to your security team
  • Exposure history for every executive
  • Executive-ready summaries and technical detail
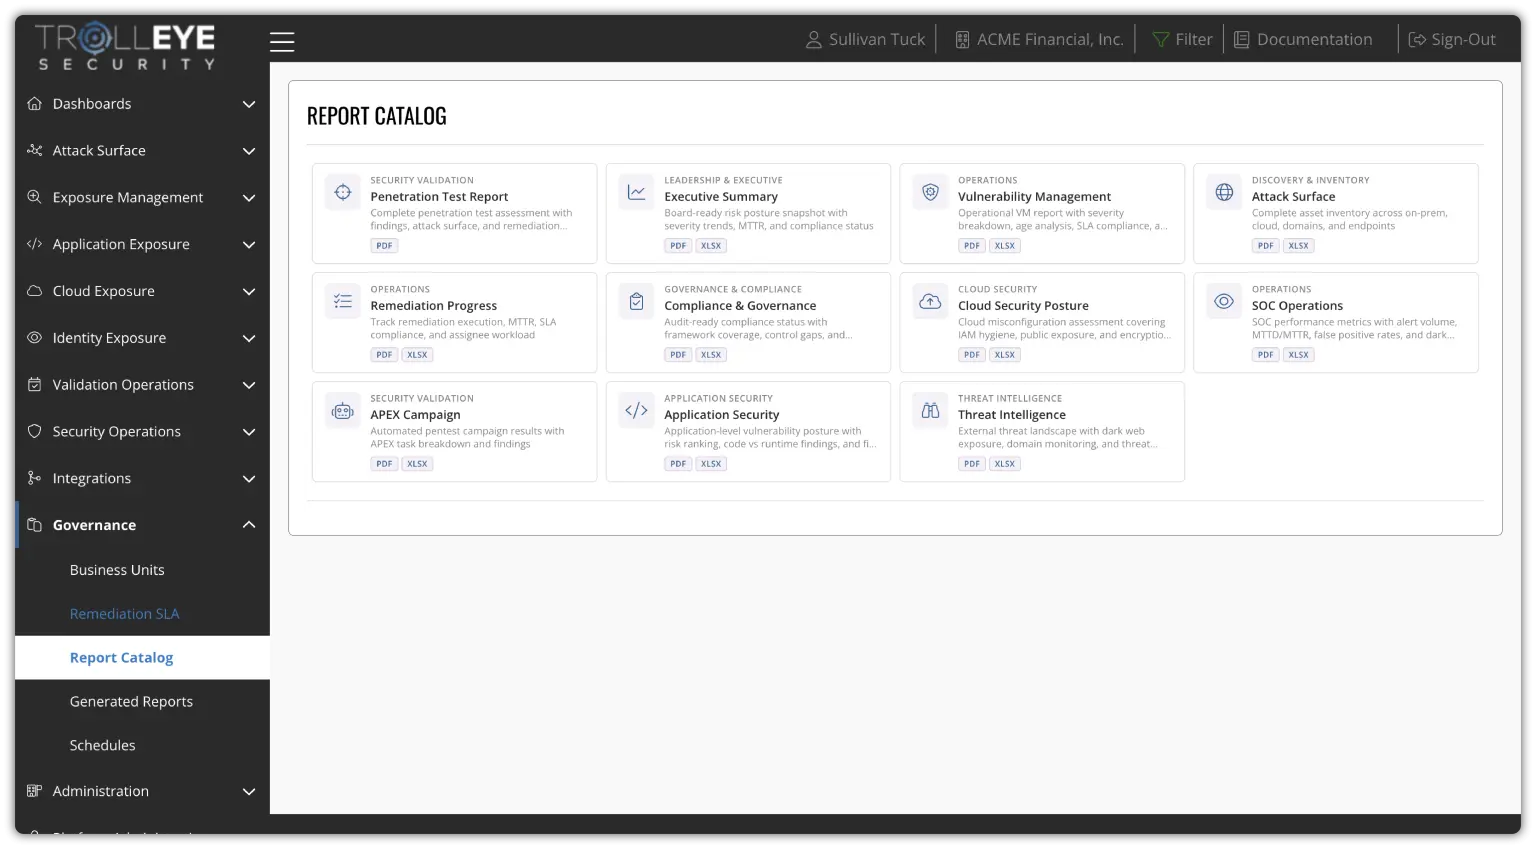
TrollEye platform report catalog

Guided Mitigation

Every finding comes with recommended actions, such as credential resets, authentication hardening, and account review, routed to the right owners and tracked centrally, so targeted follow-on attacks are shut down quickly.

  • Clear, recommended response actions
  • Owner-routed tasks with tracked progress
  • Lower risk of account takeover and impersonation
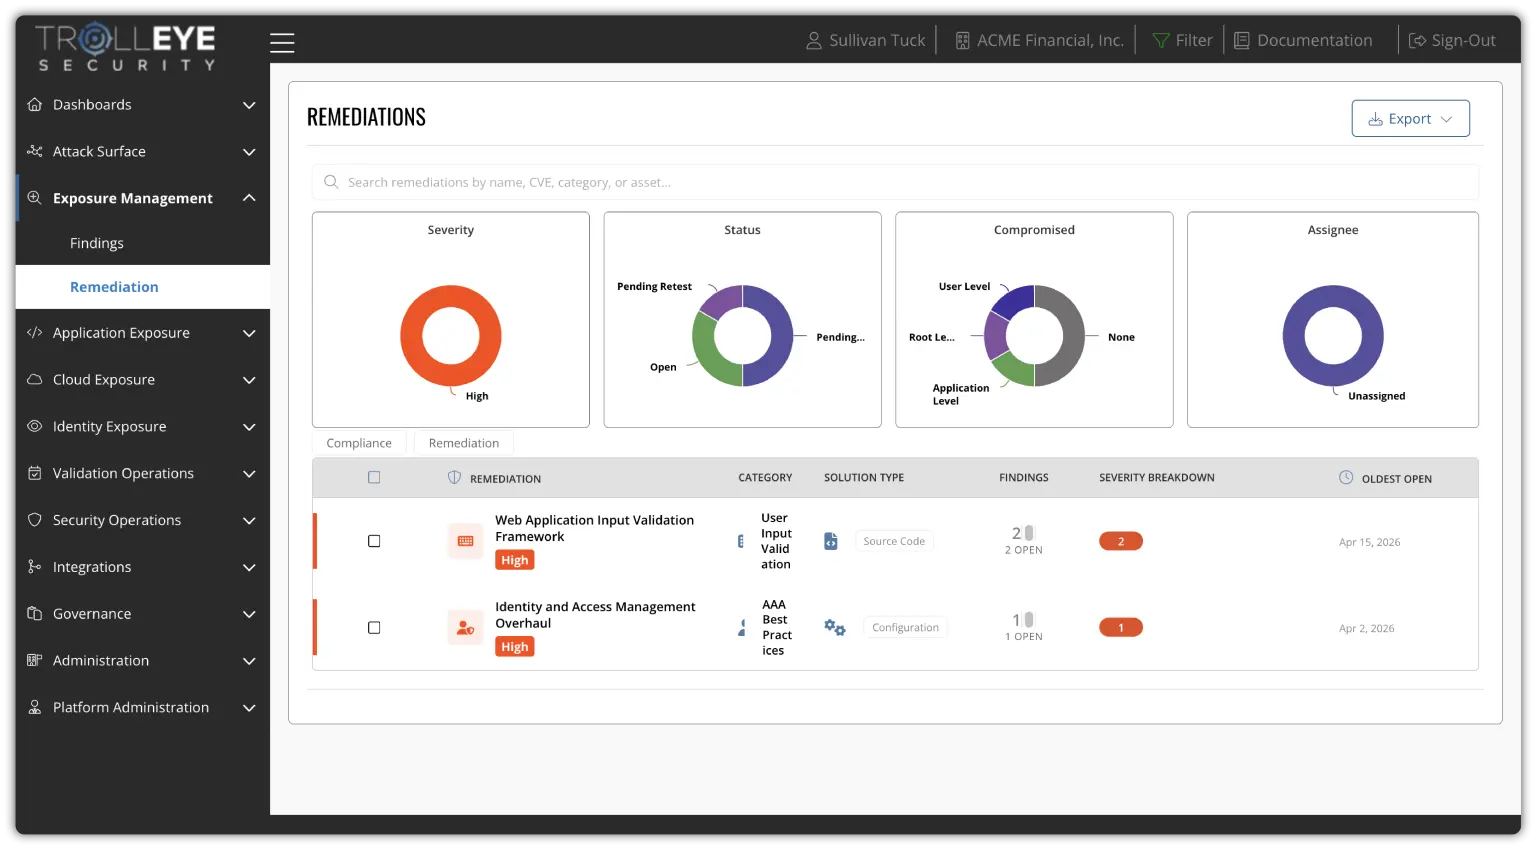
TrollEye platform remediation tracking view
EXECUTIVE MONITORING WITHIN CTEM

Bringing Leadership Exposure Into Your CTEM Program.

Executive Monitoring is part of the identity exposure intelligence layer of our Continuous Threat Exposure Management (CTEM) solution. By continuously identifying and validating exposure tied to leadership, it brings one of the most targeted groups in your organization into the CTEM lifecycle.

Most organizations don’t have a visibility problem. They have an execution problem. Executive Monitoring powers the Discovery, Validation, and Mobilization stages for leadership exposure, while Scoping and Prioritization run across your entire attack surface in the same TrollEye platform.

WITHIN OUR CTEM PACKAGES, EXECUTIVE FINDINGS COMBINE WITH
  • Credential Exposure
  • Vendor Exposure
  • Attack Surface Visibility
  • Remediation Workflows
  • Continuous Reporting
Executive Monitoring FAQ

Questions About Executive Monitoring

How executive monitoring works, what it covers, and how it fits into your Continuous Threat Exposure Management (CTEM) program.

01
SCOPEDefine Who Matters
02
DISCOVERFind Leadership Exposure
03
PRIORITIZERank by Business Impact
04
VALIDATEProve Exploitability
05
MOBILIZEReset and Harden
01What is executive monitoring?

Executive monitoring continuously analyzes breach data and dark web sources for credentials, personal accounts, and personal information tied to your leadership. Because executives hold access to sensitive systems, financial approvals, and confidential data, attackers use that exposure for phishing, impersonation, and account takeover. Monitoring surfaces it before they can.

02What types of executive exposure do you monitor?

Leaked corporate credentials, breached personal email and third-party accounts, exposed personal details such as phone numbers and home addresses, and credentials harvested by infostealer malware and sold on underground marketplaces.

03Do executives need to be involved in enrollment?

No. Your security team registers the executives to be monitored directly in the platform, and each person can be configured independently.

04How are findings validated and acted on?

Every finding shows when the data leaked, how it was obtained, and whether credentials are still active. Our penetration testers confirm what is actually exploitable, then your team receives a risk-based priority and recommended actions, such as credential resets and MFA enforcement, with remediation tracked to the right owners.

05How is it different from credential monitoring?

Credential monitoring covers corporate-domain credentials across your whole workforce. Executive monitoring focuses on leadership and adds personal accounts and personal details, which is often how attackers reach executives and what domain-based monitoring misses.

06How does it fit into Dark Web Analysis and CTEM?

It's one of three monitoring areas in our Dark Web Analysis solution, alongside credential and third-party vendor exposure. Within our Continuous Threat Exposure Management (CTEM) solution, it powers the Discovery, Validation, and Mobilization stages for leadership exposure.

PART OF DARK WEB ANALYSISExecutive Monitoring is one part of our Dark Web Analysis solution.

See how credential, executive, and third-party vendor monitoring run together in one platform and one response process.

GET STARTED

Your Executives Are Prime Targets. Protect Them Today.

Reach out today to bring proactive, executive-level protection to your security strategy. See how Executive Monitoring works alongside credential and vendor monitoring in our Dark Web Analysis solution, and how it fits into a complete CTEM program.

  • 01Early detection of leadership exposure
  • 02Validated, actionable executive findings
  • 03Reduced risk of targeted attacks
  • 04Faster, owner-routed response
Live Product Update

Meet the Future of
Risk & Remediation

Introducing two major additions to the TrollEye CTEM platform, designed to help teams move from exposure to action.

AI Remediation Agent

AI assistance to help security teams move from findings to fixes faster.

Business Risk Dashboard

New visibility into breach probability, financial risk, and compliance.

Hosted By

Avery Rozar Avery Rozar CEO, TrollEye Security
Sullivan Tuck Sullivan Tuck Head of Growth & Marketing
December 17, 2026 • 2:00 PM ET • Live Online
Reserve Your Spot →

This Content Is Gated