Another assessment won’t keep the lights on. Closed paths to operations will.
Fewer paths to operations, clear priorities for lean teams, and progress leadership can see, whether you protect substations built to last decades or add cloud and member portals this year.
Experience securing distributed utility infrastructure.
Our utility experience centers on IT infrastructure, remote assets, connectivity, identity, and the distributed systems that support essential operations. That’s where attack paths toward operations begin, and where we work.
Talquin Electric Cooperative, a TrollEye customer serving four Florida counties.
Five paths toward operations. Five ways we close them.
Most attack paths start at the edges of a utility and work inward. Select an area to see where it gets exposed and what changes with TrollEye.
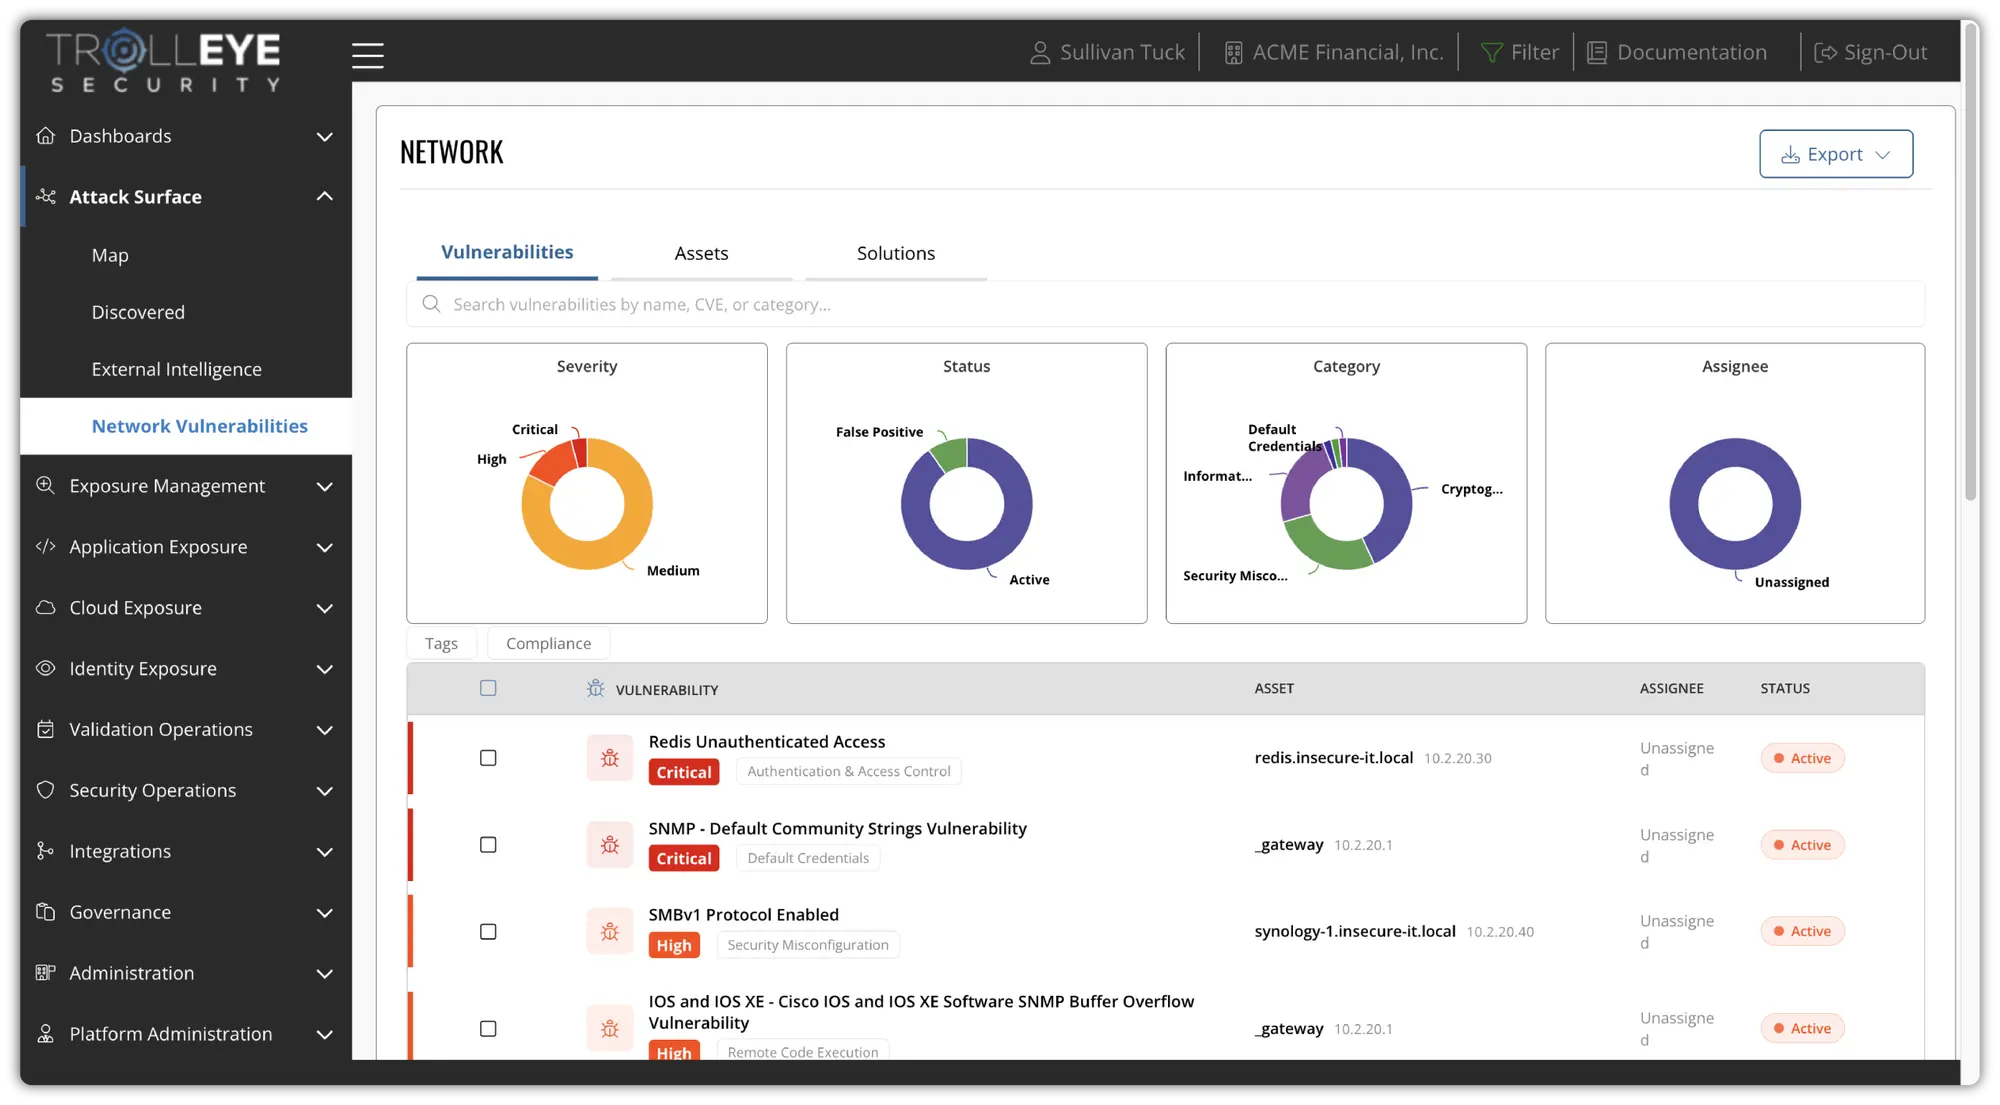
Utility IT stops being the easy way in
Internet-facing services, forgotten assets, and gaps between business IT and operational networks give attackers an easy first step.
- Internet-facing services and forgotten assets
- Identity and privilege paths to critical systems
- Segmentation gaps between business IT and operations
Paths to substations are closed
Remote access routes, default or shared credentials on network devices, and connectivity that bridges IT and substation infrastructure.
- Remote access routes into substation networks
- Default or shared credentials on network devices
- Proof of what is exploitable and reachable
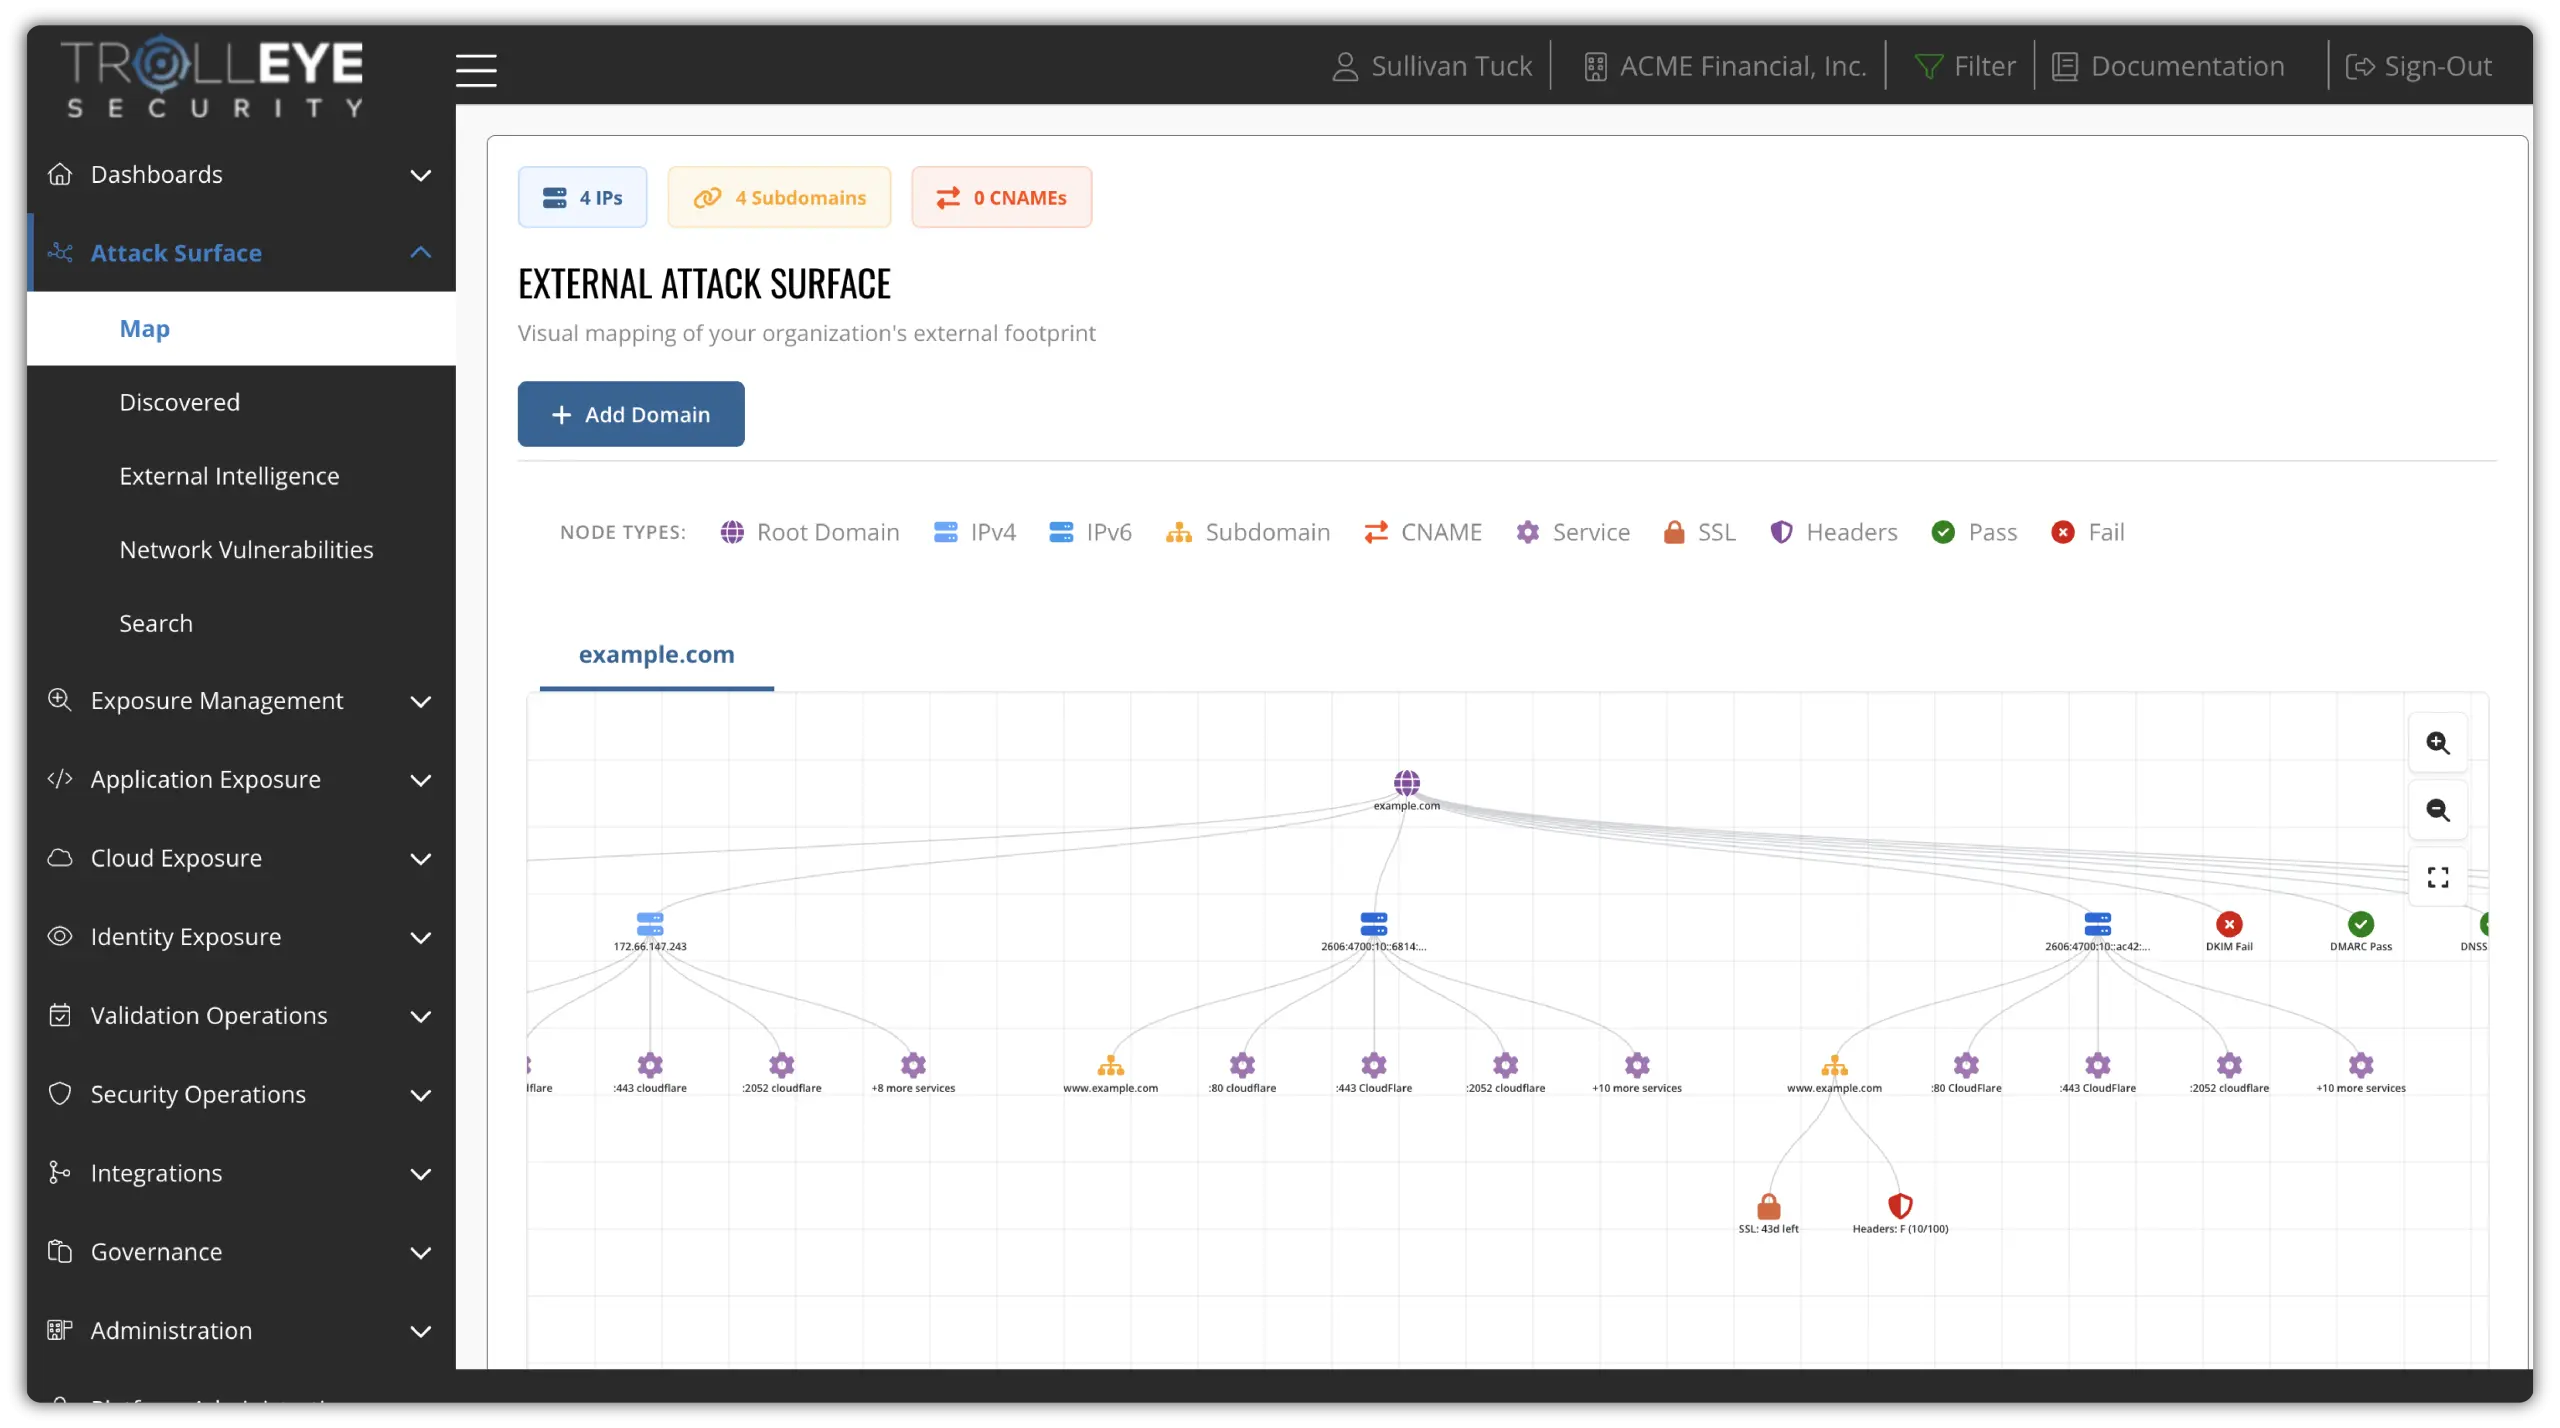
Every remote site is accounted for
Newly exposed devices, internet-reachable connectivity, and credentials reused across sites appear between assessments.
- Continuous discovery across distributed assets
- One prioritized list, not site-by-site reports
- Clear ownership for lean IT and field teams
Privilege stays where it belongs
Shared, reused, and over-privileged accounts let one foothold in utility IT turn into a path toward critical systems.
- Privilege paths mapped to critical systems
- Shared and reused credentials surfaced
- Fixes owned in Jira and retested
Modernization opens no new doors
Cloud, identity, remote access, and member portals grow faster than an annual assessment can follow.
- Newly exposed cloud assets found fast
- Member portals and apps tested on demand
- Exposure trends as new services go live
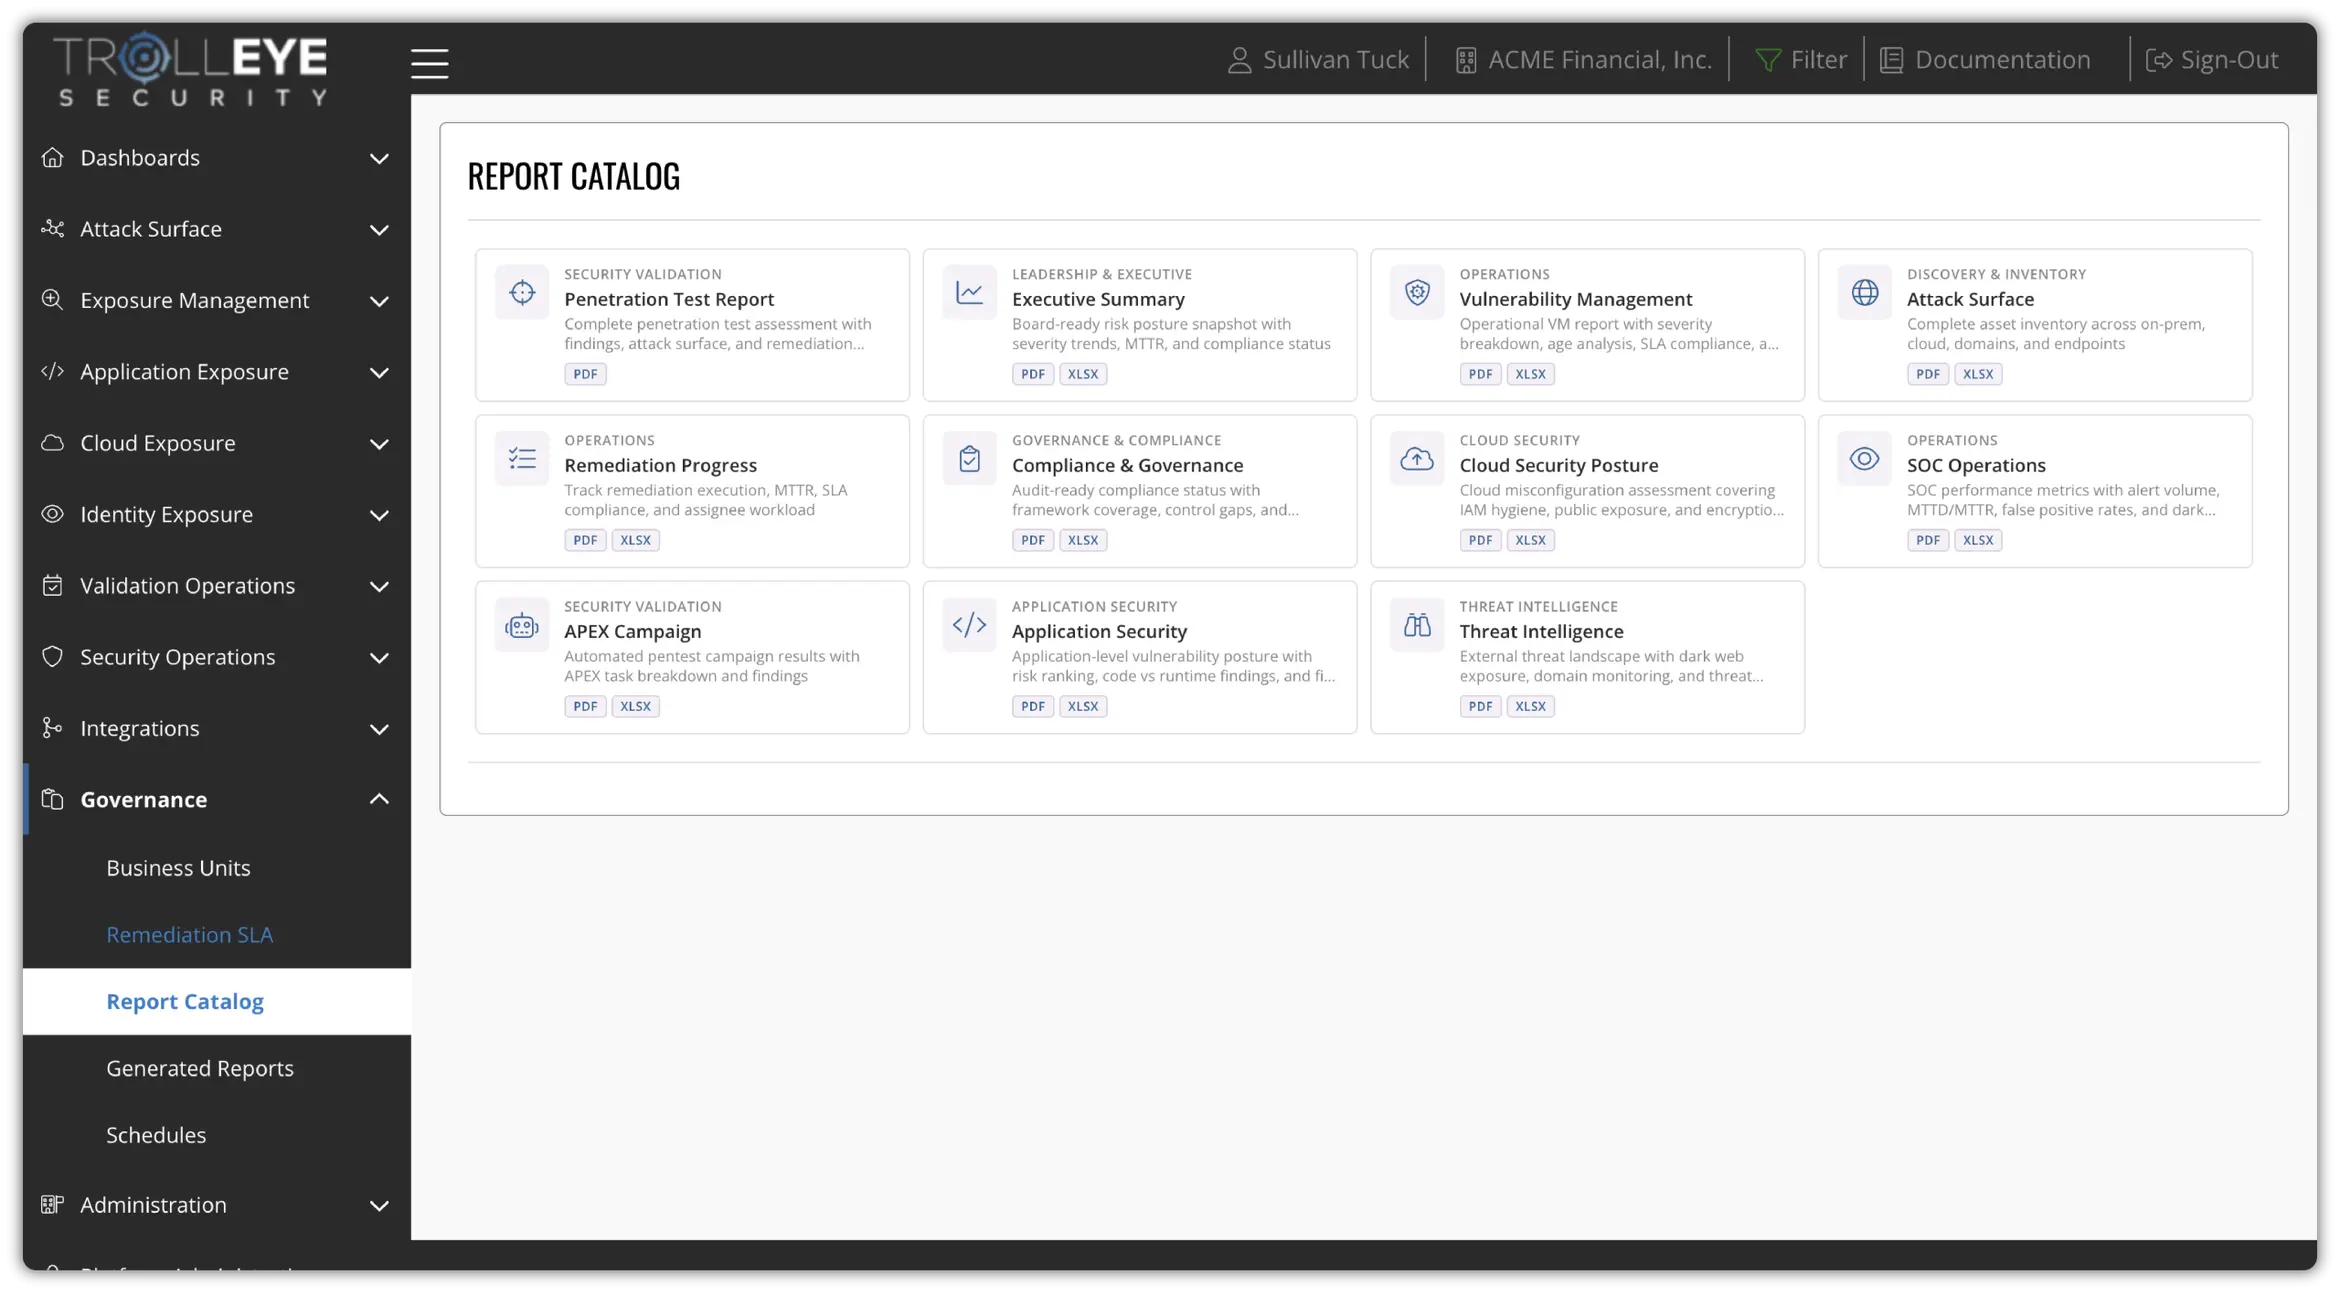
The evidence boards and auditors ask for. Kept current all year.
Boards, auditors, regulators, and cyber insurers look for testing, validated findings, clear ownership, and proof that issues were fixed. TrollEye keeps that record in one place, all year.
- NIST CSF2.0
- DOE C2M2Maturity Model
- AWIARisk & resilience assessments
- Cyber InsuranceUnderwriting reviews
- BoardRisk oversight
TrollEye provides testing evidence and remediation records that support these requirements. It doesn’t replace your compliance program or an auditor’s judgment.
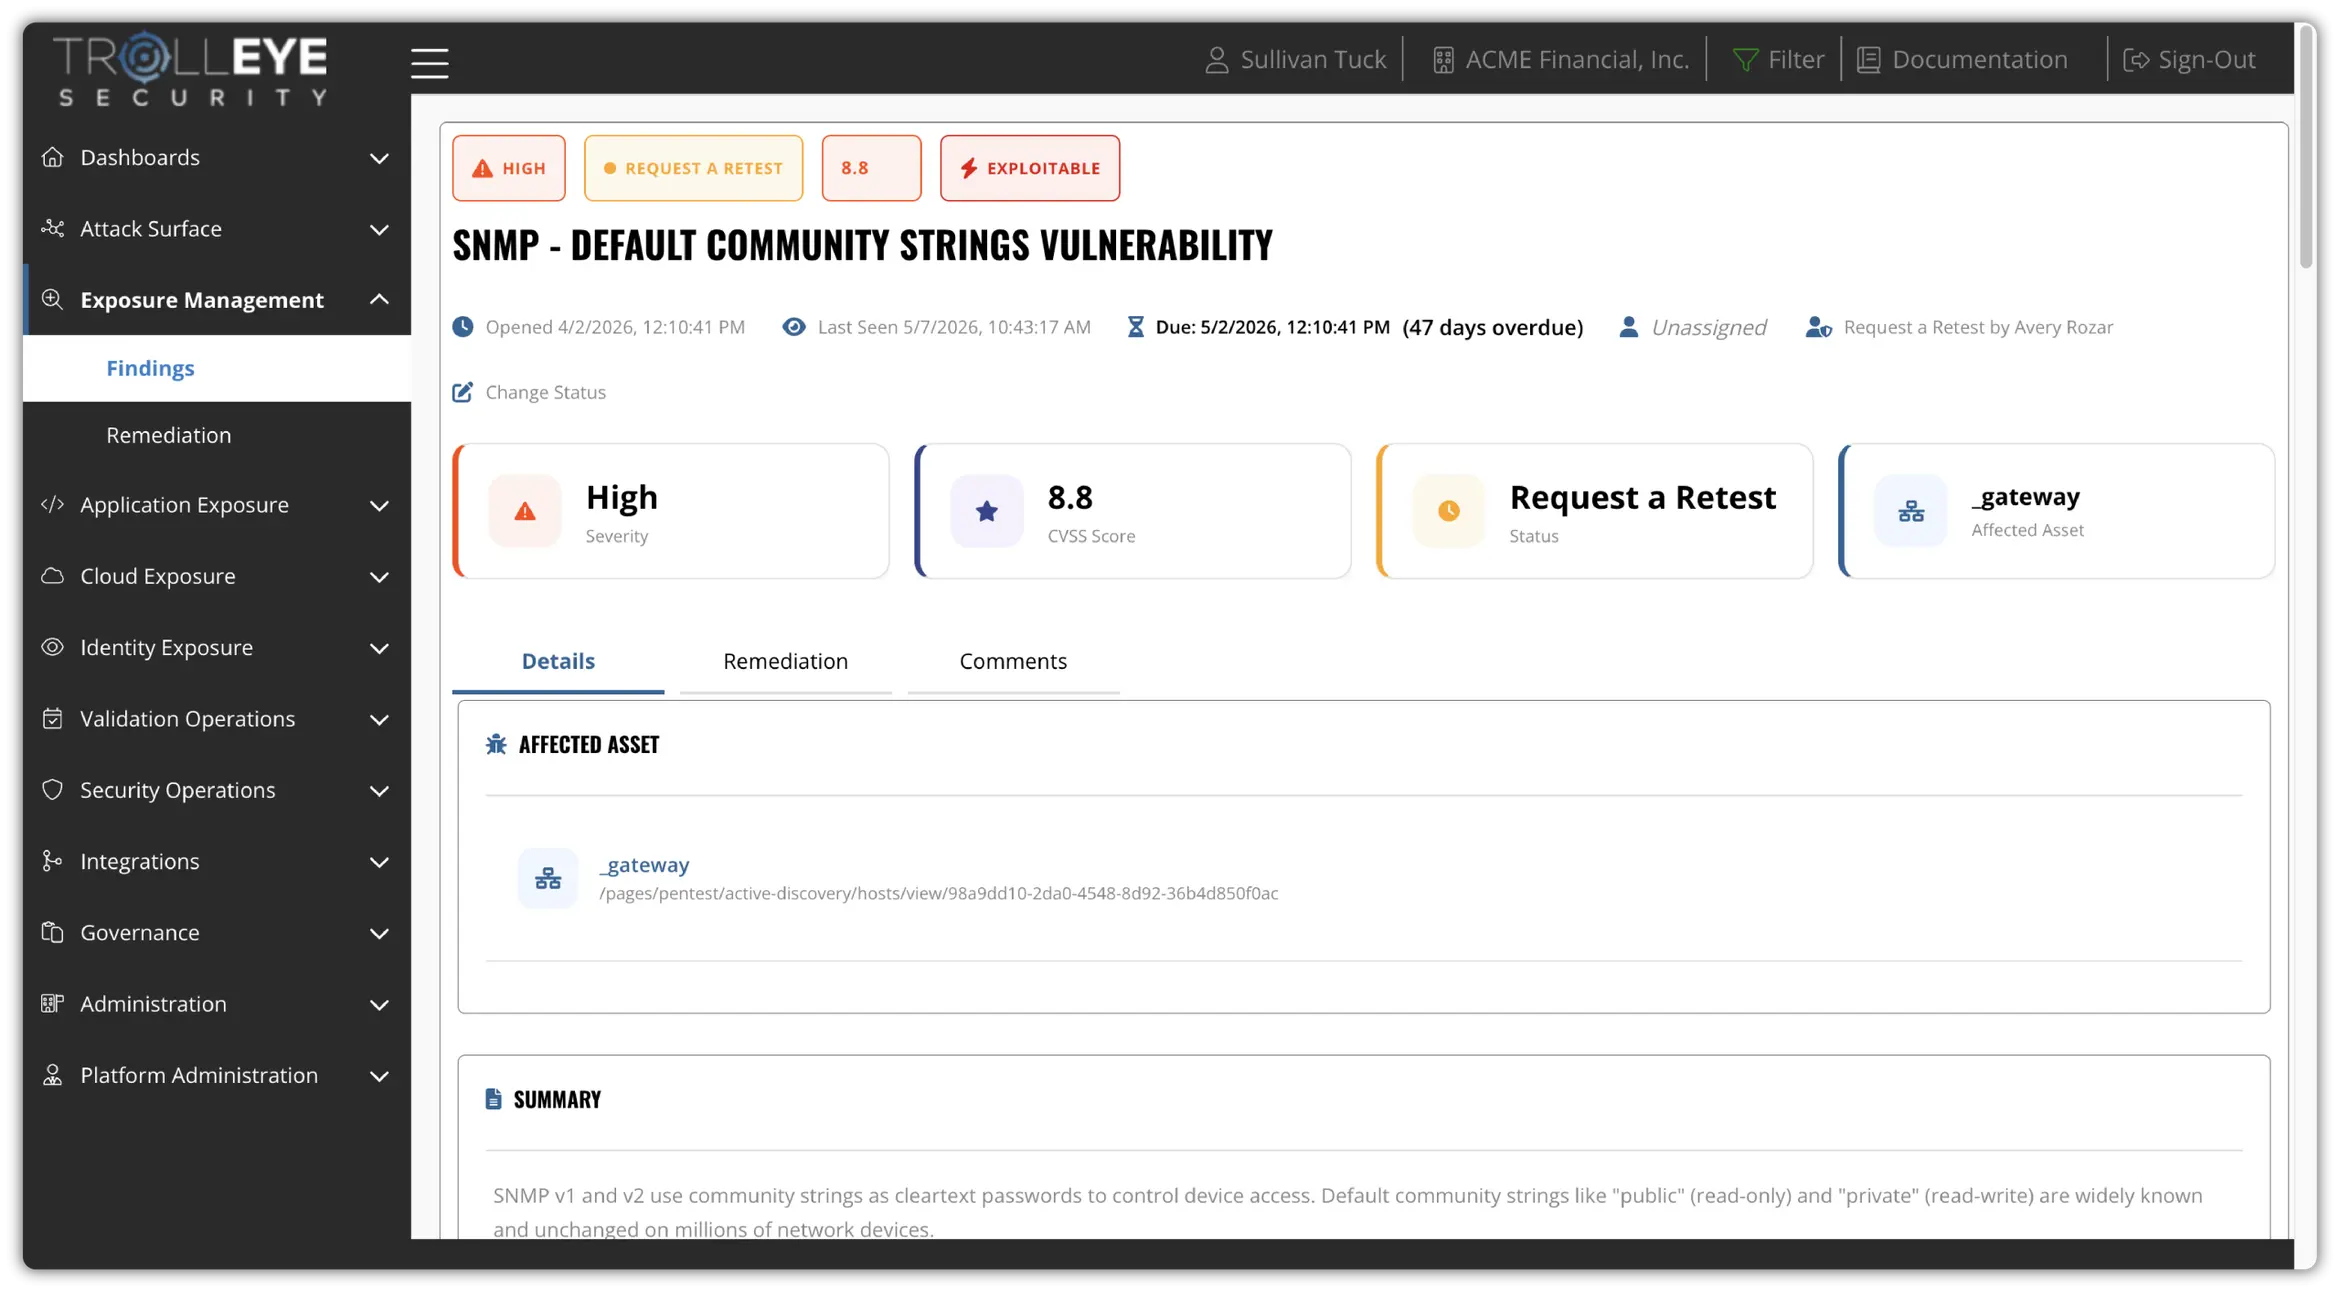
- Testing history for every assessment
- Validated, prioritized findings
- Owners held to remediation SLAs
- Retest records that confirm closure
- Your side of every vendor and member-facing connection, tested
CTEM, built around how utilities operate.
Five stages that run continuously, not once a year.
Scoping
Start with what keeps service runningDiscovery
See every assetPrioritization
Know what threatens service firstValidation
Prove what can reach operationsMobilization
Keep remediation movingSee How TrollEye Helps Lean Utility Teams Close Exposure
Choose a demo to see how audit readiness, continuous testing, attack surface discovery, and remediation work inside the TrollEye platform.
Seven years securing a cooperative’s grid.
Homes and businesses across four Florida counties rely on Talquin Electric Cooperative’s grid, and Talquin has relied on TrollEye to help secure it for seven years.
A security partner for seven years, not a once-a-year visit.
- 57,000+ homes and businesses served
- A 2,600 square-mile service territory
- More than 4,300 miles of electric line
“I consider TrollEye to be a true hidden gem in the realm of security solutions and an invaluable technology partner. Talquin has been utilizing TrollEye’s services for over four years now, and our experience has been nothing short of exceptional.”

Questions About Securing Utilities
A closer look at how TrollEye works for utilities and cooperatives: testing, service uptime, lean teams, audits, vendors, and how it all fits your CTEM program.
01How is this different from our annual penetration test?
An annual test shows your exposure on one day. Your systems, cloud services, member portals, and vendor connections keep changing after it.
TrollEye delivers agentic and human testing on demand and continuously through PTaaS, validates what is actually exploitable and reachable, routes fixes to owners, and retests to confirm closure.
02Can testing avoid disrupting essential services?
Yes. Testing is scoped and scheduled around operational windows, and remediation is weighed against availability and service continuity, not just severity.
03We have a small team. Will this create more work?
No. TrollEye validates findings before they reach your team, so you get fewer, clearer priorities with the evidence and guidance needed to act, instead of a long list of scanner results.
04How does this help with vendor and third-party risk?
Vendor assessments tell you how a provider manages its own security. TrollEye tests your side of each connection: the integrations, remote access paths, and configurations you control.
Learn more in our CTEM vs. TPRM guide.
05Can our in-house team use the platform?
Yes. In-house security and red teams can use the TrollEye platform themselves, so their findings sit alongside ours with the same validation, ownership, SLAs, and retesting.
06How does this fit into a CTEM program?
TrollEye applies each CTEM stage to your organization: scoping the systems and services that matter most, discovering every access path across IT, cloud, identity, and member-facing systems, prioritizing by exploitability and impact on essential services, validating what is actually exploitable and reachable, and mobilizing owners to close it.
Explore audit readiness, continuous testing, attack surface discovery, and remediation before starting your evaluation.
Keep essential services secure and running.
Talk with our practitioners about your utility IT, substations, and remote assets.