TrollEye Security

Web Application Penetration Testing

PART OF PTAASPenetration Testing as a Service→

Web Application Penetration Testing. Release Applications With No Known Vulnerabilities.

Most web application testing still produces long lists of findings with little context around what actually matters. Our web application penetration testing combines agentic and human testing to uncover business logic flaws, access control issues, and chained vulnerabilities, then validates which weaknesses attackers can actually exploit.

It runs inside our PTaaS solution, so every application finding flows into the same platform, the same remediation process, and the same CTEM program as the rest of your testing.
Real-World Application Testing Exploitability Validation Developer-Ready Remediation Verified Fixes
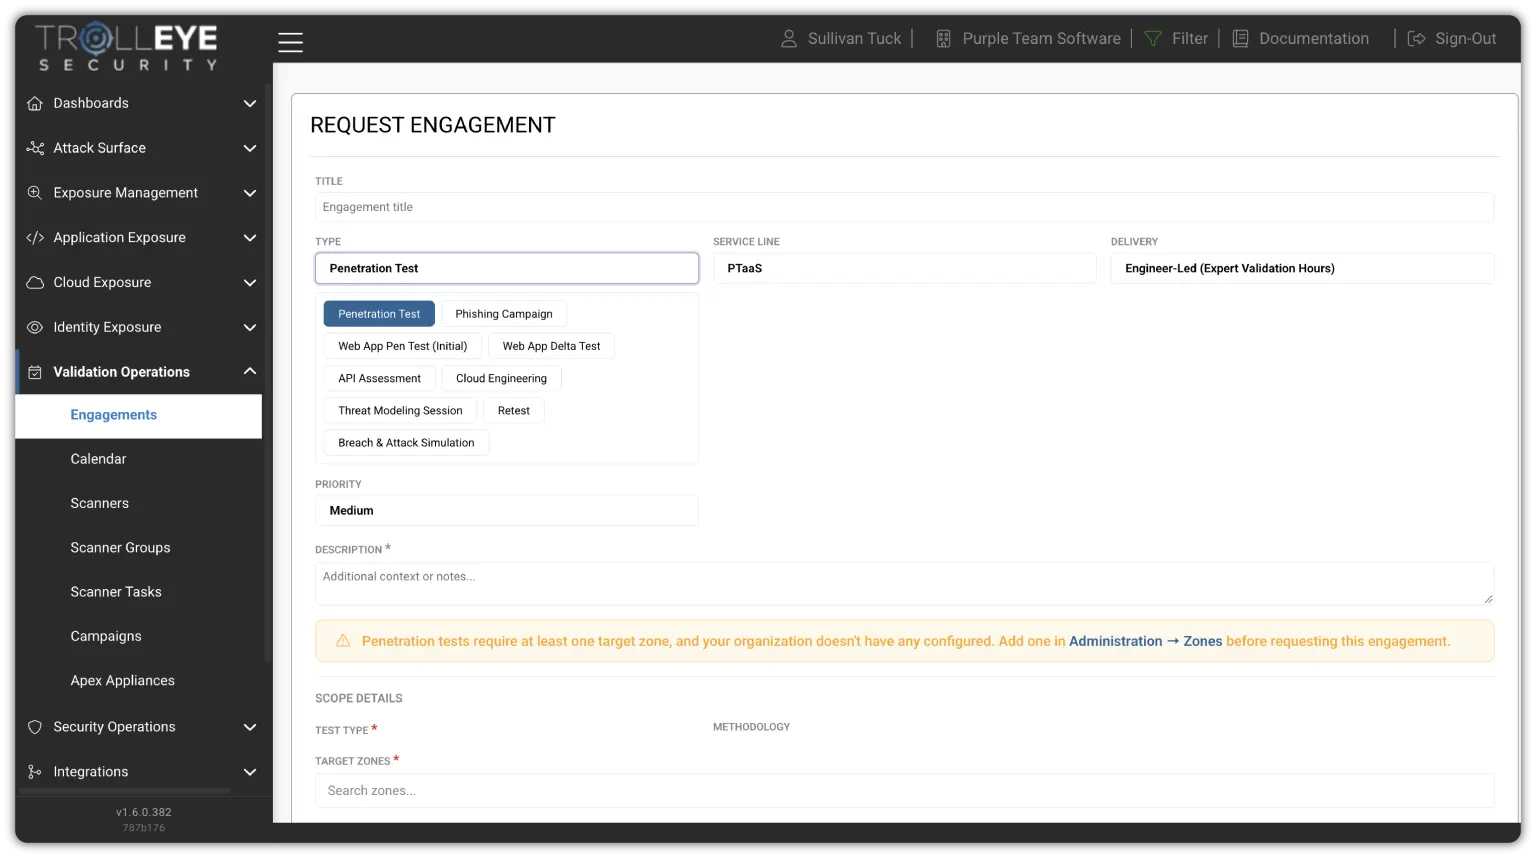
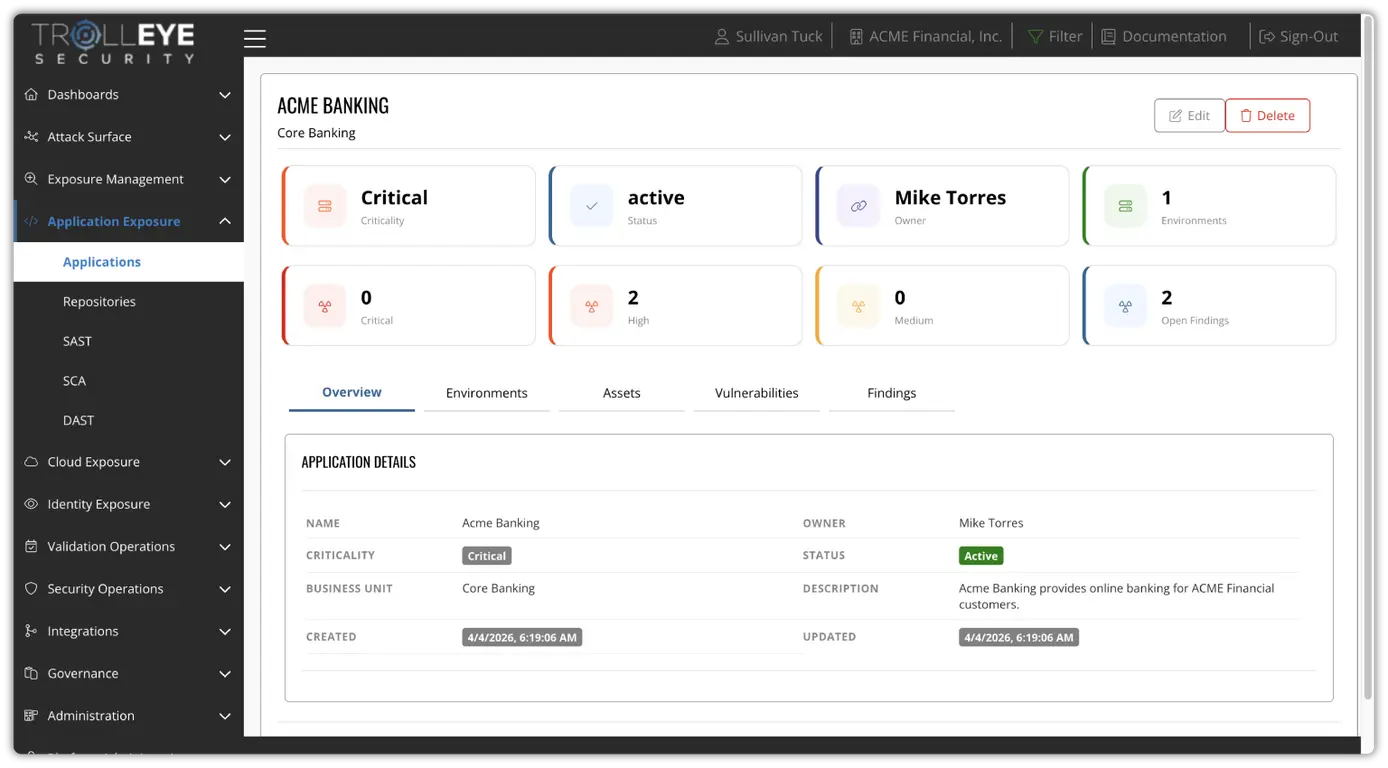
TrollEye platform application view showing findings for a web application
WEB APPLICATION TESTINGTested the way attackers target your apps
PART OF PTAASSame platform, same remediation workflow
WHAT WE TEST

Every Layer Of Your Applications.

Applications change with every release. New features, APIs, user roles, and integrations create exposure that automated scanners can't reason about. Our testers go beyond automated scans, so findings reflect how a real attacker would target your application, not theoretical issues.

Testing inside your pipeline? See DevSecOps as a Service →
01

Business Logic

Workflows, rules, and transactions attackers abuse, which automated scanners can't reason about.

02

Authentication & Sessions

Login flows, password resets, MFA, and session handling tested for weaknesses that grant access.

03

Access Control

User roles and permissions tested for privilege escalation and access to data that should be off-limits.

04

APIs & Integrations

APIs and connected services tested for exposed endpoints, broken authorization, and insecure data exchange.

05

Data Handling

Input handling, injection points, and sensitive data flows tested for exposure and manipulation.

06

Chained Vulnerabilities

Lower-severity issues combined into the high-impact attack paths that scanners routinely miss.

PROVEN IN PRACTICE

Recognized by the Industry. Trusted by Engineering Teams.

Validated application findings and measurable improvement, not just another backlog, in a model recognized by Gartner and trusted by security and engineering teams.

CASE STUDY · SOFTWARE COMPANY

How a Software Company Reduced Vulnerabilities by Over 97% with DevSecOps.

97.5%Fewer vulnerabilities
0Critical & high findings
0Known vulnerabilities at release
“We chose DevSecOps because the traditional annual testing model just wasn’t enough. With multiple fintech applications in production, we needed a way to embed security into our development lifecycle, something continuous, scalable, and built to catch issues before they ever made it to production.”
Vice President of Information Security, Software Company Read the Case Study →
What differentiates TrollEye Security is their level of engagement. They operate as a true partner, embedding into our DevSecOps workflows and working directly with our engineering teams to improve processes and drive remediation. Their ‘white glove’ support model is something we didn’t have with previous vendors. They’re responsive, accessible, and willing to engage in real time when needed.
Ricoh Danielson
Ricoh DanielsonEnterprise CISO, CorroHealth
Watch Video
INHERITED FROM PTAAS

Everything In PTaaS, Applied To Your Applications.

Web application penetration testing isn't a standalone engagement. It runs inside our PTaaS solution, alongside internal, external, network, IoT, and phishing testing, and it's also part of DevSecOps as a Service, with the same platform, the same remediation workflow, and the same agentic and human testing model.

01

Risk-Based Prioritization

Findings are prioritized by exploitability, impact, and application context, not just severity scores, so remediation effort maps directly to risk reduction.

02

Developer-Routed Remediation

Validated findings arrive with exploit evidence, reproduction steps, and clear guidance, routed to the developer or team who can fix them without slowing releases.

03

Managed, Continuous Testing

Our team manages execution, validation, guidance, and retesting, so testing keeps pace with new features, releases, and integrations without building specialized internal capabilities.

ATTACK PATHS WE VALIDATE

From Anonymous User To Business Impact.

Every finding is validated to confirm exploitability and real-world impact. We assess how vulnerabilities interact with application logic, user roles, and connected systems, so teams know which issues matter most and why.

INSIDE THE PLATFORM

How Application Testing Works Inside TrollEye.

Application findings don't arrive as a PDF. They land in the same TrollEye platform as every other PTaaS test, where developers can see what was found, what is exploitable, who owns the fix, and when it has been retested.

Continuous Testing

Automated testing runs continuously against your running applications, so new releases, features, and integrations are covered as they go live, while our testers go deeper where the risk is highest.

  • Automated testing across running applications
  • Coverage that keeps pace with every release
  • Manual testing focused where it matters most
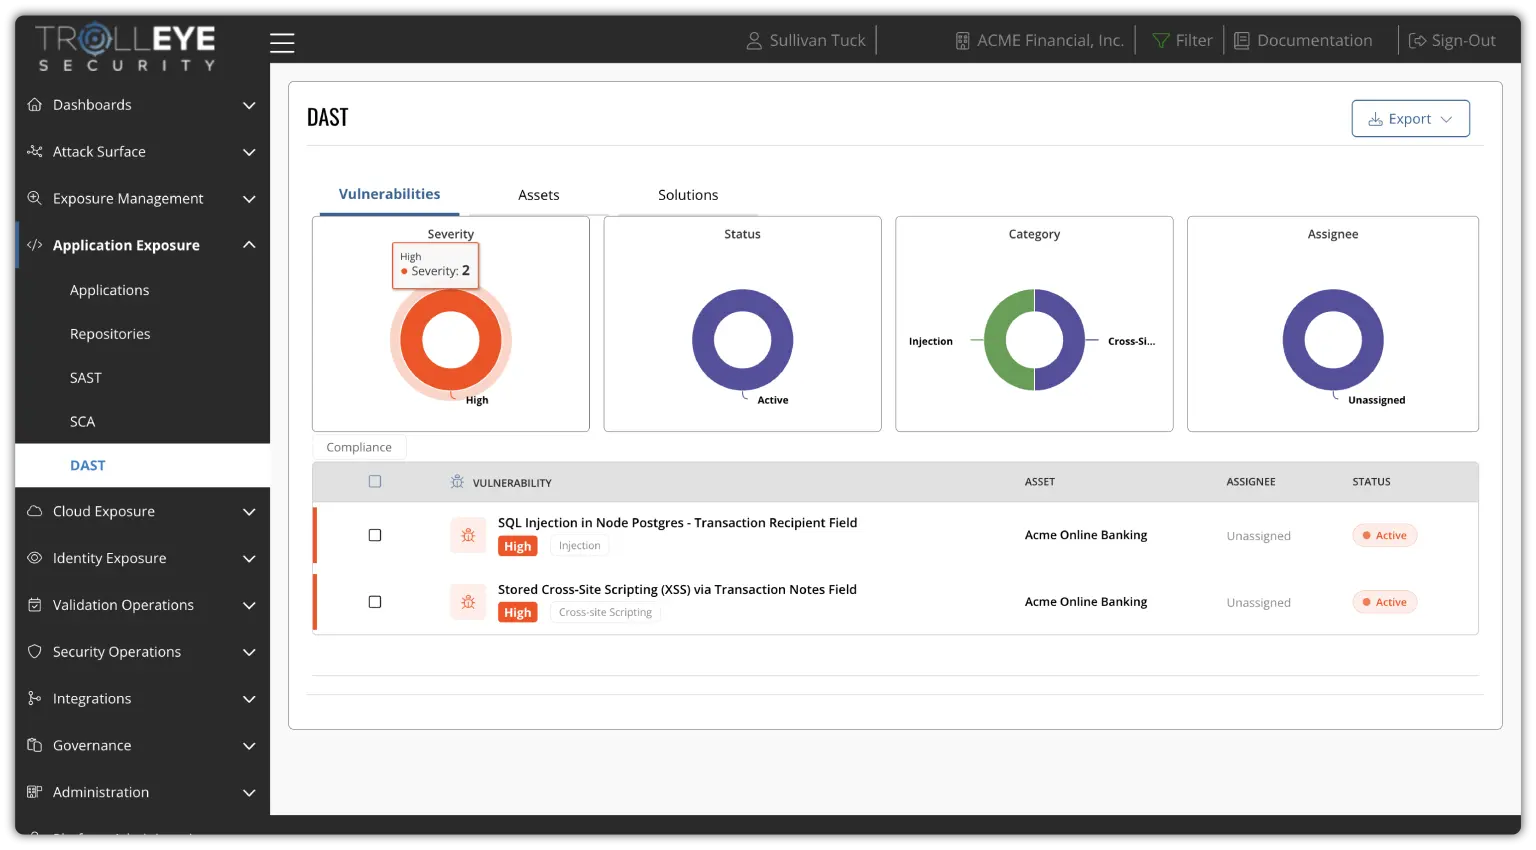
TrollEye platform continuous application testing view

Validated Findings

Each application finding arrives with exploit evidence, reproduction steps, and real-world risk context, so developers see what can actually be exploited instead of scanner severity alone.

  • Exploitability confirmed by our testers
  • Ranked by exploitability, impact, and application context
  • Reproduction steps attached to every finding
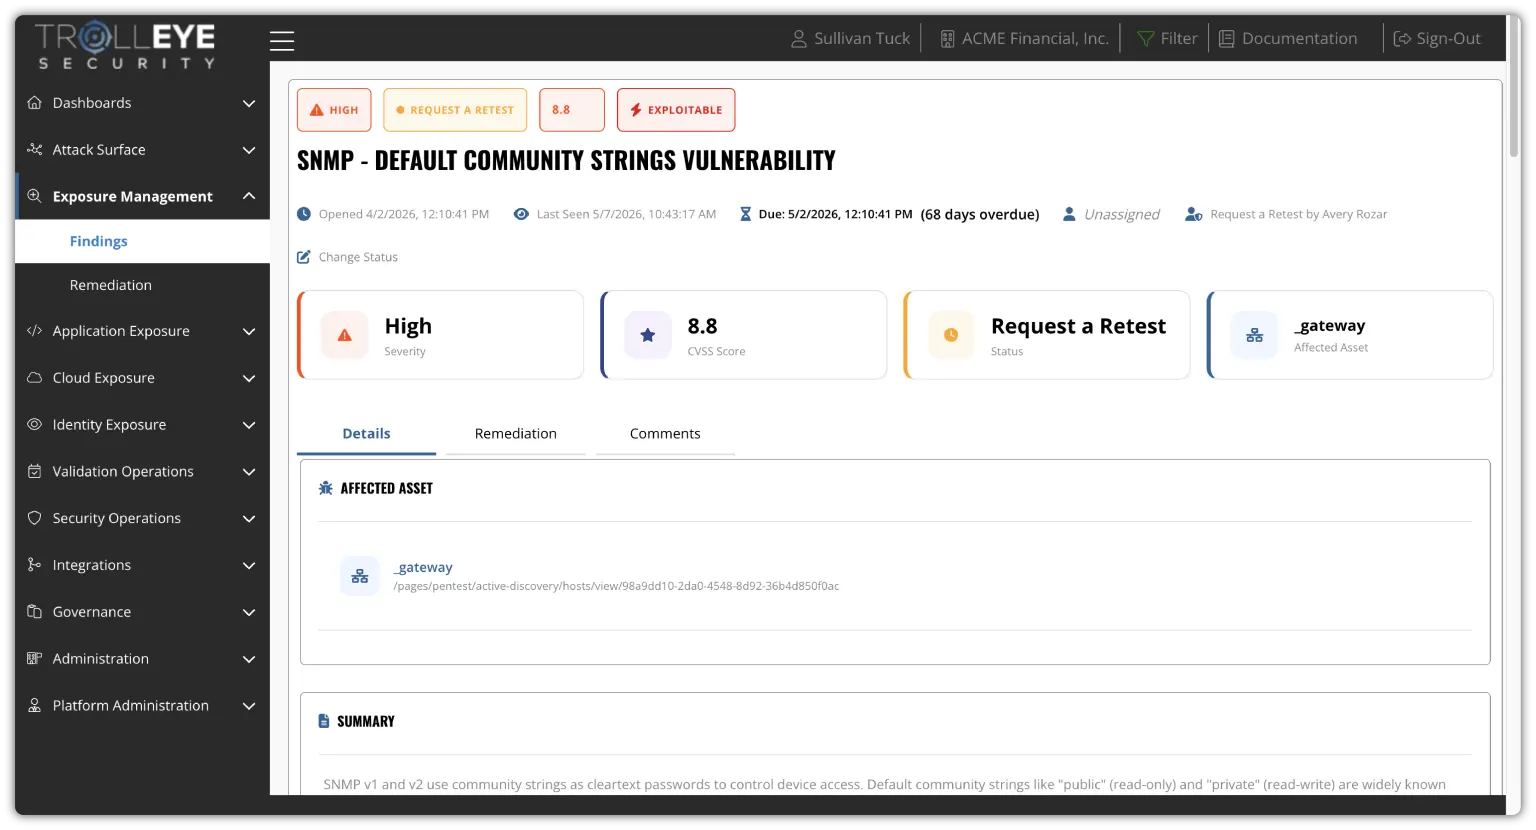
TrollEye platform validated application findings view

Remediation

Findings route to the developer or team responsible for the fix, with clear remediation guidance and progress tracked centrally, so fixes happen without slowing releases.

  • Role-based task distribution
  • Developer-ready remediation guidance
  • Root causes addressed, not just symptoms
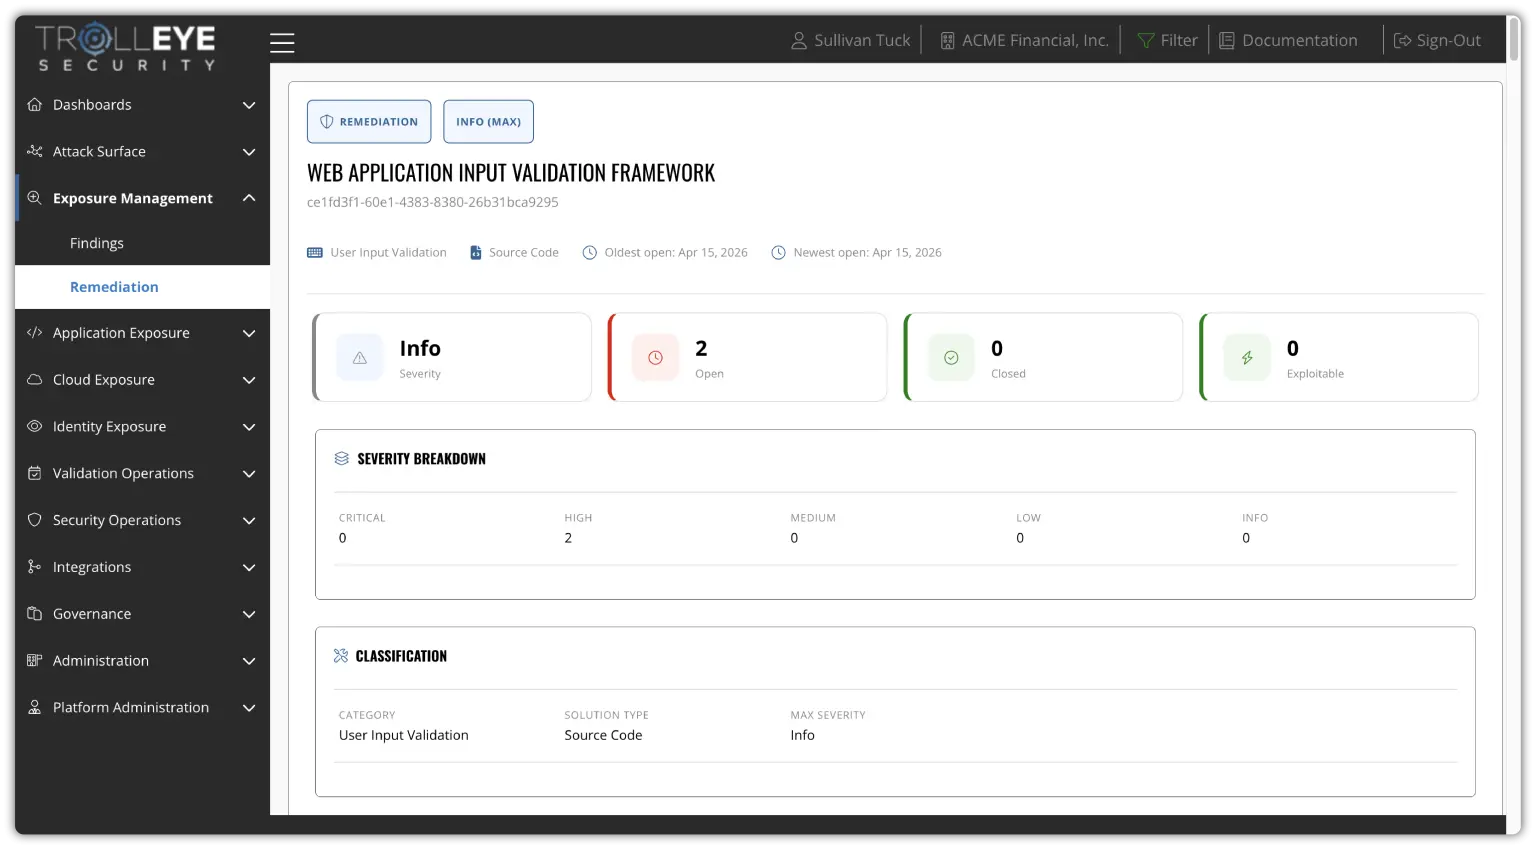
TrollEye platform remediation view

Retesting

Once a fix ships, request a retest directly from the platform and our team confirms the vulnerability is resolved and that no new exposure was introduced through code or configuration changes.

  • Retests requested in one click
  • Regression caught before it becomes a repeat finding
  • Proof for stakeholders and auditors
TrollEye platform retesting view

Reporting

Executive and technical reporting shows how your application exposure trends over time, alongside every other test in your PTaaS program.

  • Executive-ready summaries
  • Technical detail for engineering teams
  • Application results in the context of all PTaaS testing
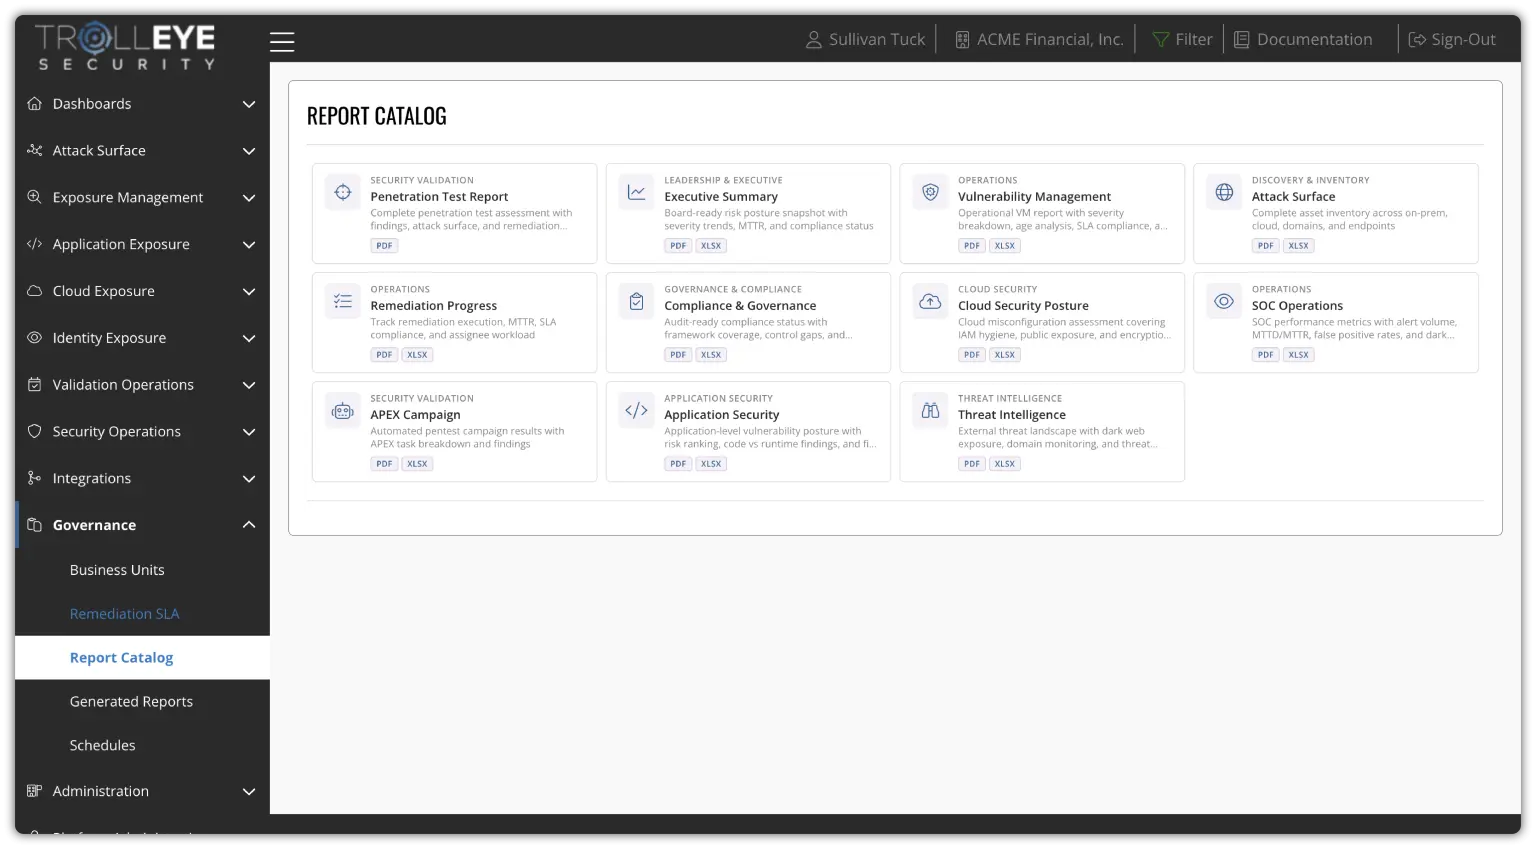
TrollEye platform reporting view
WEB APP TESTING WITHIN CTEM

Validating Your Application Attack Surface Within CTEM.

Web application penetration testing is a core validation component of our Continuous Threat Exposure Management (CTEM) solution for the application domain. By proving which application weaknesses are actually exploitable and reachable, it shows where application exposure presents real risk and where remediation effort should be focused.

Most organizations don’t have a visibility problem. They have an execution problem. Application testing powers the Discovery, Validation, and Mobilization stages for your applications, while Scoping and Prioritization run across your entire attack surface in the same TrollEye platform.

WITHIN OUR CTEM PACKAGES, APPLICATION FINDINGS COMBINE WITH
  • Attack Surface Visibility
  • Cloud Security
  • Identity Exposure
  • Remediation Workflows
  • Continuous Reporting
Web App Testing FAQ

Questions About Web Application Penetration Testing

How web application penetration testing works, what it covers, how findings are validated and prioritized, and how application testing powers the Discovery, Validation, and Mobilization stages of a Continuous Threat Exposure Management (CTEM) program.

01 · SCOPE02 · DISCOVER03 · PRIORITIZE04 · VALIDATE05 · MOBILIZE
01
SCOPEDefine Test Scope
02
DISCOVERMap Application Exposure
03
PRIORITIZERank by Real Risk
04
VALIDATEProve Exploitability
05
MOBILIZEFix and Retest
01 What is web application penetration testing?

Web application penetration testing simulates real-world attacks against your applications to find and validate business-impacting vulnerabilities in logic, authentication, access control, and data handling.

Rather than relying on automated scanning alone, TrollEye combines agentic and human testing to uncover business logic flaws, access control issues, and chained vulnerabilities that tools routinely miss.

02 How is it different from a vulnerability scan?

Scanners flag potential issues based on signatures and severity scores. Penetration testing confirms which weaknesses are actually exploitable, how an attacker would abuse them, and how they interact with your application logic, user roles, and connected systems.

The result is a prioritized set of validated exposures instead of a long list of findings with little context.

03 What does web application penetration testing cover?

Testing covers how your applications actually work, including business logic, authentication and session handling, access control and user roles, APIs and integrations, input and data handling, and the ways lower-severity issues chain together.

Coverage keeps pace with change, so new features, releases, and integrations are tested as they go live.

04 How are application findings validated and prioritized?

Every finding is validated to confirm exploitability and real-world impact, showing how vulnerabilities interact with application logic, user roles, and connected systems.

Findings are then prioritized based on exploitability, impact, and application context, so teams know which issues create real exposure, which can wait, and where remediation effort removes the most risk.

05 How does web application testing fit into PTaaS, DevSecOps, and CTEM?

Web application penetration testing is delivered through our Penetration Testing as a Service (PTaaS) model, so findings live in the same platform and the same remediation process as every other test. It’s also part of DevSecOps as a Service, where testing aligns with sprint cycles, CI/CD pipelines, and release processes alongside DAST, SAST, and SCA.

Within our Continuous Threat Exposure Management (CTEM) program, application testing powers the Discovery, Validation, and Mobilization stages for your applications, mapping application exposure, proving what is exploitable and reachable, and driving validated findings to resolution.

06 How often is web application testing performed?

Automated testing runs continuously across your applications, keeping pace as new features, releases, and integrations go live.

The frequency of expert manual testing depends on how you use your service credits, so you can direct deeper testing toward the applications and changes that matter most.

07 What happens after application findings are remediated?

Findings are delivered through the platform with role-based remediation guidance and reproduction steps, and our team supports developers by answering questions and addressing root causes, not just symptoms.

Once fixes are implemented, we retest affected areas to verify vulnerabilities are fully resolved and that new exposures haven’t been introduced through code or configuration changes, giving your team proof for stakeholders and auditors.

PART OF PTAAS Web application testing is one part of our PTaaS solution.

See how web application, internal, external, network, and IoT testing run together in one platform and one remediation process.

GET STARTED

Don’t Wait For A Breach. Start Securing Your Web Applications Today.

Forward-thinking security teams are turning to continuous web application penetration testing, delivered through Penetration Testing as a Service (PTaaS), to release applications with no known vulnerabilities, maintain regulatory compliance, and stay ahead of attackers. See how application testing fits into a complete CTEM program.

  • 01Continuous real-world application testing
  • 02Validation of exploitable weaknesses
  • 03Developer-ready remediation workflows
  • 04Retesting that confirms every fix
Live Product Update

Meet the Future of
Risk & Remediation

Introducing two major additions to the TrollEye CTEM platform, designed to help teams move from exposure to action.

AI Remediation Agent

AI assistance to help security teams move from findings to fixes faster.

Business Risk Dashboard

New visibility into breach probability, financial risk, and compliance.

Hosted By

Avery Rozar Avery Rozar CEO, TrollEye Security
Sullivan Tuck Sullivan Tuck Head of Growth & Marketing
December 17, 2026 • 2:00 PM ET • Live Online
Reserve Your Spot →

This Content Is Gated