TrollEye Security

DARK WEB ANALYSIS

Identify and Eliminate Dark Web Exposure Across Credentials, Vendors, and Executives.

Most dark web monitoring tools stop at alerting you that credentials have been found. They don’t tell you which ones matter, whether they’re still active, or how they could be used against your organization.

With monthly scanning and hands-on validation by our penetration testers, you’ll know exactly which credentials are exposed, whether they’re actionable, and what a threat actor could do with them.

Credentials
Vendors
Executives
TrollEye CTEM platform breach records view of exposed credentials
CONTINUOUS DARK WEB ANALYSISEvery validated exposure feeds your CTEM program
THE CADENCE Monthly Scanning plus hands-on validation by our penetration testers
VALIDATED RISK, NOT JUST ALERTS

Dark Web Analysis Should Reduce Identity Risk, Not Just Report It.

Our Dark Web Analysis solution is designed to turn breach data into decisions your team can act on.

Instead of a feed of unverified alerts, we combine monthly scanning with hands-on validation by our penetration testers, then carry every confirmed exposure into your CTEM program so it’s prioritized and remediated alongside the rest of your attack surface.

01

Fewer Account Takeovers

Compromised accounts are identified and closed before attackers can use them for takeover, lateral movement, or ransomware access.

02

Less Noise, Clearer Priorities

Every exposure is validated and ranked by privilege and impact, so your team works on what’s actually exploitable.

03

Lasting Exposure Reduction

Trend analysis reveals the root causes behind repeat exposure, so controls get stronger over time instead of resetting with every alert.

OUTCOME 01

Close Compromised Accounts Before They’re Exploited.

Identify exposed credentials tied to your organization and take action before they’re exploited.

01

Validate every credentialConfirm the risk behind each exposed credential instead of reacting to raw alerts.

02

Prioritize by privilegeRank affected users by privilege and business impact so the riskiest accounts are handled first.

03

Shut down accessClose compromised accounts to reduce the likelihood of account takeover, lateral movement, and ransomware access.

TrollEye breach records view of exposed credentials
OUTCOME 02

Analyze Exposure Trends to Stop Repeat Exposure.

Track how your organization’s exposure changes over time across credentials, domains, and data leaks.

01

Spot recurring patternsIdentify recurring patterns and high-risk behaviors across users and domains.

02

Find the root causeGain insight into the root causes behind repeat exposure.

03

Strengthen controlsReinforce controls where breaches and credential reuse are most likely to occur.

TrollEye breach records trend view
OUTCOME 03

Detect Malware and Infostealers Targeting Your Users.

Detect malware, infostealer activity, and credential harvesting operations targeting your environment.

01

Surface infostealer logsSee infostealer logs and harvested credentials tied to your users.

02

Add threat contextBring real-world threat context into your security program.

03

Respond fasterEnable faster response and more accurate prioritization of defensive controls.

TrollEye malware and infostealer breach records
OUTCOME 04

Validate Credentials Through Real-World Testing.

Turn dark web intelligence into action by safely validating exposed credentials during authorized security testing.

01

Confirm real-world impactProve what an exposed credential could actually reach in your environment.

02

Strengthen identity detectionImprove detection around identity-based attacks.

03

Remediate before exploitationFix weaknesses before attackers can exploit them.
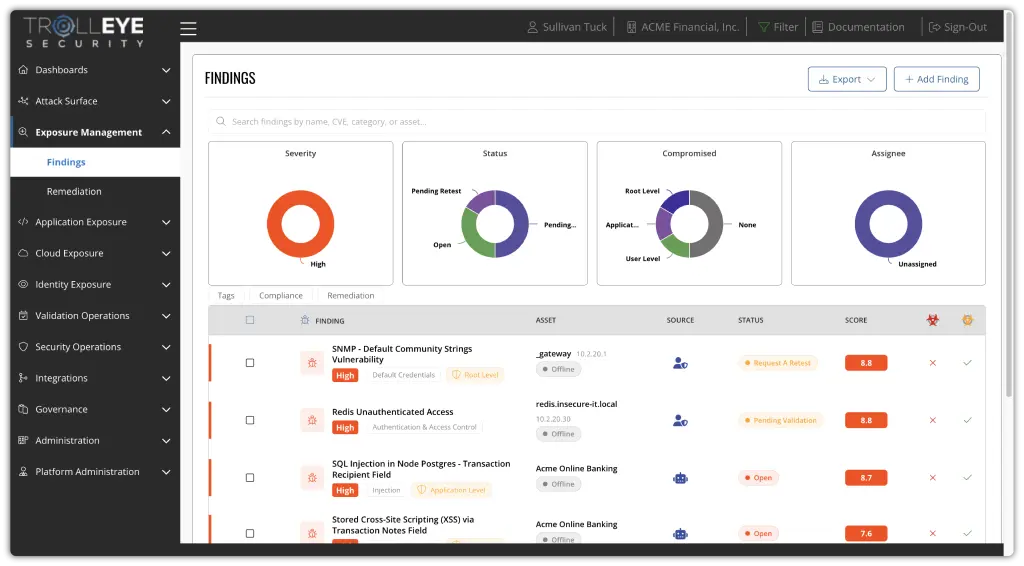
TrollEye validated findings view
COVERAGE & HOW IT WORKS

Every Source of Identity Exposure, Validated and Acted On.

Dark Web Analysis monitors marketplaces, forums, and leak sites for threats tied to your organization, then delivers that intelligence directly to your security team.

Continuous monitoring, expert validation, and coordinated response surface exposed credentials and breaches before they escalate, and make sure your data isn’t being exploited by malicious actors.

WHAT WE MONITOR
SOURCE 01

Employee Credentials

Compromised usernames and passwords for your workforce, found in breach dumps, credential-harvesting operations, and infostealer logs.

  • Leaked credentials tied to your domains
  • Credential reuse across breaches and platforms
  • Plaintext or weakly hashed passwords
SOURCE 02

Third-Party Vendors

Breach records involving the vendors and partners connected to your environment, before their exposure becomes yours.

  • Vendor and partner exposures that impact your attack surface
  • Exposure assessment when a third-party breach is detected
  • Recommended actions like MFA enforcement or vendor escalation
SOURCE 03

Executives

Exposed personal data of executives and other high-value individuals, the people attackers target first.

  • Leaked credentials and personal data tied to leadership
  • Protection from targeted attacks
  • Intelligence delivered directly to your security team
HOW IT WORKS
01
MONITOR

Monitor External Exposure

Ongoing dark web surveillance identifies leaked credentials, breached data, and exposure tied to your executives and third parties.

02
VALIDATE

Validate Compromise

Analysts and penetration testers confirm which exposed credentials and access paths are active and exploitable, so teams act before attackers do.

03
MOBILIZE

Mobilize Response

Our team adds context and routes remediation to the right owners, so compromised access is revoked and risk is reduced quickly.

EVERY VALIDATED FINDING INCLUDES
WhenThe date the data was leaked
HowHow the data was obtained
StatusWhether credentials are still active
PriorityRisk-based ranking for your team
ActionClear remediation guidance

Also monitored: exposure of confidential documents, internal systems, and proprietary data, plus active malware and infostealer campaigns targeting your environment, across every domain, brand, and subsidiary you manage.

See Dark Web Analysis in Action

Explore Dark Web Analysis Inside the TrollEye Platform

Launch the self-guided interactive demo to see how breach data is surfaced, validated, and turned into action inside the TrollEye platform.

Breach records view in the TrollEye platform
IDENTITY EXPOSURE MANAGEMENT

Dark Web Analysis Is How Identity Exposure Enters Your CTEM Program.

Dark Web Analysis provides the identity exposure intelligence layer of our Continuous Threat Exposure Management (CTEM) Solution. By continuously monitoring and validating exposed credentials, breach records, and identity-related risks, it brings one of the most commonly exploited attack vectors into the CTEM lifecycle.

Identity is one domain of your attack surface, alongside network, cloud, and applications. Dark Web Analysis powers the Discovery, Validation, and Mobilization stages for that domain, while Scoping and Prioritization run across your entire attack surface in the same TrollEye platform.

WHERE DARK WEB ANALYSIS FITS IN THE FIVE CTEM STAGES
STAGE 01PLATFORM

Scoping

Define the domains, brands, subsidiaries, executives, and third parties that matter to your business, with each one configured independently.

Explore Scoping →
STAGE 02DARK WEB

Discovery

Monthly scanning of marketplaces, forums, and leak sites surfaces leaked credentials, breach records, and infostealer activity tied to your organization.

Explore Discovery →
STAGE 03PLATFORM

Prioritization

Findings are correlated to identity controls, privilege levels, and business impact, then prioritized alongside application, cloud, and infrastructure exposures.

Explore Prioritization →
STAGE 04DARK WEB

Validation

Our penetration testers safely use exposed credentials during authorized testing to prove what is actually exploitable and reachable.

Explore Validation →
STAGE 05DARK WEB

Mobilization

Forced resets, account takedowns, MFA enforcement, and vendor escalation are routed to the right owners, with progress tracked in cadence meetings.

Explore Mobilization →
INSIDE OUR CTEM PACKAGES

Identity Exposures Don’t Exist In Isolation.

Within our CTEM packages, leaked credentials, breach records, infostealer activity, and vendor and executive exposure are correlated with application, cloud, and operational risks, helping security teams focus on the remediation activities that will have the greatest impact on overall risk reduction.

DARK WEB ANALYSIS FAQS

Dark Web Analysis Questions, Answered.

What Dark Web Analysis covers, how it differs from basic monitoring, and how it fits into your CTEM program.

COVERAGE VALIDATION REMEDIATION CTEM
01 What is Dark Web Analysis?

Dark Web Analysis is a continuous cybersecurity service that monitors dark web marketplaces, forums, and leak sites for threats tied to your organization. It identifies compromised employee credentials, breach records involving third-party vendors, and exposed personal data of executives.

This intelligence is delivered directly to your security team, enabling them to secure accounts, assess vendor risk, and protect high-value individuals from targeted attacks.

02 How is this different from basic dark web monitoring?

Basic dark web monitoring tools rely entirely on automated scraping and often return noisy, unverified results. Our Dark Web Analysis goes beyond that. Every alert is manually validated by our analysts, reducing false positives and ensuring the exposures we report are accurate, actionable, and prioritized by risk.

We also provide context, such as when the data was leaked, how it was obtained, and whether credentials are still active, so you can take targeted action.

03 What types of threats do you detect?

We identify and analyze a wide range of threats, including:

  • Leaked credentials related to your organization, including executives, employees, and customers.
  • Credential reuse across multiple breaches and platforms.
  • Passwords stored in plaintext or weakly hashed formats.
  • Exposure of confidential documents, internal systems, and proprietary data.
  • Vendor and partner exposures that could impact your attack surface.
04 Do you provide remediation recommendations?

Yes, every alert comes with clear, actionable guidance based on the nature of the exposure. For example:

  • If a password is exposed and still in use, we recommend a forced reset and review of other systems where it may have been reused.
  • If a third-party breach is detected, we help assess your exposure and recommend security actions like MFA enforcement or vendor escalation.

Our cadence meetings also provide a space to walk through exposures, prioritize response, and track risk reduction over time.

05 Can we monitor more than one domain or brand?

Absolutely. Our Dark Web Analysis solution supports multi-domain monitoring, making it ideal for holding companies, multinational organizations, or those managing multiple brands or subsidiaries. You can configure each domain or brand independently and receive reports that segment data accordingly.

06 How does Dark Web Analysis fit into CTEM?

Dark Web Analysis provides the identity exposure intelligence layer of our CTEM Solution. Within our CTEM packages, its findings are prioritized alongside application, cloud, and infrastructure exposures, validated through authorized testing, and mobilized to the teams responsible for fixing them.

STILL EVALUATING? See which exposed credentials actually put you at risk.

Start with your own domain and see how TrollEye turns dark web findings into validated, prioritized action.

GET STARTED

Dark Web Knowledge Is Power. Turn Breach Data Into Actionable Risk Reduction.

Dark Web Analysis goes beyond surface-level monitoring. It validates which exposed credentials and breach records create real, exploitable risk to your organization, correlating findings to identity controls, privilege levels, and business impact.

  • 01Monthly dark web scanning
  • 02Hands-on validation by penetration testers
  • 03Credential, vendor, and executive coverage
  • 04Remediation that revokes compromised access

Conversations with CISOs

Live CISO Roundtable & AMA

Doing More with Less

Four security leaders. One candid conversation about budgets, teams, security tools, and the tradeoffs CISOs face heading into 2027.

October 29, 2026 • 2:00 PM ET • Live Online

Join the Conversation With

Jeff Moore Jeff Moore CISO, H&M
Elizabeth Di Bene Elizabeth Di Bene CISO, Loudon County
JoJo D JoJo D Cyber Leader, Co-Founder of Chaos & Signal
Aby Rao Aby Rao Deputy CISO, Fintech
Register & Submit Your Questions →

This Content Is Gated