Find Code-Level Vulnerabilities. Before They Reach Production.
Identify injection flaws, insecure data handling, and unsafe code patterns early, before your pipeline runs and developers lose context.
TrollEye’s SAST service integrates into your CI/CD workflow and our platform, so CWE-mapped findings move from detection to developer-aligned remediation and confirmed fixes inside one continuous process.
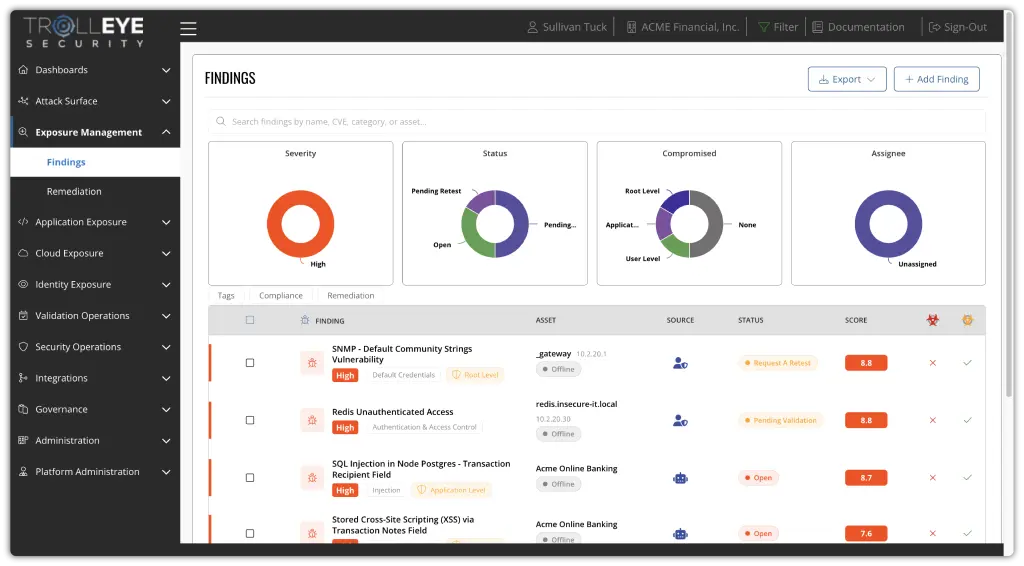
SAST Should Do More Than Flag Code Issues.
TrollEye combines continuous static analysis, expert triage, and developer-aligned remediation support to help your team eliminate code-level vulnerabilities, not just generate another scan report.
The result is a continuous operating model that catches flaws at the source, gets them to the right developers, fixes them efficiently, and keeps them out of production.
Find Vulnerabilities Before Your Pipeline Runs.
Code-level flaws such as SQL injection, broken access control, insecure deserialization, and hardcoded secrets cost far more to fix after deployment than before it. Static analysis on every commit surfaces them while developers still have context.
Scan every commit Analyze first-party source code as it’s written, not weeks later in a release review.
Map findings to CWE Identify OWASP Top 10 and CWE-mapped weaknesses down to the file and line where they live.
Cut costly rework Fix issues during development, when they’re cheapest and fastest to resolve.
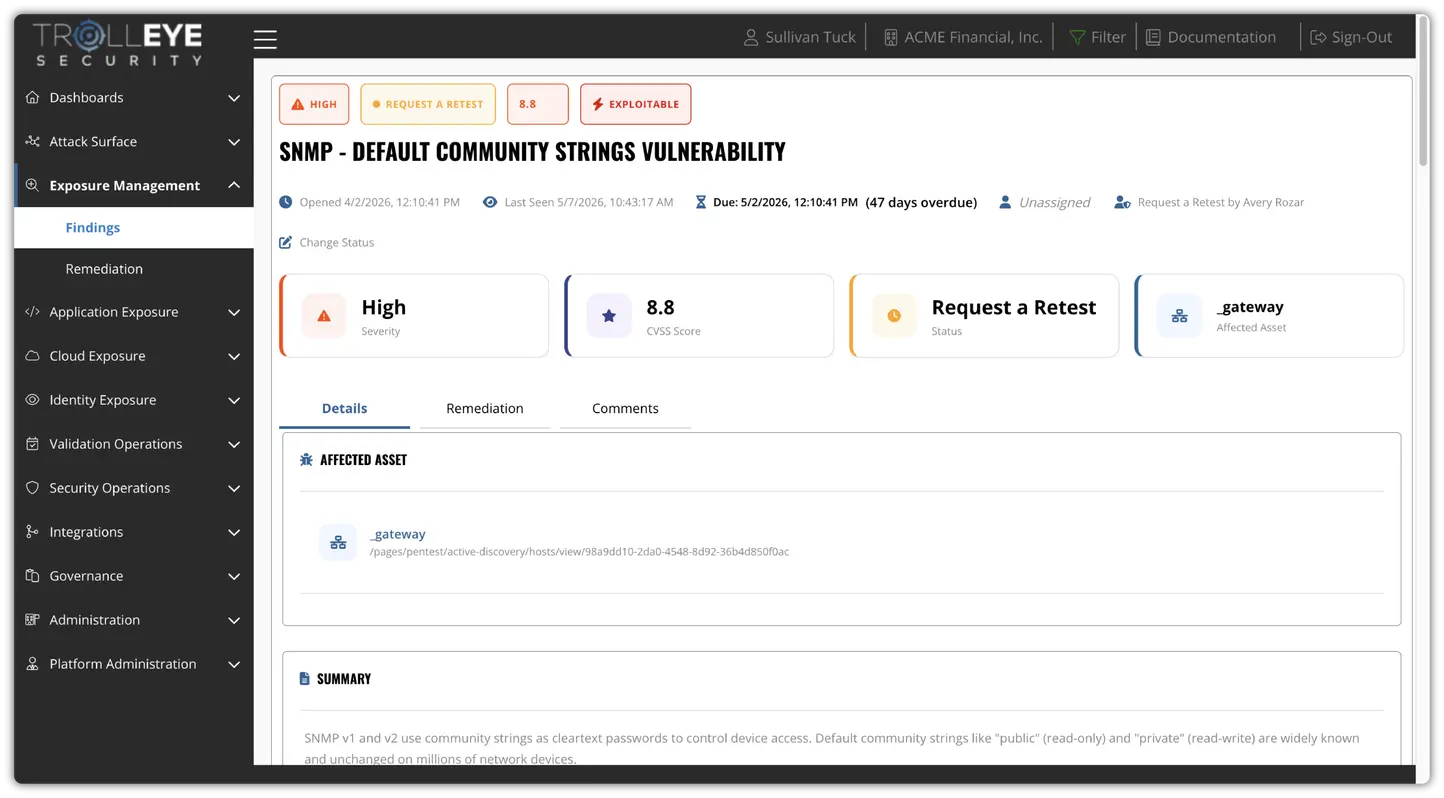
Build Secure Coding Into Everyday Engineering.
SAST gives developers real-time feedback on insecure patterns as they write code, making security a natural part of the workflow rather than a downstream checkpoint.
Embed security in development Bring static analysis into repositories and CI/CD instead of a separate review stage.
Build team-wide awareness Help developers recognize and avoid insecure patterns with every release.
Reduce late-stage reviews Rely less on last-minute security checks that stall deployments.
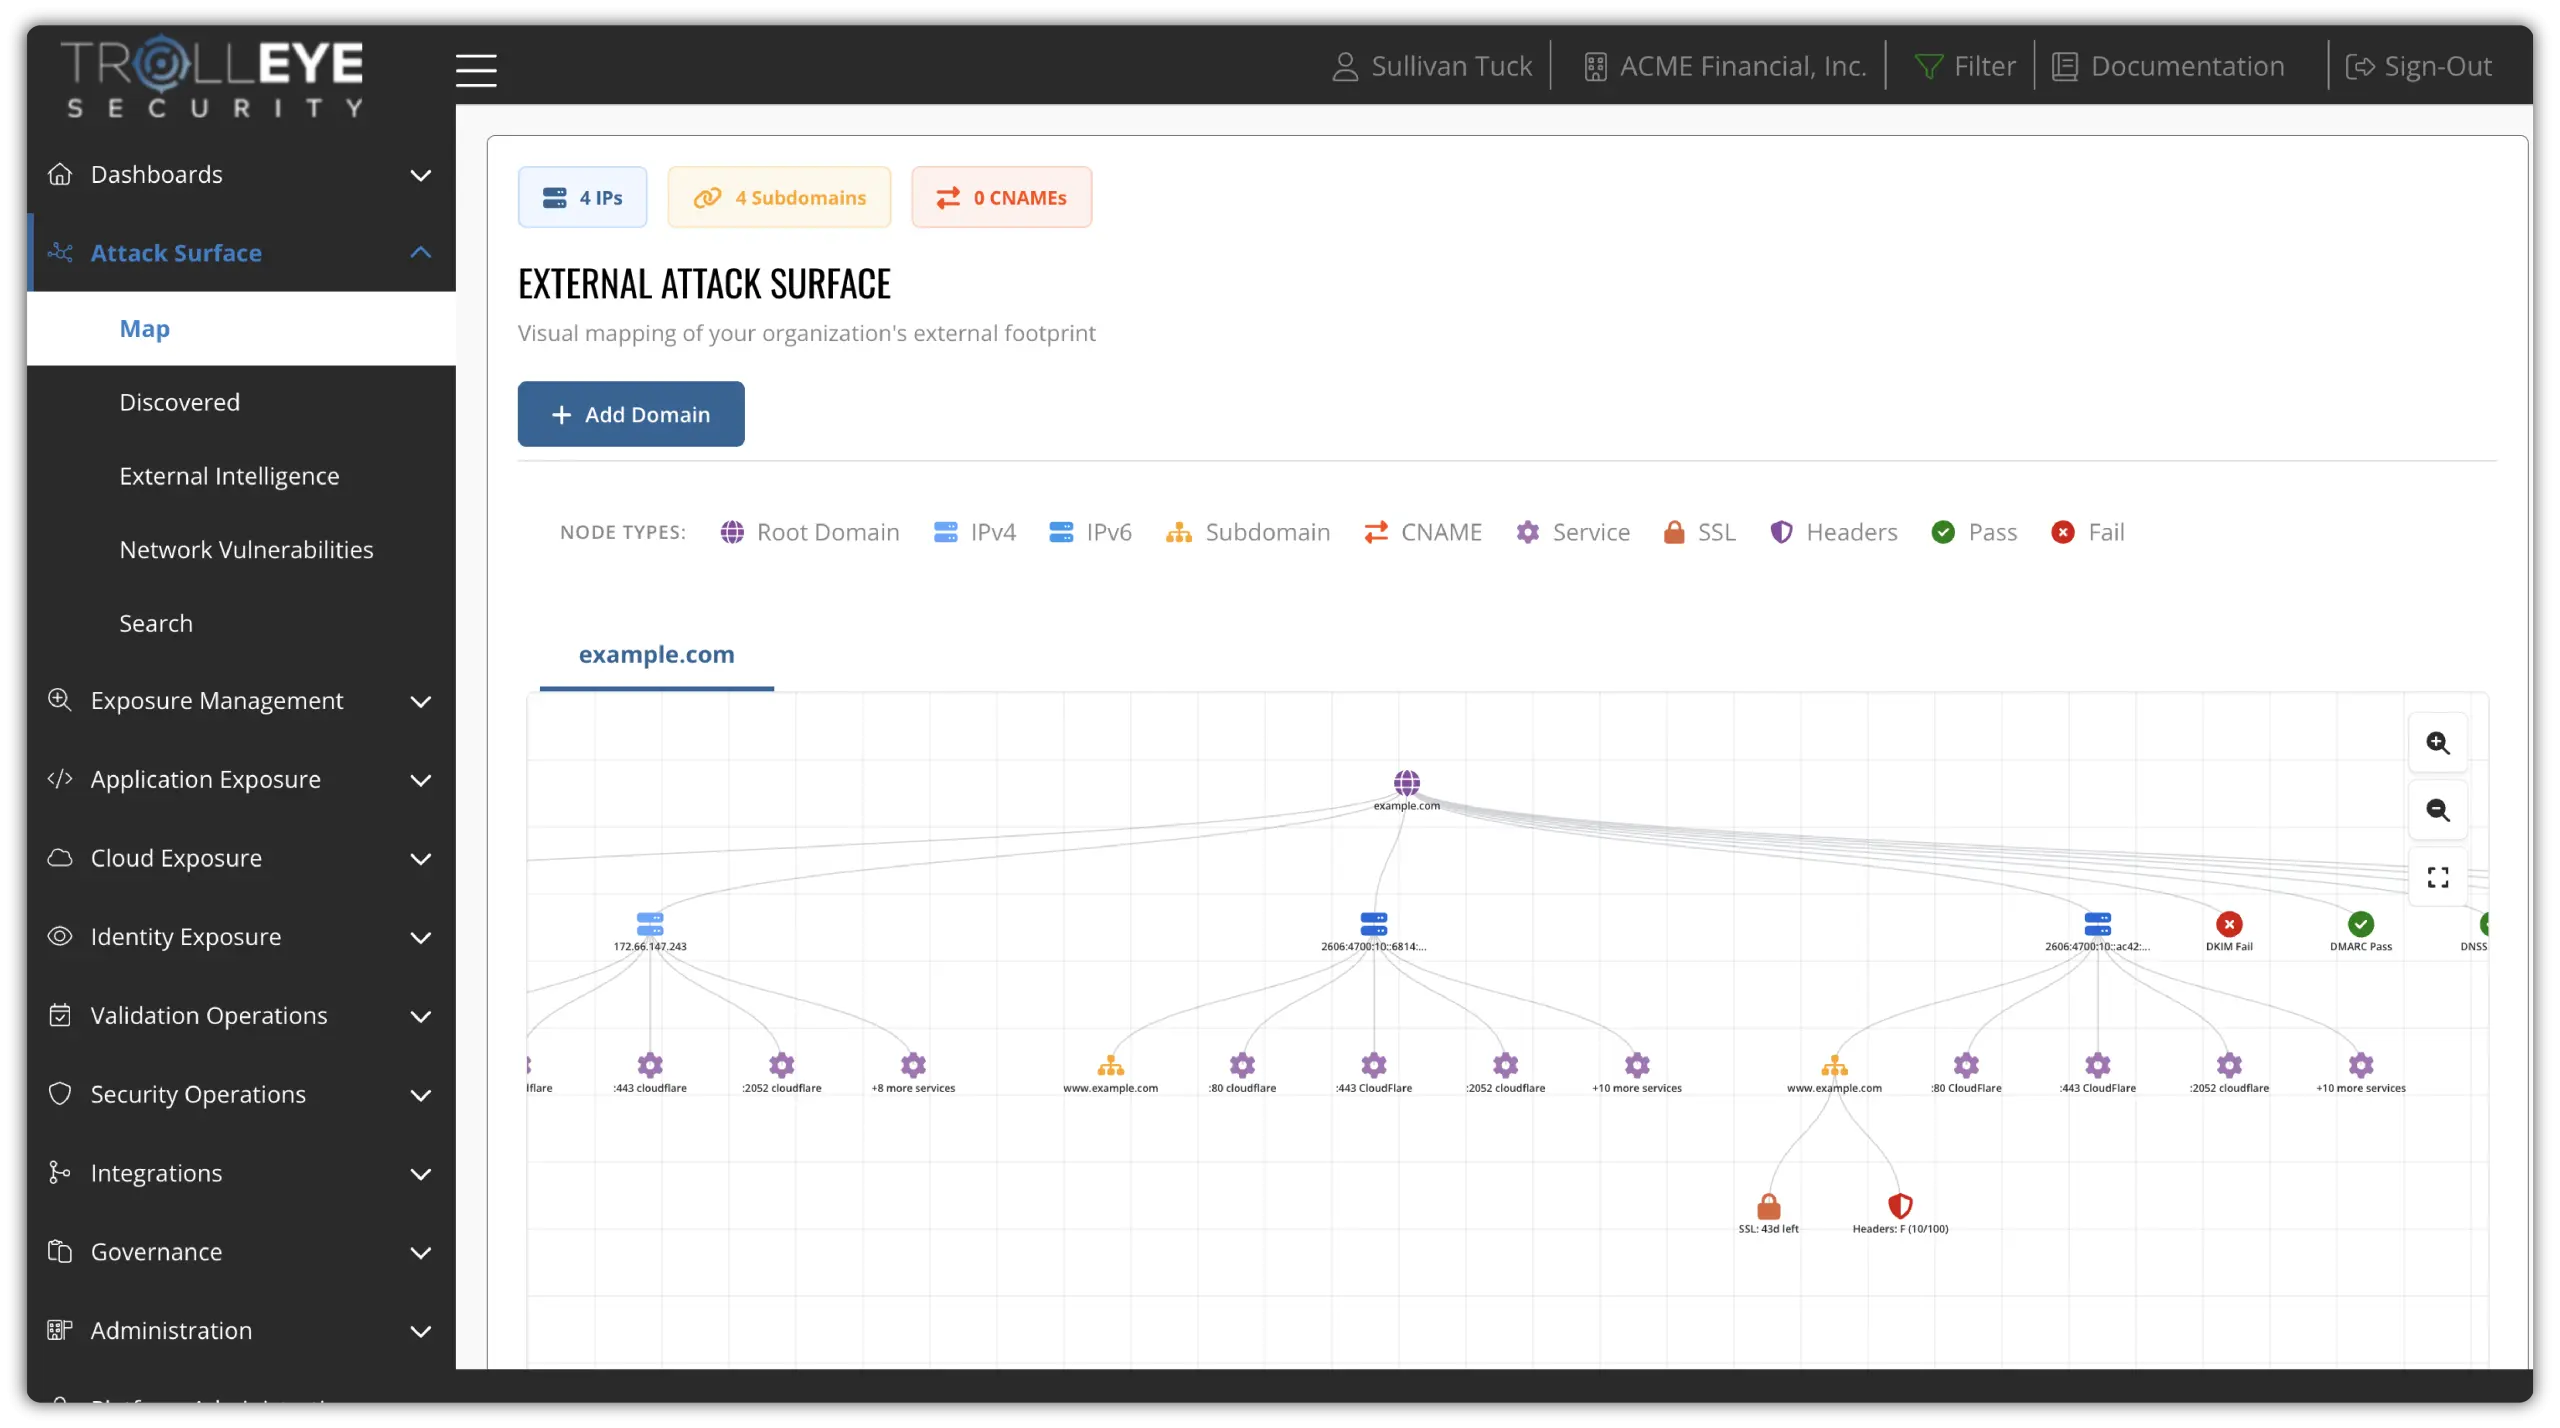
Route Every Finding To The Developer Who Can Fix It.
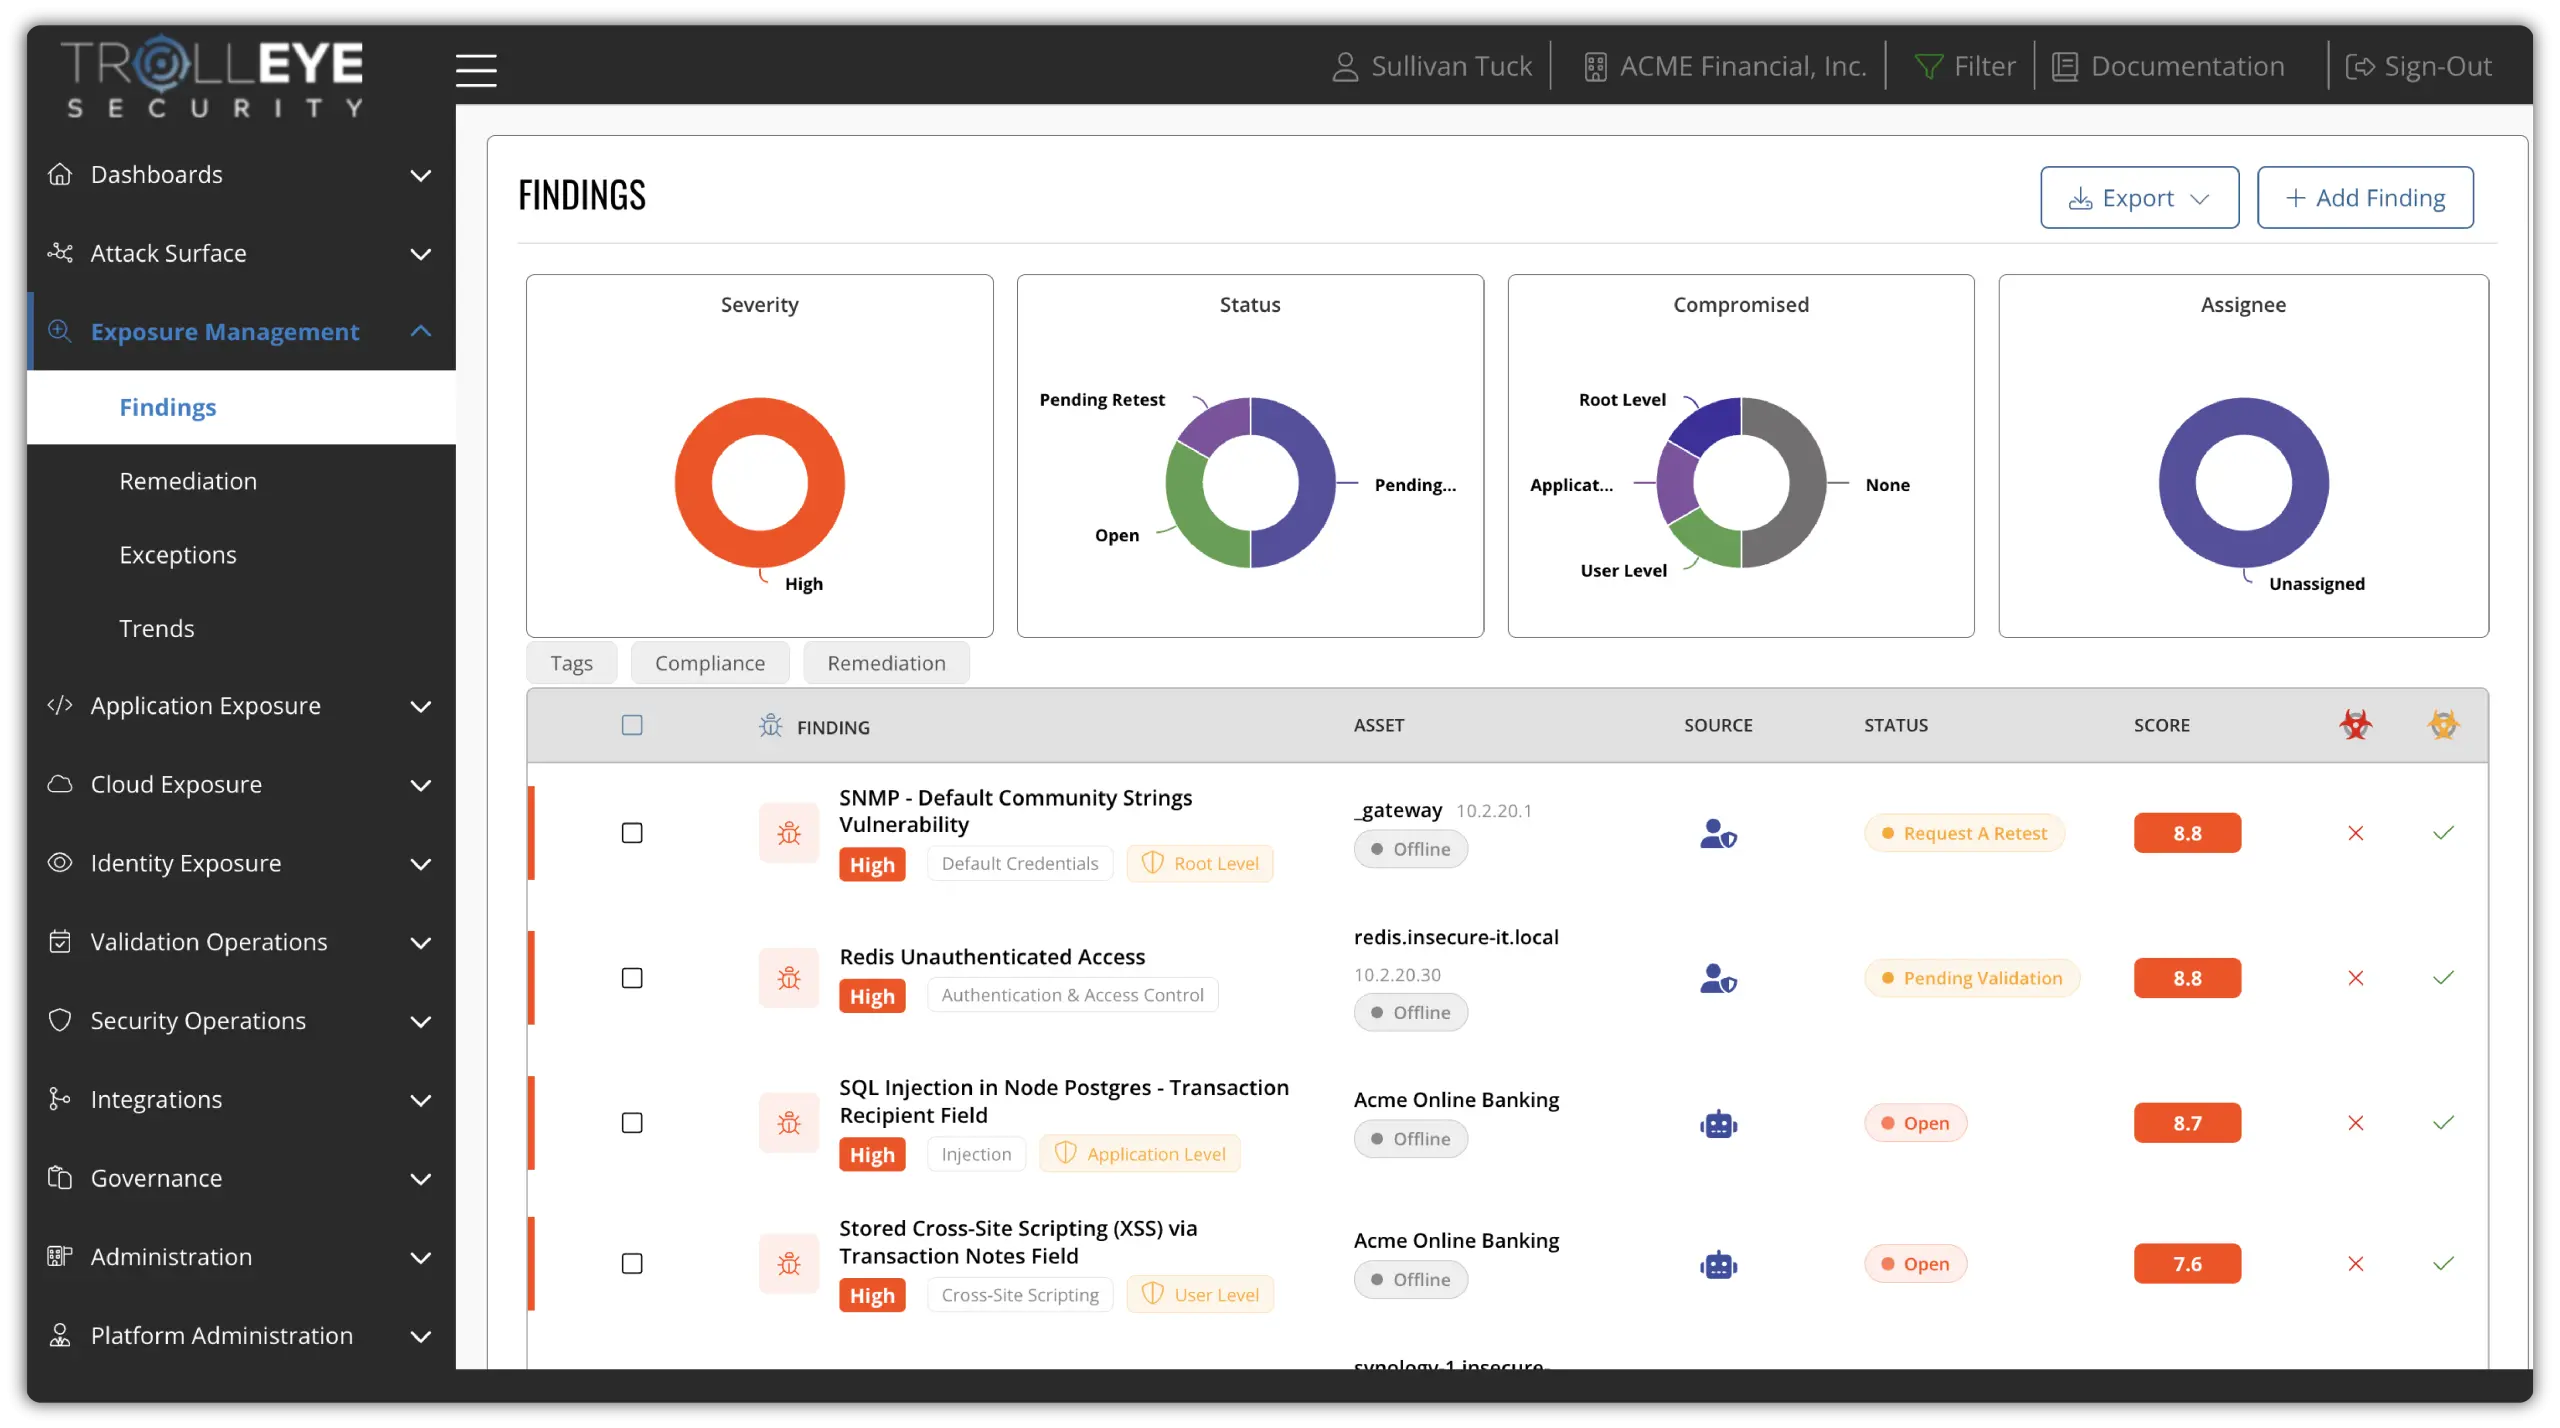
Triaged findings move directly to the repository owners responsible, with line-level context and clear guidance, so remediation is assigned, tracked, and closed inside existing workflows.
Create clear ownership Assign every finding to the team or developer responsible for the affected code.
Cut through scanner noise Remove false positives so developers spend their time on real issues, not triage.
Keep context intact Give developers the technical detail and remediation guidance they need to act without back-and-forth.
Fix The Root Cause, Not Just The Finding.
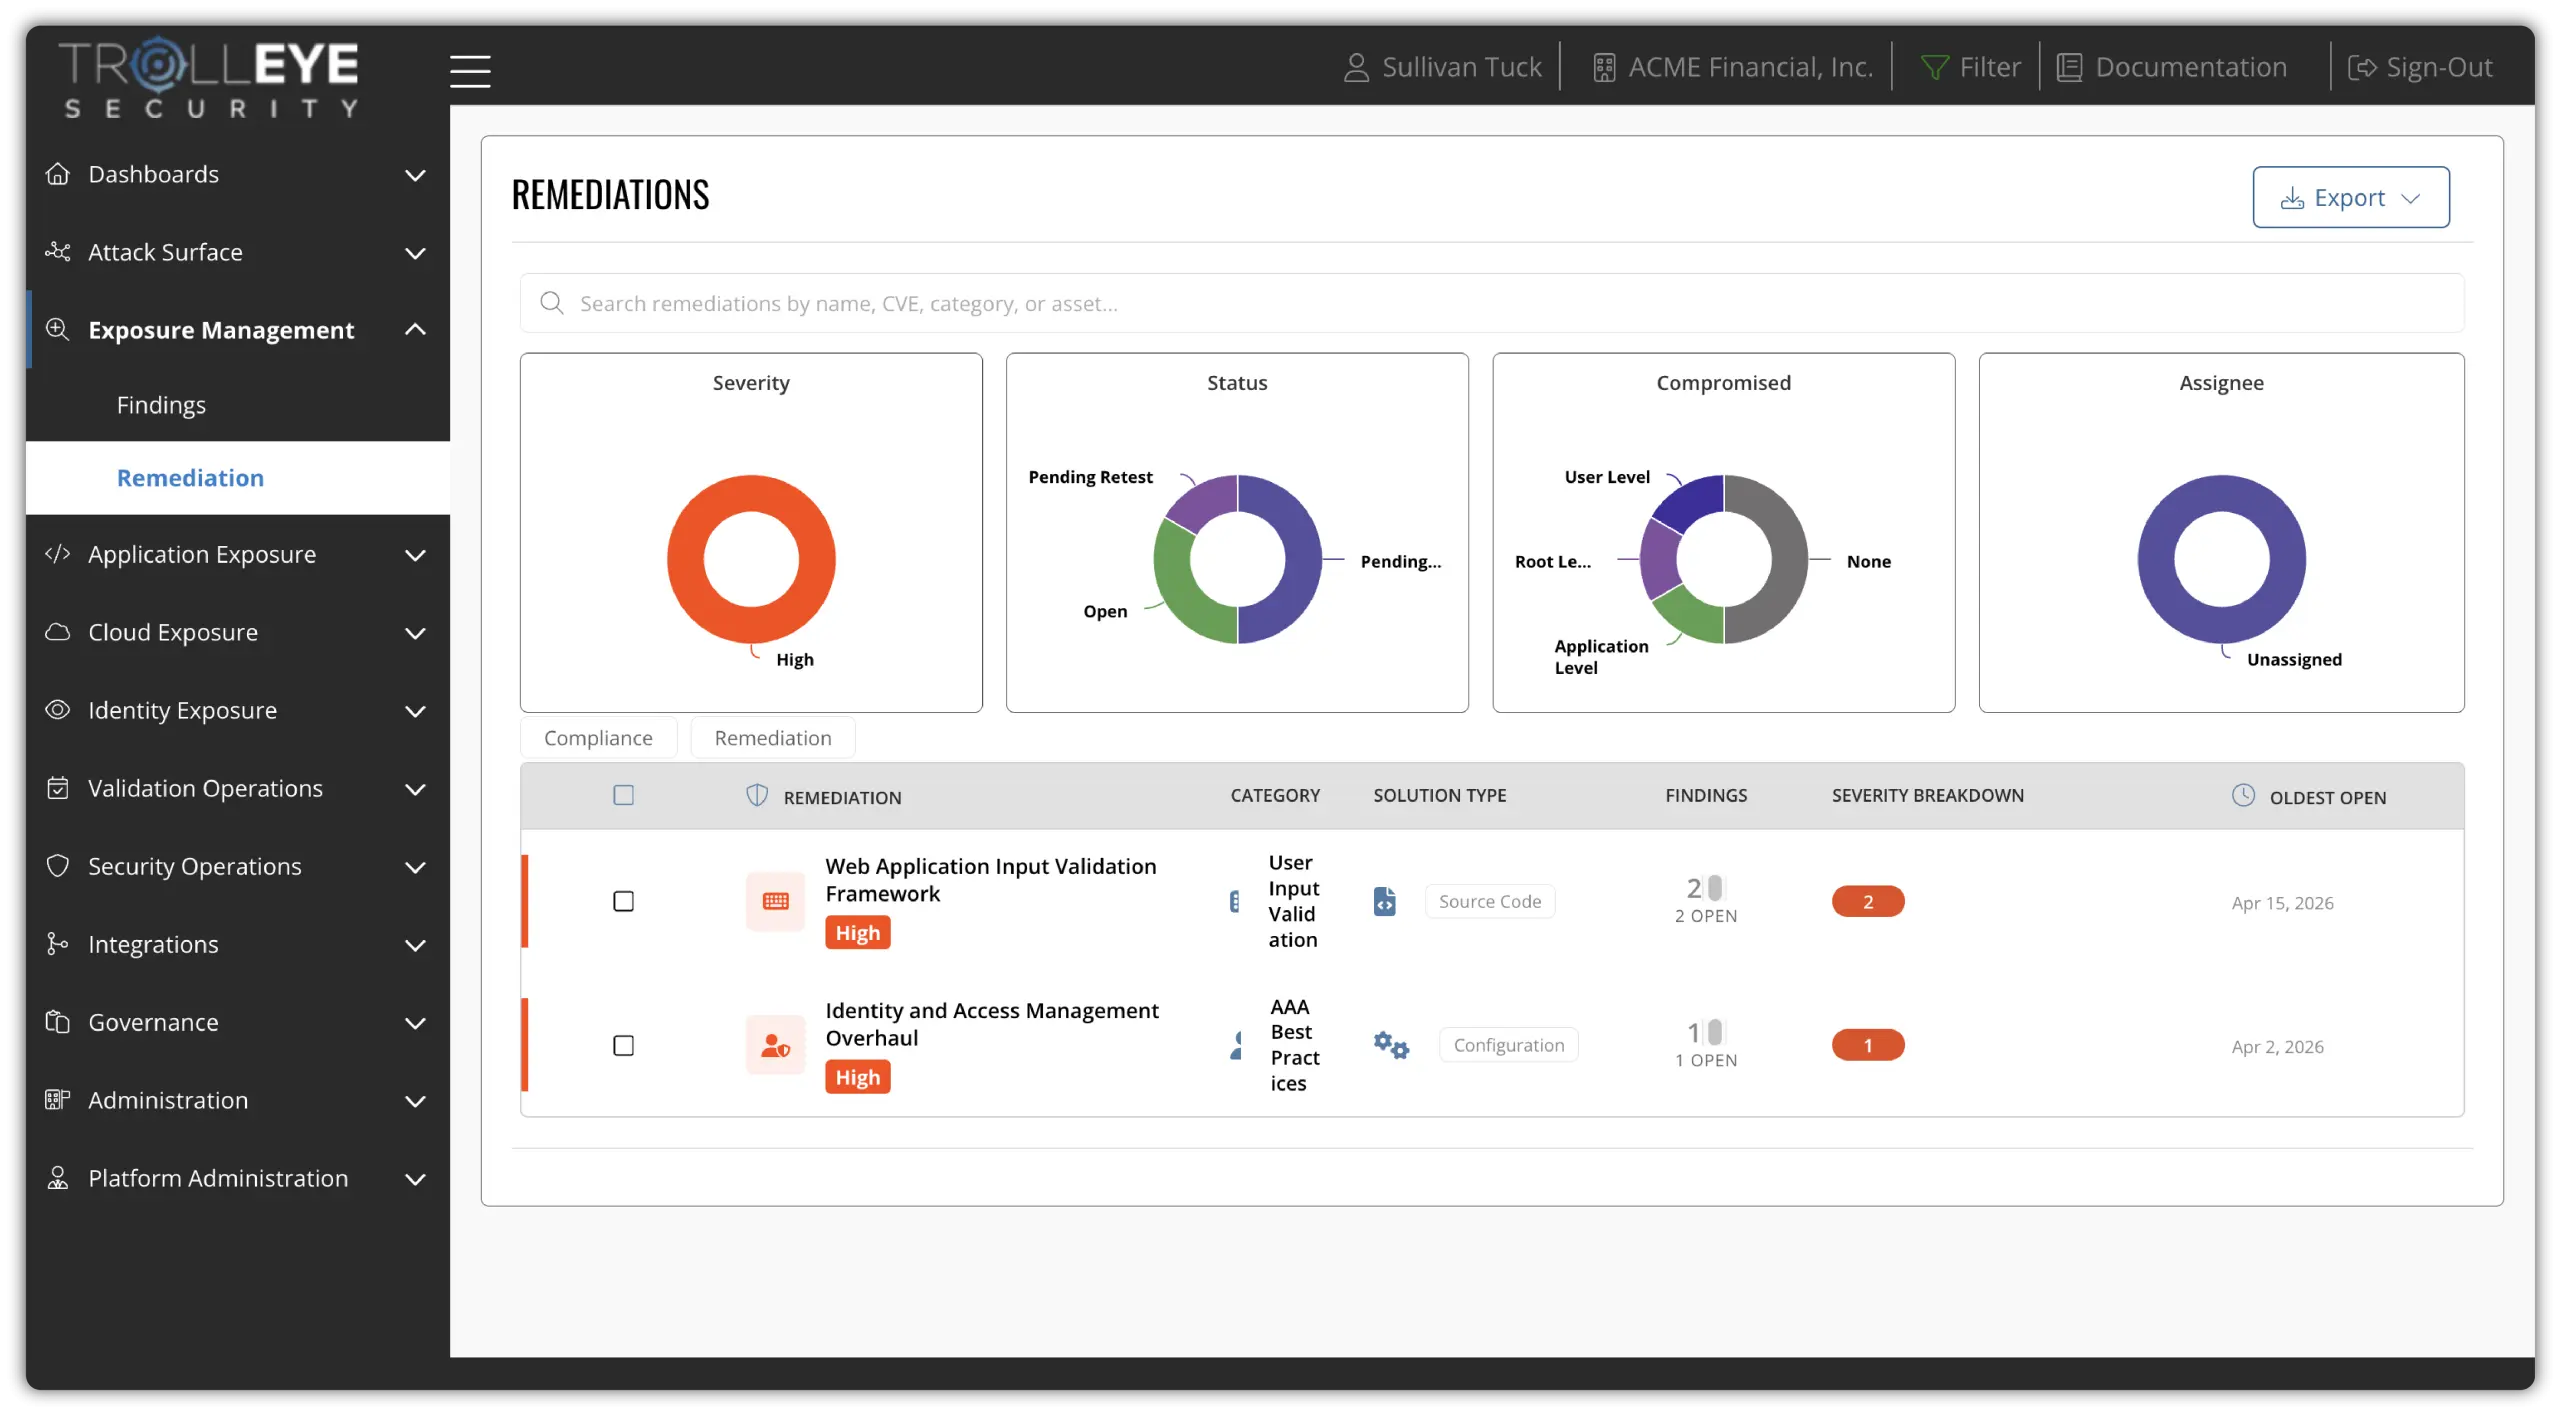
Insecure code patterns don’t stay isolated. They spread across microservices, shared libraries, and future releases. Our team works alongside yours to fix the patterns behind recurring findings, not just individual tickets.
Group related findings Tackle flaws that share an insecure pattern together instead of one ticket at a time.
Get expert remediation guidance Work with security engineers who help developers fix findings efficiently and correctly.
Fix underlying patterns Address the coding practices and shared components that keep reintroducing risk.
Keep Exploitable Flaws Out Of Live Environments.
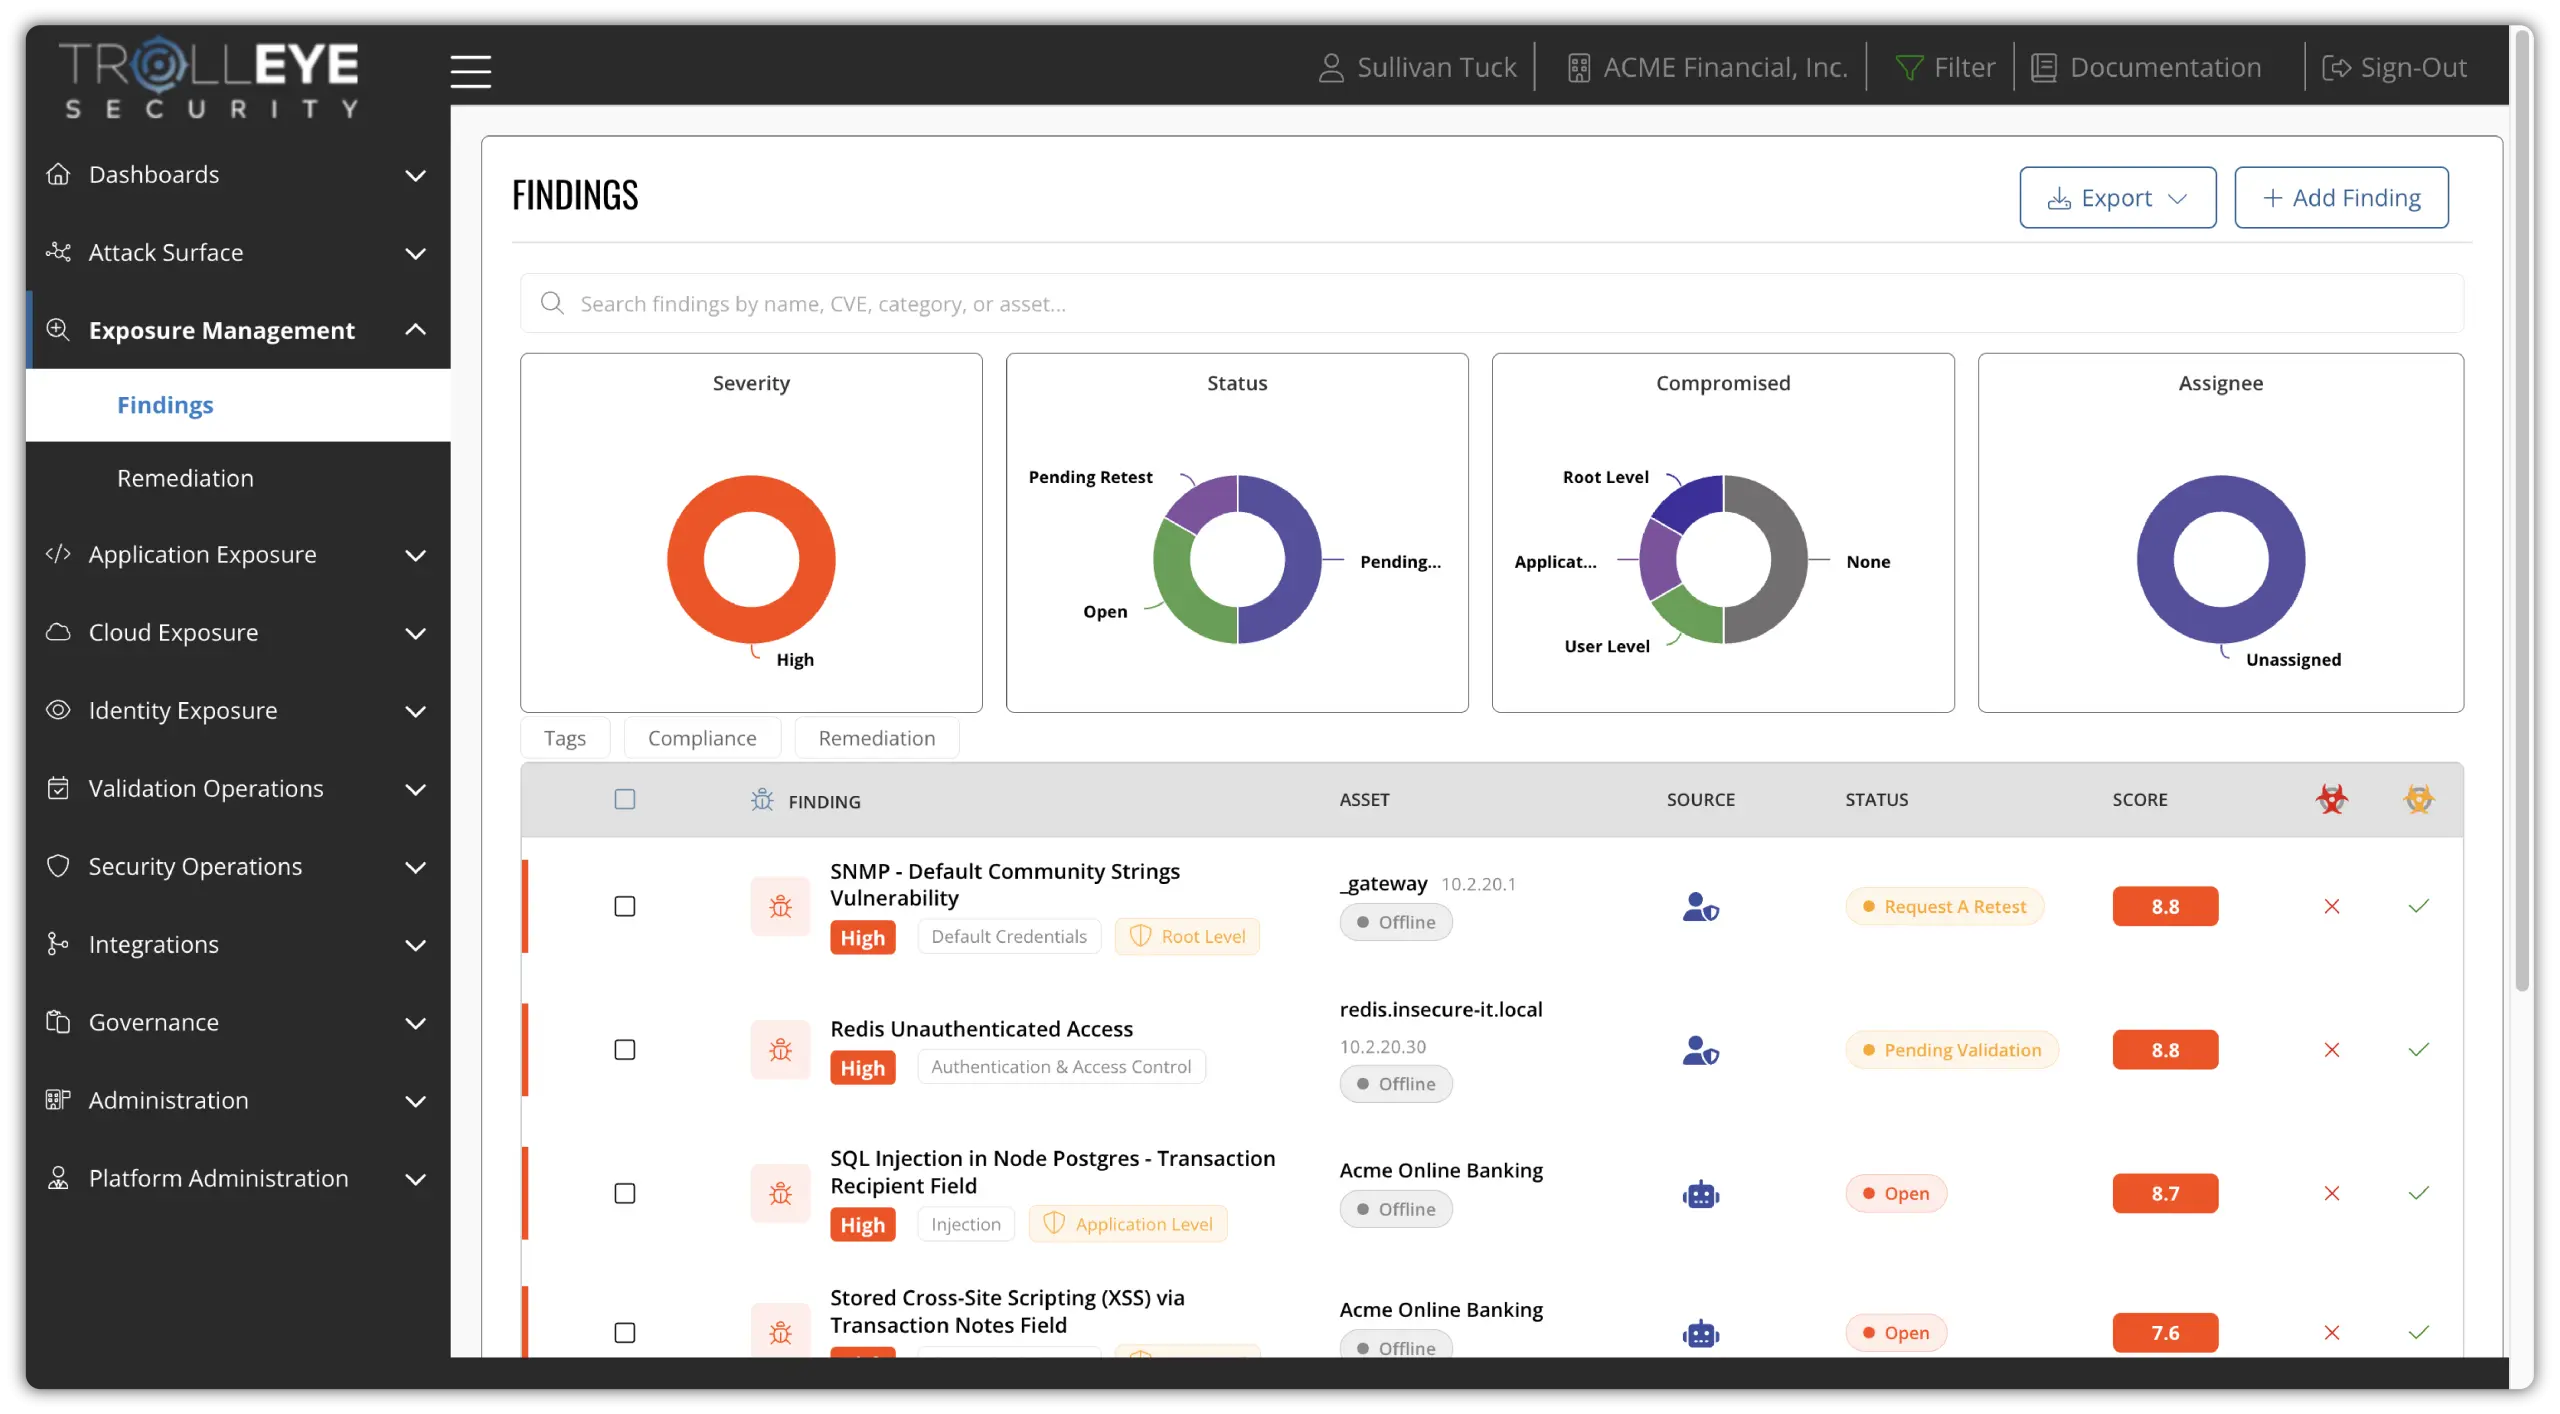
Rescans on remediated code and pipeline gates on new commits confirm that fixes hold and stop vulnerable code from merging or deploying without review, eliminating emergency patches.
Rescan remediated findings Confirm flaws are resolved instead of assuming a fix worked.
Gate vulnerable code Prevent new high-risk findings from merging or deploying without review.
Catch regression earlier Spot reintroduced flaws before they become recurring findings.
Ship On Schedule With Less Security Debt.
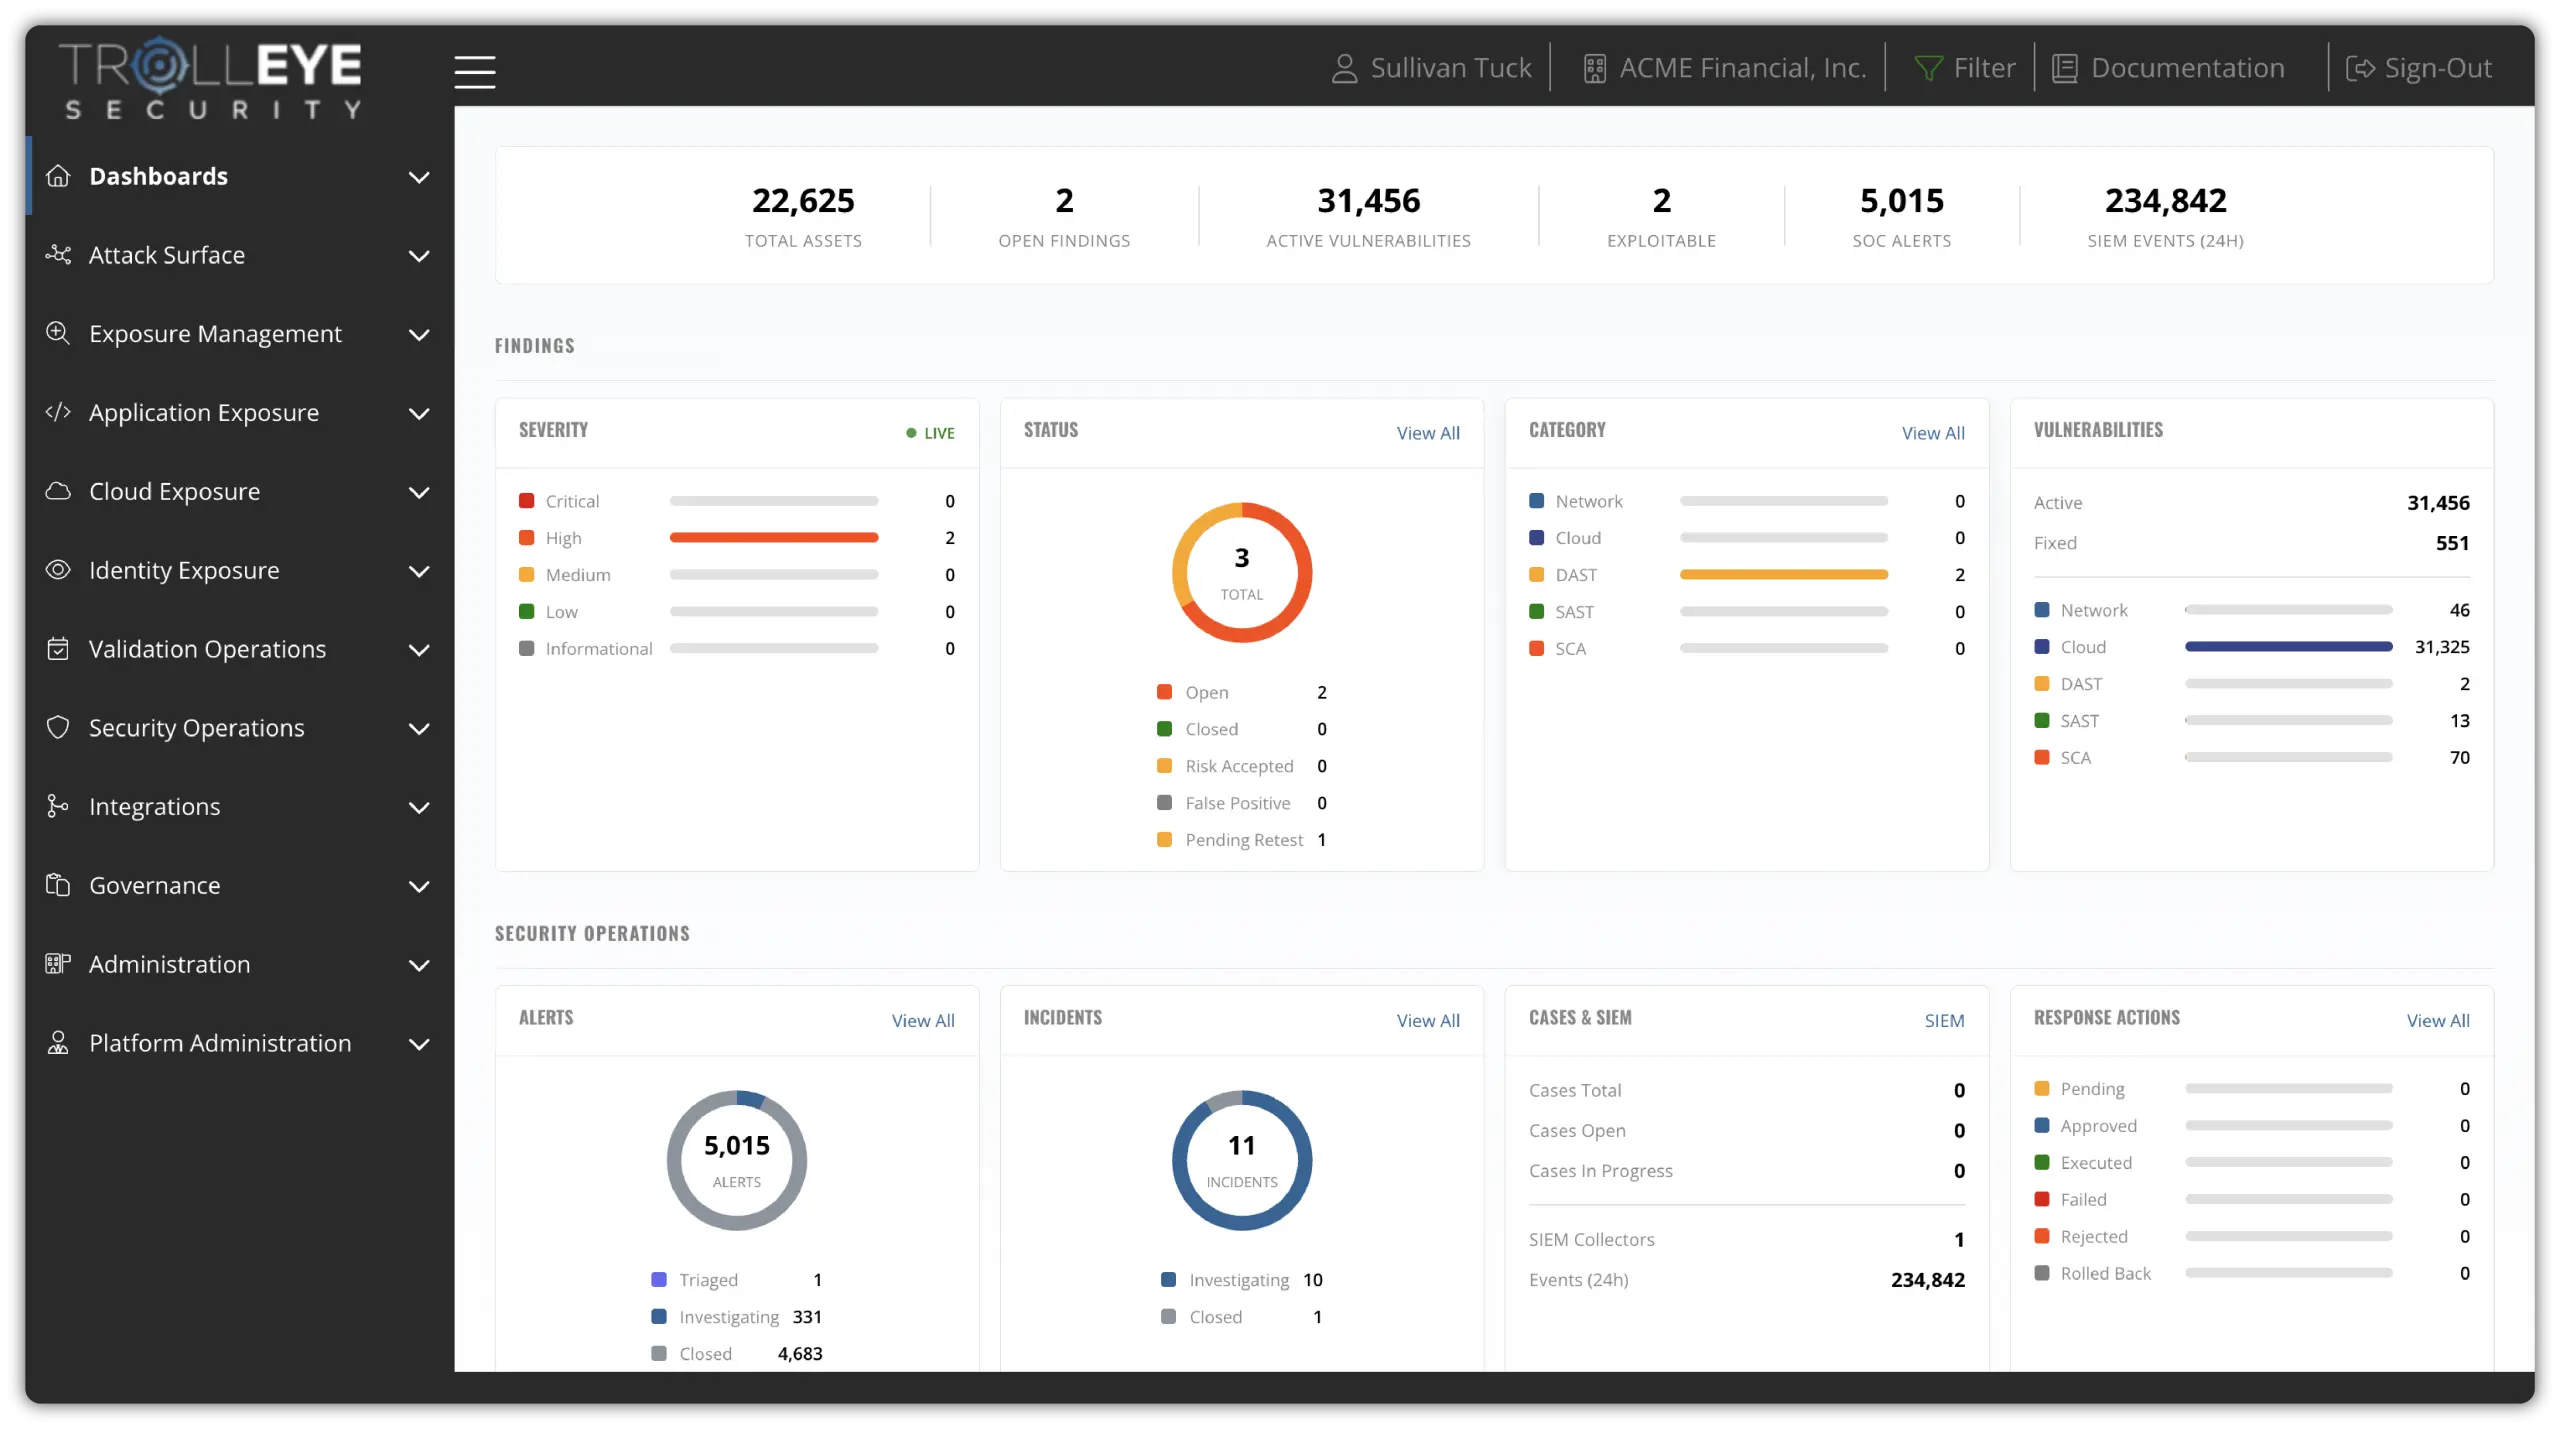
Findings that surface late in the release cycle stall deployments and create friction between security and engineering. SAST shifts them to the earliest stage possible, keeping releases predictable and security out of the critical path.
Work inside existing workflows Push findings into the repositories, ticketing, and collaboration tools developers already use.
Reduce security debt Stop vulnerabilities from accumulating across releases and into staging and production.
Pair automation with expertise Combine continuous scanning with expert triage so effort goes where it reduces the most risk.
Recognized by the Industry. Trusted by Engineering Teams.
Validated code-level findings and measurable improvement, not just another backlog, in a model recognized by Gartner and trusted by security and engineering teams.
How a Software Company Reduced Vulnerabilities by Over 97% with DevSecOps.
“We chose DevSecOps because the traditional annual testing model just wasn’t enough. With multiple fintech applications in production, we needed a way to embed security into our development lifecycle, something continuous, scalable, and built to catch issues before they ever made it to production.”
What differentiates TrollEye Security is their level of engagement. They operate as a true partner, embedding into our DevSecOps workflows and working directly with our engineering teams to improve processes and drive remediation. Their ‘white glove’ support model is something we didn’t have with previous vendors. They’re responsive, accessible, and willing to engage in real time when needed.
Every time we run one of these release tests, we find issues that otherwise would have gone into production. Maybe our internal scanners would have caught them, maybe they wouldn't, we don't know. That's what makes these additional checks so valuable.
Explore How SAST Turns Code Findings Into Secure Releases
Click through the TrollEye platform to see how static analysis findings become triaged, CWE-mapped issues, developer-aligned remediation, and confirmed fixes inside one continuous workflow.
Static Application Security Testing
Security Built Into Every Stage of the SDLC.
Our DevSecOps solution combines security expertise, continuous validation, a centralized platform, and remediation support to help organizations build and release secure software without building an internal AppSec team.
Build Security Into Design Decisions.
Security issues are significantly less expensive to address before development begins. During planning, we help teams identify risks, define security requirements, and establish secure architectural patterns before code is written.
Threat Modeling
Identifies potential attack paths, trust boundaries, and security weaknesses during application design.
Security Requirements Definition
Establishes security controls and requirements before development begins.
Risk Assessments
Evaluates business and technical risks associated with applications and infrastructure.
Secure Architecture Reviews
Analyzes application and infrastructure designs to identify insecure patterns early.
Prevent Vulnerabilities During Development.
Security validation is integrated directly into developer workflows to identify insecure code, exposed secrets, vulnerable dependencies, and infrastructure risks before they move further into the pipeline.
SAST
Scans source code for vulnerabilities and insecure coding practices during development.
SCA
Identifies vulnerable or outdated open-source dependencies within applications.
Secrets Detection
Detects exposed credentials, API keys, and sensitive information in repositories.
Secure Coding Standards
Verifies adherence to secure development standards and best practices.
SBOM Generation & Validation
Creates and validates software bills of materials for dependency transparency.
IaC Scanning
Scans infrastructure templates for security misconfigurations before deployment.
Validate Build Integrity Before Release.
As applications move through CI/CD pipelines, we continuously validate build artifacts, containers, and deployment processes to prevent insecure software from progressing toward production.
CI/CD Security Integration
Integrates automated security validation directly into development pipelines.
Container Image Scanning
Analyzes container images for vulnerabilities and insecure configurations.
Pipeline Security Validation
Secures CI/CD workflows against unauthorized modifications and injection attacks.
Artifact Signing & Verification
Confirms software artifacts and packages keep their integrity throughout the delivery pipeline.
Validate Real-World Attack Paths.
Automated testing alone cannot identify every security risk. During testing, we continuously validate applications through penetration testing, API security assessments, and business logic testing to uncover exploitable weaknesses before attackers do.
DAST
Tests running applications for exploitable vulnerabilities and insecure behavior.
API Security Testing
Validates APIs for authentication flaws, excessive exposure, and insecure endpoints.
Penetration Testing as a Service (PTaaS)
Agentic and human testing that continuously simulates real-world attacks against your applications.
Business Logic Testing
Identifies flaws in application workflows that traditional scanners often miss.
Security Regression Testing
Ensures security fixes do not introduce new vulnerabilities or regressions.
Ensure Applications Are Ready for Production.
Before release, security findings, compliance requirements, and accepted risks are reviewed so stakeholders understand remaining exposure and release decisions are properly documented.
Release Readiness Review
Verifies that applications meet security requirements before production release.
Compliance Validation
Aligns security processes with frameworks such as SOC 2, HIPAA, PCI DSS, and ISO 27001.
Risk Acceptance Review
Documents accepted risks and approved exceptions before release.
Security Gate Approval
Confirms security requirements have been met before production deployment.
Secure the Transition to Production.
As applications move into production environments, security controls, configurations, and runtime protections are verified so deployments remain secure outside of development and testing environments.
Code Signing Validation
Verifies deployed software originates from trusted and approved build processes.
Configuration Hardening Verification
Checks systems against security hardening benchmarks and best practices.
Attack Surface Verification
Reviews externally exposed assets, services, and applications before deployment to production.
Maintain Visibility Across Production Environments.
Security doesn’t end after deployment. We continuously monitor applications, infrastructure, and cloud environments to identify emerging vulnerabilities, attack surface changes, and operational security risks.
Attack Surface Management (ASM)
Continuously monitors and tracks externally exposed assets and attack surface changes.
Continuous Vulnerability Management
Maintains ongoing insight into vulnerabilities across applications and infrastructure.
Threat Intelligence Integration
Incorporates threat intelligence feeds to prioritize response based on active threats.
Patch Validation & Coordination
Coordinates and confirms security patches across the application and infrastructure stack.
Configuration Drift Detection
Monitors for unauthorized changes to security configurations in production.
Incident Response Support
Provides expert support for security incident investigation, containment, and recovery.
Cloud Security Posture Management (CSPM)
Continuously identifies cloud configuration weaknesses and security gaps in production.
Measure, Prioritize, and Reduce Risk Over Time.
Findings are tracked through remediation, retested after fixes, prioritized based on business impact, and reported to both technical teams and leadership to drive continuous security improvement.
Security Monitoring & Alerting
Provides continuous monitoring and alerting for security events and operational risks.
Risk-Based Prioritization
Ranks findings based on exploitability, exposure, and business impact.
Remediation Tracking
Tracks remediation progress and confirms issue resolution over time.
Retesting & Verification
Confirms vulnerabilities have been properly remediated after fixes are applied.
Workflow Automation
Automates security workflows to improve efficiency and reduce manual overhead.
Jira / Ticketing Integration
Routes validated findings directly into remediation workflows and ticketing systems.
Compliance Evidence Collection
Automatically collects and organizes evidence for compliance audits and reporting.
Executive Reporting
Delivers clear, business-aligned security metrics and reporting for leadership.
The Code-Level Discovery Engine Of Continuous Threat Exposure Management.
Static Application Security Testing (SAST) serves as a code-level discovery component of our Continuous Threat Exposure Management (CTEM) solution. By finding vulnerabilities in source code before it ships, SAST surfaces exposure at the earliest, least expensive point to fix it.
Most organizations don’t have a visibility problem. They have an execution problem. SAST connects code findings to every stage of CTEM, so flagged flaws turn into fixed root causes instead of another backlog.
Scoping
Define the repositories, applications, and pipelines static analysis needs to cover.
SAST defines code scope SAST CORE 02Discovery
Static analysis finds injection flaws, insecure patterns, and hardcoded secrets in source code.
SAST finds code flaws SAST STAGE 03Prioritization
Findings are triaged and ranked by severity, CWE mapping, and application context.
SAST adds code context 04Validation
DAST and penetration testing prove which code-level flaws are actually exploitable and reachable.
DAST + PTaaS prove risk SAST STAGE 05Mobilization
Findings route to the right developers, get tracked to closure, and are rescanned.
SAST drives the fix- Open-Source Risk (SCA)
- Runtime Testing (DAST)
- Penetration Testing
- Remediation Workflows
- Continuous Reporting
Where SAST Fits In A Complete AppSec Strategy.
No single testing method secures an application alone. SAST operates at the earliest stage, catching vulnerabilities in source code before any other method can.
The services below layer on top of static analysis to cover what it can’t reach, all delivered inside the same platform and the same remediation process.
Threat Modeling
Maps trust boundaries, data flows, and entry points before development begins, so static analysis rules focus on the risks that matter most for your codebase.
Software Composition Analysis
Covers what SAST can’t see in the code you import: known CVEs, outdated packages, and supply chain risk in third-party and open-source libraries.
Infrastructure as Code Security
Scans Terraform, CloudFormation, and Kubernetes manifests for misconfigurations, so the environment your code runs in is as secure as the code itself.
Pipeline Security
Turns SAST results into an enforced CI/CD gate, so vulnerable code can’t merge or deploy without review.
Dynamic Application Security Testing
Tests the running application to catch authentication, session, and business logic flaws that only surface at runtime.
DevSecOps as a Service
Brings SAST, SCA, DAST, IaC, and pipeline security together into one program that secures every stage of the SDLC.
Penetration Testing as a Service
Agentic and human testing shows how code-level flaws and other exposures can be chained into real attack paths.
Web Application Penetration Testing
Simulates real-world attacks against applications to validate business-impacting vulnerabilities in logic, authentication, and data handling.
Attack Surface Management
Continuously identifies internal, external, and on-prem assets, including the applications your code is deployed to.
SAST secures the code you write. These services cover the code you import, the infrastructure it runs on, how it behaves at runtime, and how attackers could chain it into real attack paths.
Learn More About SAST and DevSecOps
Use our latest resources, from white papers to case studies and articles, to learn how static analysis and DevSecOps give your security and engineering teams the information, tools, and guidance they need to integrate security into the entire SDLC.
Your Guide to DevSecOps
Learn how to integrate security into the entire SDLC through DevSecOps, so your organization produces more secure software, at a faster pace, cost-effectively.
How a Software Company Reduced Vulnerabilities by Over 97% with DevSecOps
See how embedding security into the development lifecycle took a fintech software company to zero critical and high findings.
Read the Case StudyTransform Your Security Posture With DevSecOps
See how integrating security into development changes the way teams build, test, and ship software.
Read the ArticleQuestions About Static Application Security Testing
How static analysis works, what it covers, how findings are triaged and fixed, and how SAST supports every stage of a Continuous Threat Exposure Management (CTEM) program.
01 What’s Static Application Security Testing (SAST)?
Static Application Security Testing (SAST) is a white-box testing method that analyzes an application’s source code for security vulnerabilities without executing it.
Because it works on code at rest, SAST can run early in the SDLC, often on every commit, catching flaws like SQL injection, insecure deserialization, and hardcoded secrets before code is compiled or shipped. It is a core part of our DevSecOps solution.
02 What’s the difference between SAST and DAST?
SAST analyzes code at rest from the inside, pinpointing the file and line where a flaw lives. Dynamic Application Security Testing (DAST) tests the running application from the outside to find authentication, session, and business logic issues that only surface at runtime.
The two methods are complementary, not redundant. Together, they cover both how your code is written and how your application behaves under attack.
03 How does SAST fit into Continuous Threat Exposure Management (CTEM)?
SAST is a code-level discovery component of our CTEM solution. It surfaces vulnerabilities in source code at the earliest point in the lifecycle, before they become exposure in production.
Within our CTEM packages, SAST findings are combined with software composition analysis, dynamic testing, penetration testing, remediation workflows, and continuous reporting, so code-level flaws are prioritized, validated, and fixed alongside the rest of your exposure.
04 How does SAST integrate with our CI/CD pipeline?
Our SAST service integrates directly into your repositories and CI/CD workflows, running scans on commits and pull requests so developers get feedback while they still have context.
Through pipeline security, scan results can act as a gate, so vulnerable code can’t merge or deploy without review.
05 What vulnerabilities does SAST detect?
SAST detects OWASP Top 10 and CWE-mapped weaknesses, including SQL injection and other injection flaws, broken access control, insecure direct object references, insecure deserialization, insecure data handling, and hardcoded secrets.
SAST analyzes the code you write. Known vulnerabilities in third-party and open-source dependencies are covered by software composition analysis (SCA).
06 How are SAST findings triaged and prioritized?
Findings are reviewed to reduce false positives and enriched with severity, CWE mapping, and application context, helping developers focus on the most critical risks first.
Through the platform, teams can track remediation progress, document accepted risks, monitor trends, and confirm fixes through rescans.
07 How is TrollEye’s SAST different from running a scanner?
A scanner produces findings. TrollEye focuses on getting them fixed and keeping them from coming back.
Through CI/CD integration, expert triage, developer-aligned remediation guidance, centralized exposure management, and rescanning, we help teams reduce security debt with every release and continuously improve how secure code gets written.
Walk through static analysis findings, triage, developer-aligned remediation, and rescanning in the platform before starting your evaluation.
Build Security Into Every Line of Code.
The foundation of secure software is secure code. TrollEye Security’s SAST service helps your teams catch vulnerabilities at the source, before they escalate into production incidents, compliance gaps, or emergency patches. See how SAST fits into a complete DevSecOps and CTEM program.
- 01Scans on every commit
- 02Triaged, CWE-mapped findings
- 03Developer-aligned remediation
- 04Rescans that confirm every fix