TrollEye Security

Network Penetration Testing

PART OF PTAASPenetration Testing as a Service→

Network Penetration Testing. Eliminate Real Attack Paths.

Our network penetration testing focuses on real-world exploitation and attack path analysis, showing which weaknesses across your internal and external infrastructure are truly exploitable, how they connect across systems, and what to fix first to eliminate lateral movement and privilege escalation risk.

It is one of the core tests inside our PTaaS solution, so every network finding flows into the same platform, the same remediation process, and the same CTEM program as the rest of your testing.

Attack Path Analysis Exploitability Validation Segmentation Testing Role-Based Remediation
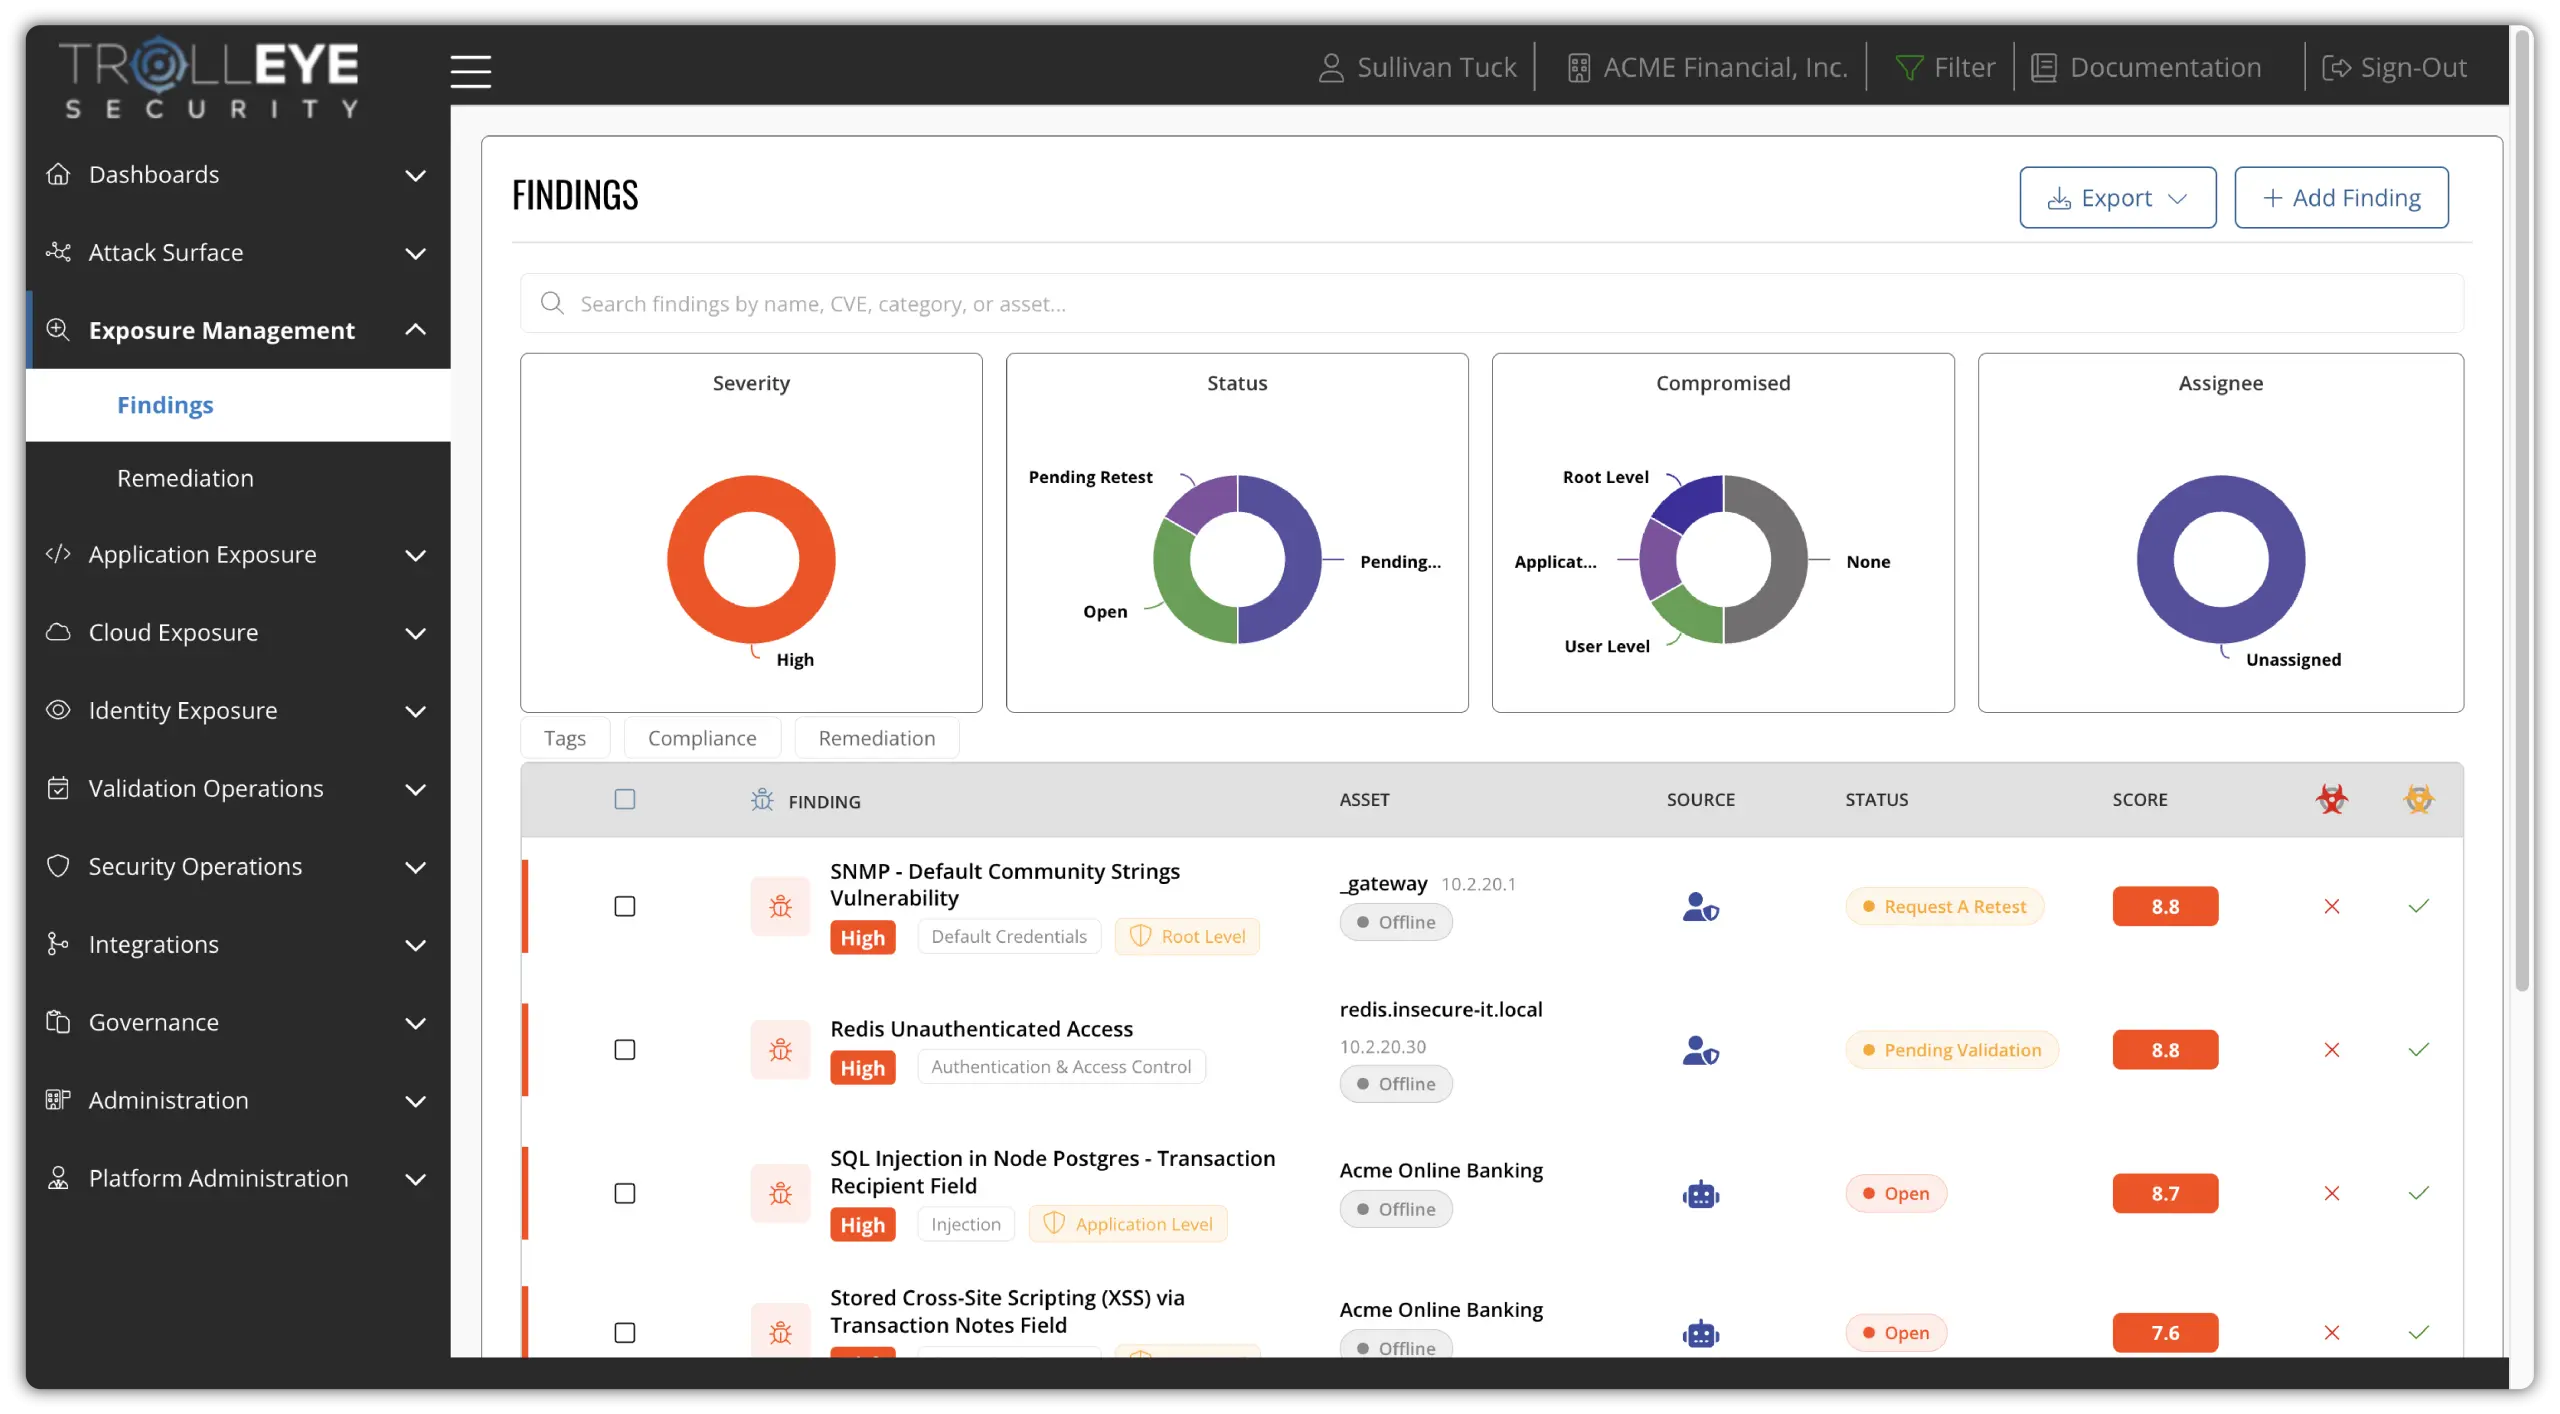
TrollEye platform showing network vulnerabilities across your infrastructure
NETWORK TESTINGAttack paths mapped across your infrastructure
PART OF PTAASSame platform, same remediation workflow
WHAT WE TEST

Every Layer Of Your Network.

We analyze internal and external network exposure to identify how attackers would realistically gain access and move laterally. Testing spans Active Directory, cloud networking, VPN access, exposed services, segmentation controls, and internal systems, combining automated discovery with hands-on reconnaissance to uncover what scanners alone miss.

Focused on internet-facing systems? See External Penetration Testing →
01

Network Infrastructure

Routers, switches, firewalls, and network services tested for weaknesses that enable access or pivoting.

02

VPN & Remote Access

VPN gateways and remote access paths tested for weaknesses that grant an attacker an initial foothold.

03

Active Directory & Identity

Directory services, credentials, and access controls tested for privilege escalation paths.

04

Cloud Networking

Cloud network configurations and connectivity tested for exposure across on-prem, cloud, and hybrid environments.

05

Segmentation Controls

Network boundaries tested to find where they fail to stop an attacker from reaching critical systems.

06

Exposed Services & Access

Risky services and weak access controls surfaced across internal and external infrastructure.

PROVEN IN PRACTICE

Recognized By The Industry. Trusted By Security Teams.

A network testing program should create measurable improvement, not just another report. TrollEye combines continuous testing, hands-on expertise, and remediation support in a model recognized by Gartner and trusted by security teams across multiple industries.

INDUSTRY RECOGNITION
01
GARTNER RESEARCH

Representative Provider in a Recent Gartner® Report

Named a Representative Provider in Gartner research covering Penetration Testing as a Service.

02
APPLICATION SECURITY

Sample Vendor in Gartner’s 2025 Hype Cycle

Recognized as a Sample Vendor for Penetration Testing as a Service in Gartner’s Hype Cycle for Application Security.

03
SECURITY OPERATIONS

Sample Vendor in Gartner’s 2025 Hype Cycle

Recognized as a Sample Vendor for Penetration Testing as a Service in Gartner’s Hype Cycle for Security Operations.

CUSTOMER OUTCOMES
“

Our clients have reduced critical and high findings to almost zero within six months.

The goal is not simply to find more vulnerabilities. It is to build a repeatable testing and remediation process that continuously drives meaningful exposure down.

Ricoh Danielson
Ricoh Danielson
★★★★★
Enterprise CISO at CorroHealth
My speed to respond and my speed to remediate have gone down dramatically. My scalability, flexibility, and agility across the environment are much faster than with the big-box vendors.
Watch Ricoh's Testimonial →
Dane Clemons
Dane Clemons
★★★★★
Director of Information Technology at Talquin Electric
I consider TrollEye to be a true hidden gem in the realm of security solutions and an invaluable technology partner. Talquin has been utilizing TrollEye's services for over four years now, and our experience has been nothing short of exceptional. TrollEye's unwavering dedication to security has ultimately bolstered Talquin's overall security posture.
Mario Andino
Mario Andino
★★★★★
Former Security Analyst at SMC3
I am pleased with all the services we are receiving from the team at TrollEye Security. Being able to actively view findings from their platform gives our information security team the insight we need to ensure our security posture across the organization.
Cyrus Yazdanpanah
Cyrus Yazdanpanah
★★★★★
Director of Information Technology at FSLSO
PTaaS has been a wonderful addition to our Development Lifecycle. TrollEye's platform provides a unique experience and excellent value!
INHERITED FROM PTAAS

Everything In PTaaS, Applied To Your Network.

Network penetration testing isn't a standalone engagement. It runs inside our PTaaS solution, alongside internal, external, IoT, and phishing testing, with the same platform, the same remediation workflow, and the same agentic and human testing model.

01

Attack Chain Prioritization

Findings are prioritized by their role within an attack chain, not severity scores alone, so remediation breaks the paths attackers would actually use.

02

Owner-Routed Remediation

Validated findings arrive with reproduction steps, business impact, and clear guidance, routed to the infrastructure, identity, or security team that owns the fix.

03

Managed, Continuous Testing

Our team manages execution, validation, guidance, and retesting, so you run a continuous network testing program without building specialized internal capabilities.

ATTACK PATHS WE VALIDATE

From Initial Access To Critical Systems.

Every finding is validated to demonstrate actual impact. Rather than theoretical severity scores, we show how vulnerabilities interact across Active Directory, cloud networking, VPN access, and internal systems, and how attackers chain them together.

INSIDE THE PLATFORM

How Network Testing Works Inside TrollEye.

Network findings don't arrive as a PDF. They land in the same TrollEye platform as every other PTaaS test, where your team can see what was found, what is exploitable, who owns the fix, and when it has been retested.

Network Assets

Every host, service, and network segment discovered during testing is tracked in one inventory, so coverage keeps pace as your infrastructure changes.

  • Hosts, services, and segments in one view
  • Internal and external exposure side by side
  • Coverage that adapts as infrastructure changes
TrollEye platform network assets view

Validated Findings

Each network finding arrives with exploit evidence, reproduction steps, and attack path context, so teams see how weaknesses chain together instead of scanner severity alone.

  • Exploitability confirmed by our testers
  • Ranked by role in the attack chain
  • Evidence attached to every finding
TrollEye platform validated findings view

Remediation

Findings route to the infrastructure, identity, or security owner responsible for the fix, with clear guidance on segmentation, service hardening, and access control changes.

  • Role-based task distribution
  • Step-by-step remediation guidance
  • No validated attack path lost in a backlog
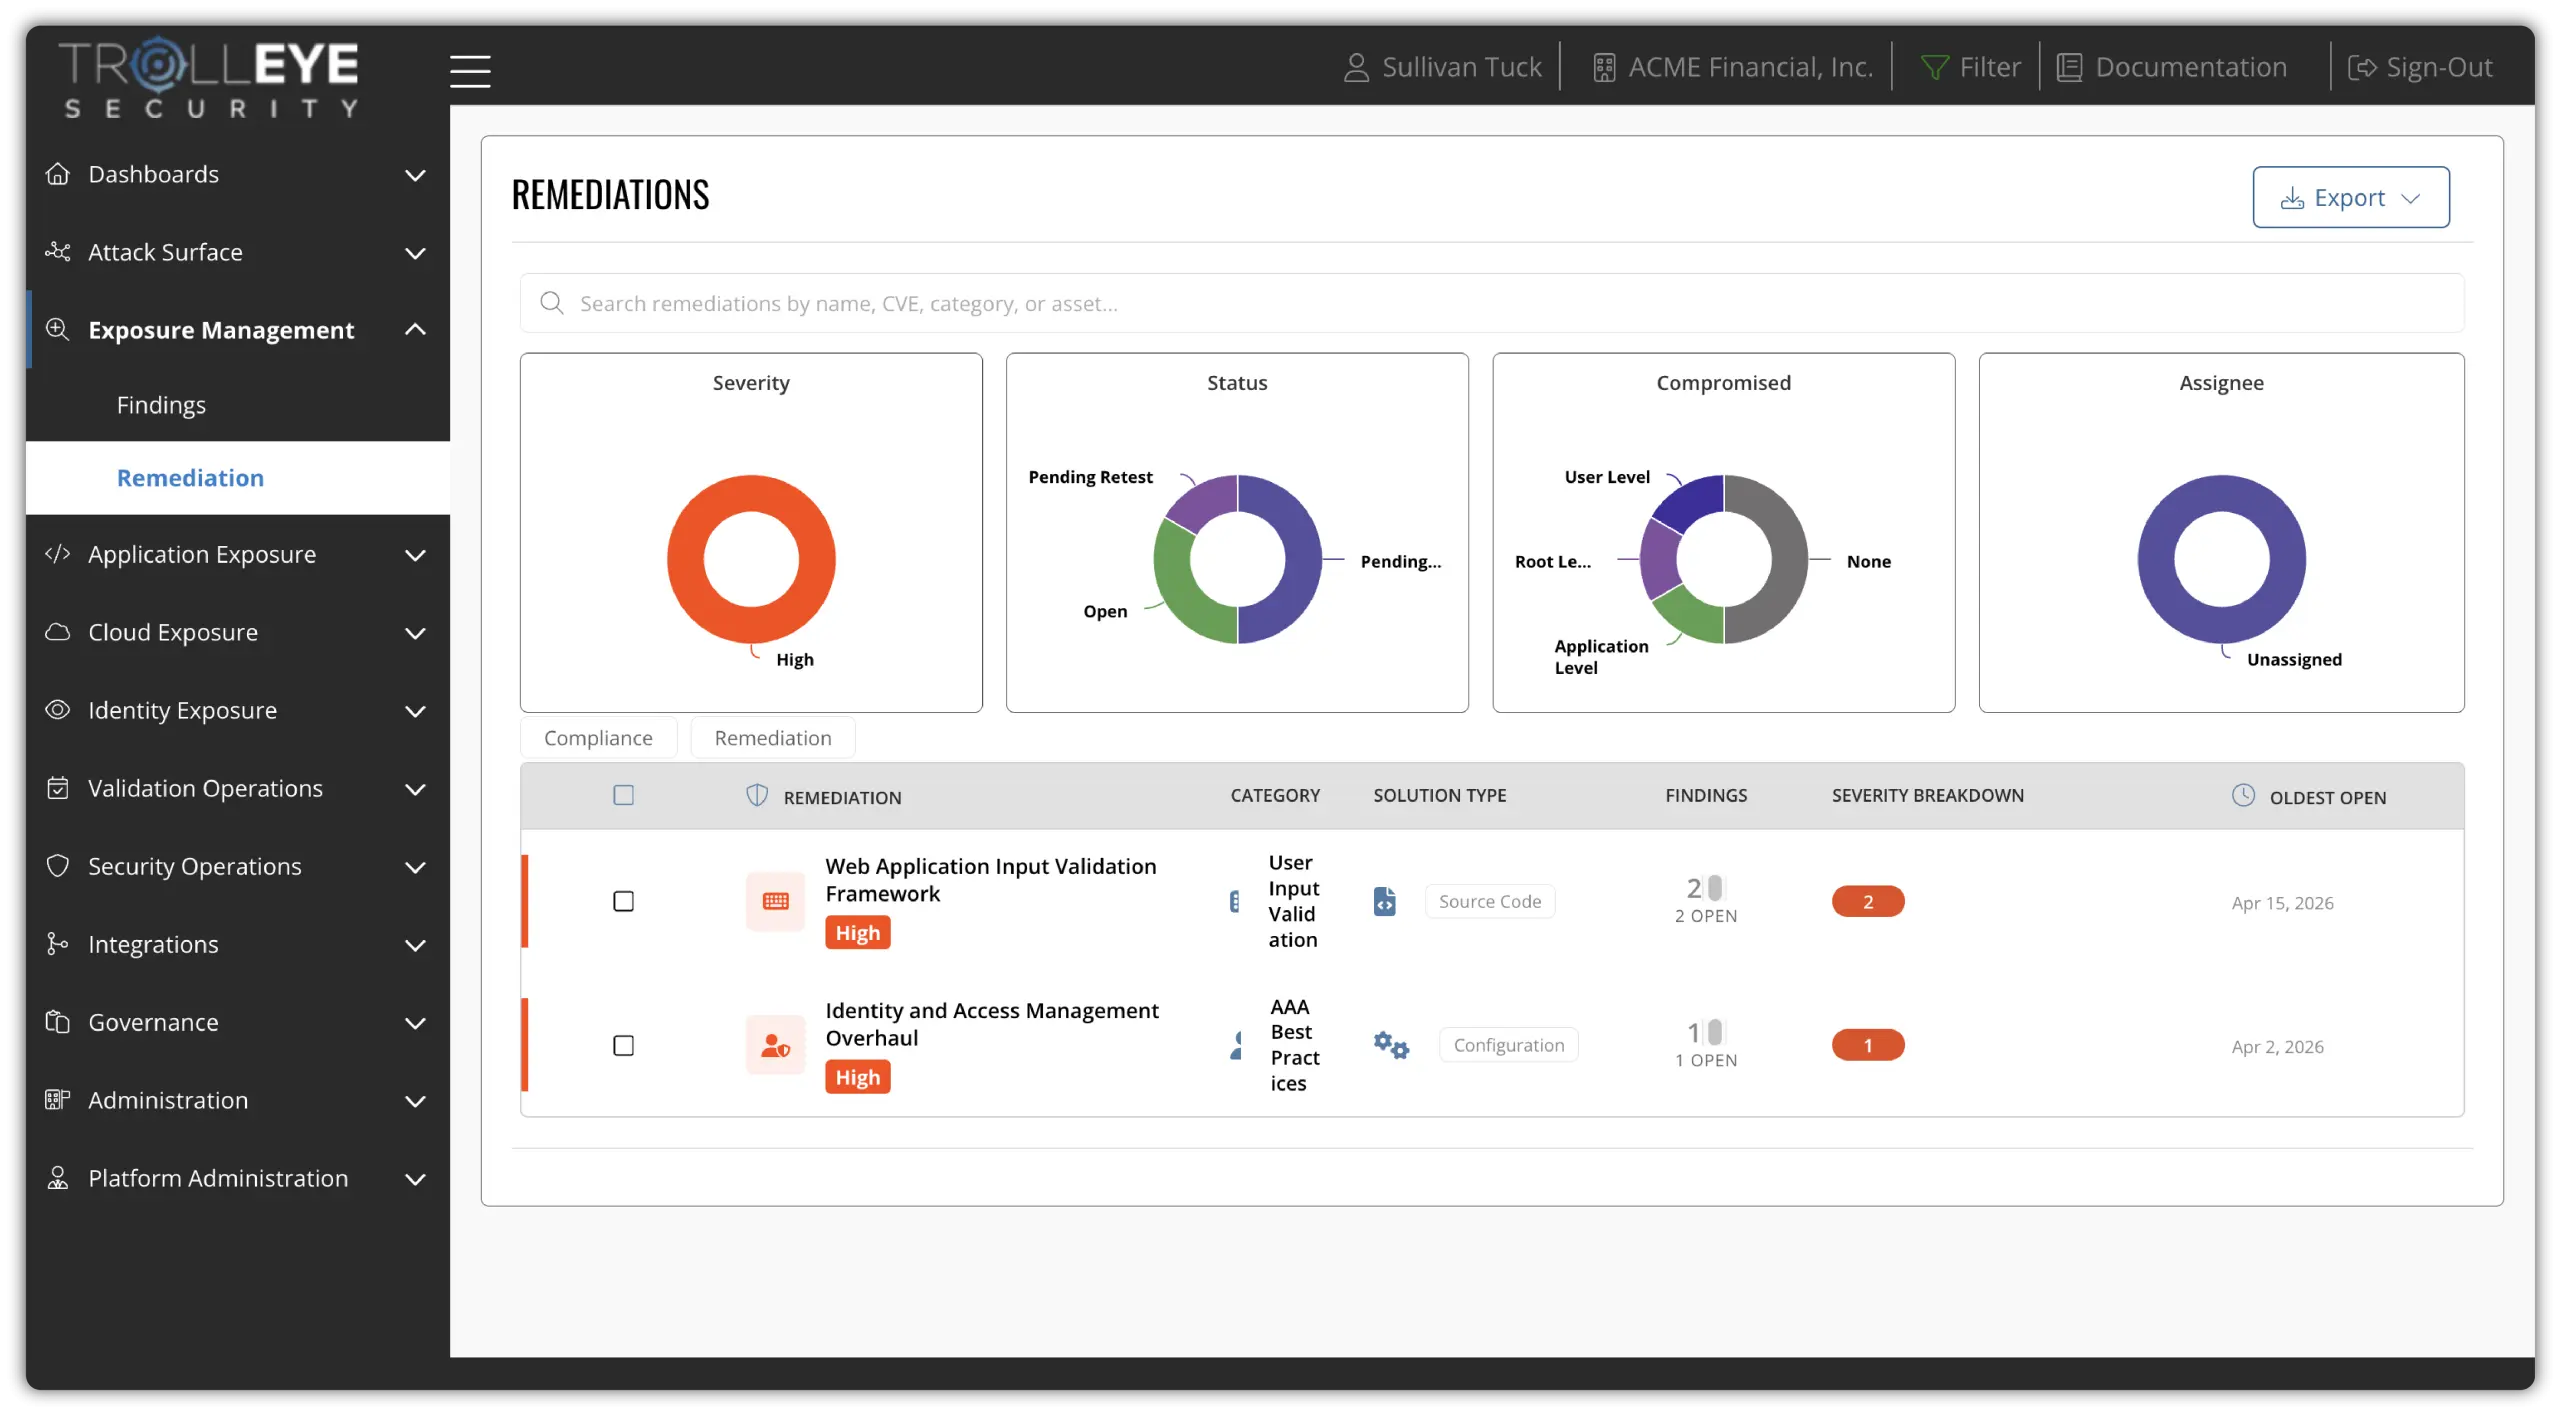
TrollEye platform remediation view

Retesting

Once a fix is in, request a retest directly from the platform and our team confirms the attack path can no longer be leveraged.

  • Retests requested in one click
  • Status updated on every finding
  • Closure confirmed by the same team that found it
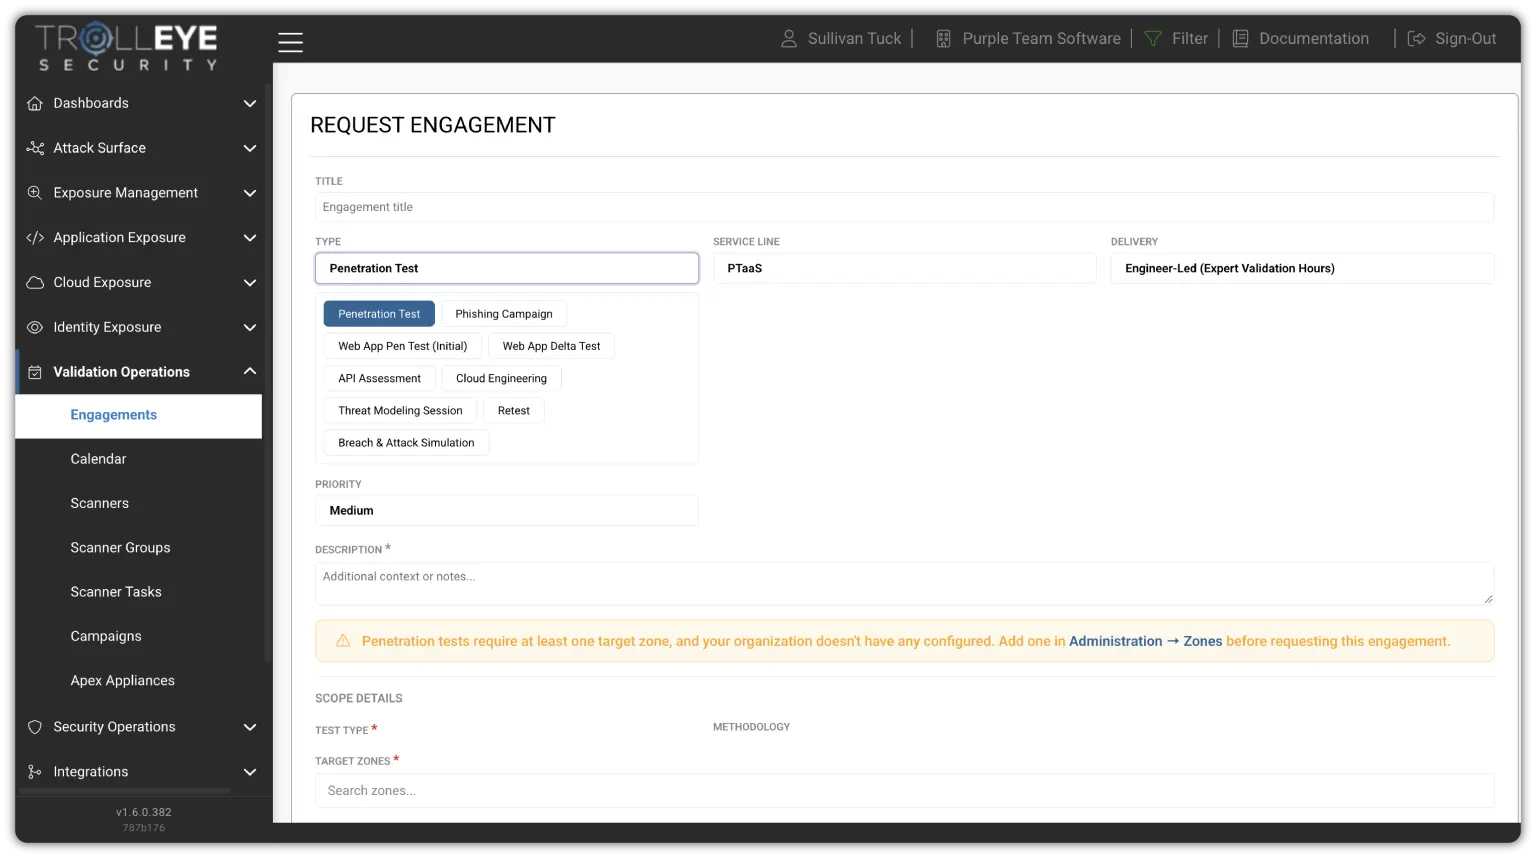
TrollEye platform retesting view

Reporting

Executive and technical reporting shows how your network exposure and repeat findings trend over time, alongside every other test in your PTaaS program.

  • Executive-ready summaries
  • Technical detail for engineering teams
  • Network results in the context of all PTaaS testing
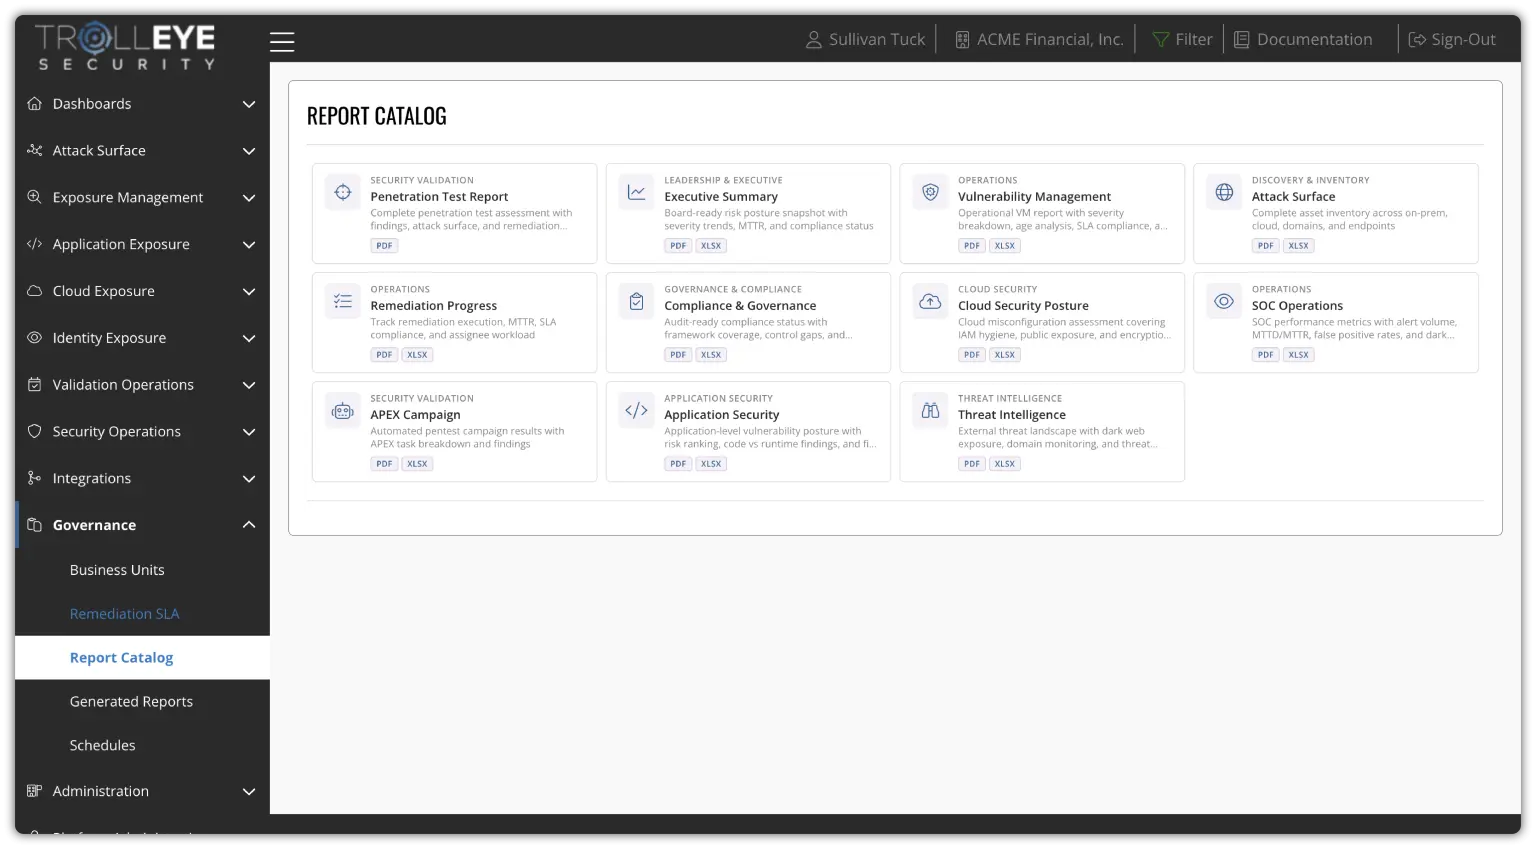
TrollEye platform reporting view
NETWORK TESTING WITHIN CTEM

Where Network Testing Fits In Continuous Threat Exposure Management.

Network Penetration Testing is delivered through Penetration Testing as a Service (PTaaS), the core validation component of our Continuous Threat Exposure Management (CTEM) solution. By identifying and validating exploitable attack paths across your infrastructure, it shows which network exposures present real risk and where remediation effort should be focused.

Most organizations don’t have a visibility problem. They have an execution problem. Network testing connects to every stage after scoping, so validated attack paths turn into fixed root causes instead of another report.

WITHIN OUR CTEM PACKAGES, NETWORK FINDINGS COMBINE WITH
  • Attack Surface Visibility
  • Cloud Security
  • Identity Exposure
  • Remediation Workflows
  • Continuous Reporting
NETWORK TESTING FAQ

Questions About Network Penetration Testing

How network penetration testing works, what it covers, how findings are validated and prioritized, and how it supports every stage of a Continuous Threat Exposure Management (CTEM) program.

01 · SCOPE02 · DISCOVER03 · PRIORITIZE04 · VALIDATE05 · MOBILIZE
01
SCOPEDefine Test Scope
02
DISCOVERMap Real Exposure
03
PRIORITIZERank by Real Risk
04
VALIDATEProve Exploitability
05
MOBILIZEFix and Retest
01 What is network penetration testing?

Network penetration testing simulates how a real attacker would gain access to and move through your infrastructure. Agentic and human testing identifies exploitable weaknesses across network devices, services, segmentation controls, and access paths, then shows how they connect and what to fix first.

02 How is it different from a vulnerability scan?

Scanners flag potential vulnerabilities and rate them by severity. Network testing uses hands-on reconnaissance and attack path analysis to confirm what an attacker can actually exploit, including pivoting, privilege escalation, and segmentation bypass.

03 What does network testing cover?

Internal and external network exposure, including Active Directory, cloud networking, VPN access, exposed services, segmentation controls, and internal systems. Scope is set by your CTEM package and runs alongside the rest of your PTaaS testing.

04 How are network findings prioritized?

Findings are prioritized by their role within an attack chain, not severity alone. Fixes that eliminate pivot points and restrict lateral access come first, so remediation effort reduces measurable risk.

05 How does network testing fit into CTEM?

Delivered through PTaaS, network testing is a core validation component of our CTEM solution. Validated attack paths then move into mobilization, where findings are routed to owners, tracked to closure, and retested to confirm the path is closed.

06 How often is network testing performed?

Automated testing runs continuously. Deeper expert testing is driven by the service credits included in every CTEM package, so you decide how often network testing happens and where it is focused.

PART OF PTAAS Network testing is one part of our PTaaS solution.

See how network, internal, external, and IoT testing run together in one platform and one remediation process.

GET STARTED

Secure Your Network. Start Eliminating Attack Paths Today.

Cyber attacks happen every moment, from internal and external sources, but only those who are prepared will withstand the assault. Don’t let hackers test your security first. See how agentic and human network testing fits into a complete CTEM program.

  • 01Real-world network exploitation
  • 02Attack path-focused validation
  • 03Role-based remediation workflows
  • 04Retesting that confirms every fix

Conversations with CISOs

Live CISO Roundtable & AMA

Doing More with Less

Four security leaders. One candid conversation about budgets, teams, security tools, and the tradeoffs CISOs face heading into 2027.

October 29, 2026 • 2:00 PM ET • Live Online

Join the Conversation With

Jeff Moore Jeff Moore CISO, H&M
Elizabeth Di Bene Elizabeth Di Bene CISO, Loudon County
JoJo D JoJo D Cyber Leader, Co-Founder of Chaos & Signal
Aby Rao Aby Rao Deputy CISO, Fintech
Register & Submit Your Questions →

This Content Is Gated