The Enterprise CTEM Buyer's Guide
How large security organizations should evaluate Continuous Threat Exposure Management when the hard part isn't finding exposures. It's getting the right ones fixed across dozens of teams, tools, and business units.
Enterprises Don't Have a Visibility Problem. They Have an Execution Problem.
Most large enterprises already run vulnerability scanners, attack surface management, cloud security posture tools, application security testing, and recurring penetration tests. Together, they produce a backlog no team can clear, owned by no one in particular, and reported in counts that say little about whether risk is going down.
Continuous Threat Exposure Management (CTEM) closes that gap by turning security work into a continuous cycle: decide what matters, find the exposures that affect it, prioritize by real-world risk, prove what is exploitable, and mobilize the people who can fix it. For enterprises, most of the value sits in the last three stages, where traditional programs break at scale.
What Enterprise Buyers Should Require at Each CTEM Stage
The five CTEM stages are the same for every organization. What changes at enterprise scale is the bar each stage has to clear. Use these requirements and red flags to structure demos and proofs of concept.
Scope defined by business service, business unit, and owner, with criticality that carries into every later stage. New acquisitions and business units should be added without rebuilding the program.
Scope is a list of IP ranges and domains with no connection to the services or owners behind them.
Continuous coverage across the attack surface, including network, applications, cloud, and identity, with duplicate assets reconciled into one record and coverage gaps reported openly.
The vendor can't show what it doesn't see, or how current its asset and exposure data is.
Explainable rankings that combine exploitability, reachability, threat intelligence, attack paths, business criticality, and compensating controls, applied consistently across business units.
A proprietary risk score that no one on your team can explain to an application owner.
Proof of which prioritized exposures are exploitable and reachable, combining continuous agentic testing with human testers for complex attack paths and business-logic flaws, with evidence the fixing team can see.
Exploitability inferred from a feed or a score, rather than demonstrated through testing.
Findings routed to accountable owners in the workflows they already use, governed by remediation SLAs that reflect your risk policy, with retesting before anything is considered done.
Remediation tracked only as ticket status, with no retest and no root-cause view of why the same exposures return.
Native, Aggregation, or Both? Making the Architecture Call
Every CTEM platform consolidates some tools and aggregates others. The real question is how far a platform leans in each direction, and what that means for your stack, your budget, and your team's workload.
Enterprises often default to aggregation because they have already invested heavily in specialist tools. That can be the right call when those tools are deeply embedded and performing well. But an aggregation layer inherits every gap in the tools beneath it: data freshness, coverage blind spots, inconsistent severity models, connector maintenance, and the licensing cost of each product.
A platform that leans native delivers more of the lifecycle itself, including discovery, validation, and remediation management, so overlapping tools can be retired and teams work in one environment. It should still integrate the specialist tools you choose to keep. Neither approach is automatically better. The right answer depends on what you own, what is up for renewal, and how much integration work your team can absorb.
Usually the better fit when…
More of the lifecycle runs in one platform, with integrations where they add value.
- Several overlapping tools are up for renewal
- Validation and penetration testing are separate contracts today
- Business units run different tools for the same job
- You want fewer connectors to build and maintain
- You need consistent evidence from discovery through retest
- Your in-house red team needs its testing tracked, evidenced, and retested alongside everything else
Usually the better fit when…
The platform correlates and coordinates output from the tools you keep.
- Specialist tools are deeply embedded and well tuned
- Procurement cycles make consolidation slow
- You mainly need correlation and reporting across existing data
- Your team has capacity to maintain connectors
- Each business unit owns and funds its own security stack
Ask every vendor the same three questions: Which capabilities are native? Which require another license or service? What happens to the program if a connected tool or integration fails?
Enterprise CTEM Evaluation Criteria and the Questions That Test Them
Weight these criteria to your priorities, but don't drop any of them. Enterprise CTEM programs rarely fail on discovery. They fail on governance, ownership, and mobilization. The eight criteria fall into four groups. Select one to see why it matters, what strong evidence looks like, and what to ask the vendor.
01Prioritization transparency
Prioritization transparency
Hundreds of owners have to trust the ranking before they will act on it.
Any finding's priority can be explained in plain terms: why it matters, why now, and what evidence supports it.
- Pick any top-ranked finding. Can you explain, in plain terms, why it outranks the rest?
02Validation depth and scale
Validation depth and scale
Exploitability proof has to keep pace with continuous change, not an annual calendar.
Exploitability demonstrated through testing, automated, human, or both, at a cadence that matches how fast the environment changes, with evidence attached to the finding.
- Show us how a finding moves from detection to proven exploitability. What evidence is attached?
- How do you keep testing safe for production systems?
03Remediation governance
Remediation governance
Policy, not individual judgment, should set deadlines across the organization.
Remediation SLAs defined by your own risk policy and applied consistently across business units, with retesting before closure.
- How are remediation SLAs defined, and can they differ by exposure type or internet exposure?
- Is every fix retested before it is marked resolved?
04Workflow integration
Workflow integration
Engineering and IT teams won't adopt another console.
Reliable two-way sync with the ticketing and collaboration tools teams already use, without losing context.
- How are owners assigned, and what happens when ownership is unclear?
05Business-unit and ownership model
Business-unit and ownership model
Accountability has to survive org-chart complexity, acquisitions, and shared infrastructure.
Assets, exposures, and SLAs scoped by business unit, with role-based views for security, IT, engineering, and leadership.
- How do you model business units, subsidiaries, and acquisitions? Can each have its own scope, owners, and SLAs?
- How do role-based views work for security, IT, engineering, and leadership?
- What is the largest comparable environment you support today, in assets, users, and cloud accounts?
06Leadership reporting
Leadership reporting
Boards and executives ask whether risk is going down and what it would cost the business if it didn't, not how many scans ran. Financial risk is the language leadership funds and prioritizes against.
Exposure trends against a fixed baseline, by business unit and critical service, with SLA adherence and exposure translated into estimated financial risk, such as potential loss, downtime cost, and regulatory impact.
- How do you translate exposure into financial risk that leadership can act on?
07Consolidation and total cost
Consolidation and total cost
Platform fees are only part of the cost of running an exposure program.
A multi-year view of total cost, including licenses, connectors and integration upkeep, services, and the tools or contracts the platform would replace or depend on.
- Which capabilities are native, and which depend on another product?
- Which of our current tools and contracts could this realistically replace, and which would it still depend on?
- What will year two cost once onboarding is complete?
08Expert capacity
Expert capacity
Even large teams sometimes need specialist skills or surge capacity.
A clear model for adding specialist testing or analysis when needed, whether from the vendor, a partner, or your own team, with results captured in the same record.
- Which testing is automated, which is performed by people, and how is each scoped and requested?
Where TrollEye Fits in the Enterprise
TrollEye is a native CTEM platform backed by expert security services. For enterprises, that combination targets the part of CTEM that tends to break at scale: turning validated exposures into verified fixes across many teams.
One platform across the lifecycle
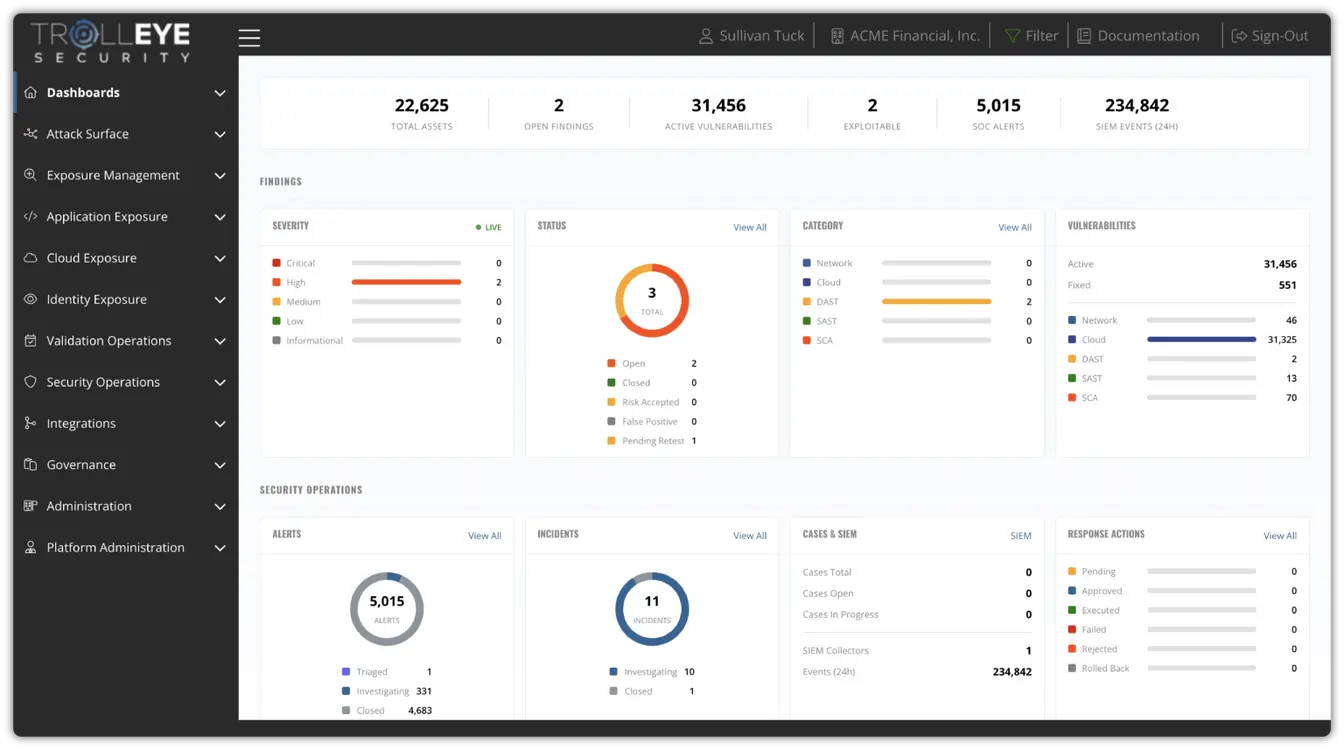
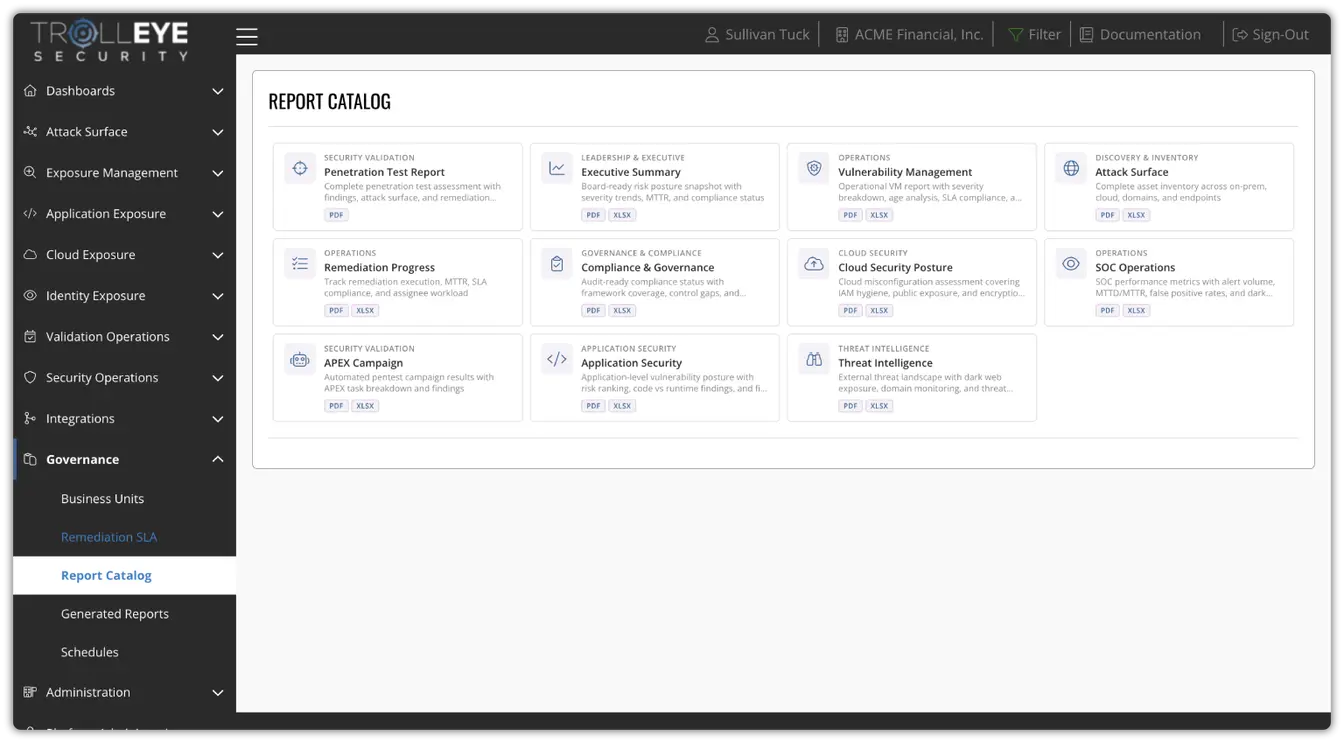
Scoping, discovery, prioritization, validation, and mobilization run in one environment, consolidating capabilities such as SAST, DAST, SCA, BAS, penetration testing, dark web monitoring, vulnerability management, and managed SIEM, while integrating the specialist tools you keep.
Validation that keeps pace
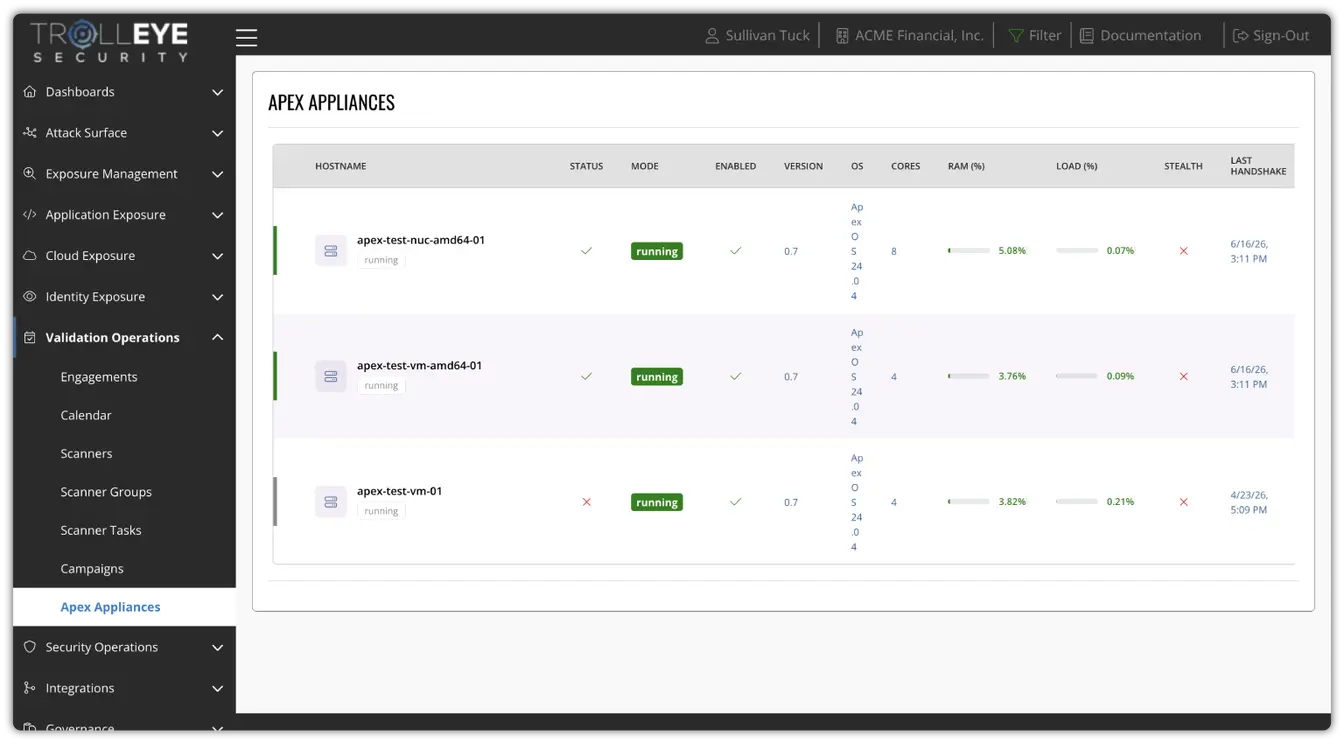
Agentic and human penetration testing, including TrollEye's Apex Penetration Testing Agent, proves which exposures are actually exploitable and reachable. Testing runs continuously and on demand, and expert testers take on complex attack paths. In-house red teams can run their own engagements in the platform too, with findings and evidence in the same record as everything else.
Governed mobilization
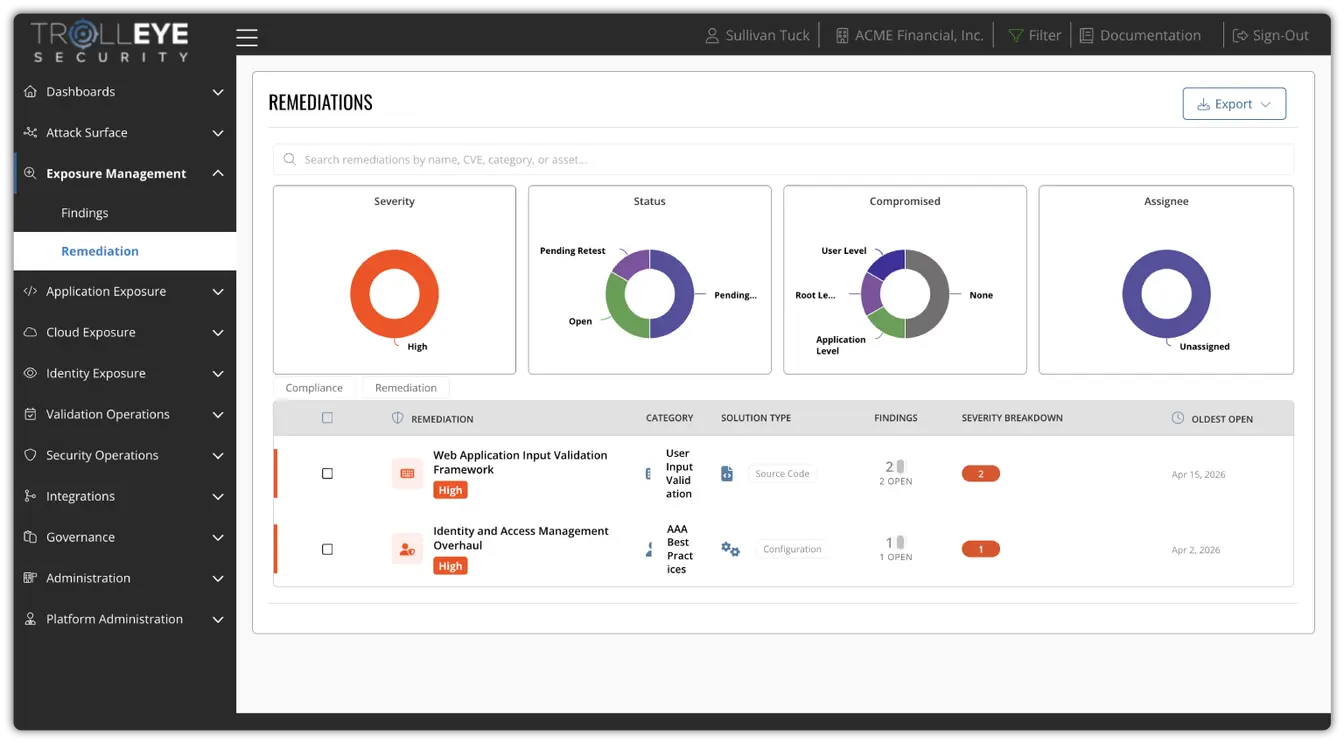
Findings appear in role-based views and sync to Jira. Custom remediation SLAs are rule-based policy, matched on severity, exploitability, internet exposure, and category. TrollEye directs the fix, your teams make the change, and retesting confirms it.
Built for business-unit complexity
The CTEM Enterprise package is designed for distributed infrastructure, multiple business units, and formal risk-management programs, with custom analysis and testing capacity, unlimited users, and monthly service credits for specialist work.
Four years of sustained exposure reduction
A FinTech software company with 500–1,000 employees and multiple applications in production replaced annual penetration testing with a continuous program connecting recurring testing, human validation, developer-ready remediation guidance, and retesting. Results are measured across annual full-scope assessments.
“With multiple fintech applications in production, we wanted to make sure we weren't deploying vulnerable code throughout the year, not just checking our security once a year.”Vice President of Information Security · FinTech Software Company
The company’s primary objective was to release products with no known vulnerabilities, and it now does.
I can identify code vulnerabilities, asset vulnerabilities, time to remediate, findings, and recommendations without chasing everything down.
TrollEye is a strong fit when
- You want to consolidate overlapping tools and testing contracts
- Mobilization across business units is your bottleneck
- You need validation evidence that engineering teams will accept
- Your in-house red team needs one place to run, track, and evidence its testing alongside agentic validation
- You want platform and expert services under one program
Consider other approaches when
- You only need a reporting layer across tools you plan to keep indefinitely
- You need a point tool for a single capability rather than a program across business units